
最新发布第823页

CVE-2024-9487: GitHub Enterprise – SAML Authentication Bypass
漏洞标题 CVE-2024-9487: GitHub Enterprise - SAML Authentication Bypass 漏洞描述 An improper verification of cryptographic signature vulnerability was identified in GitHub Enterpris...
 2024年6月3日 09:23
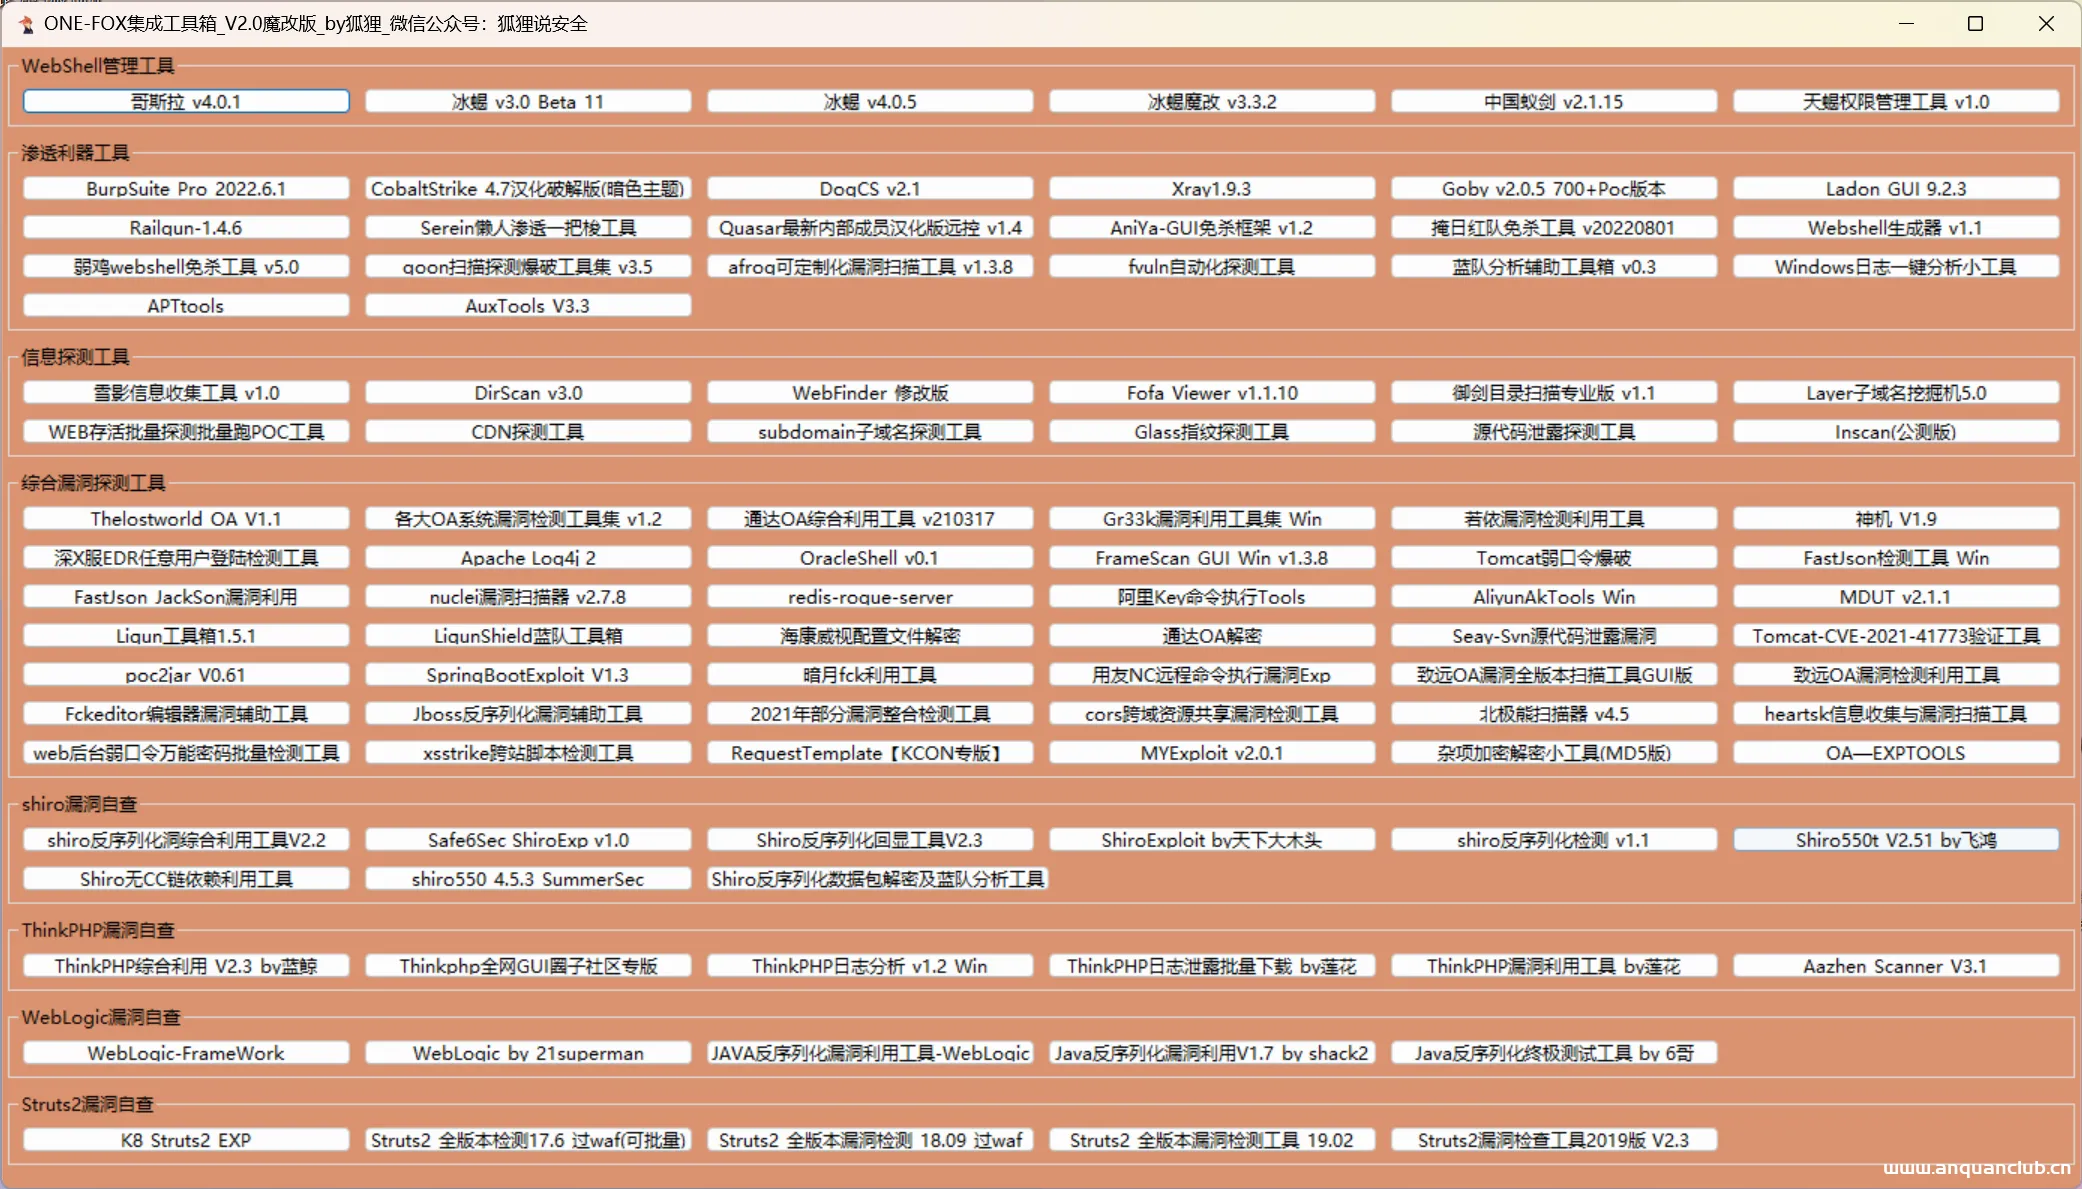
ONE-FOX集成工具箱_V2.0魔改版_by狐狸
本文转载自公众号:狐狸说安全安全小天地只做文章分享,所有文件皆属于狐狸说安全,与本博客无关。原文地址:http://mp.weixin.qq.com/s/CSF_-xbS7u4lywYxihebXQ 0x01 前言 在1.0版本的基础上去...

 2023年1月13日 19:38
CVE-2021-43734: kkFileview v4.0.0 – Local File Inclusion
漏洞标题 CVE-2021-43734: kkFileview v4.0.0 - Local File Inclusion 漏洞描述 kkFileview v4.0.0 is vulnerable to local file inclusion which may lead to a sensitive file leak on a rela...
2021年1月21日 16:59CVE-2024-4348: osCommerce v4.0 – Cross-site Scripting
漏洞标题 CVE-2024-4348: osCommerce v4.0 - Cross-site Scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in osCommerce 4. Affected is an unknown func...
2024年10月17日 05:40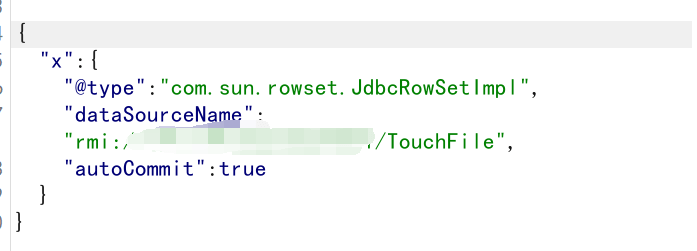
vulhub漏洞复现之fastjson1.2.47反弹shell
前言 现在java站越来越多啦,面试也基本上全部问的都是java呀,加油呀 什么是json? 借用人家的表达:“.json是用来存储简单的数据结构和对象的文件。json是一种轻量级的数据交换格式,基于ECMA...
2023年8月18日 06:48CVE-2022-32430: Lin CMS Spring Boot – Default JWT Token
漏洞标题 CVE-2022-32430: Lin CMS Spring Boot - Default JWT Token 漏洞描述 An access control issue in Lin CMS Spring Boot v0.2.1 allows attackers to access the backend information a...
2022年4月3日 01:00CVE-2009-4223: KR-Web <=1.1b2 - Remote File Inclusion
漏洞标题 CVE-2009-4223: KR-Web <=1.1b2 - Remote File Inclusion 漏洞描述 KR-Web 1.1b2 and prior contain a remote file inclusion vulnerability via adm/krgourl.php, which allows re...
2009年4月21日 06:13CVE-2024-34982: LyLme-Spage – Arbitary File Upload
漏洞标题 CVE-2024-34982: LyLme-Spage - Arbitary File Upload 漏洞描述 An arbitrary file upload vulnerability in the component /include/file.php of lylme_spage v1.9.5 allows attacker...
2024年12月2日 04:52CVE-2024-13159: Ivanti EPM – Credential Coercion Vulnerability in GetHashForWildcardRecursive
漏洞标题 CVE-2024-13159: Ivanti EPM - Credential Coercion Vulnerability in GetHashForWildcardRecursive 漏洞描述 A vulnerability in Ivanti Endpoint Manager (EPM) allows an unauthent...
2024年6月11日 08:07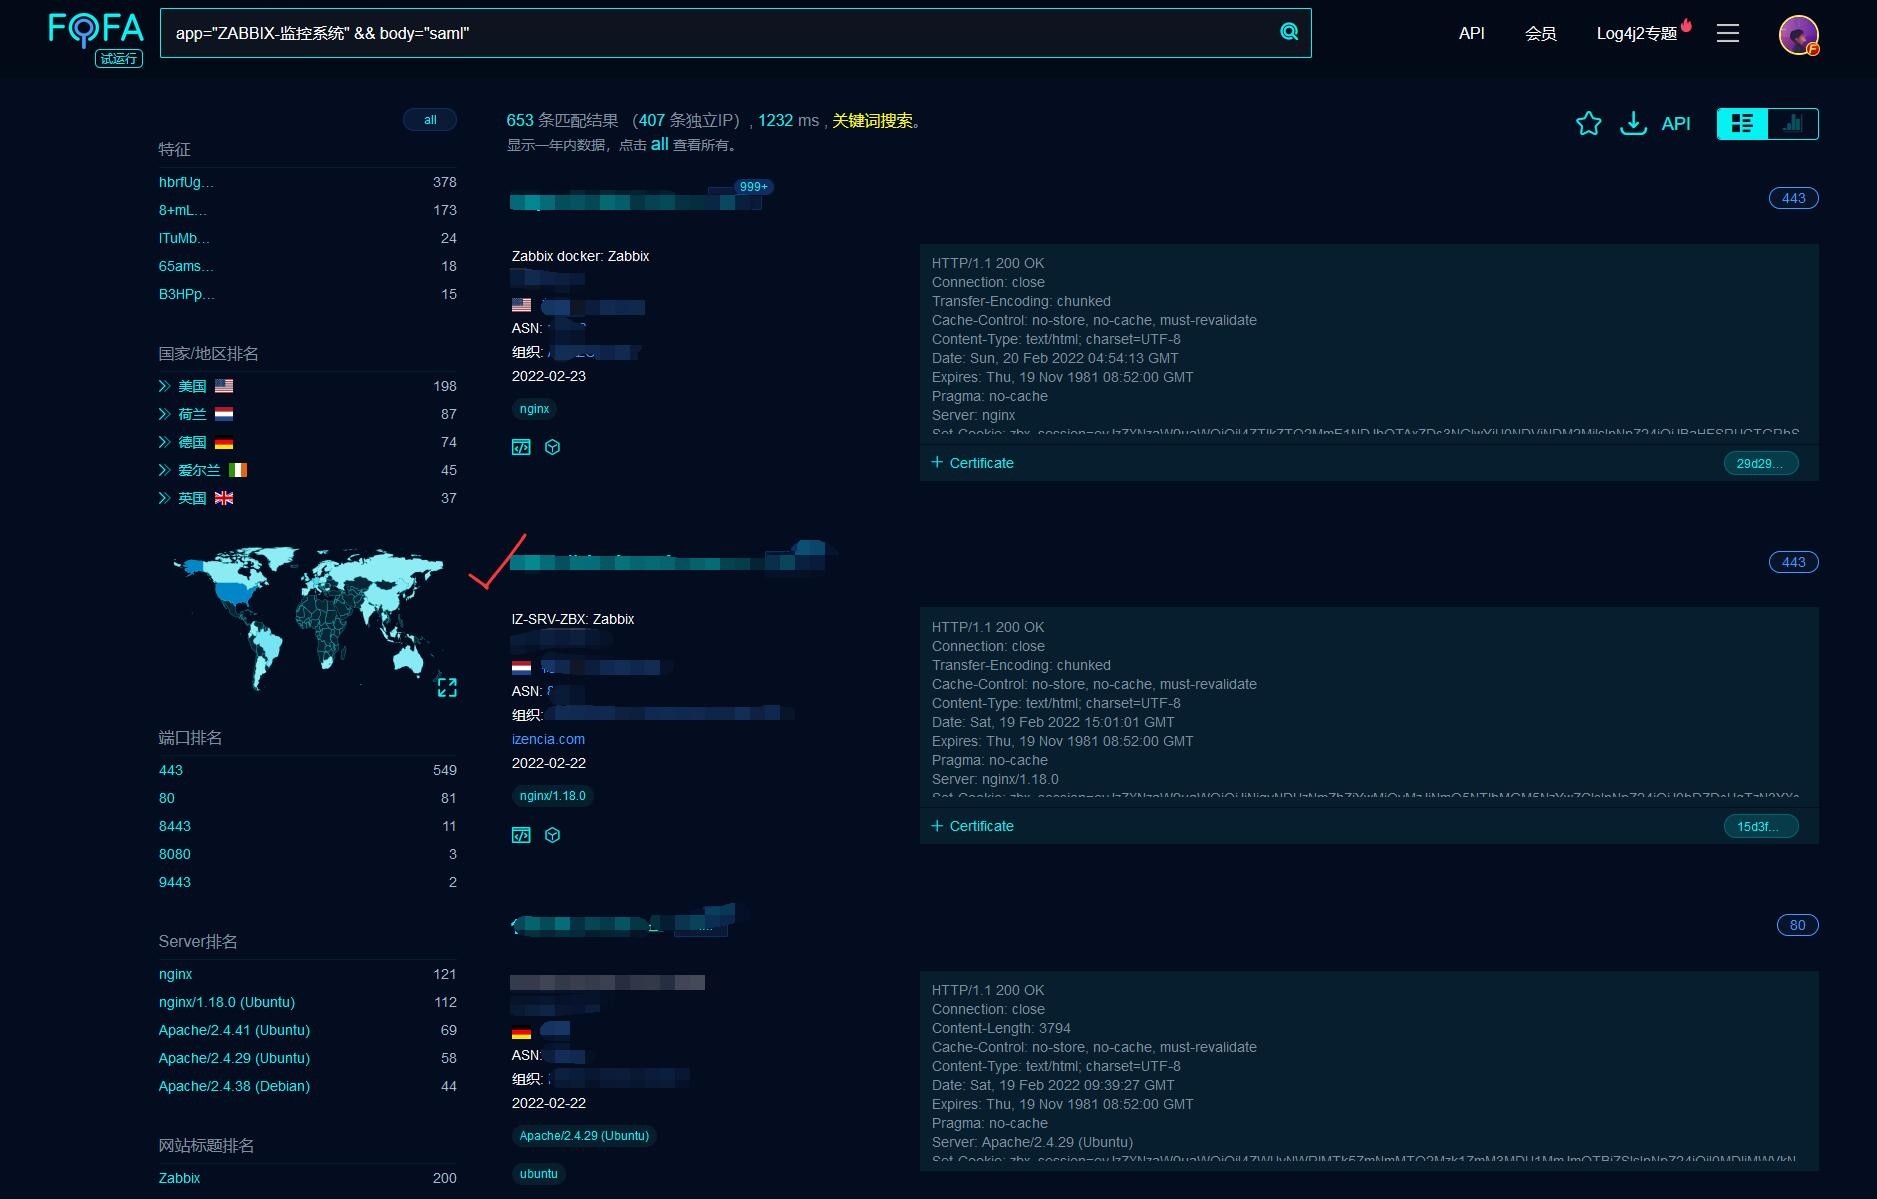
CVE-2022-23131_Zabbix登录绕过漏洞分析及复现
前言 由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,文章作者不为此承担任何责任。 本文章中的漏洞均为公开的漏洞收集,如果文章中的漏洞出现敏感...
2022年3月10日 23:37CVE-2024-21644: pyLoad Flask Config – Access Control
漏洞标题 CVE-2024-21644: pyLoad Flask Config - Access Control 漏洞描述 pyLoad is the free and open-source Download Manager written in pure Python. Any unauthenticated user can brow...
2024年11月6日 03:01CVE-2024-13624: WordPress WPMovieLibrary Plugin <= 2.1.4.8 - Cross-Site Scripting
漏洞标题 CVE-2024-13624: WordPress WPMovieLibrary Plugin <= 2.1.4.8 - Cross-Site Scripting 漏洞描述 The WPMovieLibrary WordPress plugin through version 2.1.4.8 contains a reflec...
2024年10月10日 21:25CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection
漏洞标题 CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection 漏洞描述 The wcfm_ajax_controller AJAX action of the WCFM Marketplace WordPress plugin...
2021年10月14日 23:15CVE-2018-5316: WordPress SagePay Server Gateway for WooCommerce <1.0.9 - Cross-Site Scripting
漏洞标题 CVE-2018-5316: WordPress SagePay Server Gateway for WooCommerce <1.0.9 - Cross-Site Scripting 漏洞描述 WordPress SagePay Server Gateway for WooCommerce before 1.0.9 is ...
2018年9月18日 19:42CVE-2010-1657: Joomla! Component SmartSite 1.0.0 – Local File Inclusion
漏洞标题 CVE-2010-1657: Joomla! Component SmartSite 1.0.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the SmartSite (com_smartsite) component 1.0.0 for J...
2010年4月29日 01:18CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure
漏洞标题 CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure 漏洞描述 The LearnDash LMS plugin for WordPress is vulnerable to Sensitive Information Exposure i...
2024年2月6日 12:40
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

