
最新发布第841页
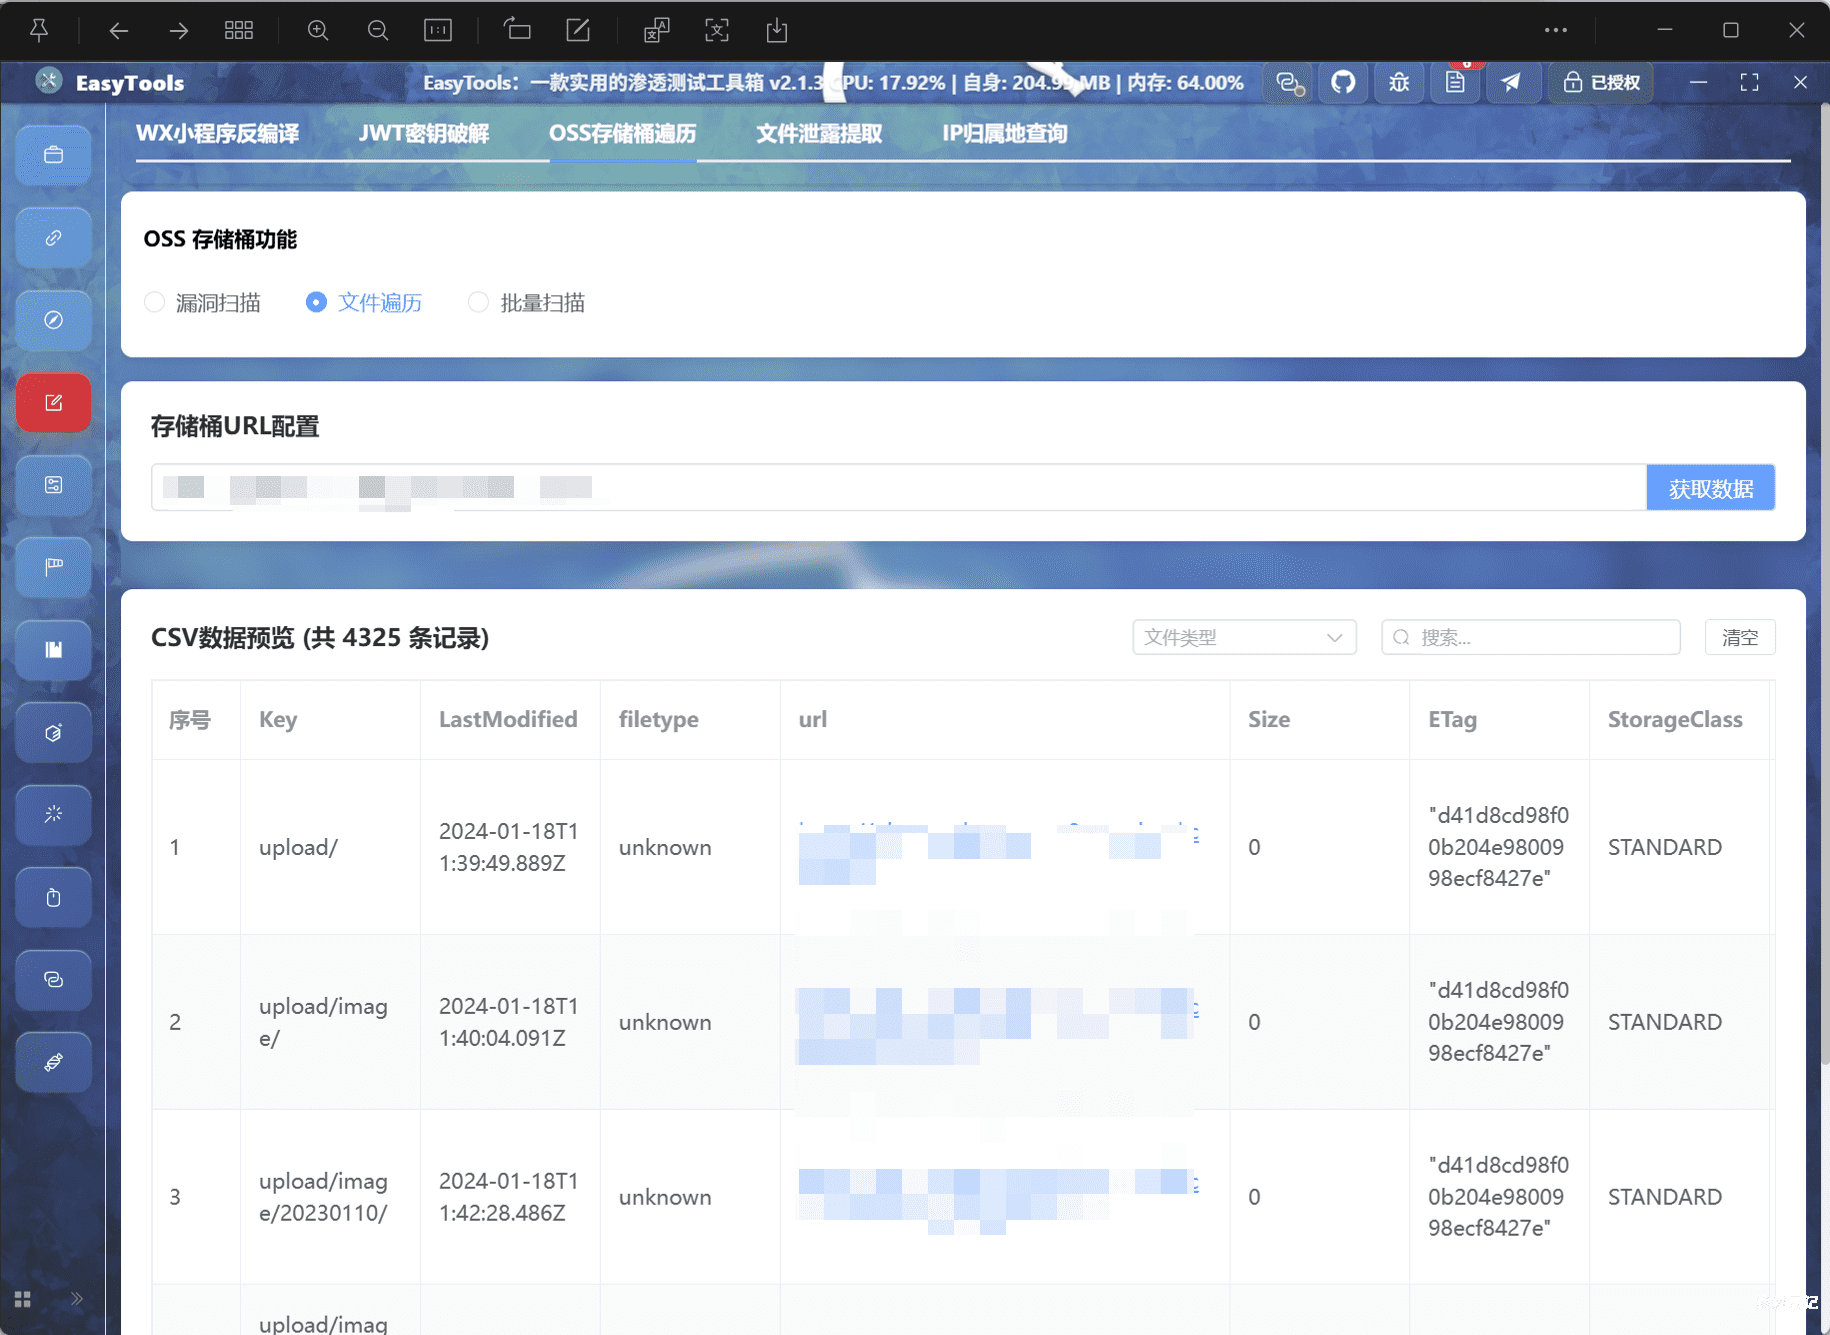
EasyTools渗透测试工具箱V2.1.4更新(优化资源桶遍历功能,支持kkfileview预览,新增空间测绘、AI版域名收集功能等诸多功能)
前言 各位看官老爷们,很久没有更新了,新的一年了在此汇报一下更新进度: 优化资源桶遍历功能,支持kkfileview预览; 重构渗透测试模块,调用httpx提高性能与准确度; 新增AI底座,方便后续功能...

 2026年3月1日 15:46

CVE-2025-40630: IceWarp Mail Server ≤11.4.0 – Open Redirect
漏洞标题 CVE-2025-40630: IceWarp Mail Server ≤11.4.0 - Open Redirect 漏洞描述 IceWarp Mail Server version 11.4.0 and below contains an open redirect vulnerability that allows atta...
 2025年7月15日 05:33
CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
2025年8月9日 03:35CVE-2018-10088: XiongMai uc-httpd 1.0.0 – Buffer Overflow
漏洞标题 CVE-2018-10088: XiongMai uc-httpd 1.0.0 - Buffer Overflow 漏洞描述 Buffer overflow in XiongMai uc-httpd 1.0.0 has unspecified impact and attack vectors, a different vulner...
2018年4月4日 23:57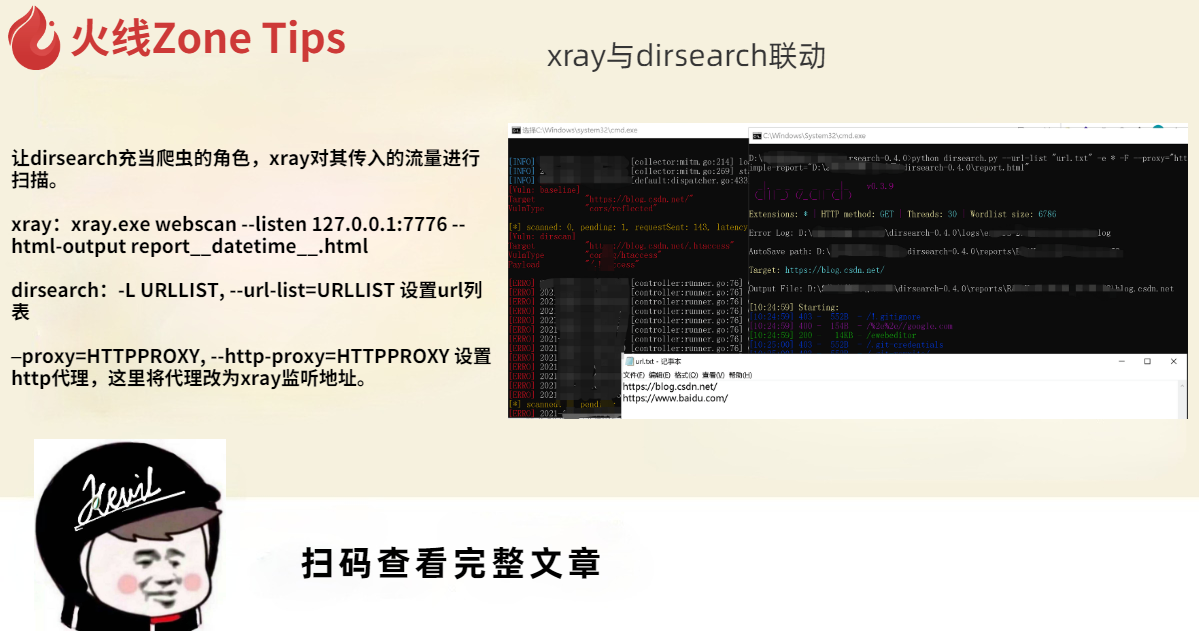
xray与dirsearch联动
让dirsearch充当爬虫的角色,xray对其传入的流量进行扫描。 xray:xray.exe webscan --listen 127.0.0.1:7776 --html-output reportdatetime.html dirsearch:-L URLLIST, --url-list=URLLIST ...
2022年3月10日 23:36Apache Druid存在服务器请求伪造漏洞(CVE-2025-27888)
漏洞标题 Apache Druid存在服务器请求伪造漏洞(CVE-2025-27888) 漏洞描述 Apache Druid存在服务器请求伪造漏洞,攻击者可以直接访问的内部系统。 PoC代码 暂无
2025年4月22日 18:53CVE-2018-6910: DedeCMS 5.7 – Path Disclosure
漏洞标题 CVE-2018-6910: DedeCMS 5.7 - Path Disclosure 漏洞描述 DedeCMS 5.7 allows remote attackers to discover the full path via a direct request for include/downmix.inc.php or inc...
2018年3月25日 23:30CVE-2004-1602: ProFTPD 1.2.x – Username Enumeration via Timing Attack
漏洞标题 CVE-2004-1602: ProFTPD 1.2.x - Username Enumeration via Timing Attack 漏洞描述 ProFTPD versions 1.2.x (including 1.2.8 and 1.2.10) are vulnerable to timing attacks that al...
2004年10月13日 20:40CVE-2023-32068: XWiki – Open Redirect
漏洞标题 CVE-2023-32068: XWiki - Open Redirect 漏洞描述 XWiki Platform is vulnerable to open redirect attacks due to improper validation of the xredirect parameter. This allows an ...
2023年5月2日 19:52CVE-2008-1547: Microsoft OWA Exchange Server 2003 – ‘redir.asp’ Open Redirection
漏洞标题 CVE-2008-1547: Microsoft OWA Exchange Server 2003 - 'redir.asp' Open Redirection 漏洞描述 Open redirect vulnerability in exchweb/bin/redir.asp in Microsoft Outlo...
2008年1月26日 23:12CVE-2024-4956: Nexus Repository Manager 文件读取漏洞
漏洞标题 CVE-2024-4956: Nexus Repository Manager 文件读取漏洞 漏洞描述 Path Traversal in Sonatype Nexus Repository 3 allows an unauthenticated attacker to read system files. Fixed ...
2024年8月26日 18:04
Linux whatis命令的使用方法_Linux
这篇文章主要介绍了Linux whatis命令的使用方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 01. 命令概述 what...
2024年4月23日 20:13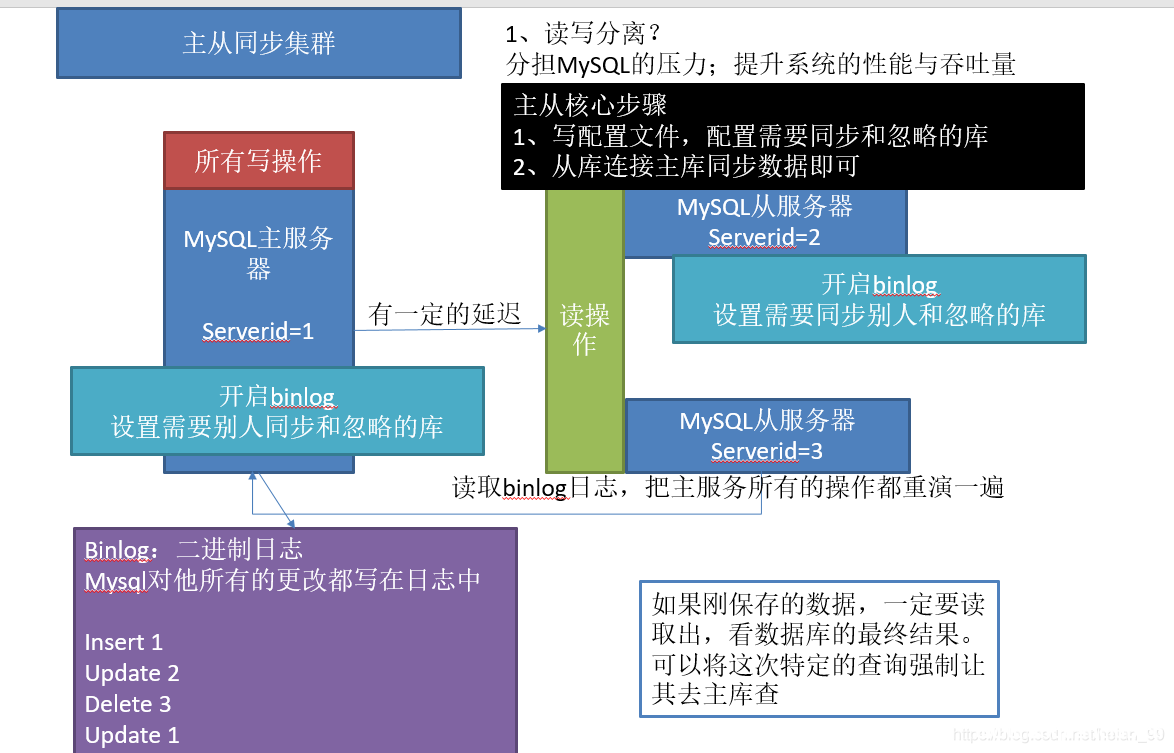
docker实现mysql主从复制的示例代码_docker
Docker它不香吗?即省去了安装Mysql所需要的步骤,有多个容器之间相互资源独立,IP互不冲突,具有一定的参考价值,感兴趣的可以了解一下 目录一、概述1、原理2、实现三、创建Slave实例四、主从配...
2022年6月15日 22:42Apache OFBiz CVE-2024-32113 目录遍历漏洞
漏洞标题 Apache OFBiz CVE-2024-32113 目录遍历漏洞 漏洞描述 Apache OFBiz 存在目录遍历漏洞,此漏洞是由于未充分验证用户输入的url所导致的。 PoC代码 暂无
2024年11月3日 13:27CVE-2021-24876: Registrations for The Events Calendar < 2.7.5 - Authenticated Reflected Cross-Site Scripting
漏洞标题 CVE-2021-24876: Registrations for The Events Calendar < 2.7.5 - Authenticated Reflected Cross-Site Scripting 漏洞描述 The Registrations for the Events Calendar WordPres...
2021年9月3日 13:04Apache HTTPD 换行解析漏洞(CVE-2017-15715)
漏洞标题 Apache HTTPD 换行解析漏洞(CVE-2017-15715) 漏洞描述 Apache HTTPD 换行解析漏洞(CVE-2017-15715) PoC代码 暂无
2017年6月28日 19:09
2026年9月25日 11:45
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

