
最新发布第850页
centos7系统部署k8s集群详细介绍_Linux
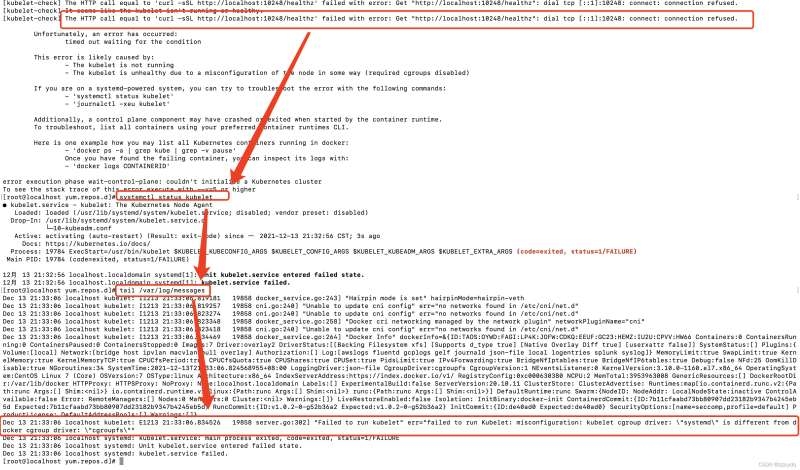
目录1 版本、规划1.1 版本信息:1.2集群规划2.部署1、关闭防火墙2、关闭selinux3、关闭swap4、添加主机名和IP对应关系5、将桥接的IPV4流量传递给iptables的链6、安装docker 安装:7、添加阿里云...
 2022年6月14日 23:03

CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
2025年6月25日 13:23CVE-2021-40524: Pure-FTPd 1.0.23 < 1.0.50 - Arbitrary File Upload
漏洞标题 CVE-2021-40524: Pure-FTPd 1.0.23 < 1.0.50 - Arbitrary File Upload 漏洞描述 Pure-FTPd versions 1.0.23 through 1.0.49 contain an arbitrary file upload vulnerability due t...
2021年12月4日 14:26
充分利用互联网资源的小tips-续集
挖掘src的时候找到一个资产如下 正常测试弱口令,未授权接口等无果 通过fofa搜索指纹,发现是一个通用的cms 把站点都薅下来,然后尝试弱口令,成功进入后台,顺便发现了一个这个后台的通用默认...
2022年3月10日 23:39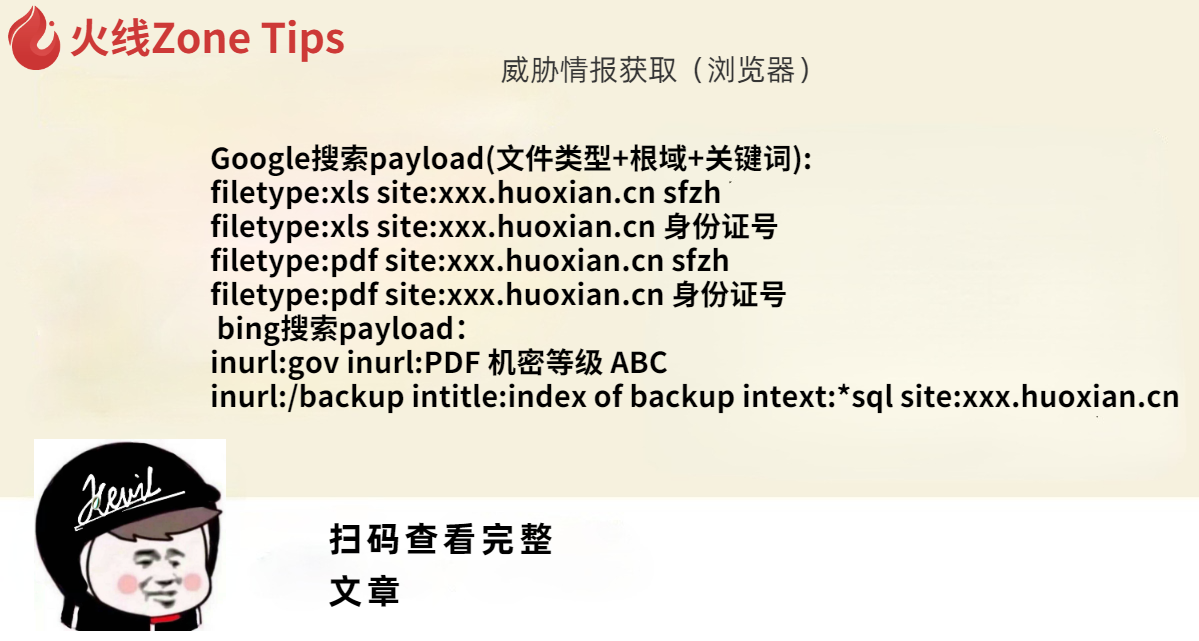
威胁情报获取(浏览器)
Google搜索payload(文件类型+根域+关键词): filetype:xls site:xxx.huoxian.cn sfzh filetype:xls site:xxx.huoxian.cn 身份证号 filetype:pdf site:xxx.huoxian.cn sfzh filetype:pdf site:xxx...
2022年3月10日 23:34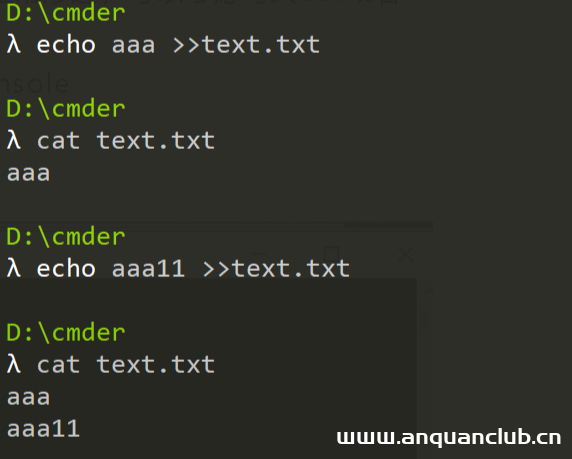
文件写入小技巧
在某些场景,我们可能需要写入bat,vbs,py等文件,当我们逐个echo将字符写入文件时,写入内容会自动换行: 可以通过命令 >>text.txt set/p='test' < nul 避免写入内容被换行 文字来源...
2022年3月10日 23:32CVE-2018-19127: PHPCMS 2008 – Remote Code Execution via Template Injection
漏洞标题 CVE-2018-19127: PHPCMS 2008 - Remote Code Execution via Template Injection 漏洞描述 PHPCMS 2008 suffers from an unauthenticated RCE via template injection in type.php, whe...
2018年7月2日 16:45CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
2024年7月31日 20:14CVE-2014-6271: ShellShock – Remote Code Execution
漏洞标题 CVE-2014-6271: ShellShock - Remote Code Execution 漏洞描述 GNU Bash through 4.3 processes trailing strings after function definitions in the values of environment variable...
2014年12月7日 14:40
bugbounty技巧聚合20211122
漏洞报告 【Internet Bug Bounty 1,200刀】Ruby - Regular Expression Denial of Service Vulnerability of Date Parsing Methods http://hackerone.com/reports/1404789 【Internet Bug Bounty...
2022年3月10日 23:33CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
2022年5月10日 13:18CVE-2017-9791: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-9791: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.1.x and 2.3.x with the Struts 1 plugin might allow remote code execution via a malici...
2017年7月4日 20:29CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
2025年4月14日 09:43CVE-2015-7297: Joomla Core SQL Injection
漏洞标题 CVE-2015-7297: Joomla Core SQL Injection 漏洞描述 Joomla 3.4.4 之前的 3.2 SQL 注入漏洞 Joomla 中的 SQL 注入漏洞!3.4.4 之前的 3.2 允许远程攻击者通过未指定的向量执行任意 SQ...
2015年9月5日 01:54CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
2023年9月3日 12:55CVE-2019-2767: Oracle Business Intelligence Publisher – XML External Entity Injection
漏洞标题 CVE-2019-2767: Oracle Business Intelligence Publisher - XML External Entity Injection 漏洞描述 Oracle Business Intelligence Publisher is vulnerable to an XML external enti...
2019年10月20日 07:41
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

