
最新发布第862页

CVE-2023-52251: Kafka UI 0.7.1 Command Injection
漏洞标题 CVE-2023-52251: Kafka UI 0.7.1 Command Injection 漏洞描述 An issue discovered in provectus kafka-ui 0.4.0 through 0.7.1 allows remote attackers to execute arbitrary code v...
 2023年7月30日 04:20
CVE-2023-45375: PrestaShop PireosPay – SQL Injection
漏洞标题 CVE-2023-45375: PrestaShop PireosPay - SQL Injection 漏洞描述 In the module “PireosPay” (pireospay) up to version 1.7.9 from 01generator.com for PrestaShop, a guest can ...
2023年8月15日 08:17CVE-2016-1000135: WordPress HDW Video Gallery <=1.2 - Cross-Site Scripting
漏洞标题 CVE-2016-1000135: WordPress HDW Video Gallery <=1.2 - Cross-Site Scripting 漏洞描述 WordPress HDW Video Gallery 1.2 and before contains a cross-site scripting vulnerabi...
2016年9月20日 15:04
使用VMware 15 安装虚拟机和使用CentOS 8的步骤详解_Linux
这篇文章主要介绍了使用VMware 15 安装虚拟机和使用CentOS 8的详细步骤,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 前言: 最近在学习Linux和.Net Core,学习一...
2024年6月18日 20:50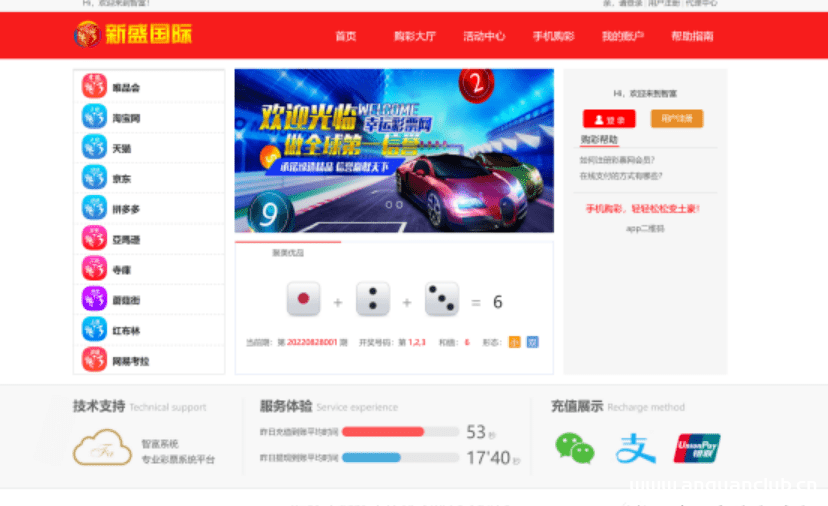
记一次彩票杀猪盘渗透
0x02 事件描述 网络赌博是指通过互联网手段(非法赌博网站、博彩App、微信群等)进行的赌博活动。由于网络赌博不合法,资金不受法律保护,有很多“出老千”的行为,很多人被骗后往往不敢报警,...
2026年2月13日 12:53CVE-2021-46418: Telesquare TLR-2855KS6 – Arbitrary File Creation
漏洞标题 CVE-2021-46418: Telesquare TLR-2855KS6 - Arbitrary File Creation 漏洞描述 An unauthorized file creation vulnerability in Telesquare TLR-2855KS6 via PUT method can allow cr...
2021年6月22日 22:43CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年12月2日 02:18CVE-2024-25852: Linksys RE7000 – Command Injection
漏洞标题 CVE-2024-25852: Linksys RE7000 - Command Injection 漏洞描述 Linksys RE7000 v2.0.9, v2.0.11, and v2.0.15 have a command execution vulnerability in the "AccessControlLi...
2024年12月10日 07:57CVE-2019-9193: PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
漏洞标题 CVE-2019-9193: PostgreSQL 9.3-12.3 Authenticated Remote Code Execution 漏洞描述 In PostgreSQL 9.3 through 11.2, the "COPY TO/FROM PROGRAM" function allows superu...
2019年11月13日 06:26CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection
漏洞标题 CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection 漏洞描述 TOTOLink 多个设备 download.cgi文件存在远程命令执行漏洞,攻击者通过构造特殊的请求可以获取服务器...
2022年5月21日 11:35CVE-2007-3010: Alcatel-Lucent OmniPCX – Remote Command Execution
漏洞标题 CVE-2007-3010: Alcatel-Lucent OmniPCX - Remote Command Execution 漏洞描述 The OmniPCX web interface has a script "masterCGI" with a remote command execution vuln...
2007年8月23日 23:10CVE-2024-6420: Hide My WP Ghost < 5.2.02 - Hidden Login Page Disclosure
漏洞标题 CVE-2024-6420: Hide My WP Ghost < 5.2.02 - Hidden Login Page Disclosure 漏洞描述 The Hide My WP Ghost plugin does not prevent redirects to the login page via the auth_r...
2024年11月23日 19:10CVE-2014-100004: Sitecore CMS – Cross-Site Scripting
漏洞标题 CVE-2014-100004: Sitecore CMS - Cross-Site Scripting 漏洞描述 Sitecore CMS contains a cross-site scripting vulnerability via the "special way" of displaying XML ...
2014年5月1日 10:49CVE-2023-23491: Quick Event Manager < 9.7.5 - Cross-Site Scripting
漏洞标题 CVE-2023-23491: Quick Event Manager < 9.7.5 - Cross-Site Scripting 漏洞描述 The Quick Event Manager WordPress Plugin, version < 9.7.5, is affected by a reflected cro...
2023年10月25日 22:07CVE-2020-13379: Grafana 3.0.1-7.0.1 – Server-Side Request Forgery
漏洞标题 CVE-2020-13379: Grafana 3.0.1-7.0.1 - Server-Side Request Forgery 漏洞描述 Grafana 3.0.1 through 7.0.1 is susceptible to server-side request forgery via the avatar feature...
2020年1月31日 05:50CVE-2004-0656: Pure-FTPd ≤ 1.0.18 – DoS via Connection Limit Exhaustion
漏洞标题 CVE-2004-0656: Pure-FTPd ≤ 1.0.18 - DoS via Connection Limit Exhaustion 漏洞描述 Pure-FTPd versions ≤ 1.0.18 are vulnerable to denial of service through connection limit...
2004年7月7日 14:07
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

