
最新发布第862页

CVE-2019-7192: QNAP QTS and Photo Station 6.0.3 – Remote Command Execution
漏洞标题 CVE-2019-7192: QNAP QTS and Photo Station 6.0.3 - Remote Command Execution 漏洞描述 This improper access control vulnerability allows remote attackers to gain unauthorized...
 2019年8月3日 20:20
CVE-2017-18580: WordPress Shortcodes Ultimate <= 5.0.0 - Authenticated Remote Code Execution
漏洞标题 CVE-2017-18580: WordPress Shortcodes Ultimate <= 5.0.0 - Authenticated Remote Code Execution 漏洞描述 Shortcodes Ultimate plugin before 5.0.1 for WordPress contains a r...
2017年3月18日 22:57
浅谈Docker run 容器处于created状态问题_docker
这篇文章主要介绍了解决Docker run 容器处于created状态问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 在最近遇到的一次问题中,有这样一种现象: 系统有一个测试脚本...
2022年8月9日 21:39CVE-2022-0540: Atlassian Jira Seraph – Authentication Bypass
漏洞标题 CVE-2022-0540: Atlassian Jira Seraph - Authentication Bypass 漏洞描述 Jira Seraph allows a remote, unauthenticated attacker to bypass authentication by sending a specially...
2022年8月1日 20:14CVE-2023-27637: PrestaShop `tshirtecommerce` Module – SQL Injection
漏洞标题 CVE-2023-27637: PrestaShop `tshirtecommerce` Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via t...
2023年8月8日 05:56
windows下快速安装nginx并配置开机自启动的方法_nginx
这篇文章主要介绍了windows下快速安装nginx 并配置开机自启动的相关知识,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、windows系统下Ng...
2022年6月15日 09:43CVE-2021-24406: WordPress wpForo Forum < 1.9.7 - Open Redirect
漏洞标题 CVE-2021-24406: WordPress wpForo Forum < 1.9.7 - Open Redirect 漏洞描述 WordPress wpForo Forum < 1.9.7 is susceptible to an open redirect vulnerability because the p...
2021年9月25日 08:11CVE-2025-27505: GeoServer – Missing Authorization on REST API Index
漏洞标题 CVE-2025-27505: GeoServer - Missing Authorization on REST API Index 漏洞描述 GeoServer contains a missing authorization vulnerability that allows unauthorized access to th...
2025年1月27日 20:53CVE-2017-9805: Apache Struts2 S2-052 – Remote Code Execution
漏洞标题 CVE-2017-9805: Apache Struts2 S2-052 - Remote Code Execution 漏洞描述 The REST Plugin in Apache Struts 2.1.1 through 2.3.x before 2.3.34 and 2.5.x before 2.5.13 uses an XS...
2017年4月11日 00:12CVE-2005-3634: SAP Web Application Server 6.x/7.0 – Open Redirect
漏洞标题 CVE-2005-3634: SAP Web Application Server 6.x/7.0 - Open Redirect 漏洞描述 frameset.htm in the BSP runtime in SAP Web Application Server (WAS) 6.10 through 7.00 allows rem...
2005年6月11日 07:32CVE-2019-11507: Pulse Secure Pulse Connect Secure – Cross-Site Scripting (Reflected)
漏洞标题 CVE-2019-11507: Pulse Secure Pulse Connect Secure - Cross-Site Scripting (Reflected) 漏洞描述 Pulse Secure Pulse Connect Secure (PCS) 8.3.x before 8.3R7.1 and 9.0.x before...
2019年6月19日 14:42CVE-2023-26842: ChurchCRM 4.5.3 – Cross-Site Scripting
漏洞标题 CVE-2023-26842: ChurchCRM 4.5.3 - Cross-Site Scripting 漏洞描述 A stored Cross-site scripting (XSS) vulnerability in ChurchCRM 4.5.3 allows remote attackers to inject arbi...
2023年12月30日 01:40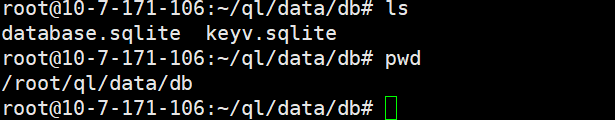
最新版青龙面板密码忘记之后怎么找回
前言 安装完青龙面板之后,咱们很容易忘记密码是什么,这个时间咱们如果是docker安装的话,可以通过以下方式找回密码。 找回密码 登录青龙面板服务器 查看启动docker的具体配置 docker inspect ...

 2026年3月9日 22:15
CVE-2019-9618: WordPress GraceMedia Media Player 1.0 – Local File Inclusion
漏洞标题 CVE-2019-9618: WordPress GraceMedia Media Player 1.0 - Local File Inclusion 漏洞描述 WordPress GraceMedia Media Player plugin 1.0 is susceptible to local file inclusion vi...
2019年9月10日 17:24CVE-2020-2096: Jenkins Gitlab Hook <=1.4.2 - Cross-Site Scripting
漏洞标题 CVE-2020-2096: Jenkins Gitlab Hook <=1.4.2 - Cross-Site Scripting 漏洞描述 Jenkins Gitlab Hook 1.4.2 and earlier does not escape project names in the build_now endpoint...
2020年1月26日 10:42CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting
漏洞标题 CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting 漏洞描述 WordPress e-search 1.0 and before contains a reflected cross-site scripting vulnerability via...
2016年9月29日 14:36
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

