
最新发布第874页

CVE-2020-12478: TeamPass 2.1.27.36 – Improper Authentication
漏洞标题 CVE-2020-12478: TeamPass 2.1.27.36 - Improper Authentication 漏洞描述 TeamPass 2.1.27.36 is susceptible to improper authentication. An attacker can retrieve files from the...
 2020年4月12日 16:08
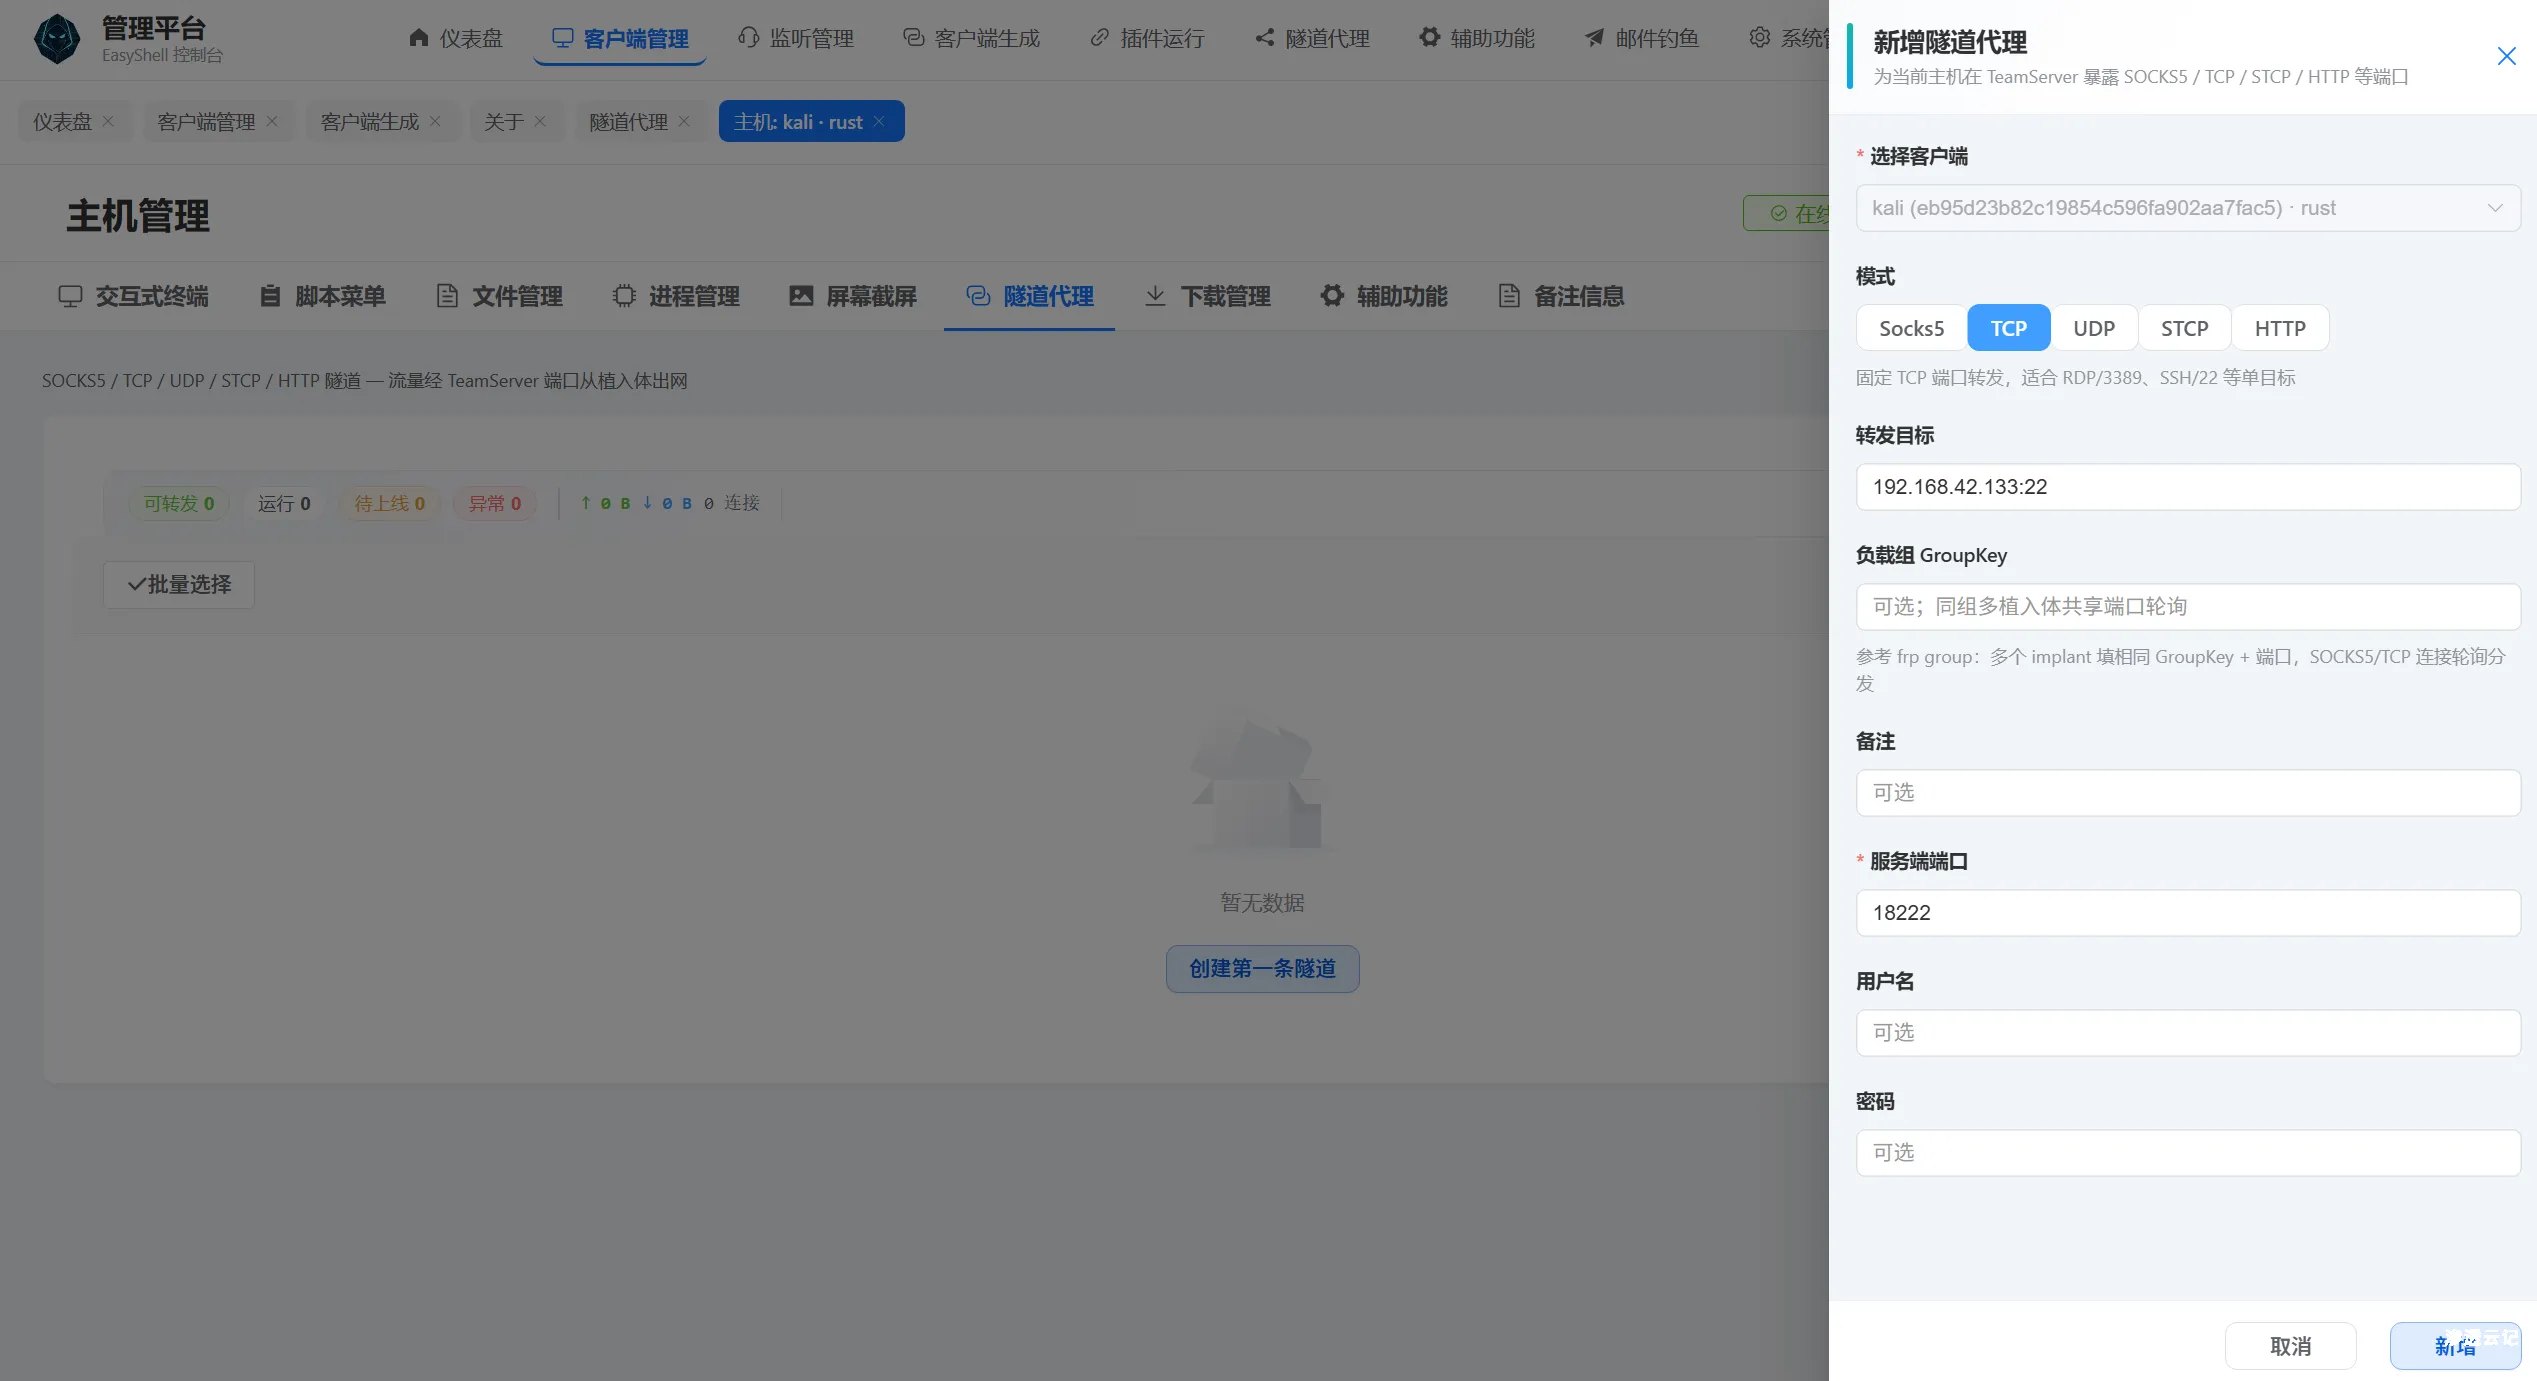
【工具更新】EasyShell v2.7 版本更新,新增tcp udp等端口转发协议,支持稳定实现ssh、rdp等协议的稳定连接
更新说明 感谢各位师傅们的热心测试,发现了诸多bug,目前已经修复的有: 修复菜单标签刷新空白页面的bug 修复文件管理无法修改时间的bug 新增tcp stcp udp等协议隧道代理功能,支持rdp、ssh等...

 2026年8月16日 20:18
Atlassian Confluence 远程代码执行漏洞(CVE-2021-26084)
漏洞标题 Atlassian Confluence 远程代码执行漏洞(CVE-2021-26084) 漏洞描述 Atlassian 官方发布了Confluence Server Webwork OGNL注入漏洞(CVE-2021-26084)的安全公告,远程攻击者在经过身份...
2021年5月13日 20:13
Docker遇到Intellij IDEA,Java开发提升了十倍生产力_docker
这篇文章主要介绍了Docker遇到Intellij IDEA,Java开发提升了十倍生产力,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、开发前准备 ...
2023年4月6日 21:05CVE-2024-1021: Rebuild <= 3.5.5 - Server-Side Request Forgery
漏洞标题 CVE-2024-1021: Rebuild <= 3.5.5 - Server-Side Request Forgery 漏洞描述 There is a security vulnerability in Rebuild 3.5.5, which is due to a server-side request forgery...
2024年5月6日 16:50CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection
漏洞标题 CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection 漏洞描述 WordPress Pricing Deals for WooCommerce plugin through 2.0.2.02 contains a SQ...
2022年1月16日 10:02CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting
漏洞标题 CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting 漏洞描述 HashiCorp Consul and Consul Enterprise up to version 1.9.4 are vulnerable to ...
2020年7月18日 14:23CVE-2024-13853: WordPress SEO Tools Plugin 4.0.7 – Cross-Site Scripting
漏洞标题 CVE-2024-13853: WordPress SEO Tools Plugin 4.0.7 - Cross-Site Scripting 漏洞描述 The SEO Tools WordPress plugin through version 4.0.7 contains a reflected cross-site scrip...
2024年4月7日 21:23CVE-2023-36934: MOVEit Transfer – SQL Injection
漏洞标题 CVE-2023-36934: MOVEit Transfer - SQL Injection 漏洞描述 In Progress MOVEit Transfer before 2020.1.11 (12.1.11), 2021.0.9 (13.0.9), 2021.1.7 (13.1.7), 2022.0.7 (14.0.7), 2...
2023年10月24日 16:02CVE-2023-39650: PrestaShop Theme Volty CMS Blog – SQL Injection
漏洞标题 CVE-2023-39650: PrestaShop Theme Volty CMS Blog - SQL Injection 漏洞描述 In the module 'Theme Volty CMS Blog' (tvcmsblog) up to versions 4.0.1 from Theme Volty f...
2023年5月28日 17:23
windows10下Hexo与GitHub绑定自定义域名的配置方法_win服务器
这篇文章主要介绍了windows10下Hexo与GitHub绑定自定义域名的方法,本文通过图文并茂的形式给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 windows10下Hexo与GitHub绑定自...
2026年8月19日 11:45
以隐私保护为卖点的搜索引擎DuckDuckGo在2021年增长了46%
DuckDuckGo是总部位于美国的一款网络搜索引擎,主张保护使用者的隐私,承诺不监控、不记录使用者的搜寻内容。DuckDuckGo还是应用商店下载量最大的浏览应用程序之一,在美国约有2700万用户。2020...
2022年3月10日 23:34CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting
漏洞标题 CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting 漏洞描述 WSO2 Management Console through 5.10 is susceptible to reflected cross-site script...
2020年10月20日 17:17CVE-2021-24746: WordPress Sassy Social Share Plugin <3.3.40 - Cross-Site Scripting
漏洞标题 CVE-2021-24746: WordPress Sassy Social Share Plugin <3.3.40 - Cross-Site Scripting 漏洞描述 WordPress plugin Sassy Social Share < 3.3.40 contains a reflected cross-s...
2021年12月11日 18:42CVE-2024-50340: Symfony Profiler – Remote Access via Injected Arguments
漏洞标题 CVE-2024-50340: Symfony Profiler - Remote Access via Injected Arguments 漏洞描述 symfony/runtime is a module for the Symphony PHP framework which enables decoupling PHP ap...
2024年5月6日 20:26CVE-2023-5561: WordPress Core – Post Author Email Disclosure
漏洞标题 CVE-2023-5561: WordPress Core - Post Author Email Disclosure 漏洞描述 WordPress Core is vulnerable to Sensitive Information Exposure in versions between 4.7.0 and 6.3.1 vi...
2023年3月4日 00:52
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

