
最新发布第879页
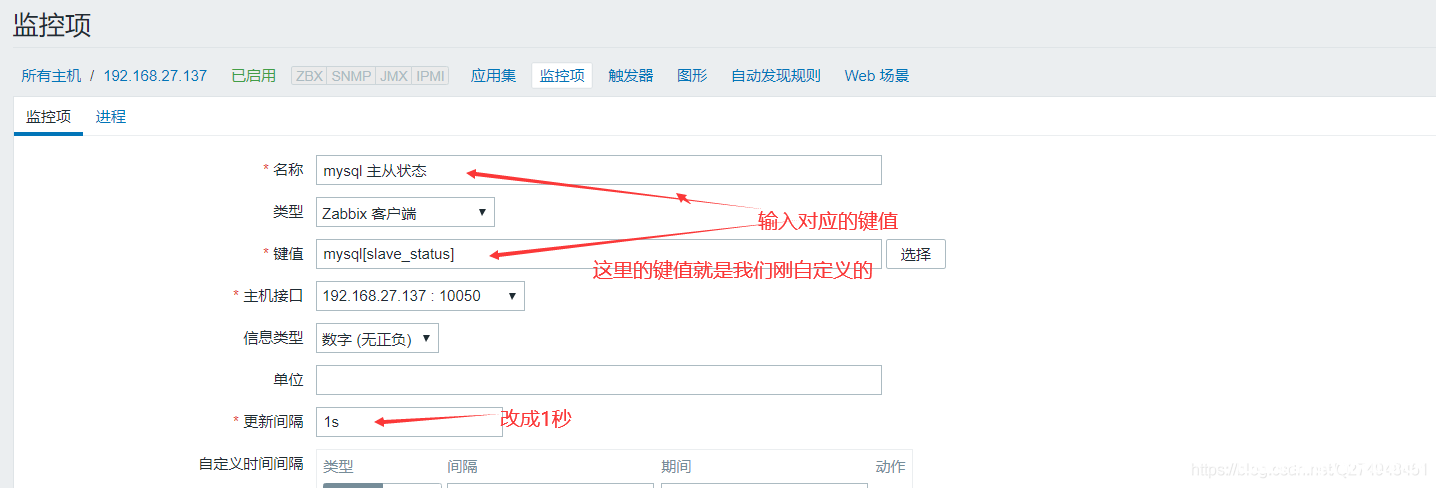
zabbix 监控mysql的方法_zabbix
这篇文章主要介绍了zabbix 监控mysql的方法,本文给大家介绍的非常详细,对大家的学习或工作或学习具有一定的参考借鉴价值,需要的朋友可以参考下 zabbix部署文档 zabbix部署完之后 zabbix-agent...
 2023年4月15日 21:17

CVE-2021-24219: All Thrive Themes and Plugins – Unauthenticated Option Update
漏洞标题 CVE-2021-24219: All Thrive Themes and Plugins - Unauthenticated Option Update 漏洞描述 The Thrive Optimize WordPress plugin before 1.4.13.3, Thrive Comments WordPress plug...
2021年6月16日 12:13CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal
漏洞标题 CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal 漏洞描述 spring-boot-actuator-logview before version 0.2.13 contains a directory traversal vulnerability i...
2021年10月25日 23:32
每日云安全技术资讯20220223
容器环境红队手法总结 http://mp.weixin.qq.com/s/WaRECg79Nxx08iekakrlMA 如何使用 Kubesploit 和 KubiScan 提高云原生安全性 http://www.conjur.org/blog/tutorial-kubernetes-vulnerability-...
2022年3月10日 23:32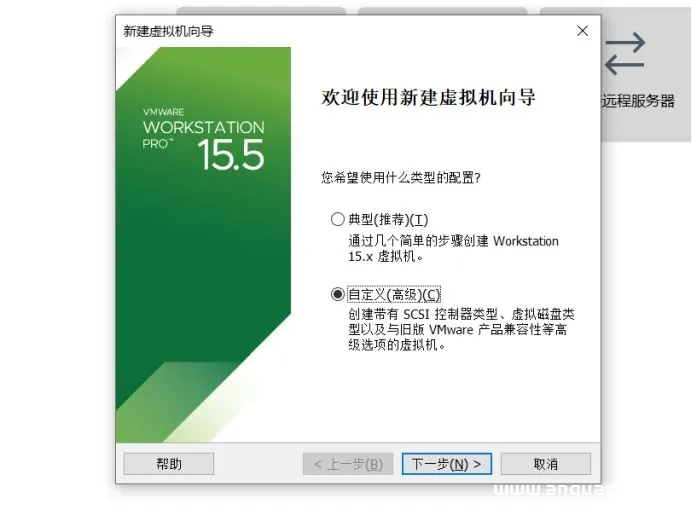
在VMware上 安装 centos8的详细教程_VMware
这篇文章主要介绍了VMware 安装 centos8的详细教程,本文图文并茂给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 centos官网地址 http://www.centos.org/ 首先下载好自己...
2026年5月31日 11:45CVE-2024-48248: NAKIVO Backup and Replication Solution – Unauthenticated Arbitrary File Read
漏洞标题 CVE-2024-48248: NAKIVO Backup and Replication Solution - Unauthenticated Arbitrary File Read 漏洞描述 NAKIVO Backup & Replication is a data protection solution used fo...
2024年2月12日 18:37
引领全球网安生态共享新模式,ISC2022《我要上ISC》议题征集全球启动!
3月29日,ISC 2022议题征集通道正式开启。本届大会以网安生态共享共建的全新模式,面向全球召集网络安全Speaker,致力构建全球网络安全的“智汇”高地。 作为一年一度的全球性安全峰会,...
2022年3月30日 14:54CVE-2023-41109: SmartNode SN200 Analog Telephone Adapter (ATA) & VoIP Gateway – Command Injection
漏洞标题 CVE-2023-41109: SmartNode SN200 Analog Telephone Adapter (ATA) & VoIP Gateway - Command Injection 漏洞描述 The SmartNode SN200 Analog Telephone Adapter (ATA) & VoI...
2023年8月15日 11:39CVE-2021-30461: VoipMonitor <24.61 - Remote Code Execution
漏洞标题 CVE-2021-30461: VoipMonitor <24.61 - Remote Code Execution 漏洞描述 VoipMonitor prior to 24.61 is susceptible to remote code execution vulnerabilities because of its us...
2021年6月5日 04:53
年仅16岁,攻击微软、三星、英伟达的幕后主使浮出水面
Lapsus$是一个近来异常活跃的黑客组织,主要事迹有窃取并泄露英伟达、三星、微软、Okta等科技巨头的源代码和专有数据,此外受害者还有游戏开发商育碧Ubisoft,电信公司Vodafone和电子商务巨头Me...
2022年3月27日 14:55CVE-2023-39650: PrestaShop Theme Volty CMS Blog – SQL Injection
漏洞标题 CVE-2023-39650: PrestaShop Theme Volty CMS Blog - SQL Injection 漏洞描述 In the module 'Theme Volty CMS Blog' (tvcmsblog) up to versions 4.0.1 from Theme Volty f...
2023年5月18日 02:18CVE-2022-48253: Nostromo nhttpd path traversal
漏洞标题 CVE-2022-48253: Nostromo nhttpd path traversal 漏洞描述 nhttpd in Nostromo before 2.1 is vulnerable to a path traversal that may allow an attacker to execute arbitrary com...
2022年9月20日 19:09CVE-2020-5515: Gila CMS 1.11.8 SQL Injection.
漏洞标题 CVE-2020-5515: Gila CMS 1.11.8 SQL Injection. 漏洞描述 Gila CMS 1.11.8 SQL Injection. fofa: "Gila CMS" PoC代码
2020年9月18日 16:27CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
2023年8月21日 10:28CVE-2010-1980: Joomla! Component Joomla! Flickr 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1980: Joomla! Component Joomla! Flickr 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in joomlaflickr.php in the Joomla! Flickr (com_joom...
2010年5月23日 13:36CVE-2022-32772: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32772: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
2022年9月11日 05:05
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

