
最新发布第890页

CVE-2013-3526: WordPress Plugin Traffic Analyzer – ‘aoid’ Cross-Site Scripting
漏洞标题 CVE-2013-3526: WordPress Plugin Traffic Analyzer - 'aoid' Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in js/ta_loaded.js.php in the Traffi...
 2013年6月5日 10:09
CVE-2022-2486: Wavlink WN535K2/WN535K3 – OS Command Injection
漏洞标题 CVE-2022-2486: Wavlink WN535K2/WN535K3 - OS Command Injection 漏洞描述 Wavlink WN535K2 and WN535K3 routers are susceptible to OS command injection in an unknown part of th...
2022年4月29日 16:32CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the key and redi...
2025年7月31日 14:20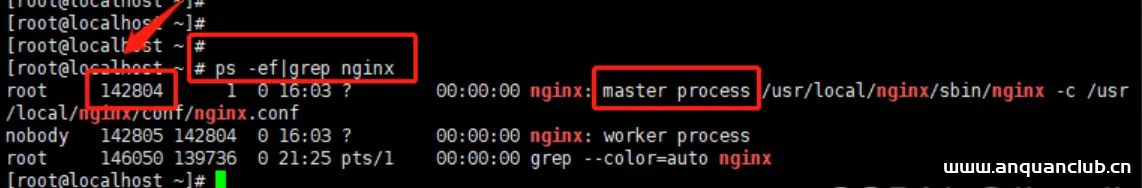
Linux中nginx如何重启、启动与停止/设置开机自启动
解决nginx报错: [warn] conflicting server name “localhost“ on 0.0.0.0:80, ignored 一、启动 /usr/local/nginx/sbin/nginx -c /usr/local/nginx/conf/nginx.conf 启动代码格式:nginx安装...

 2023年1月13日 19:45
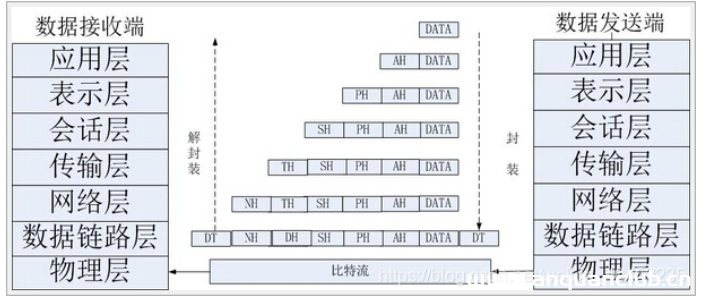
一文教你怎么搞定流量包(二)
前言 承接第一篇CTF流量分析,中间涉及部分知识内容,顺便自己再熟悉一遍,常规CTF或者说工控流量分析用到的工具wireshark之外似乎不怎涉及,,, 协议 TCP协议 TCP(Transmission Control Proto...
2022年3月10日 23:39CVE-2017-17731: DedeCMS 5.7 – SQL Injection
漏洞标题 CVE-2017-17731: DedeCMS 5.7 - SQL Injection 漏洞描述 DedeCMS through 5.7 has SQL Injection via the $_FILES superglobal to plus/recommend.php. PoC代码
2017年6月24日 12:39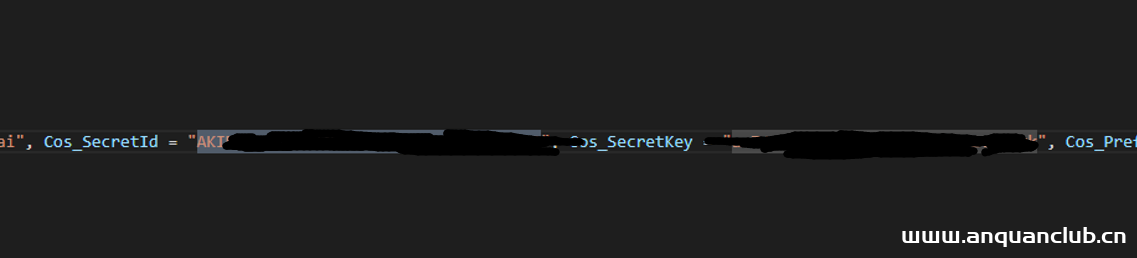
某鹅一次AK /SK 泄露导致拿下存储桶
第一次写文章师傅们 轻喷~ 起因 大二学生上课摸鱼,然后正常在测一些东西,emm 偶然在前端发现 发现了 AK 等字样~ 心里窃喜 洞要来了 ? !! 直接用现成的工具 就好 然后进一步利用的话 可以做...
2022年3月10日 23:37CVE-2024-0305: Ncast busiFacade – Remote Command Execution
漏洞标题 CVE-2024-0305: Ncast busiFacade - Remote Command Execution 漏洞描述 The Ncast Yingshi high-definition intelligent recording and playback system is a newly developed audio ...
2024年10月9日 05:06CVE-2021-30128: Apache OFBiz <17.12.07 - Arbitrary Code Execution
漏洞标题 CVE-2021-30128: Apache OFBiz <17.12.07 - Arbitrary Code Execution 漏洞描述 Apache OFBiz before 17.12.07 is susceptible to arbitrary code execution via unsafe deserializ...
2021年11月30日 00:12CVE-2018-10956: IPConfigure Orchid Core VMS 2.0.5 – Local File Inclusion
漏洞标题 CVE-2018-10956: IPConfigure Orchid Core VMS 2.0.5 - Local File Inclusion 漏洞描述 IPConfigure Orchid Core VMS 2.0.5 is susceptible to local file inclusion. PoC代码
2018年10月29日 17:49CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape
漏洞标题 CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow...
2025年6月11日 15:25CVE-2021-21972: VMware vSphere Client (HTML5) – Remote Code Execution
漏洞标题 CVE-2021-21972: VMware vSphere Client (HTML5) - Remote Code Execution 漏洞描述 VMware vCenter vSphere Client (HTML5) contains a remote code execution vulnerability in a vC...
2021年4月6日 12:33CVE-2015-1880: Fortinet FortiOS <=5.2.3 - Cross-Site Scripting
漏洞标题 CVE-2015-1880: Fortinet FortiOS <=5.2.3 - Cross-Site Scripting 漏洞描述 Fortinet FortiOS 5.2.x before 5.2.3 contains a cross-site scripting vulnerability in the SSL VPN...
2015年12月21日 19:26CVE-2022-44951: Rukovoditel <= 3.2.1 - Cross Site Scripting
漏洞标题 CVE-2022-44951: Rukovoditel <= 3.2.1 - Cross Site Scripting 漏洞描述 Rukovoditel v3.2.1 was discovered to contain a stored cross-site scripting (XSS) vulnerability in t...
2022年9月19日 18:09CVE-2024-0692: SolarWinds Security Event Manager – Unauthenticated RCE
漏洞标题 CVE-2024-0692: SolarWinds Security Event Manager - Unauthenticated RCE 漏洞描述 The SolarWinds Security Event Manager was susceptible to Remote Code Execution Vulnerabilit...
2024年8月15日 16:44CVE-2022-23131: Zabbix – SAML SSO Authentication Bypass
漏洞标题 CVE-2022-23131: Zabbix - SAML SSO Authentication Bypass 漏洞描述 When SAML SSO authentication is enabled (non-default), session data can be modified by a malicious actor b...
2022年1月1日 05:52
2026年9月17日 11:45
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

