
最新发布第892页
漏洞分类及安全防护 – hvv面试题
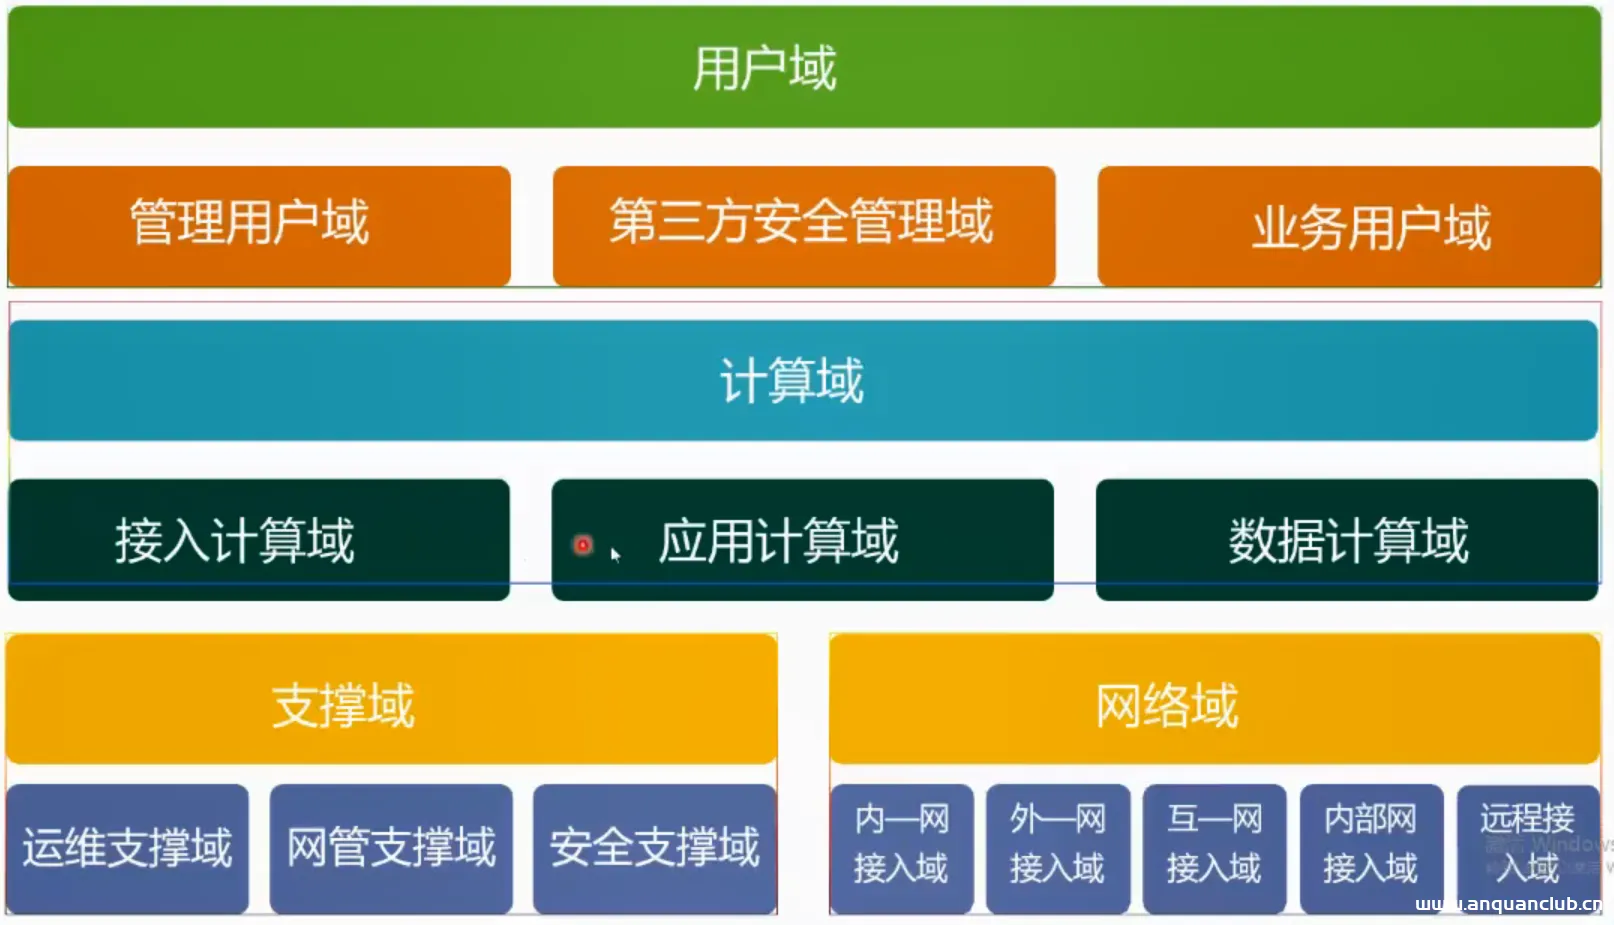
常见漏洞分类 CNNVD漏洞分类 漏洞分类 依据国标信息安全技术-安全漏洞分类标准,按照形成原因、所处空间和时间特征进行分类。 其他漏洞分类 操作系统漏洞-远程代码执行漏洞(MS17-010)加固方案 ...

 2022年6月30日 18:26

CVE-2024-38353: CodiMD <2.5.4 - Insecure Filename Randomization
漏洞标题 CVE-2024-38353: CodiMD <2.5.4 - Insecure Filename Randomization 漏洞描述 CodiMD does not require valid authentication to access uploaded images or to upload new image d...
 2024年7月11日 13:54
CVE-2020-15500: TileServer GL <=3.0.0 - Cross-Site Scripting
漏洞标题 CVE-2020-15500: TileServer GL <=3.0.0 - Cross-Site Scripting 漏洞描述 TileServer GL through 3.0.0 is vulnerable to reflected cross-site scripting via server.js because ...
2020年8月25日 18:29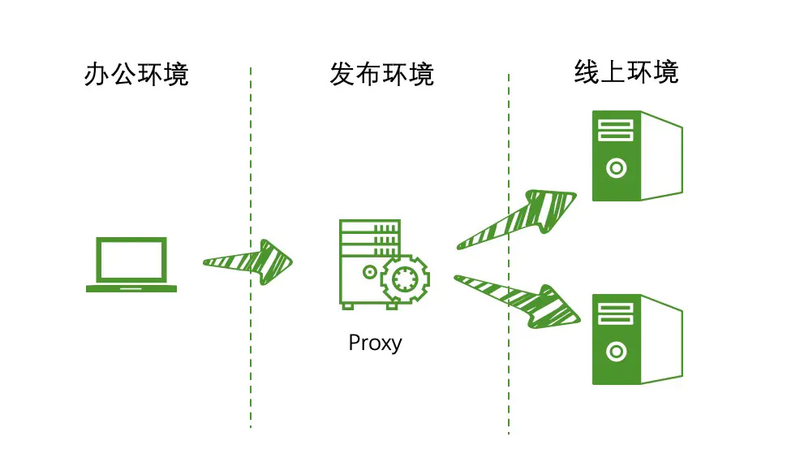
通过Nginx解决网络隔离实践记录详解_nginx
这篇文章主要介绍了通过Nginx解决网络隔离实践记录详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 需求 最近...
2024年1月29日 20:40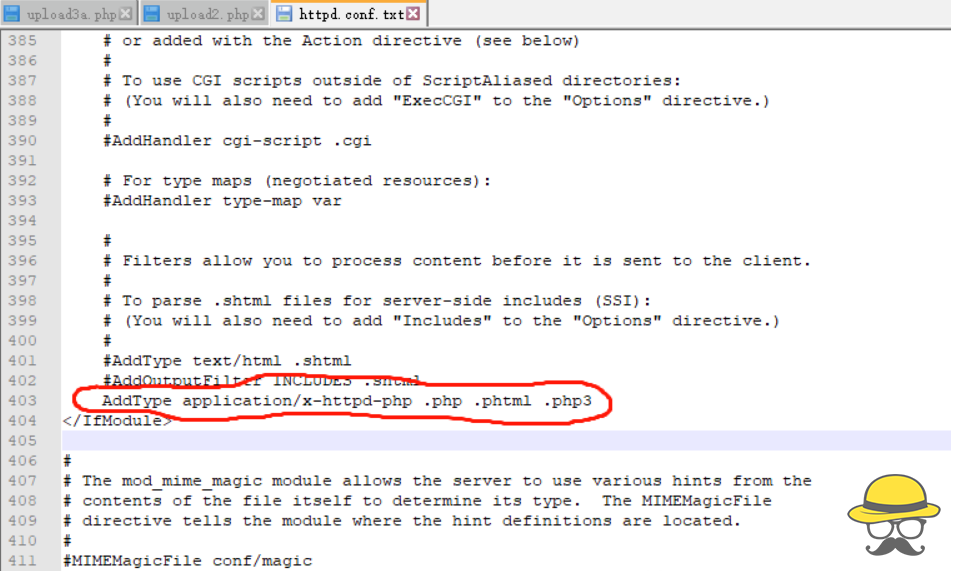
【网安笔记】文件上传漏洞总结
上传文件的时,如果未对上传的文件进行严格的验证和过滤,就容易造成文件上传漏洞,上传脚本等。 造成的危害 导致网站甚至整个服务器被控制,恶意的脚本文件又称为WebShell,WebShell具有强大的...
2022年2月28日 17:50CVE-2021-3110: PrestaShop 1.7.7.0 – SQL Injection
漏洞标题 CVE-2021-3110: PrestaShop 1.7.7.0 - SQL Injection 漏洞描述 PrestaShop 1.7.7.0 contains a SQL injection vulnerability via the store system. It allows time-based boolean SQL...
2021年12月3日 13:49CVE-2018-6910: DedeCMS 5.7 – Path Disclosure
漏洞标题 CVE-2018-6910: DedeCMS 5.7 - Path Disclosure 漏洞描述 DedeCMS 5.7 allows remote attackers to discover the full path via a direct request for include/downmix.inc.php or inc...
2018年10月18日 08:30CVE-2012-4273: 2 Click Socialmedia Buttons < 0.34 - Cross-Site Scripting
漏洞标题 CVE-2012-4273: 2 Click Socialmedia Buttons < 0.34 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in libs/xing.php in the 2 Click Social Media Butt...
2012年10月11日 23:47CVE-2025-2075: Uncanny Automator <= 6.3.0.2 - Missing Authorization to Authenticated (Subscriber+) Privilege Escalation
漏洞标题 CVE-2025-2075: Uncanny Automator <= 6.3.0.2 - Missing Authorization to Authenticated (Subscriber+) Privilege Escalation 漏洞描述 The Uncanny Automator - Easy Automation...
2025年4月8日 13:20BigAnt Server 任意文件下载(CVE-2022-23347)
漏洞标题 BigAnt Server 任意文件下载(CVE-2022-23347) 漏洞描述 BigAnt具有自主知识产权的大蚂蚁企业级即时通讯软件则是为政府、企业的实时安全通信打造的私有云即时通讯产品。存在任意文件下...
2022年6月24日 23:27CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting
漏洞标题 CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting 漏洞描述 Advanced Custom Fields beofre 6.1.6 is susceptible to cross-site scripting via the post_s...
2023年11月3日 18:14CVE-2023-25573: Metersphere – Arbitrary File Read
漏洞标题 CVE-2023-25573: Metersphere - Arbitrary File Read 漏洞描述 Metersphere is an open source continuous testing platform. In affected versions an improper access control vulne...
2023年3月28日 13:03
记一次某事业单位的二杀
记一次某事业单位的二杀作者:用户iT40DJEXyzhttps://xz.aliyun.com/news/91912文章转载自 先知社区 思路总结:找到同一个子域名的其他网站 把存在弱口令登录成功的响应包复制 然后替换给目标网...
2026年4月24日 17:11CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting
漏洞标题 CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting 漏洞描述 The Store Locator WordPress plugin before 1.4.13 does not sanitise and escape an invalid...
2023年8月9日 13:05CVE-2022-2373: WordPress Simply Schedule Appointments <1.5.7.7 - Information Disclosure
漏洞标题 CVE-2022-2373: WordPress Simply Schedule Appointments <1.5.7.7 - Information Disclosure 漏洞描述 WordPress Simply Schedule Appointments plugin before 1.5.7.7 is suscept...
2022年7月26日 07:03CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年5月3日 17:41
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

