
最新发布第894页
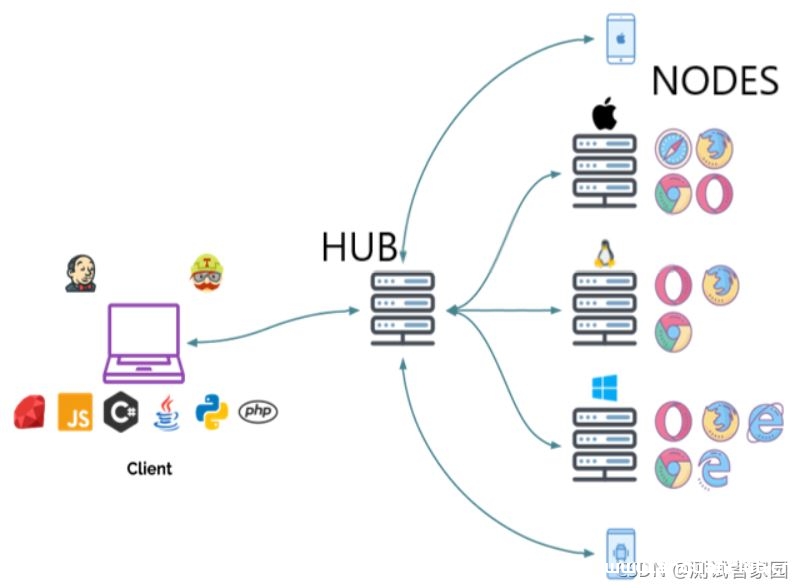
基于Docker+Selenium Grid的测试技术应用示例代码_docker
Selenium Grid允许我们在多台计算机上并行运行测试,并集中管理不同的浏览器版本和浏览器配置。这篇文章给大家介绍基于Docker+Selenium Grid的测试技术应用示例代码,需要的朋友参考下吧 Seleni...
 2022年6月15日 22:43

Linux修改主机名命令详解_Linux
在本篇文章里小编给大家整理的关于Linux修改主机名命令的知识点详解,有兴趣的朋友可以参考学习下。 Linux修改主机名命令 1、如果只需要临时更改主机名,可以使用hostname命令。 sudo hostname ...
2024年5月24日 20:45
CVE-2010-1302: Joomla! Component DW Graph – Local File Inclusion
漏洞标题 CVE-2010-1302: Joomla! Component DW Graph - Local File Inclusion 漏洞描述 A directory traversal vulnerability in dwgraphs.php in the DecryptWeb DW Graphs (com_dwgraphs) co...
2010年12月20日 02:18
Linux系统(CentOS7安装)安装JDK8的教程详解_Linux
这篇文章主要介绍了Linux系统(CentOS7安装)安装JDK8的教程,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 JDK 的安装 系统安装就不做过多介绍,大家从网上寻找安装...
2024年6月8日 20:25CVE-2018-13379: Fortinet FortiOS – Credentials Disclosure
漏洞标题 CVE-2018-13379: Fortinet FortiOS - Credentials Disclosure 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.3 to 5.6.7 and 5.4.6 to 5.4.12 and FortiProxy 2.0.0, 1.2.0 to 1.2.8...
2018年8月6日 22:34Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556)
漏洞标题 Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556) 漏洞描述 在Struts2 WebWork 2.1+ 和 Struts 2 的“altSyntax”功能允许将 OGNL表达式插入到文本字符串中并进行递归处理。这...
2007年12月26日 08:50(CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞
漏洞标题 (CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞 漏洞描述 (CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞 PoC代码 暂无
2010年8月6日 04:55CVE-2020-14144: Gitea 1.1.0 – 1.12.5 – Remote Code Execution
漏洞标题 CVE-2020-14144: Gitea 1.1.0 - 1.12.5 - Remote Code Execution 漏洞描述 Gitea 1.1.0 through 1.12.5 is susceptible to authenticated remote code execution, via the git hook fu...
2020年6月18日 18:25CVE-2025-53558: ZTE ZXHN-F660T/F660A – Default Credentials
漏洞标题 CVE-2025-53558: ZTE ZXHN-F660T/F660A - Default Credentials 漏洞描述 ZXHN-F660T and ZXHN-F660A provided by ZTE Japan K.K. use a common credential for all installations. Wit...
2025年5月22日 23:01CVE-2023-6977: Mlflow <2.8.0 - Local File Inclusion
漏洞标题 CVE-2023-6977: Mlflow <2.8.0 - Local File Inclusion 漏洞描述 Mlflow before 2.8.0 is susceptible to local file inclusion due to path traversal in GitHub repository mlflo...
2023年1月29日 02:23CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting 漏洞描述 WordPress Advanced Order Export For WooCommerce plu...
2021年11月16日 20:10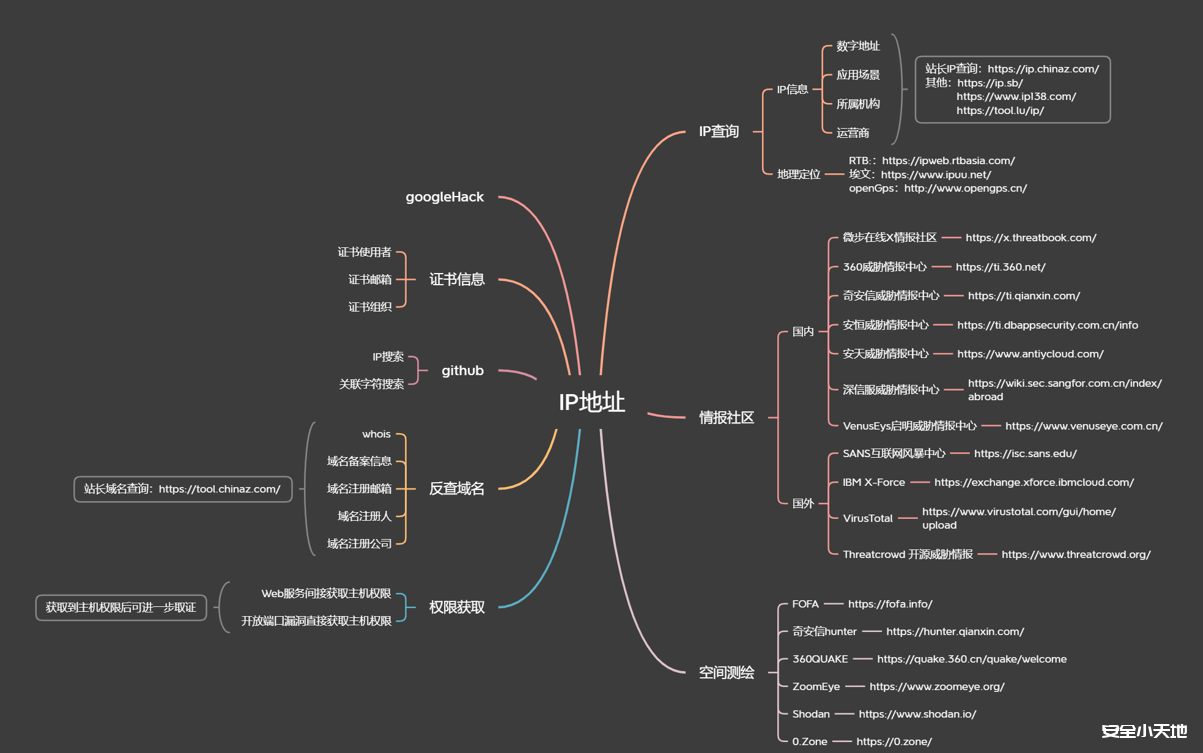
攻防演练中如何从单一IP进行最大限度溯源
前言 随着网络安全的不断演变,现在攻击方和防守方的手法都愈加复杂,对于攻击方来说,代理池、vps已经是入门级操作。但是对于蓝队而言,相信师傅们一定遇到过只捕获到一个攻击IP并需要对其溯源...

 2023年8月18日 15:39
CVE-2023-4911: Looney Tunables Linux – Local Privilege Escalation
漏洞标题 CVE-2023-4911: Looney Tunables Linux - Local Privilege Escalation 漏洞描述 A buffer overflow was discovered in the GNU C Library's dynamic loader ld.so while processi...
2023年2月11日 08:17Aviatrix Controller 6.x 任意文件上传(CVE-2021-40870)
漏洞标题 Aviatrix Controller 6.x 任意文件上传(CVE-2021-40870) 漏洞描述 Aviatrix Controller是一个集中控制面板,用于编排和管理各种网络和连接解决方案。在 6.5-1804.1922 之前的 Aviatrix...
2021年10月26日 02:15CVE-2022-26138: Atlassian Questions For Confluence – Hardcoded Credentials
漏洞标题 CVE-2022-26138: Atlassian Questions For Confluence - Hardcoded Credentials 漏洞描述 Atlassian Questions For Confluence contains a hardcoded credentials vulnerability. When...
2022年3月23日 11:50
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

