
最新发布第906页
Ubuntu编译内核模块,内容体现系统日志中_Linux
目录1.Linux登陆界面2.编写代码3.编写Makefile文件4.编译:5.插入模块6.查看日志输出1.Linux登陆界面 1.检查当前文件目录: 通过Xshell连接Linux系统后 输入命令:ls 2. 新建code/kernel文件夹 2....
 2022年6月15日 08:45

CVE-2025-12139: Integrate Google Drive <= 1.5.3 - Information Disclosure
漏洞标题 CVE-2025-12139: Integrate Google Drive <= 1.5.3 - Information Disclosure 漏洞描述 File Manager for Google Drive - Integrate Google Drive with WordPress plugin for WordP...
2025年11月8日 09:56
bugbounty技巧聚合20210811
漏洞报告 HackerOne #1256371 PII data Leakage through hackerone reports #1145563 Tab nabbing in Hackerone inbox. Basecamp #1288898 Password reset link not expiring after changing pa...
2022年4月1日 18:36CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
2020年9月17日 10:20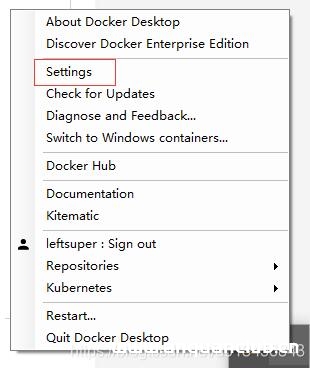
docker 设置windows存储路径的操作_docker
这篇文章主要介绍了docker 设置windows存储路径的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 在win10下安装docker时,选择container类型为Linux container之后,设...
2022年8月1日 21:13CVE-2020-36289: Jira Server and Data Center – Information Disclosure
漏洞标题 CVE-2020-36289: Jira Server and Data Center - Information Disclosure 漏洞描述 Jira Server and Data Center is susceptible to information disclosure. An attacker can enumera...
2020年6月23日 10:18CVE-2022-4447: WordPress Fontsy <=1.8.6 - SQL Injection
漏洞标题 CVE-2022-4447: WordPress Fontsy <=1.8.6 - SQL Injection 漏洞描述 WordPress Fontsy plugin through 1.8.6 is susceptible to SQL injection. The plugin does not properly san...
2022年8月2日 20:09CVE-2010-1475: Joomla! Component Preventive And Reservation 1.0.5 – Local File Inclusion
漏洞标题 CVE-2010-1475: Joomla! Component Preventive And Reservation 1.0.5 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Preventive & Reservation (...
2010年3月25日 01:48CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection
漏洞标题 CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection 漏洞描述 Agentejo Cockpit prior to 0.12.0 is vulnerable to NoSQL Injection via the newpassword method of the ...
2020年8月3日 14:04
-Struts2-015 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-Struts2-015 远程命令执行漏洞 Struts是Apache软件基金会(ASF)赞助的一个开源项目。它最初是Jakarta项目中的一个子项目,并在2004...

 2023年2月4日 14:54
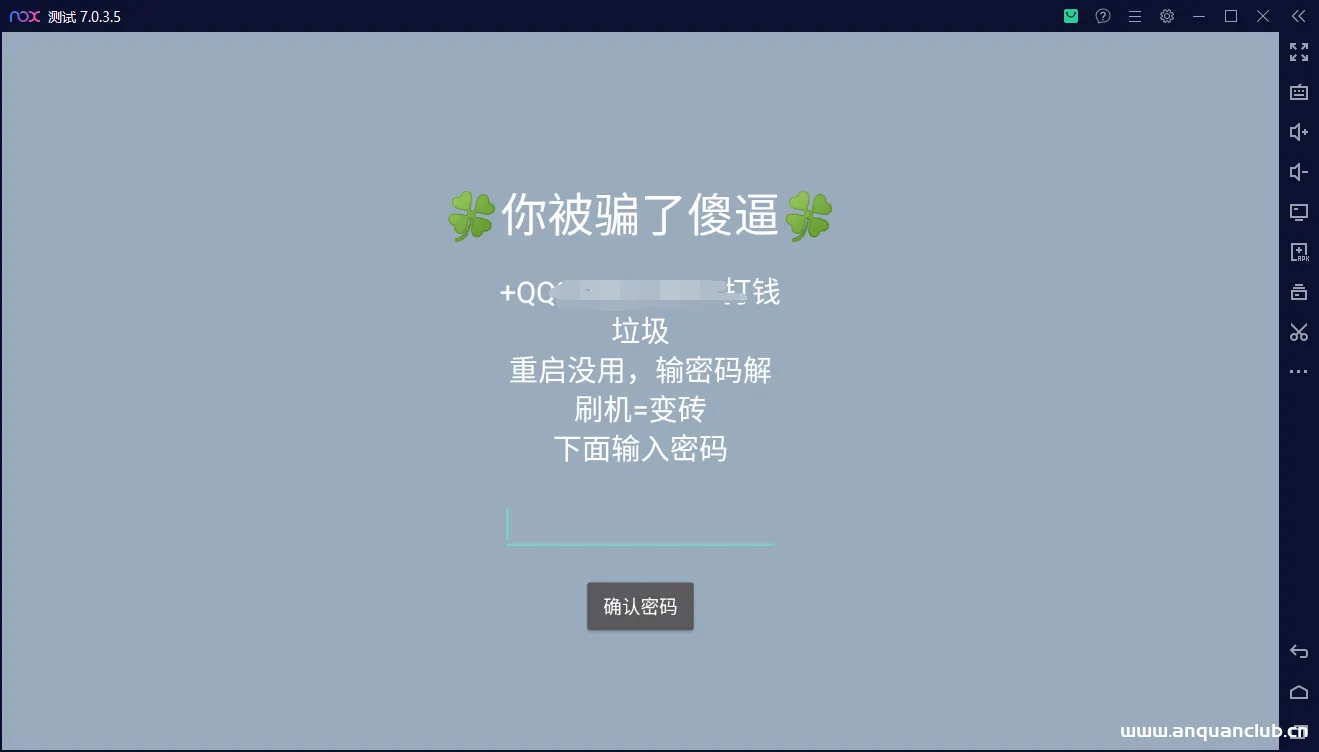
记一次违规锁机APP的渗透测试
0x00前言 今天闲着无聊,发呆时间,好兄弟突然发来一张锁机图片,乍一想锁机这玩意还是咱初中那段时间火啊。因为隐私问题,这里就直接放模拟器运行图片 那些莫名其妙的小软件,大家懂得都懂,都...
2023年1月13日 19:28CVE-2019-7276: Optergy Proton/Enterprise – Unauthenticated RCE via Backdoor Console
漏洞标题 CVE-2019-7276: Optergy Proton/Enterprise - Unauthenticated RCE via Backdoor Console 漏洞描述 Optergy Proton/Enterprise devices allow Remote Root Code Execution via a Backd...
2019年6月27日 13:27
在centos7上搭建mysql主从服务器的方法(图文教程)_Linux
这篇文章主要介绍了在centos7上搭建mysql主从服务器的方法,本文通过图文并茂的形式给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 本文主要是介绍在centos上搭建mysql的...
2026年8月25日 11:45CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
2019年8月19日 11:11CVE-2019-18393: Ignite Realtime Openfire <4.42 - Local File Inclusion
漏洞标题 CVE-2019-18393: Ignite Realtime Openfire <4.42 - Local File Inclusion 漏洞描述 Ignite Realtime Openfire through 4.4.2 is vulnerable to local file inclusion via PluginSe...
2019年10月18日 07:57Artica Pandora FMS未授权访问(CVE-2020-8497)
漏洞标题 Artica Pandora FMS未授权访问(CVE-2020-8497) 漏洞描述 Artica Pandora FMS是西班牙Artica公司的一套监控系统,在 Artica Pandora FMS 到 7.42中,未经身份验证的攻击者可以读取聊天...
2020年7月18日 05:17
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

