
最新发布第907页

CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
 2022年12月8日 07:56
CVE-2022-31101: Prestashop Blockwishlist 2.1.0 SQL Injection
漏洞标题 CVE-2022-31101: Prestashop Blockwishlist 2.1.0 SQL Injection 漏洞描述 Prestashop Blockwishlist module version 2.1.0 suffers from a remote authenticated SQL injection vulne...
2022年4月24日 01:43CVE-2023-3380: WAVLINK WN579X3 – Remote Command Execution
漏洞标题 CVE-2023-3380: WAVLINK WN579X3 - Remote Command Execution 漏洞描述 Remote Command Execution vulnerability in WAVLINK WN579X3 routers via pingIp parameter in /cgi-bin/adm.c...
2023年4月11日 16:24CVE-2010-0157: Joomla! Component com_biblestudy – Local File Inclusion
漏洞标题 CVE-2010-0157: Joomla! Component com_biblestudy - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Bible Study (com_biblestudy) component 6.1 for J...
2010年5月29日 15:52CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery
漏洞标题 CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery 漏洞描述 WordPress PhonePe Payment Solutions plugin through 1.0.15 is suscept...
2022年6月23日 16:41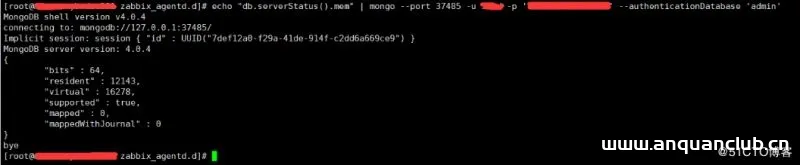
Zabbix3.4监控mongodb数据库状态的方法_zabbix
mongodb有db.serverStatus()命令,可以查看mongodb的运行状态,那么zabbix就可以调用这个命令实现mongodb的监控。这篇文章主要介绍了Zabbix3.4监控mongodb状态的方法,需要的朋友可以参考下 mong...
2026年4月17日 11:46CVE-2023-27637: PrestaShop `tshirtecommerce` Module – SQL Injection
漏洞标题 CVE-2023-27637: PrestaShop `tshirtecommerce` Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via t...
2023年2月6日 05:06CVE-2023-1454: Jeecg-boot 3.5.0 qurestSql – SQL Injection
漏洞标题 CVE-2023-1454: Jeecg-boot 3.5.0 qurestSql - SQL Injection 漏洞描述 A vulnerability classified as critical has been found in jeecg-boot 3.5.0. This affects an unknown part ...
2023年12月9日 22:51CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway – Remote Code Injection
漏洞标题 CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway - Remote Code Injection 漏洞描述 Citrix ADC and NetScaler Gateway are susceptible to remote code injection. An attac...
2020年9月27日 22:51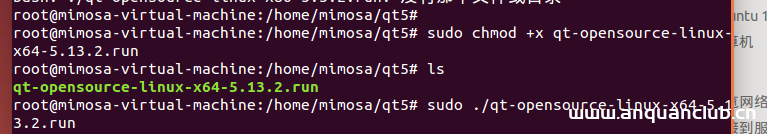
Ubuntu14.04安装、配置与卸载QT5的步骤详解_Linux
这篇文章主要介绍了Ubuntu14.04安装、配置与卸载QT5详细步骤,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1.之前我下载的是...
2023年12月22日 21:08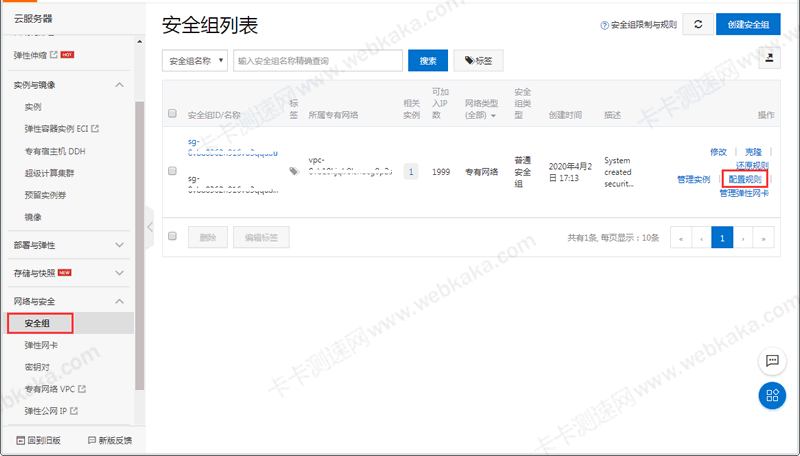
阿里云主机不能用IP访问网站的解决方法(配置安全组规则搞定)_服务器其它
刚买了一台阿里云主机,迫不待及的试试速度,怎知网站访问不了,用IP或绑定域名都无法访问,后来提交工单才知道,需要配置安全组规则才行。针对同样像我一样的新手,本文就介绍一下如何在开通阿...
2023年10月30日 21:05CVE-2023-3578: DedeCMS 5.7.109 – Server-Side Request Forgery
漏洞标题 CVE-2023-3578: DedeCMS 5.7.109 - Server-Side Request Forgery 漏洞描述 Manipulation of the rssurl parameter in co_do.php leads to server-side request forgery in DedeCMS ver...
2023年7月1日 08:46CVE-2024-0305: Ncast busiFacade – Remote Command Execution
漏洞标题 CVE-2024-0305: Ncast busiFacade - Remote Command Execution 漏洞描述 The Ncast Yingshi high-definition intelligent recording and playback system is a newly developed audio ...
2024年9月9日 12:25
渗透测试小技巧之绕过“请在微信客户端打开链接”
前言 现在在渗透测试的过程中,针对微信公众号、微信小程序的测试变得越来越普遍。 但是某些网站限制只能在微信客户端中打开,不利于咱们进行测试,如何绕过“请在微信客户端打开链接”因此变得...

 2024年6月2日 22:40
CVE-2014-4558: WooCommerce Swipe <= 2.7.1 - Cross-Site Scripting
漏洞标题 CVE-2014-4558: WooCommerce Swipe <= 2.7.1 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in test-plugin.php in the Swipe Checkout for WooCommerce ...
2014年10月24日 04:57CVE-2009-0932: Horde/Horde Groupware – Local File Inclusion
漏洞标题 CVE-2009-0932: Horde/Horde Groupware - Local File Inclusion 漏洞描述 Horde before 3.2.4 and 3.3.3 and Horde Groupware before 1.1.5 are susceptible to local file inclusion ...
2009年9月26日 00:19
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

