
最新发布第915页

CVE-2019-6802: Pypiserver <1.2.5 - Carriage Return Line Feed Injection
漏洞标题 CVE-2019-6802: Pypiserver <1.2.5 - Carriage Return Line Feed Injection 漏洞描述 Pypiserver through 1.2.5 and below is susceptible to carriage return line feed injection...
 2019年8月8日 15:17

linux userdel 命令的使用_Linux
这篇文章主要介绍了linux userdel 命令的使用,帮助大家更好的理解和使用Linux系统,感兴趣的朋友可以了解下 1.命令简介 userdel(user delete) 命令是系统管理员命令,用于删除用户账户和相关...
2023年6月11日 21:52CVE-2025-27892: Shopware < 6.5.8.13 - SQL Injection
漏洞标题 CVE-2025-27892: Shopware < 6.5.8.13 - SQL Injection 漏洞描述 The Shopware application API contains a search functionality which enables users to search through informat...
2025年6月17日 23:23CVE-2020-35580: SearchBlox <9.2.2 - Local File Inclusion
漏洞标题 CVE-2020-35580: SearchBlox <9.2.2 - Local File Inclusion 漏洞描述 SearchBlox prior to version 9.2.2 is susceptible to local file inclusion in FileServlet that allows re...
2020年7月24日 04:08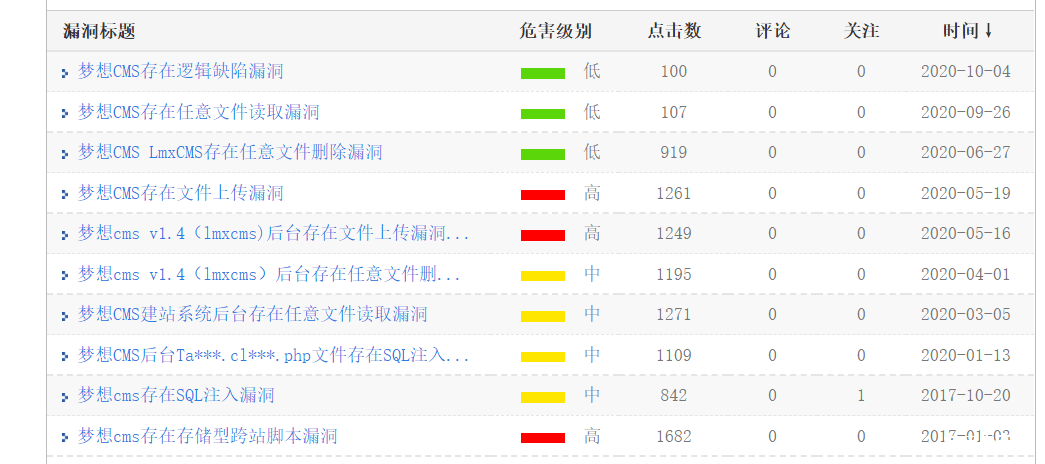
【CNVD-1day代码审计】 梦想CMS1.4代码审计学习
前言 每天学习一天,走大佬走过的路线,向大佬逐步靠近,虽然这个路程很难,同时有一大堆的问题让人劝退,坚持一点是一点吧。 介绍 梦想CMS简称“lmxcms”是一套开源的网站管理系统(cms),无...

 2023年6月3日 17:17
CVE-2015-9414: WordPress Symposium <=15.8.1 - Cross-Site Scripting
漏洞标题 CVE-2015-9414: WordPress Symposium <=15.8.1 - Cross-Site Scripting 漏洞描述 WordPress Symposium through 15.8.1 contains a reflected cross-site scripting vulnerability v...
2015年12月18日 18:23CVE-2022-1910: WordPress Shortcodes and Extra Features for Phlox <2.9.8 - Cross-Site Scripting
漏洞标题 CVE-2022-1910: WordPress Shortcodes and Extra Features for Phlox <2.9.8 - Cross-Site Scripting 漏洞描述 WordPress Shortcodes and extra features plugin for the Phlox the...
2022年1月19日 09:49CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年6月26日 06:25CVE-2024-32870: iTop Hub Connector – Information Disclosure
漏洞标题 CVE-2024-32870: iTop Hub Connector - Information Disclosure 漏洞描述 Combodo iTop is a simple, web based IT Service Management tool. Server, OS, DBMS, PHP, and iTop info (...
2024年11月7日 15:45CVE-2018-1273 Spring Data Commons 远程命令执行
漏洞标题 CVE-2018-1273 Spring Data Commons 远程命令执行 漏洞描述 Pivotal Spring Data Commons和Spring Data REST都是美国Pivotal Software公司的产品。PivotalSpring Data Commons是一个为...
2018年1月29日 01:28CVE-2017-15287: Dreambox WebControl 2.0.0 – Cross-Site Scripting
漏洞标题 CVE-2017-15287: Dreambox WebControl 2.0.0 - Cross-Site Scripting 漏洞描述 Dream Multimedia Dreambox devices via their WebControl component are vulnerable to reflected cros...
2017年7月30日 20:17CVE-2024-2473: WPS Hide Login <= 1.9.15.2 - Login Page Disclosure
漏洞标题 CVE-2024-2473: WPS Hide Login <= 1.9.15.2 - Login Page Disclosure 漏洞描述 The WPS Hide Login plugin for WordPress is vulnerable to Login Page Disclosure in all version...
2024年6月1日 01:26CVE-2024-33288: Prison Management System – SQL Injection Authentication Bypass
漏洞标题 CVE-2024-33288: Prison Management System - SQL Injection Authentication Bypass 漏洞描述 Sql injection vulnerability was found on the login page in Prison Management System...
2024年4月28日 10:58CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery
漏洞标题 CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery 漏洞描述 WordPress PhonePe Payment Solutions plugin through 1.0.15 is suscept...
2022年12月4日 04:22CVE-2017-9506: Atlassian Jira IconURIServlet – Cross-Site Scripting/Server-Side Request Forgery
漏洞标题 CVE-2017-9506: Atlassian Jira IconURIServlet - Cross-Site Scripting/Server-Side Request Forgery 漏洞描述 The Atlassian Jira IconUriServlet of the OAuth Plugin from version...
2017年2月4日 08:43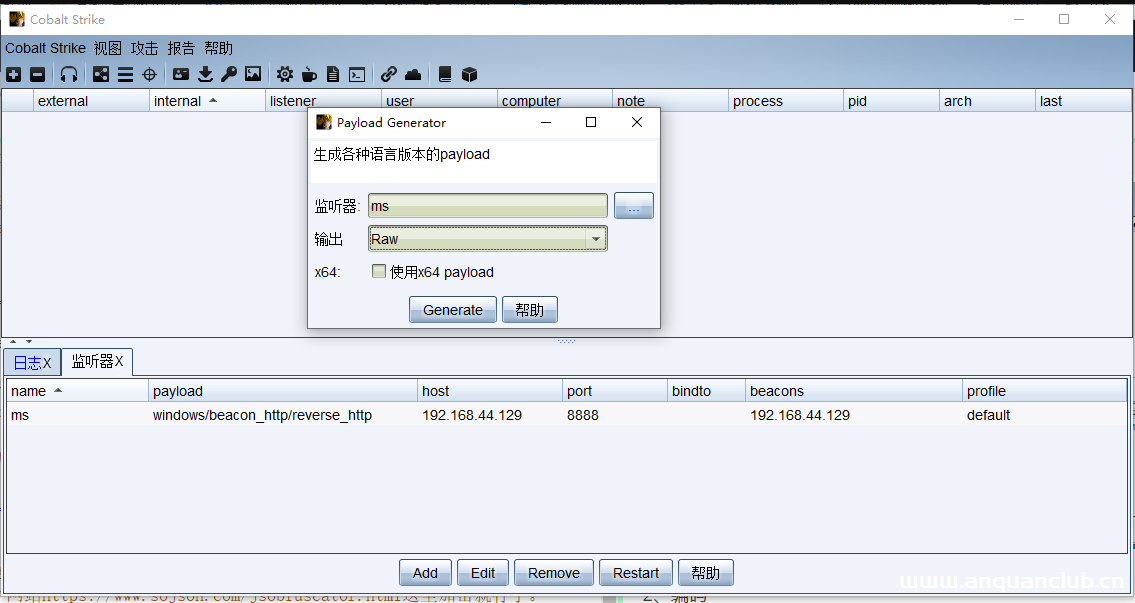
cobaltstrike免杀过360和火绒
在免杀之前需要自己处理一下cobaltstrike的相关特征,和更新一下证书。不然虽然文件免杀了,可是上线的时候会有特征,会被火绒拦截。 具体参考以下文章 http://www.wangan.com/articles/1144 ht...
2022年3月16日 09:16
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

