
最新发布第917页

CVE-2023-43261: Milesight Routers – Information Disclosure
漏洞标题 CVE-2023-43261: Milesight Routers - Information Disclosure 漏洞描述 A critical security vulnerability has been identified in Milesight Industrial Cellular Routers, comprom...
 2023年2月7日 04:27
CVE-2022-2034: WordPress Sensei LMS <4.5.0 - Information Disclosure
漏洞标题 CVE-2022-2034: WordPress Sensei LMS <4.5.0 - Information Disclosure 漏洞描述 WordPress Sensei LMS plugin before 4.5.0 is susceptible to information disclosure. The plug...
2022年1月5日 09:12CVE-2025-47539: Eventin <= 4.0.26 - Privilege Escalation
漏洞标题 CVE-2025-47539: Eventin <= 4.0.26 - Privilege Escalation 漏洞描述 The Eventin WordPress plugin before 4.0.27 suffers from an unauthenticated privilege escalation vulner...
2025年1月27日 19:04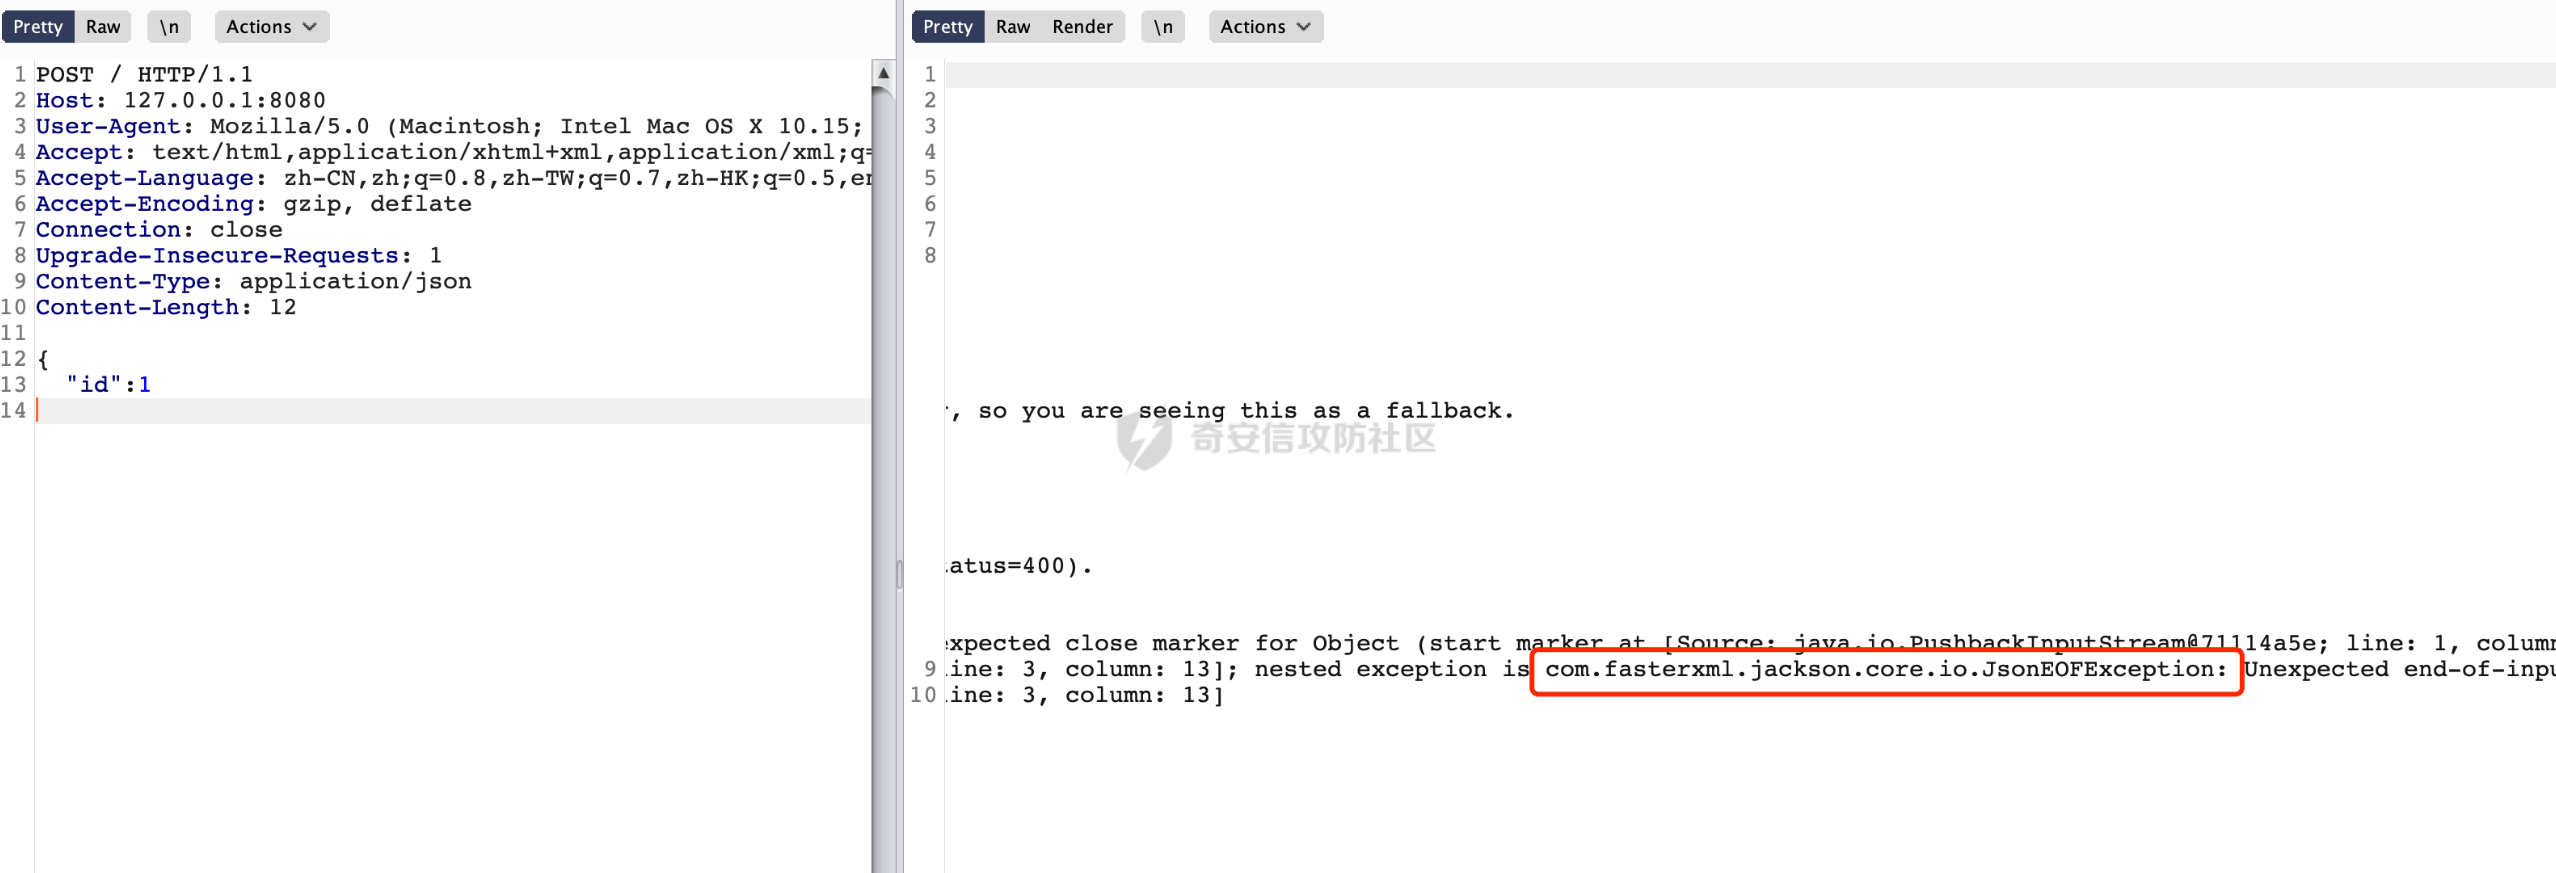
如何在渗透测试中区分Fastjson/Jackson
前言 关于对一个站点进行信息收集,能够尽最大程度收集到该站点的信息是最好,这样会极大的提高我们的渗透效率,今天我们来简单聊聊Fastjson/Jackson组件的区分。 最理想的情况 在最理想的情况...

 2023年10月28日 10:38
CVE-2006-2173: FileZilla FTP Server 2.2.22 – Buffer Overflow
漏洞标题 CVE-2006-2173: FileZilla FTP Server 2.2.22 - Buffer Overflow 漏洞描述 FileZilla FTP Server version 2.2.22 contains a buffer overflow vulnerability that allows remote authe...
2006年6月21日 12:33CVE-2018-1000130: Jolokia Agent – JNDI Code Injection
漏洞标题 CVE-2018-1000130: Jolokia Agent - JNDI Code Injection 漏洞描述 Jolokia agent is vulnerable to a JNDI injection vulnerability that allows a remote attacker to run arbitrary...
2018年3月14日 15:26CVE-2022-0140: WordPress Visual Form Builder <3.0.8 - Information Disclosure
漏洞标题 CVE-2022-0140: WordPress Visual Form Builder <3.0.8 - Information Disclosure 漏洞描述 WordPress Visual Form Builder plugin before 3.0.8 contains a information disclosur...
2022年11月7日 02:04CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 – Template Injection
漏洞标题 CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 - Template Injection 漏洞描述 Node.js Embedded JavaScript 3.1.6 is susceptible to server-side template injection via sett...
2022年6月18日 06:32CVE-2023-4415: Ruijie RG-EW1200G Router Background – Login Bypass
漏洞标题 CVE-2023-4415: Ruijie RG-EW1200G Router Background - Login Bypass 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 07161417 r483. It has been rated as critical. Aff...
2023年2月17日 02:23CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
2022年9月17日 03:12CVE-2020-7136: HPE Smart Update Manager < 8.5.6 - Remote Unauthorized Access
漏洞标题 CVE-2020-7136: HPE Smart Update Manager < 8.5.6 - Remote Unauthorized Access 漏洞描述 HPE Smart Update Manager (SUM) prior to version 8.5.6 could allow remote unauthori...
2020年7月4日 05:34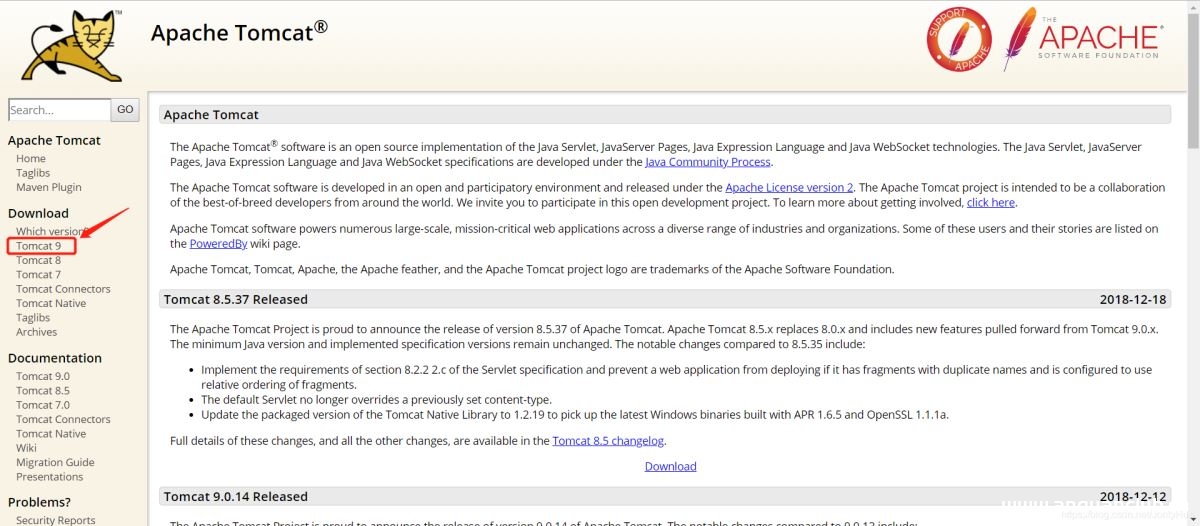
如何在IntelliJ IDEA 2018上配置Tomcat并运行第一个JavaWeb项目_Tomcat
这篇文章主要介绍了在IntelliJ IDEA 2018上配置Tomcat并运行第一个JavaWeb项目,需要的朋友可以参考下 1 下载和启动Tomcat 进入官网 http://tomcat.apache.org/ ,下载最新版本的Tomcat 9 根据自...
2023年5月24日 21:25CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation
漏洞标题 CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation 漏洞描述 The plugin is vulnerable to privilege escalation due...
2024年2月3日 19:50CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File
漏洞标题 CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File 漏洞描述 The Google for WooCommerce plugin for WordPress ...
2024年10月1日 01:05
记一次钓鱼网站的渗透记录 ——水文预告!!!
看之前请注意,这是一篇水文,无任何技术!! 记一次钓鱼网站的渗透记录,首先请出我们的主角:114.5x.1xx.xxx 看一下网站打开样子吧 中规中矩的页面,如果你看到这里,认为,这种钓鱼只要一看...
2023年1月13日 19:37CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection
漏洞标题 CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection 漏洞描述 WordPress Order Listener for WooCommerce plugin before 3.2.2 contains a SQL inje...
2022年1月3日 20:13
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

