
最新发布第934页

CVE-2021-25118: Yoast SEO 16.7-17.2 – Information Disclosure
漏洞标题 CVE-2021-25118: Yoast SEO 16.7-17.2 - Information Disclosure 漏洞描述 Yoast SEO plugin 16.7 to 17.2 is susceptible to information disclosure, The plugin discloses the full...
 2021年10月31日 19:24
CVE-2020-25506: D-Link DNS-320 – Unauthenticated Remote Code Execution
漏洞标题 CVE-2020-25506: D-Link DNS-320 - Unauthenticated Remote Code Execution 漏洞描述 D-Link DNS-320 FW v2.06B01 Revision Ax is susceptible to a command injection vulnerability ...
2020年9月16日 16:11CVE-2024-43919: YARPP <= 5.30.10 - Missing Authorization
漏洞标题 CVE-2024-43919: YARPP <= 5.30.10 - Missing Authorization 漏洞描述 The YARPP Yet Another Related Posts Plugin plugin for WordPress is vulnerable to unauthorized access d...
2024年2月27日 09:27CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload
漏洞标题 CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload 漏洞描述 Arbitrary File Upload vulnerability in WordPress Royal Elementor Addon...
2023年12月8日 07:43CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting
漏洞标题 CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting 漏洞描述 Adiscon LogAnalyzer before 4.1.7 contains a cross-site scripting vulnerability in the 'r...
2018年2月16日 00:46CVE-2025-53771: Microsoft SharePoint Server – Authentication Bypass (ToolShell)
漏洞标题 CVE-2025-53771: Microsoft SharePoint Server - Authentication Bypass (ToolShell) 漏洞描述 Microsoft Office SharePoint Server contains an improper authentication vulnerabili...
2025年7月31日 16:00CVE-2004-1641: Titan FTP ≤ 3.21 – Heap Overflow via Long Commands
漏洞标题 CVE-2004-1641: Titan FTP ≤ 3.21 - Heap Overflow via Long Commands 漏洞描述 Titan FTP versions ≤ 3.21 contain heap overflow vulnerabilities when processing long FTP comma...
2004年8月17日 15:09
2021年挖矿木马趋势报告
概述 2021年以来,我国加大了整治虚拟货币的力度,陆续出台了相关政策封杀虚拟货币交易平台,后续又发布了《关于整治虚拟货币“挖矿”活动》的通知,重点强调全面梳理排查虚拟货币“挖矿”项目...
2022年3月28日 08:53CVE-2024-13853: WordPress SEO Tools Plugin 4.0.7 – Cross-Site Scripting
漏洞标题 CVE-2024-13853: WordPress SEO Tools Plugin 4.0.7 - Cross-Site Scripting 漏洞描述 The SEO Tools WordPress plugin through version 4.0.7 contains a reflected cross-site scrip...
2024年9月14日 16:13CVE-2025-41243: Spring Cloud Gateway Server Webflux – Broken Access Control
漏洞标题 CVE-2025-41243: Spring Cloud Gateway Server Webflux - Broken Access Control 漏洞描述 Spring Cloud Gateway Server Webflux contains a vulnerability caused by unsecured and e...
2025年12月15日 15:39CVE-2018-17254: Joomla! JCK Editor SQL Injection
漏洞标题 CVE-2018-17254: Joomla! JCK Editor SQL Injection 漏洞描述 The JCK Editor component 6.4.4 for Joomla! allows SQL Injection via the jtreelink/dialogs/links.php parent parame...
2018年2月14日 15:09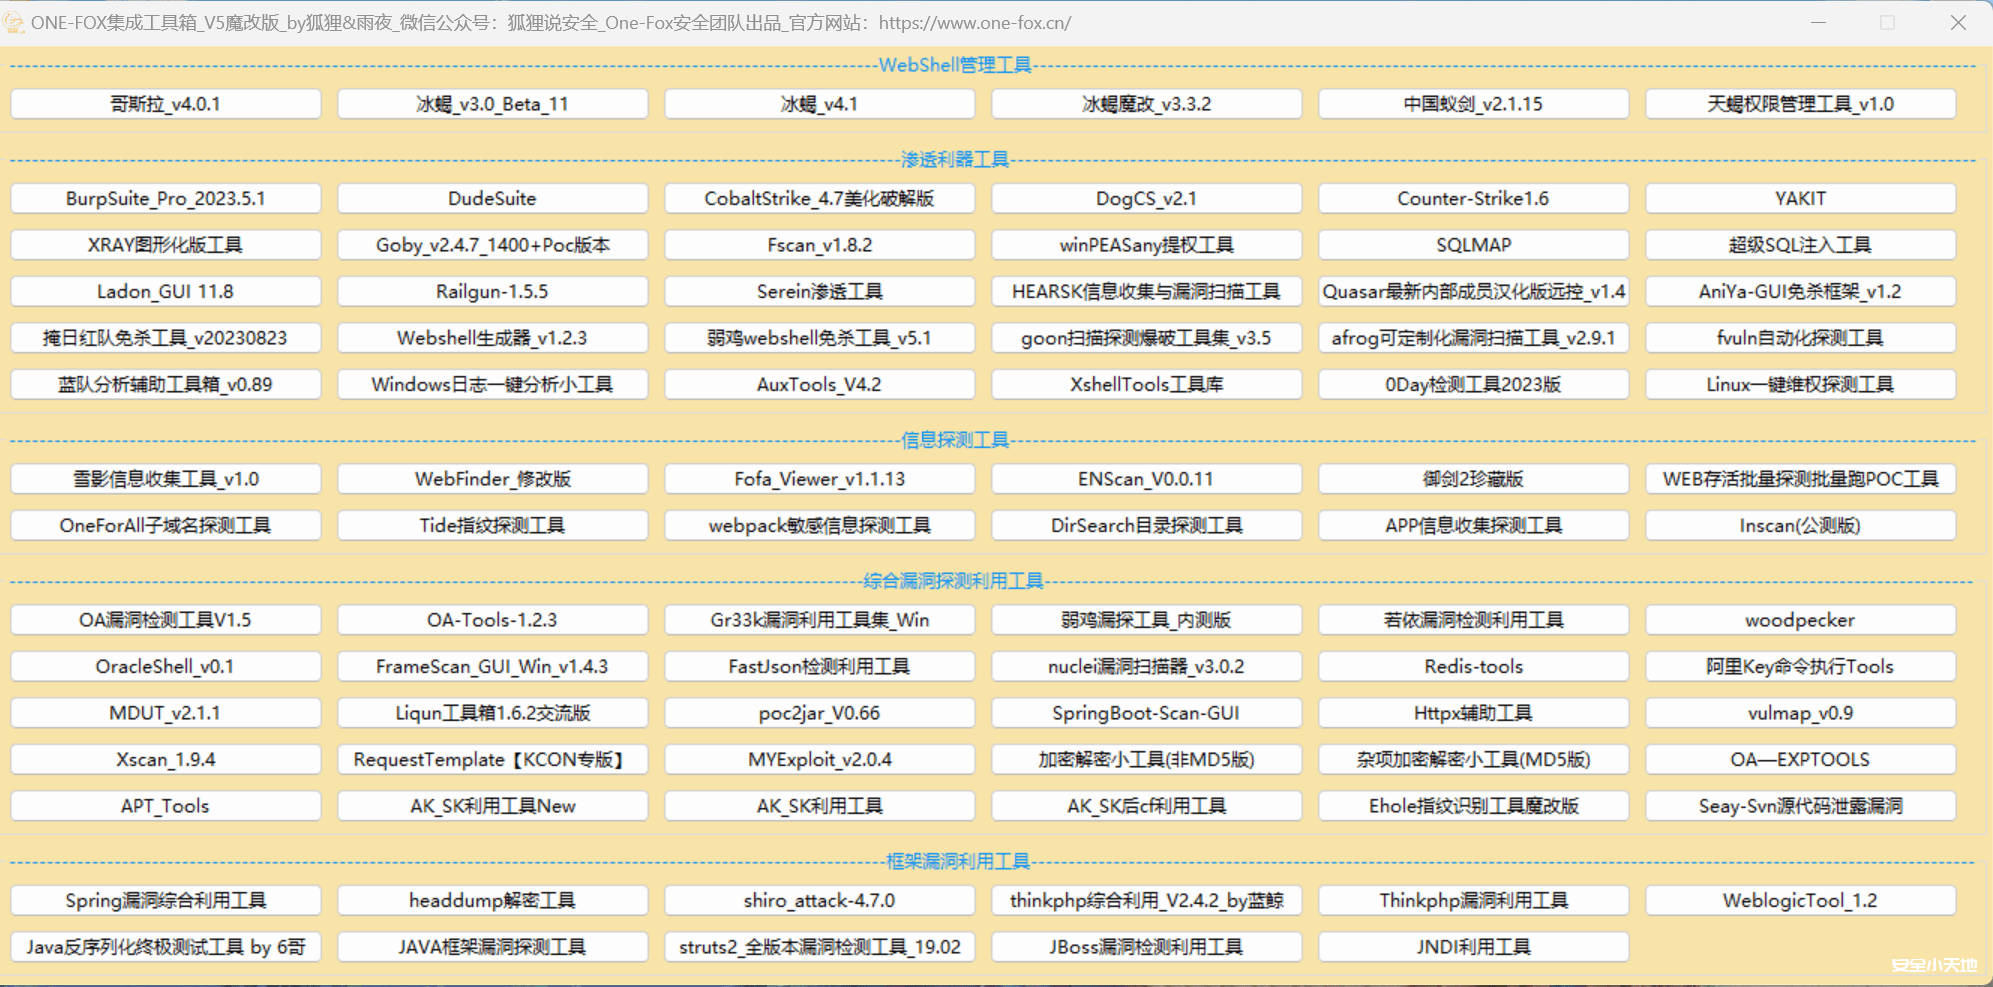
One-Fox工具箱V5魔改版已发布!
免责声明 安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机...

 2026年3月15日 12:27

nginx用正则表达式实现泛域名自动匹配目录的方法_nginx
这篇文章主要介绍了nginx用正则表达式实现泛域名自动匹配目录的相关知识,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 nginx用正则表达式实现泛...
2024年1月21日 21:07CVE-2021-46418: Telesquare TLR-2855KS6 – Arbitrary File Creation
漏洞标题 CVE-2021-46418: Telesquare TLR-2855KS6 - Arbitrary File Creation 漏洞描述 An unauthorized file creation vulnerability in Telesquare TLR-2855KS6 via PUT method can allow cr...
2021年12月30日 06:51CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting
漏洞标题 CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting 漏洞描述 The Store Locator WordPress plugin before 1.4.13 does not sanitise and escape an invalid...
2023年8月9日 13:05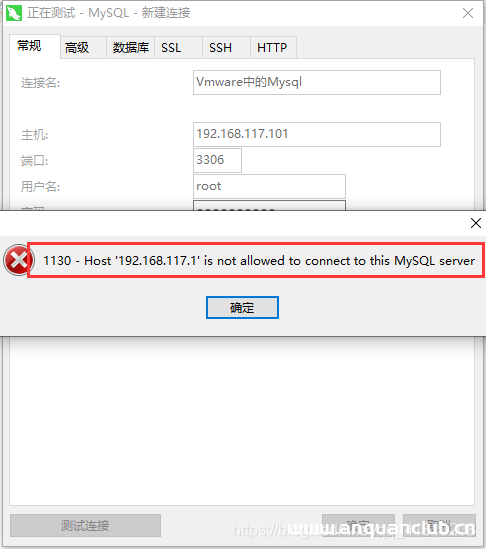
解决Navicat无法连接 VMware中Centos系统中的 MySQL服务器的问题_VMware
这篇文章主要介绍了解决Navicat无法连接 VMware中Centos系统中的 MySQL服务器的问题,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以...
2022年7月4日 20:08
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

