
最新发布第939页

CVE-2019-10758: mongo-express Remote Code Execution
漏洞标题 CVE-2019-10758: mongo-express Remote Code Execution 漏洞描述 mongo-express before 0.54.0 is vulnerable to remote code execution via endpoints that uses the `toBSON` method...
 2019年1月29日 12:49
CVE-2021-39312: WordPress True Ranker <2.2.4 - Local File Inclusion
漏洞标题 CVE-2021-39312: WordPress True Ranker <2.2.4 - Local File Inclusion 漏洞描述 WordPress True Ranker before version 2.2.4 allows sensitive configuration files such as wp-...
2021年11月3日 16:38CVE-2018-19518: PHP imap – Remote Command Execution
漏洞标题 CVE-2018-19518: PHP imap - Remote Command Execution 漏洞描述 University of Washington IMAP Toolkit 2007f on UNIX, as used in imap_open() in PHP and other products, launche...
2018年5月18日 11:01CVE-2020-23972: Joomla! Component GMapFP 3.5 – Arbitrary File Upload
漏洞标题 CVE-2020-23972: Joomla! Component GMapFP 3.5 - Arbitrary File Upload 漏洞描述 Joomla! Component GMapFP 3.5 is vulnerable to arbitrary file upload vulnerabilities. An attac...
2020年5月27日 06:05
详解CentOS7 安装 MariaDB 10.2.4的方法_Linux
这篇文章主要介绍了CentOS7 安装 MariaDB 10.2.4的方法,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 CentOS 6 及之前的版本中提供的是 MySQL 的服务器/客户端安装...
2026年8月23日 11:45CVE-2011-0049: Majordomo2 – SMTP/HTTP Directory Traversal
漏洞标题 CVE-2011-0049: Majordomo2 - SMTP/HTTP Directory Traversal 漏洞描述 A directory traversal vulnerability in the _list_file_get function in lib/Majordomo.pm in Majordomo 2 be...
2011年6月26日 17:05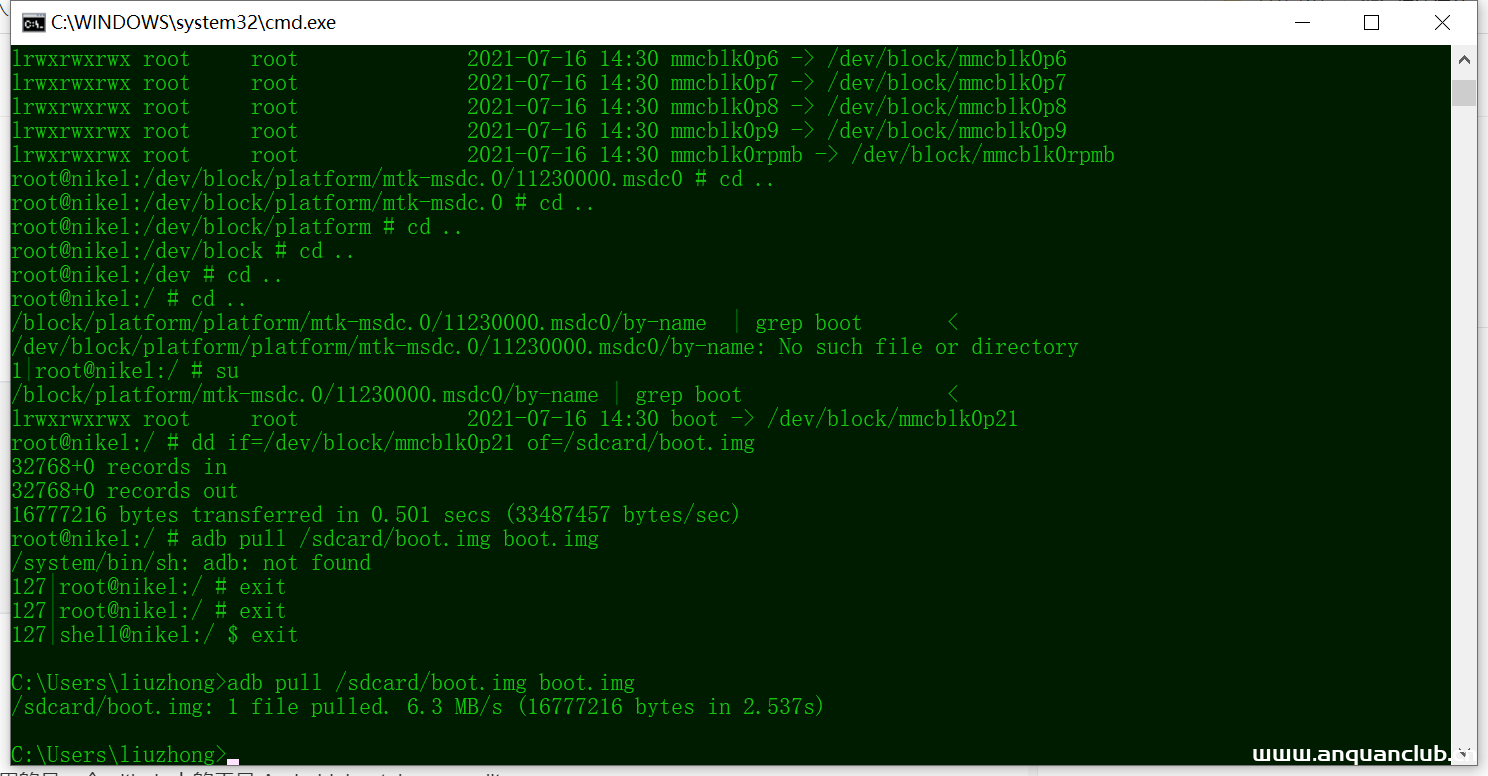
安卓系统修改系统内核绕过TracerPid检测–反防调试
背景: 得到一个Android的CrackMe来考察逆向知识,分析后发现其关键函数位于native so库中,并且在函数开始时启动了线程进行TracerPid检测的反调试,当发现程序被调试时会直接杀死应用。虽然题...
2022年3月10日 23:34CVE-2017-18529: PromoBar by BestWebSoft < 1.1.1 - Cross-Site Scripting
漏洞标题 CVE-2017-18529: PromoBar by BestWebSoft < 1.1.1 - Cross-Site Scripting 漏洞描述 The promobar plugin before 1.1.1 for WordPress has multiple XSS issues. PoC代码
2017年6月1日 03:14CVE-2023-38879: openSIS v9.0 – Path Traversal
漏洞标题 CVE-2023-38879: openSIS v9.0 - Path Traversal 漏洞描述 A path traversal vulnerability exists in openSIS Classic Community Edition v9.0 via the 'filename' paramet...
2023年9月28日 22:18CVE-2023-48728: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2023-48728: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 A reflected XSS vulnerability exists in the functiongetOpenGraph videoName functionality of WWBN AVideo 11...
2023年8月19日 21:15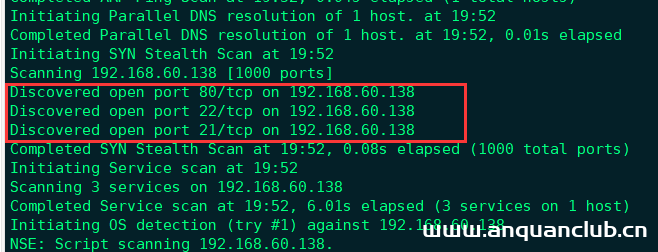
Vulnhub 靶场 DRIPPING BLUES: 1
前期准备: 靶机地址:http://www.vulnhub.com/entry/dripping-blues-1,744/ kali攻击机ip:192.168.60.128靶机地址:192.168.660.138 注:这个靶机有坑,别钻死胡同。 一、信息收集 1.使用nmap...

 2022年3月26日 20:27

bugbounty技巧聚合20211108
漏洞报告 【MariaDB】Path Traversal CVE-2021-26086 CVE-2021-26085 http://hackerone.com/reports/1369288 【Logitech】clickjacking on deleting user's clips [http://crossclip.com/clips]...
2022年3月10日 23:39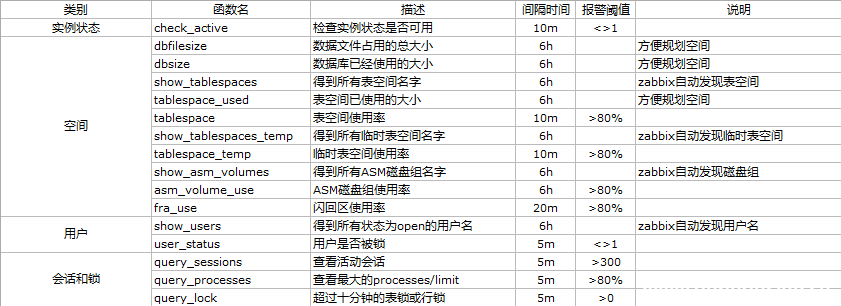
使用zabbix监控oracle数据库的方法详解_zabbix
这篇文章主要介绍了使用zabbix监控oracle数据库的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一、概述 zabbix是一款非常强大,同时也是...
2022年8月21日 21:51CVE-2020-25213: WordPress File Manager Plugin – Remote Code Execution
漏洞标题 CVE-2020-25213: WordPress File Manager Plugin - Remote Code Execution 漏洞描述 The WordPress File Manager plugin prior to version 6.9 is susceptible to remote code executi...
2020年3月5日 21:17CVE-2023-3844: MooDating 1.2 – Cross-Site Scripting
漏洞标题 CVE-2023-3844: MooDating 1.2 - Cross-Site Scripting 漏洞描述 A vulnerability was found in mooSocial mooDating 1.2. It has been declared as problematic. Affected by this vu...
2023年8月17日 03:06CVE-2023-5561: WordPress Core – Post Author Email Disclosure
漏洞标题 CVE-2023-5561: WordPress Core - Post Author Email Disclosure 漏洞描述 WordPress Core is vulnerable to Sensitive Information Exposure in versions between 4.7.0 and 6.3.1 vi...
2023年11月22日 20:21
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

