
最新发布第940页

Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
 2023年9月11日 05:33

Manjaro安装CUDA实现教程解析_服务器其它
这篇文章主要介绍了Manjaro安装CUDA实现教程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 去年年底安装将我的Thinkpad T450的双系...
2023年3月17日 20:29黑客攻击方法之【CC攻击】
免责声明 前言 网络攻击的方法有很多种,比如我们常见的DDOS等攻击,或者用kali执行一些脚本也可以实现DDOS攻击,再或者自行问度娘 正文 在进行攻击之前,我们要知道CC攻击它的原理 CC(Challeng...

 2022年9月16日 22:20
CVE-2019-6112: WordPress Sell Media 2.4.1 – Cross-Site Scripting
漏洞标题 CVE-2019-6112: WordPress Sell Media 2.4.1 - Cross-Site Scripting 漏洞描述 WordPress Plugin Sell Media v2.4.1 contains a cross-site scripting vulnerability in /inc/class-se...
2019年5月28日 09:00CVE-2017-9791: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-9791: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.1.x and 2.3.x with the Struts 1 plugin might allow remote code execution via a malici...
2017年2月25日 05:48CVE-2019-12985: Citrix SD-WAN Center – Remote Command Injection
漏洞标题 CVE-2019-12985: Citrix SD-WAN Center - Remote Command Injection 漏洞描述 Citrix SD-WAN Center is susceptible to remote command injection via the ping function in Diagnosti...
2019年12月28日 02:08CVE-2012-1835: WordPress Plugin All-in-One Event Calendar 1.4 – Cross-Site Scripting
漏洞标题 CVE-2012-1835: WordPress Plugin All-in-One Event Calendar 1.4 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in the All-in-One Event Calenda...
2012年1月9日 10:44CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
2025年4月27日 03:34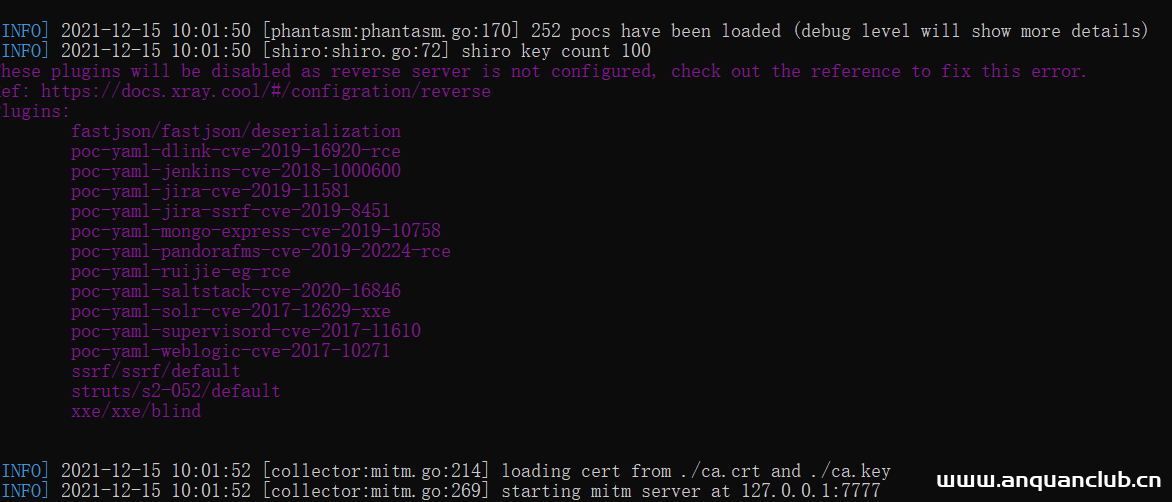
空白页面不要慌,我来跟你讲一讲
一次偶然的src挖掘,上班摸鱼中没啥事干,觉得有点空虚就来挖会洞吧,打开xray直接联动,点开页面开始整 点开发现虽然有title,但是页面是空白的 但是响应正常,这就很烦啊 瞅了一眼xray,发现...
2022年3月10日 23:32CVE-2023-0037: WordPress 10Web Map Builder < 1.0.73 - Unauthenticated SQL Injection
漏洞标题 CVE-2023-0037: WordPress 10Web Map Builder < 1.0.73 - Unauthenticated SQL Injection 漏洞描述 The 10Web Map Builder for Google Maps WordPress plugin before 1.0.73 does n...
2023年10月3日 14:07CVE-2019-14312: Aptana Jaxer 1.0.3.4547 – Local File inclusion
漏洞标题 CVE-2019-14312: Aptana Jaxer 1.0.3.4547 - Local File inclusion 漏洞描述 Aptana Jaxer 1.0.3.4547 is vulnerable to local file inclusion in the wikilite source code viewer. A...
2019年9月8日 19:24CVE-2021-26855: Microsoft Exchange Server Remote Code Execution
漏洞标题 CVE-2021-26855: Microsoft Exchange Server Remote Code Execution 漏洞描述 Microsoft Exchange Server Remote Code Execution Vulnerability PoC代码
2021年9月5日 05:56CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 – Remote Code Execution (XXE)
漏洞标题 CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 - Remote Code Execution (XXE) 漏洞描述 The JIRA Workflow Designer Plugin in Atlassian JIRA...
2017年8月24日 04:53CVE-2020-13483: Bitrix24 <=20.0.0 - Cross-Site Scripting
漏洞标题 CVE-2020-13483: Bitrix24 <=20.0.0 - Cross-Site Scripting 漏洞描述 The Web Application Firewall in Bitrix24 up to and including 20.0.0 allows XSS via the items[ITEMS][ID...
2020年10月5日 04:21CVE-2024-1208: LearnDash LMS < 4.10.3 - Sensitive Information Exposure
漏洞标题 CVE-2024-1208: LearnDash LMS < 4.10.3 - Sensitive Information Exposure 漏洞描述 The LearnDash LMS plugin for WordPress is vulnerable to Sensitive Information Exposure i...
2024年6月24日 11:37CVE-2024-3300: Delmia Apriso – Pre-Authentication Unsafe .NET Object Deserialization
漏洞标题 CVE-2024-3300: Delmia Apriso - Pre-Authentication Unsafe .NET Object Deserialization 漏洞描述 An unsafe .NET object deserialization vulnerability in DELMIA Apriso Release ...
2024年7月11日 22:34
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

