
最新发布第941页

CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection
漏洞标题 CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection 漏洞描述 WordPress Personal Dictionary plugin before 1.3.4 contains a blind SQL injection vuln...
 2022年2月2日 03:13
CVE-2023-22047: Oracle Peoplesoft – Unauthenticated File Read
漏洞标题 CVE-2023-22047: Oracle Peoplesoft - Unauthenticated File Read 漏洞描述 Vulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component- Port...
2023年3月26日 01:52CVE-2022-22963: Spring Cloud – Remote Code Execution
漏洞标题 CVE-2022-22963: Spring Cloud - Remote Code Execution 漏洞描述 Spring Cloud Function versions 3.1.6, 3.2.2 and older unsupported versions are susceptible to remote code exe...
2022年5月2日 09:28
-Struts2-009 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-Struts2-009 远程命令执行漏洞 Struts是Apache软件基金会(ASF)赞助的一个开源项目。它最初是Jakarta项目中的一个子项目,并在2004年3...

 2023年2月4日 14:54
CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
2025年11月19日 06:23CVE-2017-11107: phpLDAPadmin <= 1.2.3 - Reflected XSS
漏洞标题 CVE-2017-11107: phpLDAPadmin <= 1.2.3 - Reflected XSS 漏洞描述 phpLDAPadmin <= 1.2.3 contains a reflected cross-site scripting caused by unsanitized input in htdocs/...
2017年10月23日 04:38CVE-2025-4008: MeteoBridge <= 6.1 - Remote Code Execution
漏洞标题 CVE-2025-4008: MeteoBridge <= 6.1 - Remote Code Execution 漏洞描述 The Meteobridge web interface let meteobridge administrator manage their weather station data collect...
2025年5月28日 16:08CVE-2023-6380: OpenCms 14 & 15 – Open Redirect
漏洞标题 CVE-2023-6380: OpenCms 14 & 15 - Open Redirect 漏洞描述 Open redirect vulnerability has been found in the Open CMS product affecting versions 14 and 15 of the 'Me...
2023年1月1日 03:25
浅谈cs的shellcode的使用方法
前言:学习心得,大佬勿喷 看完本文你会了解到: 1、cs中的shellcode是做什么的? 2、用类似于cs、msf生成的shellcode的加载器是什么样的? 3、windows api是什么? 4、怎样从msf及cs生成的shel...
2022年3月10日 23:32CVE-2021-44910: SpringBlade – Information Leakage
漏洞标题 CVE-2021-44910: SpringBlade - Information Leakage 漏洞描述 SpringBlade is a comprehensive project upgraded and optimized from a commercial-grade project, featuring both a ...
2021年1月29日 20:23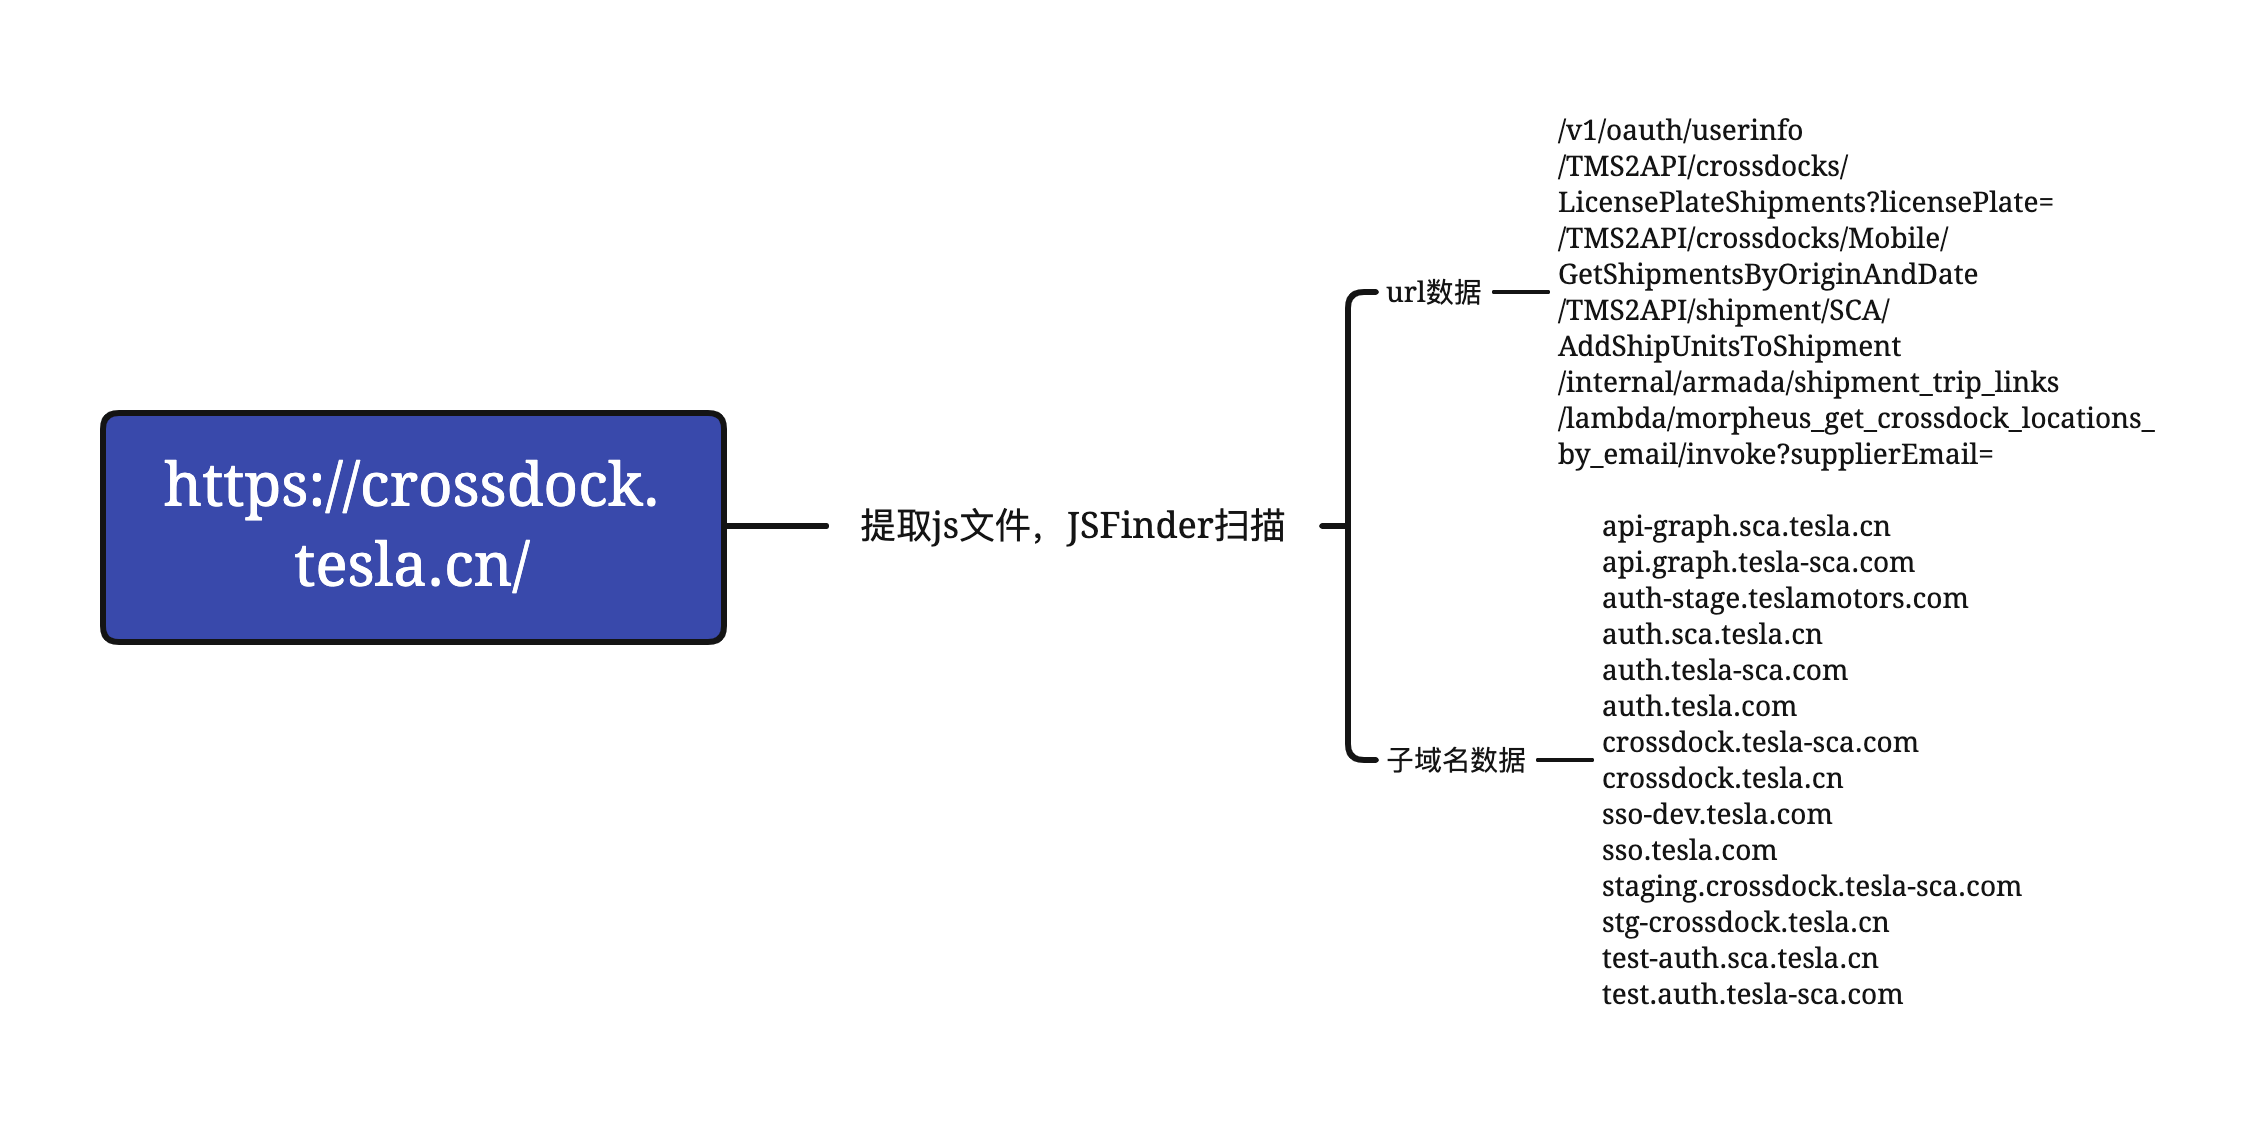
信息收集系列之JavaScript文件敏感信息提取
0x01 前言 在我们渗透或者漏洞挖掘的过程中,发现越来越多的网站使用webpack技术,开发人员通常会把api路由打包进js文件里。JSFinder这款工具可以帮助我们快速从js文件中提取api和其他敏感信息...
2022年3月10日 23:36
【】-webmin CVE-2020-35606
0x01 webmin描述 Webmin是Webmin社区的一套基于Web的用于类Unix操作系统中的系统管理工具。Webmin 1.962版本及之前版本存在安全漏洞,该漏洞允许执行任意命令。任何被授权使用Package Updates模...
2022年10月31日 11:01
Docker容器应用中,10个要不得的坏习惯_docker
这篇文章主要介绍了Docker容器的应用中,10个要不得的坏习惯,帮助大家更好的理解和使用docker,感兴趣的朋友可以了解下 毋庸置疑,容器已经成为企业IT基础设施中必不可少的部分,它具有许多的...
2023年7月30日 20:02CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload
漏洞标题 CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload 漏洞描述 WordPress Fancy Product Designer plugin before 4.6.9 is susceptible to an arbit...
2021年4月20日 14:30CVE-2020-4463: IBM Maximo Asset Management Information Disclosure – XML External Entity Injection
漏洞标题 CVE-2020-4463: IBM Maximo Asset Management Information Disclosure - XML External Entity Injection 漏洞描述 IBM Maximo Asset Management is vulnerable to an XML external ent...
2020年4月30日 20:32CVE-2019-9874: Sitecore Experience Platform – Deserialization of Untrusted Data
漏洞标题 CVE-2019-9874: Sitecore Experience Platform - Deserialization of Untrusted Data 漏洞描述 Sitecore Experience Platform before 8.2 Update-7 and 9.0 before Update-2 is vulner...
2019年4月10日 10:27
2026年10月18日 11:45
2026年10月18日 11:45
2026年10月17日 11:45
2026年10月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

