
最新发布第945页

CVE-2024-8353: GiveWP Donation Plugin <= 3.16.1 - Unauthenticated PHP Object Injection
漏洞标题 CVE-2024-8353: GiveWP Donation Plugin <= 3.16.1 - Unauthenticated PHP Object Injection 漏洞描述 The GiveWP – Donation Plugin and Fundraising Platform plugin for WordPr...
 2024年1月22日 13:09
CVE-2021-29441: Nacos <1.4.1 - Authentication Bypass
漏洞标题 CVE-2021-29441: Nacos <1.4.1 - Authentication Bypass 漏洞描述 This template only works on Nuclei engine prior to version 2.3.3 and version >= 2.3.5. In Nacos before ...
2021年2月16日 07:02CVE-2021-35250: SolarWinds Serv-U 15.3 – Directory Traversal
漏洞标题 CVE-2021-35250: SolarWinds Serv-U 15.3 - Directory Traversal 漏洞描述 SolarWinds Serv-U 15.3 is susceptible to local file inclusion, which may allow an attacker access to ...
2021年3月13日 21:24CVE-2015-4127: WordPress Church Admin <0.810 - Cross-Site Scripting
漏洞标题 CVE-2015-4127: WordPress Church Admin <0.810 - Cross-Site Scripting 漏洞描述 WordPress Church Admin plugin before 0.810 allows remote attackers to inject arbitrary web ...
2015年6月8日 16:43CVE-2019-3911: LabKey Server Community Edition <18.3.0 - Cross-Site Scripting
漏洞标题 CVE-2019-3911: LabKey Server Community Edition <18.3.0 - Cross-Site Scripting 漏洞描述 LabKey Server Community Edition before 18.3.0-61806.763 contains a reflected cros...
2019年7月9日 18:03CVE-2021-20086: Odoo Apps – Cross-Site Scripting via Prototype Pollution
漏洞标题 CVE-2021-20086: Odoo Apps - Cross-Site Scripting via Prototype Pollution 漏洞描述 jquery-bbq 1.2.1 contains a prototype pollution caused by improperly controlled modificat...
2021年1月25日 05:31CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access
漏洞标题 CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access 漏洞描述 PowerJob V4.3.1 is vulnerable to Insecure Permissions. via the list job interface. PoC代码
2023年3月24日 15:36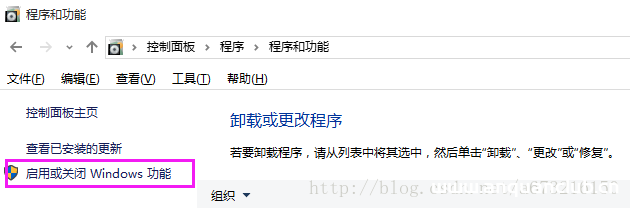
Win10下配置IIS10并支持调试ASP程序的步骤_win服务器
今天临时需要在Win10下配置IIS10并支持调试ASP程序的步骤,不像windows服务器版本比较好找,这个得找到放风,这里九尾大家分享一下需要的朋友可以参考下 微软公司的IIS IIS(Internet Informatio...
2024年2月12日 20:00CVE-2022-22965: Spring – Remote Code Execution
漏洞标题 CVE-2022-22965: Spring - Remote Code Execution 漏洞描述 Spring MVC and Spring WebFlux applications running on Java Development Kit 9+ are susceptible to remote code execut...
2022年7月28日 19:57CVE-2018-19753: Tarantella Enterprise <3.11 - Local File Inclusion
漏洞标题 CVE-2018-19753: Tarantella Enterprise <3.11 - Local File Inclusion 漏洞描述 Tarantella Enterprise versions prior to 3.11 are susceptible to local file inclusion. PoC代...
2018年3月3日 09:36
bugbounty技巧聚合20220107
漏洞报告 【MariaDB】Grafana LFI注入 http://hackerone.com/reports/1419213 挖洞技巧 CVE-2021-44515是 ManageEngine Desktop Central 中的身份验证绕过漏洞,可能导致远程代码执行。 http://...
2022年4月1日 18:36在 Linux 上查看和配置密码时效的方法_Linux
这篇文章主要介绍了在 Linux 上查看和配置密码时效的相关知识,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 使用正确的设置,可以强制 Linux 用...
2024年2月19日 20:34CVE-2022-23881: ZZZCMS zzzphp 2.1.0 – Remote Code Execution
漏洞标题 CVE-2022-23881: ZZZCMS zzzphp 2.1.0 - Remote Code Execution 漏洞描述 ZZZCMS zzzphp v2.1.0 is susceptible to a remote command execution vulnerability via danger_key() at zz...
2022年10月8日 12:17CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure
漏洞标题 CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure 漏洞描述 WordPress Guppy plugin through 1.1 is susceptible to an API disclosure vulnerability. This can a...
2021年7月6日 05:14CVE-2023-34751: bloofoxCMS v0.5.2.1 – SQL Injection
漏洞标题 CVE-2023-34751: bloofoxCMS v0.5.2.1 - SQL Injection 漏洞描述 bloofox v0.5.2.1 was discovered to contain a SQL injection vulnerability via the gid parameter at admin/index....
2023年11月26日 01:30CVE-2022-44957: WebTareas 2.4p5 – Cross-Site Scripting
漏洞标题 CVE-2022-44957: WebTareas 2.4p5 - Cross-Site Scripting 漏洞描述 webtareas 2.4p5 was discovered to contain a cross-site scripting (XSS) vulnerability in the component /clie...
2022年4月8日 16:55
2026年10月18日 11:45
2026年10月18日 11:45
2026年10月17日 11:45
2026年10月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

