
最新发布第958页

CVE-2020-8615: WordPress Plugin Tutor LMS 1.5.3 – Cross-Site Request Forgery
漏洞标题 CVE-2020-8615: Wordpress Plugin Tutor LMS 1.5.3 - Cross-Site Request Forgery 漏洞描述 A CSRF vulnerability in the Tutor LMS plugin before 1.5.3 for WordPress can result in...
 2020年9月27日 05:16
CVE-2019-16932: Visualizer <3.3.1 - Blind Server-Side Request Forgery
漏洞标题 CVE-2019-16932: Visualizer <3.3.1 - Blind Server-Side Request Forgery 漏洞描述 Visualizer prior to 3.3.1 suffers from a blind server-side request forgery vulnerability ...
2019年6月9日 23:22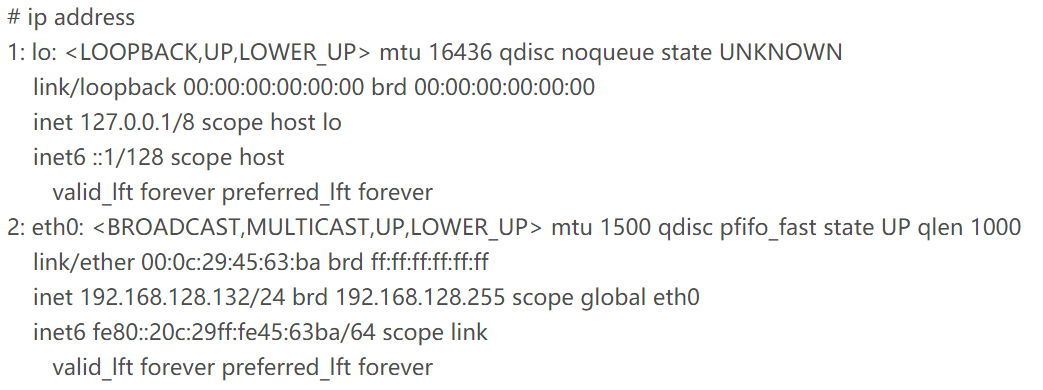
Linux查看ip的实例方法_Linux
在本篇文章里小编给大家整理的是关于Linux查看ip的实例方法,对此有需要的朋友们可以学习下。 在排除网络问题,设置新连接或配置防火墙时,了解设备的 IP 地址非常重要。下面我们就来看看Linux...
2024年5月24日 20:45CVE-2022-29303: SolarView Compact 6.00 – OS Command Injection
漏洞标题 CVE-2022-29303: SolarView Compact 6.00 - OS Command Injection 漏洞描述 SolarView Compact 6.00 was discovered to contain a command injection vulnerability via conf_mail.php...
2022年2月22日 02:01CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
2019年12月28日 13:44CVE-2021-21973: VMware vSphere – Server-Side Request Forgery
漏洞标题 CVE-2021-21973: VMware vSphere - Server-Side Request Forgery 漏洞描述 VMware vSphere (HTML5) is susceptible to server-side request forgery due to improper validation of UR...
2021年1月22日 00:49CVE-2019-20141: WordPress Laborator Neon Theme 2.0 – Cross-Site Scripting
漏洞标题 CVE-2019-20141: WordPress Laborator Neon Theme 2.0 - Cross-Site Scripting 漏洞描述 WordPress Laborator Neon theme 2.0 contains a cross-site scripting vulnerability via the...
2019年10月24日 17:29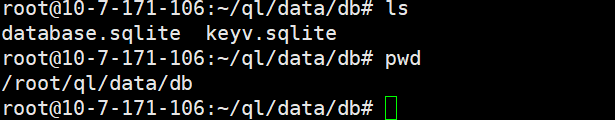
最新版青龙面板密码忘记之后怎么找回
前言 安装完青龙面板之后,咱们很容易忘记密码是什么,这个时间咱们如果是docker安装的话,可以通过以下方式找回密码。 找回密码 登录青龙面板服务器 查看启动docker的具体配置 docker inspect ...

 2026年3月9日 22:15
CVE-2021-27748: IBM WebSphere HCL Digital Experience – Server-Side Request Forgery
漏洞标题 CVE-2021-27748: IBM WebSphere HCL Digital Experience - Server-Side Request Forgery 漏洞描述 IBM WebSphere HCL Digital Experience is vulnerable to server-side request forge...
2021年1月17日 16:05
基于http.server搭建局域网服务器过程解析_服务器其它
这篇文章主要介绍了基于http.server搭建局域网服务器过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 不知道大家有没有遇到过这样...
2023年4月5日 20:22
【新奇思路】不错的漏洞搜集思路分享
思路收集于网络,安全小天地只是做了一点整理。 1.利用google语法 发现注入: site:target.com intext:'sql syntax near' | intext:'incorrect syntax near' site:target.com intext:'sql synta...
2023年5月6日 22:12CVE-2024-9772: WordPress UIX Shortcodes <= 1.9.7 - Unauthenticated Shortcode Execution
漏洞标题 CVE-2024-9772: WordPress UIX Shortcodes <= 1.9.7 - Unauthenticated Shortcode Execution 漏洞描述 The The Uix Shortcodes – Compatible with Gutenberg plugin for WordPress...
2024年3月28日 14:56CVE-2017-5487: WordPress<4.7.1 Exist Username Enumeration
漏洞标题 CVE-2017-5487: Wordpress<4.7.1 Exist Username Enumeration 漏洞描述 WordPress (是一种使用PHP语言开发的博客平台)WordPress 在4.7.0版本之后将REST API插件集成到默认功能之...
2017年11月23日 02:43(CVE-2025-10210) ChanCMS Search功能SQL注入漏洞
漏洞标题 (CVE-2025-10210) ChanCMS Search功能SQL注入漏洞 漏洞描述 (CVE-2025-10210) ChanCMS Search功能SQL注入漏洞 PoC代码 暂无
2025年11月3日 00:31CVE-2024-7593: Ivanti vTM – Authentication Bypass
漏洞标题 CVE-2024-7593: Ivanti vTM - Authentication Bypass 漏洞描述 Incorrect implementation of an authentication algorithm in Ivanti vTM other than versions 22.2R1 or 22.7R2 allow...
2024年9月17日 13:37CVE-2025-25291: GitLab – SAML Authentication Bypass
漏洞标题 CVE-2025-25291: GitLab - SAML Authentication Bypass 漏洞描述 ruby-saml provides security assertion markup language (SAML) single sign-on (SSO) for Ruby. An authentication ...
2025年2月21日 06:06
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

