
最新发布第958页

每日云安全技术资讯20220225
云风险百科,搜索 900 多个云安全风险 http://orca.security/resources/cloud-risk-encyclopedia/ Microsoft Security 提供新的多云功能 http://www.microsoft.com/security/blog/2022/02/23/mi...
 2022年3月10日 23:38

CVE-2023-49230: Peplink Balance Two before 8.4.0 – Unauthenticated Config Upload
漏洞标题 CVE-2023-49230: Peplink Balance Two before 8.4.0 - Unauthenticated Config Upload 漏洞描述 A vulnerability in Peplink Balance Two prior to version 8.4.0 allows unauthentica...
2023年5月19日 17:21CVE-2023-4450: JeecgBoot JimuReport – Template injection
漏洞标题 CVE-2023-4450: JeecgBoot JimuReport - Template injection 漏洞描述 A vulnerability was found in jeecgboot JimuReport up to 1.6.0. It has been declared as critical. Affected...
2023年10月31日 09:23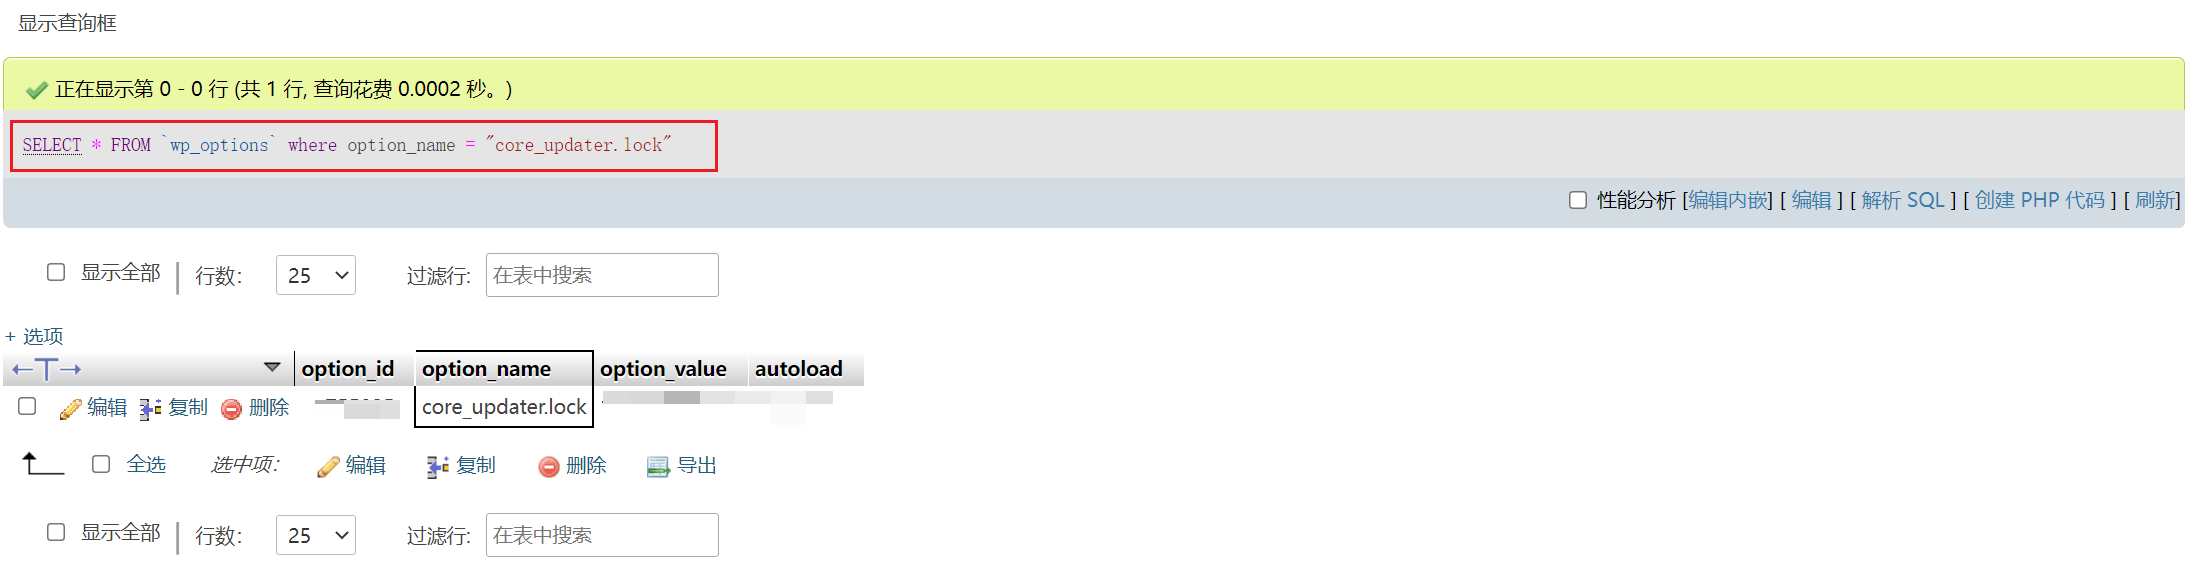
升级WordPress提示另一更新正在进行的原因及解决办法
前言 今天进行wordpress更新的时间遇到了一个小问题:升级WordPress 另一更新正在进行。出现这个提示,多数情况是上传一次的更新还没有结束,然后重新点击了刷新页面,导致更新中断。 原因分析 ...

 2023年10月28日 10:19
CVE-2021-29203: HPE Edgeline Infrastructure Manager <1.22 - Authentication Bypass
漏洞标题 CVE-2021-29203: HPE Edgeline Infrastructure Manager <1.22 - Authentication Bypass 漏洞描述 HPE Edgeline Infrastructure Manager, also known as HPE Edgeline Infrastructur...
2021年9月2日 23:44CVE-2025-53118: Securden Unified PAM – Authentication Bypass
漏洞标题 CVE-2025-53118: Securden Unified PAM - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists which allows an unauthenticated attacker to control adm...
2025年7月5日 07:30CVE-2022-32015: Complete Online Job Search System 1.0 – SQL Injection
漏洞标题 CVE-2022-32015: Complete Online Job Search System 1.0 - SQL Injection 漏洞描述 Complete Online Job Search System 1.0 contains a SQL injection vulnerability via /eris/index...
2022年11月19日 01:55CVE-2023-6875: WordPress POST SMTP Mailer <= 2.8.7 - Authorization Bypass
漏洞标题 CVE-2023-6875: WordPress POST SMTP Mailer <= 2.8.7 - Authorization Bypass 漏洞描述 The POST SMTP Mailer – Email log, Delivery Failure Notifications and Best Mail SMTP ...
2023年2月4日 15:32CVE-2021-20086: Odoo Apps – Cross-Site Scripting via Prototype Pollution
漏洞标题 CVE-2021-20086: Odoo Apps - Cross-Site Scripting via Prototype Pollution 漏洞描述 jquery-bbq 1.2.1 contains a prototype pollution caused by improperly controlled modificat...
2021年2月10日 11:44CVE-2020-24148: Import XML & RSS Feeds WordPress Plugin <= 2.0.1 Server-Side Request Forgery
漏洞标题 CVE-2020-24148: Import XML & RSS Feeds WordPress Plugin <= 2.0.1 Server-Side Request Forgery 漏洞描述 WordPress plugin Import XML and RSS Feeds (import-xml-feed) pl...
2020年2月12日 10:54CVE-2020-5902: F5 BIG-IP TMUI – Remote Code Execution
漏洞标题 CVE-2020-5902: F5 BIG-IP TMUI - Remote Code Execution 漏洞描述 F5 BIG-IP versions 15.0.0-15.1.0.3, 14.1.0-14.1.2.5, 13.1.0-13.1.3.3, 12.1.0-12.1.5.1, and 11.6.1-11.6.5.1, ...
2020年3月13日 21:51CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution
漏洞标题 CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution 漏洞描述 A remote code execution vulnerability occurs in OpenTSDB through 2.4.0 via command injection in the yrange pa...
2020年11月16日 16:20CVE-2019-17230: WordPress OneTone theme <= 3.0.6 – Unauthenticated Options Changes
漏洞标题 CVE-2019-17230: WordPress OneTone theme <= 3.0.6 – Unauthenticated Options Changes 漏洞描述 includes/theme-functions.php in the OneTone theme through 3.0.6 for WordPre...
2019年9月20日 05:27CVE-2023-1671: Sophos Web Appliance – Remote Code Execution
漏洞标题 CVE-2023-1671: Sophos Web Appliance - Remote Code Execution 漏洞描述 A pre-auth command injection vulnerability in the warn-proceed handler of Sophos Web Appliance older t...
2023年5月2日 18:55CVE-2022-45362: WordPress Paytm Payment Gateway <=2.7.0 - Server-Side Request Forgery
漏洞标题 CVE-2022-45362: WordPress Paytm Payment Gateway <=2.7.0 - Server-Side Request Forgery 漏洞描述 WordPress Paytm Payment Gateway plugin through 2.7.0 contains a server-si...
2022年1月24日 09:12
bugbounty技巧聚合20211008
时事热点 上古杂志Phrack更新 ? http://www.phrack.org/issues/70/1.html 实时流媒体视频平台Twitch的敏感数据遭泄露 http://mp.weixin.qq.com/s/Vu5JaUcSwEJx38xsRrTtCQ 下载地址:http://noth...
2022年3月10日 23:32
2026年10月18日 11:45
2026年10月18日 11:45
2026年10月17日 11:45
2026年10月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

