
最新发布第965页

CVE-2010-2033: Joomla! Percha Categories Tree 0.6 – Local File Inclusion
漏洞标题 CVE-2010-2033: Joomla! Percha Categories Tree 0.6 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Percha Fields Attach (com_perchafieldsattach) ...
 2010年6月4日 22:27
CVE-2010-1491: Joomla! Component MMS Blog 2.3.0 – Local File Inclusion
漏洞标题 CVE-2010-1491: Joomla! Component MMS Blog 2.3.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the MMS Blog (com_mmsblog) component 2.3.0 for Jooml...
2010年12月10日 02:30CVE-2024-8877: Riello Netman 204 – SQL Injection
漏洞标题 CVE-2024-8877: Riello Netman 204 - SQL Injection 漏洞描述 The three endpoints /cgi-bin/db_datalog_w.cgi, /cgi-bin/db_eventlog_w.cgi, and /cgi-bin/db_multimetr_w.cgi are vu...
2024年4月20日 08:27CVE-2021-36888: WordPress Image Hover Ultimate – Unauthenticated Settings Update
漏洞标题 CVE-2021-36888: WordPress Image Hover Ultimate - Unauthenticated Settings Update 漏洞描述 Unauthenticated Arbitrary Options Update vulnerability leading to full website co...
2021年7月22日 00:33CVE-2017-1000028: GlassFish LFI
漏洞标题 CVE-2017-1000028: GlassFish LFI 漏洞描述 GlassFish是一款强健的商业兼容应用服务器,达到产品级质量,可免费用于开发、部署和重新分发。开发者可以免费获得源代码,还可以对代码进...
2017年8月21日 22:40CVE-2023-24488: Citrix Gateway and Citrix ADC – Cross-Site Scripting
漏洞标题 CVE-2023-24488: Citrix Gateway and Citrix ADC - Cross-Site Scripting 漏洞描述 Citrix ADC and Citrix Gateway versions before 13.1 and 13.1-45.61, 13.0 and 13.0-90.11, 12.1 ...
2023年2月7日 05:48CVE-2023-25194: Apache Druid Kafka Connect – Remote Code Execution
漏洞标题 CVE-2023-25194: Apache Druid Kafka Connect - Remote Code Execution 漏洞描述 The vulnerability has the potential to enable a remote attacker with authentication to run any ...
2023年5月5日 00:19CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection
漏洞标题 CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection 漏洞描述 WordPress My Calendar plugin versions before 3.4.22 are vulnerable to an unauthenticated SQL injec...
2023年6月23日 23:52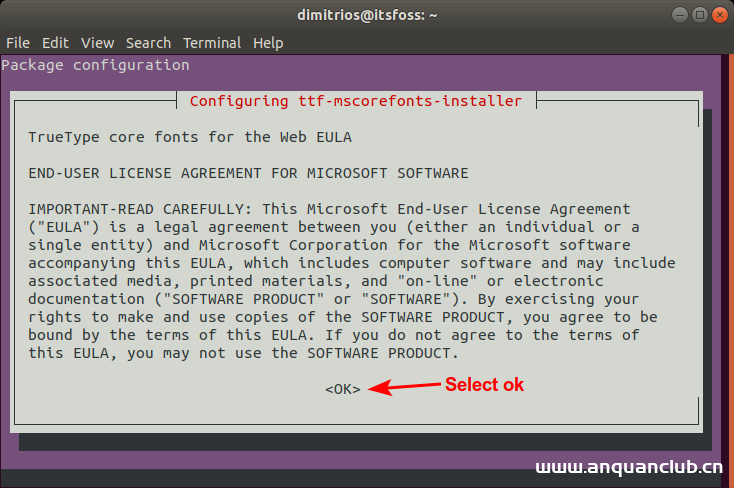
基于 Ubuntu 的发行版上安装微软 TrueType 字体的教程_Linux
这篇文章主要介绍了基于 Ubuntu 的发行版上安装微软 TrueType 字体的教程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 如果你在 Linux 上用 Li...
2024年2月17日 20:04CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass
漏洞标题 CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass 漏洞描述 Stacks Mobile App Builder WordPress plugin ≤ 5.2.3 suffers from an authent...
2024年5月29日 05:57
基于Python的身份证后四/六/八位爆破 + 实名二要素验证组合拳
本文声明 此文仅用于技术科普,教育与研究用途,请勿用于商业甚至非法用途,否则一切后果自负。若用户利用此文章而受到惩处,本人及本平台对其行为概不负责,亦不承担任何连带责任。 实战分享 ...

 2022年12月30日 21:43
CVE-2015-10141: Xdebug <= 2.5.5 - Command Injection
漏洞标题 CVE-2015-10141: Xdebug <= 2.5.5 - Command Injection 漏洞描述 Xdebug <= 2.5.5 contains an unauthenticated command injection caused by accepting debugger protocol comm...
2015年2月11日 06:44CVE-2023-1671: Sophos Web Appliance – Remote Code Execution
漏洞标题 CVE-2023-1671: Sophos Web Appliance - Remote Code Execution 漏洞描述 A pre-auth command injection vulnerability in the warn-proceed handler of Sophos Web Appliance older t...
2023年7月31日 23:00CVE-2021-21985: VMware vSphere Client (HTML5) – Remote Code Execution
漏洞标题 CVE-2021-21985: VMware vSphere Client (HTML5) - Remote Code Execution 漏洞描述 The vSphere Client (HTML5) contains a remote code execution vulnerability due to lack of inp...
2021年2月21日 22:36CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
2022年12月27日 16:07CVE-2023-45375: PrestaShop PireosPay – SQL Injection
漏洞标题 CVE-2023-45375: PrestaShop PireosPay - SQL Injection 漏洞描述 In the module “PireosPay” (pireospay) up to version 1.7.9 from 01generator.com for PrestaShop, a guest can ...
2023年10月10日 17:34
2026年10月17日 11:45
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

