
最新发布第976页
springboot中寻找redis info
如果目录扫描发现springboot的/actuator,但是拿不到关键的heapdump或env等信息,可以查看该服务器是否开放redis服务,如果有,可以访问http://xxx.huoxian.cn:6375/actuator/redis/info读取red...
 2022年3月10日 23:36

CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting
漏洞标题 CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in files/installer.cleanup.php in the Duplicator...
2013年6月10日 14:48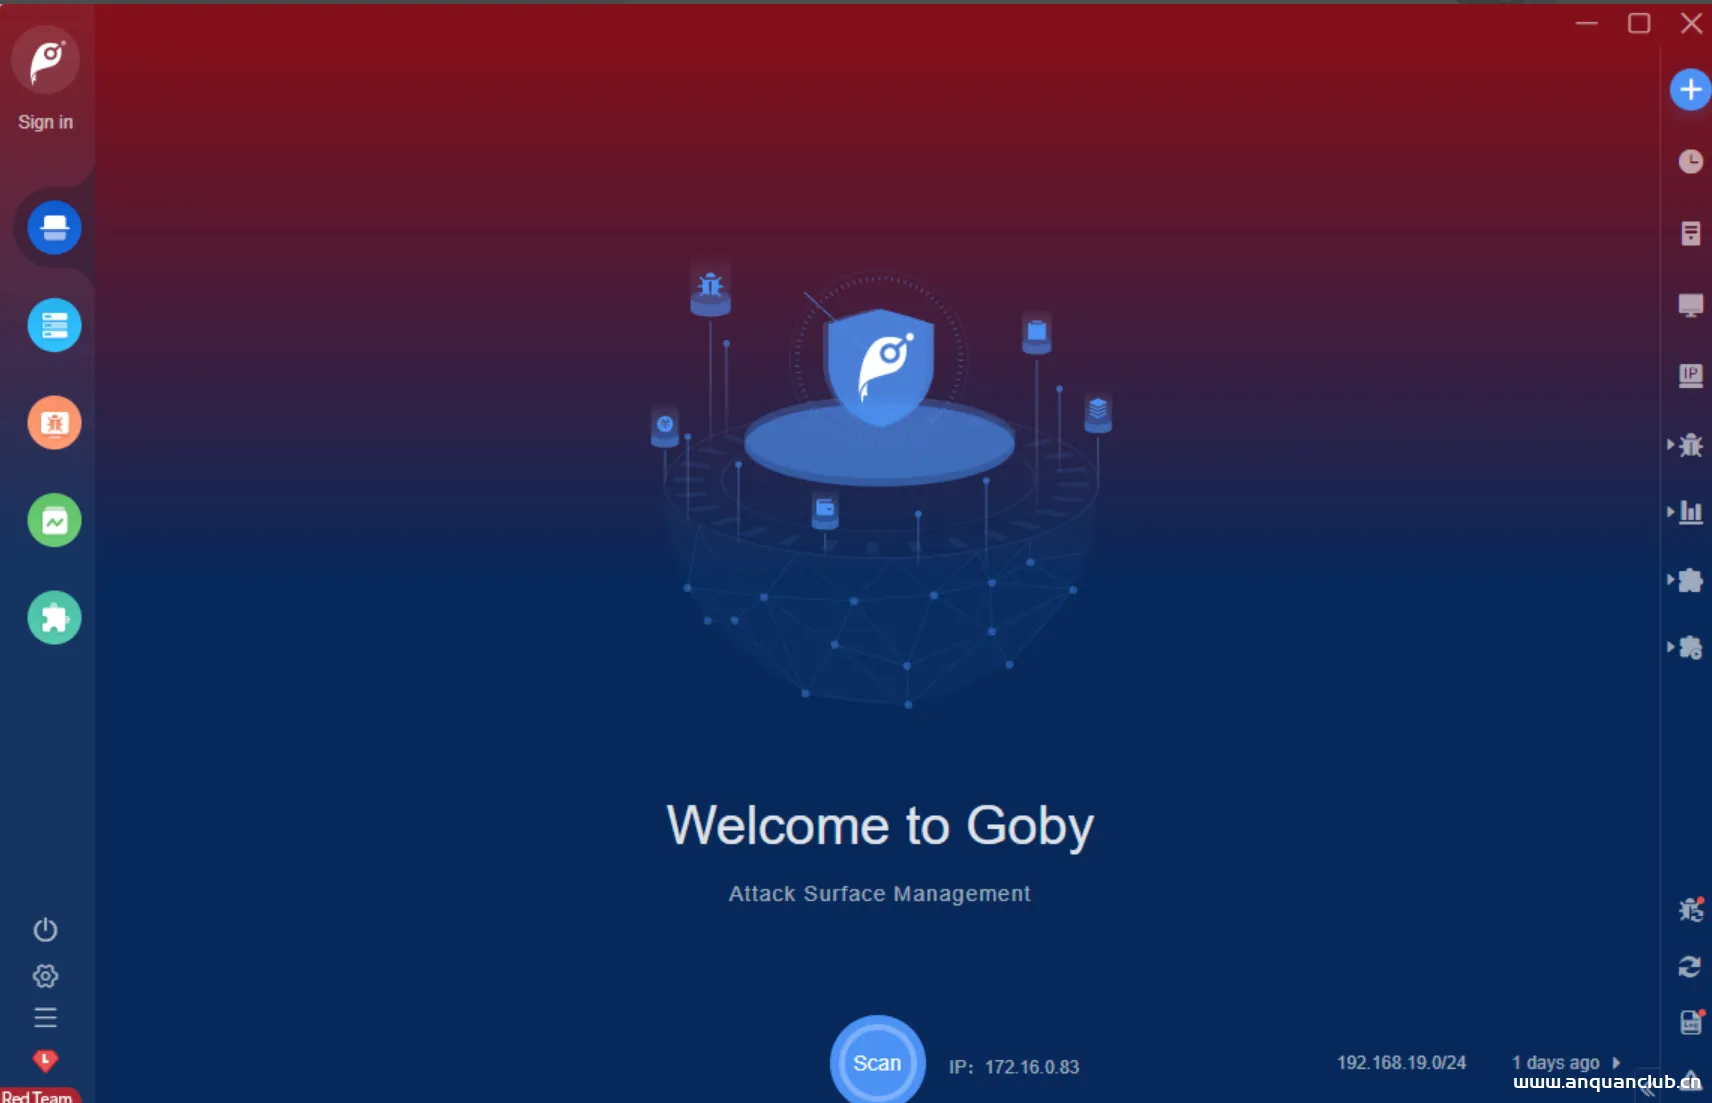
Goby 2.0.5 Beta红队版 包含1288POC
相关声明 以下工具仅用于企业授权渗透测试,请勿用于非法用途。 界面截图 红队POC更新日志 NETGEAR ProSafe SSL VPN firmware platform.cgi SQL盲注漏洞(CVE-2022-29383) Yawcam HTTP服务器路...

 2026年3月15日 12:29
CVE-2025-1023: ChurchCRM – SQL Injection
漏洞标题 CVE-2025-1023: ChurchCRM - SQL Injection 漏洞描述 A vulnerability exists in ChurchCRM 5.13.0 and prior that allows an attacker to execute arbitrary SQL queries by exploiti...
2025年10月27日 09:22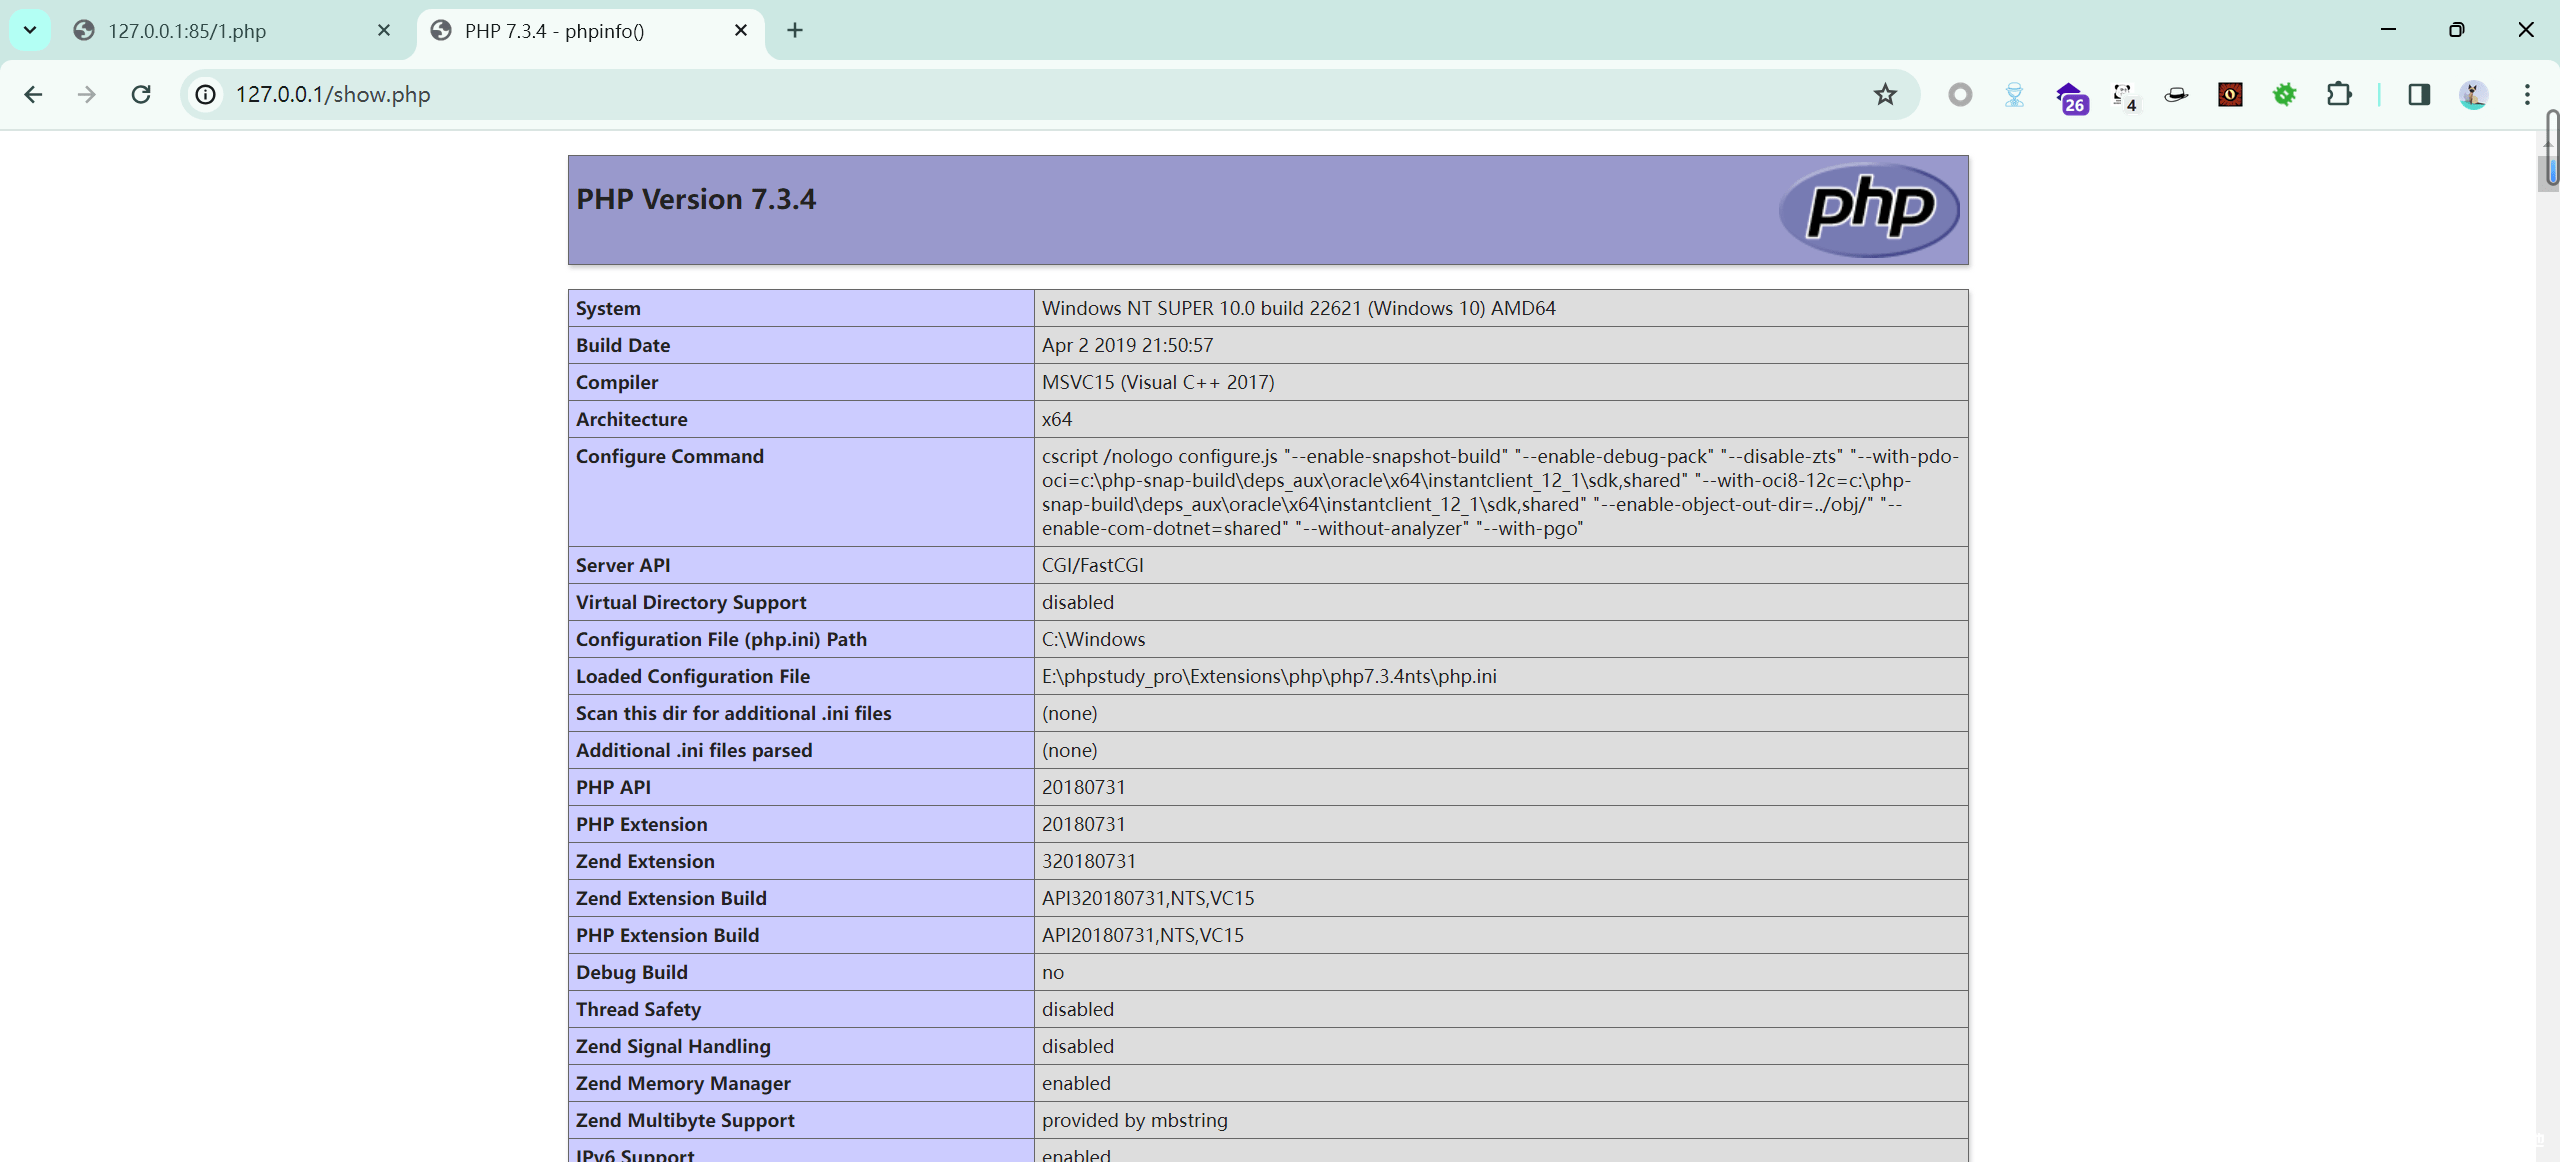
PhpStorm + Phpstudy 设置xdebug详细教程(避开大部分的坑)
前言 其实这篇教程本来是不准备出的,网上已经有很多很多类似的了(真的很烦把同一个东西抄过来抄过去,搜的人半天解决不了问题,很浪费精力的) 可是为什么有准备写这篇重复文章呢,昨天十分钟...
2024年2月16日 18:55CVE-2024-1209: LearnDash LMS < 4.10.2 - Sensitive Information Exposure via assignments
漏洞标题 CVE-2024-1209: LearnDash LMS < 4.10.2 - Sensitive Information Exposure via assignments 漏洞描述 The LearnDash LMS plugin for WordPress is vulnerable to Sensitive Inform...
2024年10月18日 13:05CVE-2022-40443: ZZCMS 2022 – Path Information Disclosure
漏洞标题 CVE-2022-40443: ZZCMS 2022 - Path Information Disclosure 漏洞描述 An absolute path traversal vulnerability in ZZCMS 2022 allows attackers to obtain sensitive information v...
2022年2月25日 15:18CVE-2024-48208: Pure-FTPd < 1.0.52 - Buffer Overflow
漏洞标题 CVE-2024-48208: Pure-FTPd < 1.0.52 - Buffer Overflow 漏洞描述 Pure-FTPd versions prior to 1.0.52 contain a buffer overflow vulnerability due to an out-of-bounds read in...
2024年10月14日 12:59Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
2020年5月6日 13:05CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting
漏洞标题 CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting 漏洞描述 The Wordpress plugin WooCommerce PDF Invoices &am...
2021年8月15日 00:57CVE-2017-20192: Formidable Forms < 2.05.02 - Cross-Site Scripting
漏洞标题 CVE-2017-20192: Formidable Forms < 2.05.02 - Cross-Site Scripting 漏洞描述 Formidable Form Builder for WordPress versions before 2.05.03 contains a stored cross-site sc...
2017年8月30日 13:50
Bluecmsv1.6-代码审计
前言 一直想学习代码审计,但是想着一大堆php函数都不清楚,要啃下这个大骨头太难了,就这样一拖一拖就到现在了,终于是下定决心,一点一点开始吧,看了大家的学习思路,基本都是从Bluecmsv1.6...
2023年6月3日 17:17CVE-2019-11013: Nimble Streamer <=3.5.4-9 - Local File Inclusion
漏洞标题 CVE-2019-11013: Nimble Streamer <=3.5.4-9 - Local File Inclusion 漏洞描述 Nimble Streamer 3.0.2-2 through 3.5.4-9 is vulnerable to local file inclusion. An attacker can...
2019年11月1日 02:56CVE-2023-21839: Oracle WebLogic Server – Unauthorized Access
漏洞标题 CVE-2023-21839: Oracle WebLogic Server - Unauthorized Access 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Su...
2023年2月5日 13:53Atlassian Confluence 远程代码执行漏洞(CVE-2021-26084)
漏洞标题 Atlassian Confluence 远程代码执行漏洞(CVE-2021-26084) 漏洞描述 Atlassian 官方发布了Confluence Server Webwork OGNL注入漏洞(CVE-2021-26084)的安全公告,远程攻击者在经过身份...
2021年5月25日 16:08CVE-2023-23492: Login with Phone Number – Cross-Site Scripting
漏洞标题 CVE-2023-23492: Login with Phone Number - Cross-Site Scripting 漏洞描述 Login with Phone Number, versions < 1.4.2, is affected by an reflected XSS vulnerability in the ...
2023年10月24日 21:06
2026年10月31日 11:45
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

