
最新发布第977页

CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 – Information Disclosure
漏洞标题 CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 - Information Disclosure 漏洞描述 JD Edwards EnterpriseOne Tools 9.2 is susceptible to information disclosure via the Mon...
 2020年6月22日 03:12
CVE-2017-16894: Laravel .env 配置文件泄露
漏洞标题 CVE-2017-16894: Laravel .env 配置文件泄露 漏洞描述 Laravel Framework是Taylor Otwell软件开发者开发的一款基于PHP的Web应用程序开发框架。 Laravel framework 5.5.21及之前的版本...
2017年9月16日 15:47
linux下获取文件的创建时间与实战教程_Linux
这篇文章主要给大家介绍了关于linux下获取文件的创建时间与实战的相关资料,文中通过示例代码介绍的非常详细,对大家学习或者使用linux系统具有一定的参考学习价值,需要的朋友们下面来一起学习...
2026年4月4日 11:45CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection
漏洞标题 CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection 漏洞描述 The HTML5 Video Player WordPress plugin before 2.5.27 does not sanitize and escape a param...
2024年2月17日 14:01CVE-2023-49103: OwnCloud – Phpinfo Configuration
漏洞标题 CVE-2023-49103: OwnCloud - Phpinfo Configuration 漏洞描述 An issue was discovered in ownCloud owncloud/graphapi 0.2.x before 0.2.1 and 0.3.x before 0.3.1. The graphapi app...
2023年6月24日 04:45
bugbounty技巧聚合20210831
漏洞报告 Gitlab #1113289 Guest users can create new test cases #475098 A profile page of a user can be denied from loading by appending .html to the username #1192460 A deactivated...
2022年3月10日 23:33CVE-2019-18394: Ignite Realtime Openfire <=4.4.2 - Server-Side Request Forgery
漏洞标题 CVE-2019-18394: Ignite Realtime Openfire <=4.4.2 - Server-Side Request Forgery 漏洞描述 Ignite Realtime Openfire through version 4.4.2 allows attackers to send arbitrar...
2019年4月13日 07:16CVE-2021-41691: openSIS Student Information System 8.0 SQL Injection
漏洞标题 CVE-2021-41691: openSIS Student Information System 8.0 SQL Injection 漏洞描述 openSIS Student Information System version 8.0 is susceptible to SQL injection via the studen...
2021年12月26日 21:41CVE-2020-24391: Mongo-Express – Remote Code Execution
漏洞标题 CVE-2020-24391: Mongo-Express - Remote Code Execution 漏洞描述 Mongo-Express before 1.0.0 is susceptible to remote code execution because it uses safer-eval to validate us...
2020年11月10日 00:12CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access
漏洞标题 CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access 漏洞描述 WordPress Welcart e-Commerce plugin before 2.8.5 is susceptible to arbitrary file ac...
2022年8月5日 18:34
在VMware虚拟机中安装windowsserver2016步骤详解(附激活教程及激活码)
前言 去msdn上面找了一下这个资源,给了一个种子链接,明明记得以前百度网盘可以下载的,结果这次就是不行,无奈下载一个迅雷,结果告诉我没会员不能下载,我都去搜索资源了,怎么可能还去付费...

 2026年3月27日 14:57
CVE-2019-19825: TOTOLINK/Realtek Routers – CAPTCHA Bypass
漏洞标题 CVE-2019-19825: TOTOLINK/Realtek Routers - CAPTCHA Bypass 漏洞描述 On certain TOTOLINK Realtek SDK based routers, the CAPTCHA text can be retrieved via a POST request to t...
2019年7月29日 05:05CVE-2016-1000136: WordPress heat-trackr 1.0 – Cross-Site Scripting
漏洞标题 CVE-2016-1000136: WordPress heat-trackr 1.0 - Cross-Site Scripting 漏洞描述 WordPress heat-trackr 1.0 contains a cross-site scripting vulnerability via heat-trackr_abtest_...
2016年5月15日 00:57CVE-2019-7192: QNAP QTS and Photo Station 6.0.3 – Remote Command Execution
漏洞标题 CVE-2019-7192: QNAP QTS and Photo Station 6.0.3 - Remote Command Execution 漏洞描述 This improper access control vulnerability allows remote attackers to gain unauthorized...
2019年2月8日 09:48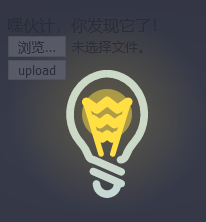
[ACTF2020 新生赛]Upload – buu刷题笔记
[ACTF2020 新生赛]Upload 考点 前端后缀名绕过的方式 php可执行文件后缀名的种类主界面 有一个灯泡,提示你上传文件,前端有验证,只能上传 jpg|png|gif 这个时候我们有两种方式绕过前端验证 直...
2022年4月14日 20:02CVE-2020-27615: WordPress Loginizer < 1.6.4 – Unauthenticated SQL Injection via `log` Parameter
漏洞标题 CVE-2020-27615: WordPress Loginizer < 1.6.4 – Unauthenticated SQL Injection via `log` Parameter 漏洞描述 The Loginizer plugin before 1.6.4 for WordPress allows SQL inj...
2020年4月10日 01:39
2026年10月31日 11:45
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

