
最新发布第978页

可疑样本静态分析检查清单
可疑样本静态分析检查清单 目标: 在不运行样本的前提下,快速识别可疑迹象,确认一个样本是否恶意。 此清单用于快速初步判断,不能100%确定样本是否恶意。 “是”的答案越多,样本恶意性...

 2026年3月1日 15:46

CVE-2023-2986: Abandoned Cart Lite for WooCommerce – Authentication Bypass
漏洞标题 CVE-2023-2986: Abandoned Cart Lite for WooCommerce - Authentication Bypass 漏洞描述 The Abandoned Cart Lite for WooCommerce plugin for WordPress is vulnerable to authentic...
 2023年1月12日 16:21
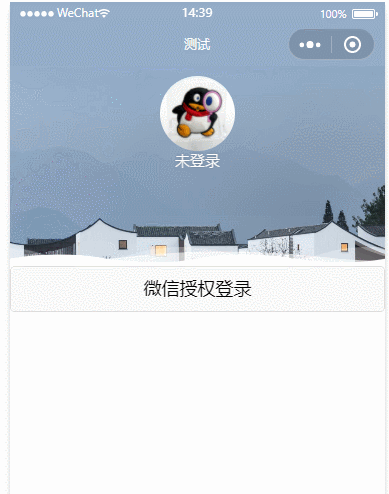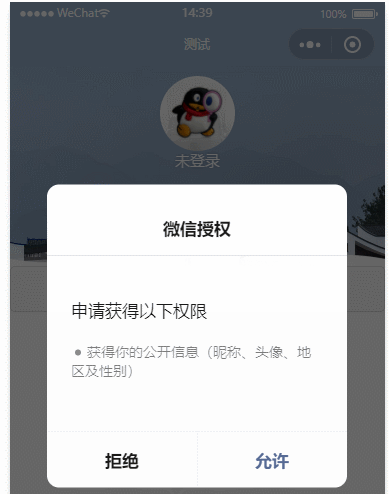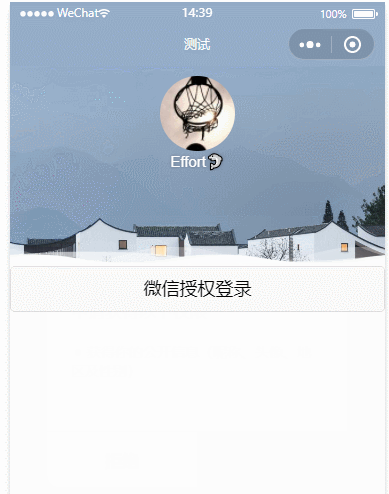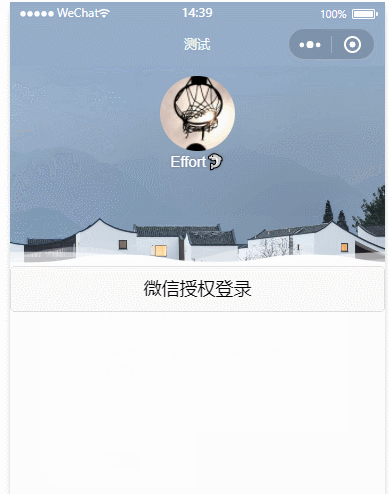
Python Flask微信小程序登录流程及登录api实现代码_Tomcat
这篇文章主要介绍了Python Flask微信小程序登录流程及登录api实现方法,本文通过实例代码给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一、先来看看...
2023年11月26日 20:35Nginx正向反向代理区别及原理解析_nginx
这篇文章主要介绍了Nginx正向反向代理区别及原理解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、正向代理和反向代理的区别 正向...
2024年3月31日 20:34CVE-2017-5521: Bypassing Authentication on NETGEAR Routers
漏洞标题 CVE-2017-5521: Bypassing Authentication on NETGEAR Routers 漏洞描述 NETGEAR routers before 6.0.10 allow remote attackers to bypass authentication and gain access to the ro...
2017年8月23日 02:48CVE-2016-8706: Memcached Server SASL Authentication – Remote Code Execution
漏洞标题 CVE-2016-8706: Memcached Server SASL Authentication - Remote Code Execution 漏洞描述 An integer overflow in process_bin_sasl_auth function in Memcached, which is responsib...
2016年2月23日 21:07CVE-2019-1821: Cisco Prime Infrastructure and Cisco Evolved Programmable Network Manager – Remote Code Execution
漏洞标题 CVE-2019-1821: Cisco Prime Infrastructure and Cisco Evolved Programmable Network Manager - Remote Code Execution 漏洞描述 Cisco Prime Infrastructure (PI) and Cisco Evolved...
2019年3月28日 09:24Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
2022年3月19日 18:48CVE-2023-2648: Weaver E-Office 9.5 – Remote Code Execution
漏洞标题 CVE-2023-2648: Weaver E-Office 9.5 - Remote Code Execution 漏洞描述 A vulnerability was found in Weaver E-Office 9.5. It has been classified as critical. This affects an u...
2023年4月15日 12:04CVE-2024-4956: Sonatype Nexus Repository Manager 3 – Local File Inclusion
漏洞标题 CVE-2024-4956: Sonatype Nexus Repository Manager 3 - Local File Inclusion 漏洞描述 Path Traversal in Sonatype Nexus Repository 3 allows an unauthenticated attacker to read...
2024年4月4日 17:01CVE-2024-30569: Netgear R6850 – Information Disclosure
漏洞标题 CVE-2024-30569: Netgear R6850 - Information Disclosure 漏洞描述 Netgear R6850 router firmware version V1.1.0.88 contains an information leakage vulnerability in the curren...
2024年12月11日 05:49
【Wireshark教程】如何通过语音获取对方IP 支持钉钉/QQ/WX
相关声明 本教程仅用于hvv、红蓝攻防对抗等专业领域,请勿用于非法用途。 相关阅读 Wireshark的功能实在强大,可以做很多事情,我们之前提供过很多篇教程 工具下载 Wireshark3.6.2官网稳定版下...
2023年1月13日 20:04CVE-2021-33221: CommScope Ruckus IoT Controller – Information Disclosure
漏洞标题 CVE-2021-33221: CommScope Ruckus IoT Controller - Information Disclosure 漏洞描述 CommScope Ruckus IoT Controller is susceptible to information disclosure vulnerabilities ...
2021年4月23日 15:04CVE-2008-6080: Joomla! ionFiles 4.4.2 – Local File Inclusion
漏洞标题 CVE-2008-6080: Joomla! ionFiles 4.4.2 - Local File Inclusion 漏洞描述 Joomla! ionFiles 4.4.2 is susceptible to local file inclusion in download.php in the ionFiles (com_io...
2008年6月22日 01:10CVE-2022-30525: Zyxel Firewall – OS Command Injection
漏洞标题 CVE-2022-30525: Zyxel Firewall - OS Command Injection 漏洞描述 An OS command injection vulnerability in the CGI program of Zyxel USG FLEX 100(W) firmware versions 5.00 thr...
2022年11月6日 20:51CVE-2019-8442: Atlassian Jira webroot leak
漏洞标题 CVE-2019-8442: Atlassian Jira webroot leak 漏洞描述 Atlassian Jira是澳大利亚Atlassian公司的一套缺陷跟踪管理系统。该系统主要用于对工作中各类问题、缺陷进行跟踪管理。 Atlassi...
2019年11月23日 23:34
2026年10月31日 11:45
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

