
最新发布第980页

CVE-2022-3933: WordPress Essential Real Estate <3.9.6 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2022-3933: WordPress Essential Real Estate <3.9.6 - Authenticated Cross-Site Scripting 漏洞描述 WordPress Essential Real Estate plugin before 3.9.6 contains an auth...
 2022年1月4日 07:49
CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
2020年9月17日 10:20Atlassian Jira XSS(CVE-2019-3402)
漏洞标题 Atlassian Jira XSS(CVE-2019-3402) 漏洞描述 8.1.1之前的Jira通过searchOwnerUserName参数中的ConfigurePortalPages.jspa资源包含跨站点脚本漏洞。 PoC代码 暂无
2019年7月1日 16:22CVE-2024-4257: BlueNet Technology Clinical Browsing System 1.2.1 – Sql Injection
漏洞标题 CVE-2024-4257: BlueNet Technology Clinical Browsing System 1.2.1 - Sql Injection 漏洞描述 A vulnerability was found in BlueNet Technology Clinical Browsing System 1.2.1. I...
2024年5月1日 20:55CVE-2022-29775: iSpy 7.2.2.0 – Authentication Bypass
漏洞标题 CVE-2022-29775: iSpy 7.2.2.0 - Authentication Bypass 漏洞描述 iSpy 7.2.2.0 contains an authentication bypass vulnerability. An attacker can craft a URL and possibly obtain...
2022年11月23日 14:11CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure
漏洞标题 CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure 漏洞描述 WordPress WPS Hide Login plugin before 1.9.1 is susceptible to incorrect authorization...
2021年12月1日 18:57CVE-2025-34038: Fanwei e-cology – SQL Injection
漏洞标题 CVE-2025-34038: Fanwei e-cology - SQL Injection 漏洞描述 Fanwei e-cology 8.0 contains a sql injection caused by unsanitized user input in the sql parameter of getdata.jsp,...
2025年8月23日 13:12CVE-2018-9118: WordPress 99 Robots WP Background Takeover Advertisements <=4.1.4 - Local File Inclusion
漏洞标题 CVE-2018-9118: WordPress 99 Robots WP Background Takeover Advertisements <=4.1.4 - Local File Inclusion 漏洞描述 WordPress 99 Robots WP Background Takeover Advertisemen...
2018年8月5日 08:24CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting
漏洞标题 CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting 漏洞描述 WordPress wpForo Forum plugin before 1.4.12 for WordPress allows unauthenticated reflec...
2018年1月26日 12:52CVE-2021-21315: Node.JS System Information Library <5.3.1 - Remote Command Injection
漏洞标题 CVE-2021-21315: Node.JS System Information Library <5.3.1 - Remote Command Injection 漏洞描述 Node.JS System Information Library System before version 5.3.1 is suscepti...
2021年7月16日 02:56Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965)
漏洞标题 Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965) 漏洞描述 S2-012中,包含特制请求参数的请求可用于将任意 OGNL代码注入属性,然后用作重定向地址的请求参数,这将导致进一步...
2013年4月29日 05:03
Linux 通过Rsync+Inotify实现本、异地远程数据实时同步功能_Linux
这篇文章主要介绍了Linux 通过Rsync+Inotify实现本、异地远程数据实时同步功能,需要的朋友可以参考下 0x0 测试环境 总部生产服务器与分部备份服务器要求实现异地数据备份,环境如下 **centos 6....
2024年2月10日 21:09拯救xmlrpc.php让WordPress瘫痪的的六种办法
我们都知道xmlrpc.php文件位于网站根目录下,其实我对这个文件一直没有放在心上,认为我的网站放在了阿里云,又加了服务器安全防护,况且WP团队早就解决了漏洞,不过确实存在一种另类的wordpres...

 2022年9月18日 10:51
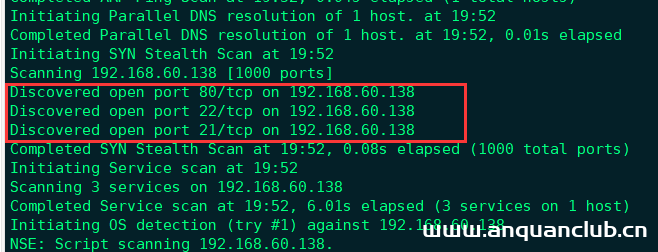
Vulnhub 靶场 DRIPPING BLUES: 1
前期准备: 靶机地址:http://www.vulnhub.com/entry/dripping-blues-1,744/ kali攻击机ip:192.168.60.128靶机地址:192.168.660.138 注:这个靶机有坑,别钻死胡同。 一、信息收集 1.使用nmap...
2022年3月26日 20:27CVE-2025-34026: Versa Concerto Actuator Endpoint – Authentication Bypass
漏洞标题 CVE-2025-34026: Versa Concerto Actuator Endpoint - Authentication Bypass 漏洞描述 An authentication bypass vulnerability affected the Spring Boot Actuator endpoints in Ver...
2025年4月20日 18:37CVE-2023-49494: DedeCMS v5.7.111 – Cross-Site Scripting
漏洞标题 CVE-2023-49494: DedeCMS v5.7.111 - Cross-Site Scripting 漏洞描述 DedeCMS v5.7.111 was discovered to contain a reflective cross-site scripting (XSS) vulnerability via the c...
2023年6月23日 18:30
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

