
最新发布第983页

CVE-2023-22518: Atlassian Confluence Server – Improper Authorization
漏洞标题 CVE-2023-22518: Atlassian Confluence Server - Improper Authorization 漏洞描述 All versions of Confluence Data Center and Server are affected by this unexploited vulnerabil...
 2023年12月28日 04:48
CVE-2022-1221: WordPress Gwyn’s Imagemap Selector <=0.3.3 - Cross-Site Scripting
漏洞标题 CVE-2022-1221: WordPress Gwyn's Imagemap Selector <=0.3.3 - Cross-Site Scripting 漏洞描述 Wordpress Gwyn's Imagemap Selector plugin 0.3.3 and prior contains a...
2022年6月29日 16:16CVE-2021-46069: Vehicle Service Management System 1.0 – Stored Cross Site Scripting
漏洞标题 CVE-2021-46069: Vehicle Service Management System 1.0 - Stored Cross Site Scripting 漏洞描述 Vehicle Service Management System 1.0 contains a stored cross-site scripting v...
2021年12月4日 05:07CVE-2025-52970: Fortinet FortiWeb – Authentication Bypass to Admin Privilege
漏洞标题 CVE-2025-52970: Fortinet FortiWeb - Authentication Bypass to Admin Privilege 漏洞描述 A improper handling of parameters in Fortinet FortiWeb versions 7.6.3 and below, vers...
2025年6月20日 21:26CVE-2024-45241: CentralSquare CryWolf – Path Traversal
漏洞标题 CVE-2024-45241: CentralSquare CryWolf - Path Traversal 漏洞描述 A traversal vulnerability in GeneralDocs.aspx in CentralSquare CryWolf (False Alarm Management) through 202...
2024年2月7日 19:11CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
2021年5月28日 06:20CVE-2024-21633: MobSF – Path Traversal
漏洞标题 CVE-2024-21633: MobSF - Path Traversal 漏洞描述 MobSF is vulnerable to an issue with apktool (CVE-2024-21633) that allows for RCE or arbitrary file writing. It does this t...
2024年1月9日 00:53CVE-2016-10940: WordPress zm-gallery plugin 1.0 SQL Injection
漏洞标题 CVE-2016-10940: WordPress zm-gallery plugin 1.0 SQL Injection 漏洞描述 zm-gallery plugin 1.0 for WordPress is susceptible to SQL injection via the order parameter. PoC代码
2016年2月5日 06:23CVE-2024-35693: WordPress 12 Step Meeting List Plugin <= 3.14.33 - Cross-Site Scripting
漏洞标题 CVE-2024-35693: WordPress 12 Step Meeting List Plugin <= 3.14.33 - Cross-Site Scripting 漏洞描述 Code for Recovery 12 Step Meeting List versions up to 3.14.33 contain a...
2024年2月23日 23:28
微软称发现针对乌克兰的破坏性恶意软件
2022年1月15日,微软安全团队发布了一份报告,称在乌克兰政府机构及与乌克兰密切合作的组织系统中观察到破坏性恶意软件。该恶意软件一旦被攻击者激活,受感染的计算机系统将无法运行。微软威胁...
2022年3月10日 23:34
在docker中开启sshd操作_docker
这篇文章主要介绍了在docker中开启sshd操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 首先在docker中安装openssh-server,安装完毕后切换到openssh-server的安装目录/e...
2023年1月13日 21:25CVE-2024-48248: NAKIVO Backup and Replication Solution – Unauthenticated Arbitrary File Read
漏洞标题 CVE-2024-48248: NAKIVO Backup and Replication Solution - Unauthenticated Arbitrary File Read 漏洞描述 NAKIVO Backup & Replication is a data protection solution used fo...
2024年2月12日 18:37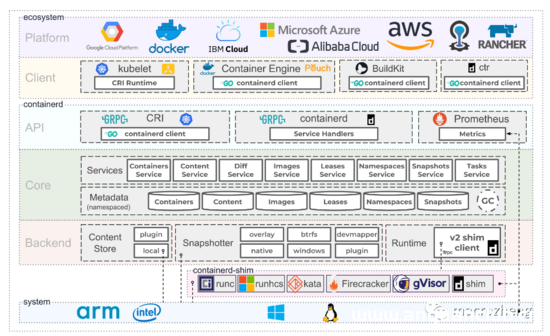
再见 Docker如何5分钟转型 containerd_docker
这篇文章主要介绍了再见 Docker如何5分钟转型 containerd,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 Docker作为非常流行的容器技术,之前经...
2022年8月31日 21:08CVE-2009-1496: Joomla! Cmimarketplace 0.1 – Local File Inclusion
漏洞标题 CVE-2009-1496: Joomla! Cmimarketplace 0.1 - Local File Inclusion 漏洞描述 Joomla! Cmimarketplace 0.1 is susceptible to local file inclusion because com_cmimarketplace allo...
2009年7月1日 02:01CVE-2021-38314: WordPress Redux Framework <=4.2.11 - Information Disclosure
漏洞标题 CVE-2021-38314: WordPress Redux Framework <=4.2.11 - Information Disclosure 漏洞描述 WordPress Redux Framework plugin through 4.2.11 is susceptible to information discl...
2021年2月6日 06:18CVE-2021-3654: Nova noVNC – Open Redirect
漏洞标题 CVE-2021-3654: Nova noVNC - Open Redirect 漏洞描述 Nova noVNC contains an open redirect vulnerability. An attacker can redirect a user to a malicious site and possibly obt...
2021年4月25日 06:18
2026年11月1日 11:45
2026年10月31日 11:45
2026年10月30日 11:45
2026年10月29日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

