
最新发布第988页

CVE-2024-12987: DrayTek Vigor – Command Injection
漏洞标题 CVE-2024-12987: DrayTek Vigor - Command Injection 漏洞描述 DrayTek Gateway devices (Vigor2960, Vigor300B, etc.) are vulnerable to command injection via the session paramet...
 2024年11月23日 19:35
ALIN MDaemon电子邮件服务器安全网关 V8.5.0 XML注入(CVE-2022-25356)
漏洞标题 ALIN MDaemon电子邮件服务器安全网关 V8.5.0 XML注入(CVE-2022-25356) 漏洞描述 ALIN MDaemon是电子邮件服务器安全网关,在V8.5.0版本中存在XML注入,可获取安全设置、管理员信息和产...
2022年7月28日 03:53CVE-2020-10548: rConfig 3.9.4 – SQL Injection
漏洞标题 CVE-2020-10548: rConfig 3.9.4 - SQL Injection 漏洞描述 rConfig 3.9.4 and previous versions have unauthenticated devices.inc.php SQL injection. Because nodes' password...
2020年10月28日 13:41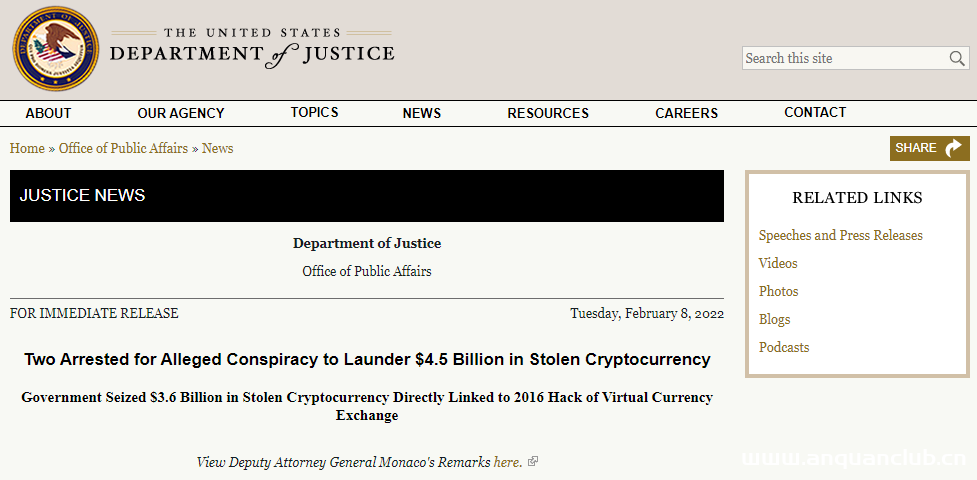
美国追回六年前黑客从Bitfinex窃取的现值36亿美元加密货币
2022年2月8日,美国司法部在一篇新闻稿中称,其以涉嫌共谋加密货币洗钱的罪名逮捕了一对夫妇,该案件涉及的加密货币价值约45亿美元,并且查明这些加密货币与六年前的一起黑客攻击案有关。总部设...
2022年3月10日 23:40CVE-2017-18527: Pagination by BestWebSoft < 1.0.7 - Cross-Site Scripting
漏洞标题 CVE-2017-18527: Pagination by BestWebSoft < 1.0.7 - Cross-Site Scripting 漏洞描述 The pagination plugin before 1.0.7 for WordPress has multiple XSS issues. PoC代码
2017年6月23日 11:14CVE-2022-23898: MCMS 5.2.5 – SQL Injection
漏洞标题 CVE-2022-23898: MCMS 5.2.5 - SQL Injection 漏洞描述 MCMS 5.2.5 contains a SQL injection vulnerability via the categoryId parameter in the file IContentDao.xml. An attacker...
2022年7月4日 19:08CVE-2020-9043: WordPress wpCentral <1.5.1 - Information Disclosure
漏洞标题 CVE-2020-9043: WordPress wpCentral <1.5.1 - Information Disclosure 漏洞描述 WordPress wpCentral plugin before 1.5.1 is susceptible to information disclosure. An attacke...
2020年9月9日 15:34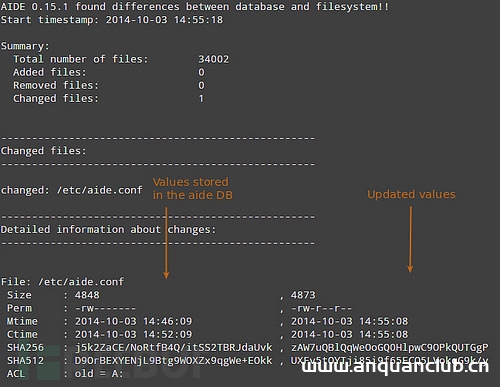
Linux如何基于AIDE检测文件系统完整性_Linux
这篇文章主要介绍了Linux如何基于AIDE检测文件系统完整性,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、AIDE AIDE(Advanced Intrusi...
2023年8月16日 20:49
【技术分享】去除logo免费生成网站的水印 方法通用
声明 本文章仅供技术科普,对案例中涉及的网站并无恶意,如需原图,请前往官网下载!!! 请勿用作非法用途,如有违反,概不负责!如有侵权,联系站长! 相关阅读 案例 1、打开百度,搜索logo在...

 2023年1月13日 19:10
CVE-2011-0049: Majordomo2 – SMTP/HTTP Directory Traversal
漏洞标题 CVE-2011-0049: Majordomo2 - SMTP/HTTP Directory Traversal 漏洞描述 A directory traversal vulnerability in the _list_file_get function in lib/Majordomo.pm in Majordomo 2 be...
2011年6月26日 17:05Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
2022年5月16日 23:40CVE-2024-40711: Veeam Backup & Replication – Unauthenticated
漏洞标题 CVE-2024-40711: Veeam Backup & Replication - Unauthenticated 漏洞描述 A deserialization of untrusted data vulnerability with a malicious payload can allow an unauthent...
2024年1月24日 20:13
Linux tac命令的实现示例_Linux
这篇文章主要介绍了Linux tac命令的实现示例,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 1.命令简介 tac(cat ...
2024年5月1日 21:29CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop
漏洞标题 CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when using ...
2005年2月16日 08:14CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年4月10日 16:26CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection
漏洞标题 CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection 漏洞描述 TOTOLink 多个设备 download.cgi文件存在远程命令执行漏洞,攻击者通过构造特殊的请求可以获取服务器...
2022年2月18日 00:11
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

