
最新发布第990页

CVE-2021-38647: Microsoft Open Management Infrastructure – Remote Code Execution
漏洞标题 CVE-2021-38647: Microsoft Open Management Infrastructure - Remote Code Execution 漏洞描述 Microsoft Open Management Infrastructure is susceptible to remote code execution ...
 2021年7月17日 14:33
CVE-2020-11450: MicroStrategy Web 10.4 – Information Disclosure
漏洞标题 CVE-2020-11450: MicroStrategy Web 10.4 - Information Disclosure 漏洞描述 MicroStrategy Web 10.4 is susceptible to information disclosure. The JVM configuration, CPU archit...
2020年1月11日 10:42
bugbounty技巧聚合20220126
漏洞报告 【Imgur】密码无长度 http://hackerone.com/reports/1411363 【Mail.ru 】子域接管 http://hackerone.com/reports/1348504 【Lark Technologies】能够使用 Lark 的 Compose Email 功能...
2022年3月10日 23:39CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
2024年8月2日 11:23
懒人快速验证漏洞小工具
前言 懒人必备 简简单单 快速验证 逐步完善 持续更新 该工具主要是方便自己整理容易复现的poc,批量测试,然后恰烂洞,大佬勿喷呀(抱住狗头) 因为以前收集的poc都是东一个西一个的存放,到用...

 2023年2月12日 18:33
CVE-2023-2745: WordPress Core <=6.2 - Directory Traversal
漏洞标题 CVE-2023-2745: WordPress Core <=6.2 - Directory Traversal 漏洞描述 WordPress Core is vulnerable to Directory Traversal in versions up to, and including, 6.2, via the ‘...
2023年1月12日 04:30CVE-2021-20792: WordPress Quiz and Survey Master <7.1.14 - Cross-Site Scripting
漏洞标题 CVE-2021-20792: WordPress Quiz and Survey Master <7.1.14 - Cross-Site Scripting 漏洞描述 WordPress Quiz and Survey Master plugin prior to 7.1.14 contains a cross-site s...
2021年12月28日 09:07CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection
漏洞标题 CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection 漏洞描述 The plugin does not sanitise and escape some parameter before using it in a SQL statement via ...
2022年8月29日 13:27CVE-2021-3122: NCR Command Center Agent 16.3 – Remote Command Execution
漏洞标题 CVE-2021-3122: NCR Command Center Agent 16.3 - Remote Command Execution 漏洞描述 CMCAgent in NCR Command Center Agent 16.3 on Aloha POS/BOH servers permits the submission ...
2021年5月18日 12:18CVE-2024-24565: CrateDB数据库任意文件读取漏洞
漏洞标题 CVE-2024-24565: CrateDB数据库任意文件读取漏洞 漏洞描述 CrateDB is a distributed SQL database that makes it simple to store and analyze massive amounts of data in real-time...
2024年9月13日 05:58CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年8月17日 10:29CVE-2017-15944: Palo Alto Network PAN-OS – Remote Code Execution
漏洞标题 CVE-2017-15944: Palo Alto Network PAN-OS - Remote Code Execution 漏洞描述 Palo Alto Network PAN-OS and Panorama before 6.1.19, 7.0.x before 7.0.19, 7.1.x before 7.1.14, an...
2017年5月21日 02:36CVE-2023-41265: Qlik Sense Enterprise – HTTP Request Smuggling
漏洞标题 CVE-2023-41265: Qlik Sense Enterprise - HTTP Request Smuggling 漏洞描述 An HTTP Request Tunneling vulnerability found in Qlik Sense Enterprise for Windows for versions May...
2023年1月11日 21:28CVE-2004-2687: Distccd v1 – Remote Code Execution
漏洞标题 CVE-2004-2687: Distccd v1 - Remote Code Execution 漏洞描述 distcc 2.x, as used in XCode 1.5 and others, when not configured to restrict access to the server port, allows r...
2004年2月22日 14:40CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass
漏洞标题 CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass 漏洞描述 The MStore API plugin for WordPress is vulnerable to authentication bypass in versions up to, and in...
2023年12月30日 14:04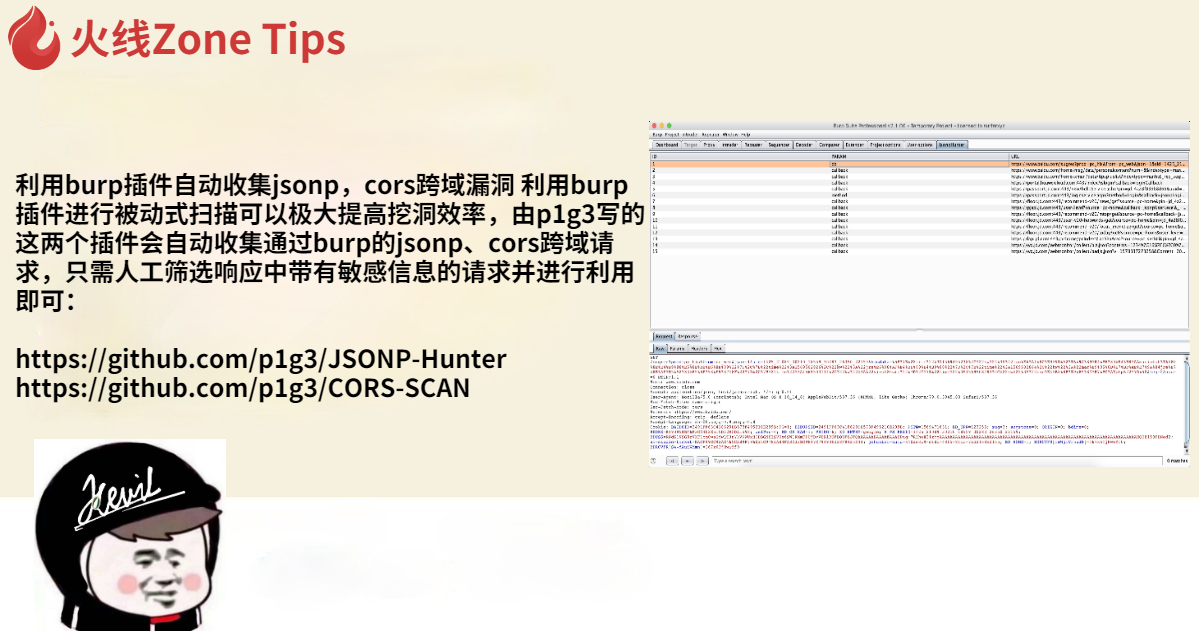
利用burp插件自动收集jsonp,cors跨域漏洞
利用burp插件进行被动式扫描可以极大提高挖洞效率,由p1g3写的这两个插件会自动收集通过burp的jsonp、cors跨域请求,只需人工筛选响应中带有敏感信息的请求并进行利用即可: http://github.com/...
2022年3月10日 23:35
2026年11月2日 11:45
2026年11月2日 11:45
2026年11月1日 11:45
2026年10月31日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

