
最新发布第996页

CVE-2023-32243: WordPress Elementor Lite 5.7.1 – Arbitrary Password Reset
漏洞标题 CVE-2023-32243: WordPress Elementor Lite 5.7.1 - Arbitrary Password Reset 漏洞描述 Improper Authentication vulnerability in WPDeveloper Essential Addons for Elementor allo...
 2023年2月21日 15:04

bugbounty技巧聚合20211027
挖洞技巧 What can I do with Open Redirect with OAuth? http://flex0geek.blogspot.com/2021/10/what-can-i-do-with-open-redirect-with.html Metacommunication and Bug Bounty Programs htt...
2022年3月10日 23:39CVE-2018-7314: Joomla SQL Inject
漏洞标题 CVE-2018-7314: Joomla SQL Inject 漏洞描述 Joomla SQL Inject fofa: app="Joomla" shodan: http.html:"Joomla" PoC代码
2018年2月15日 16:19CVE-2022-21587: Oracle E-Business Suite 12.2.3 -12.2.11 – Remote Code Execution
漏洞标题 CVE-2022-21587: Oracle E-Business Suite 12.2.3 -12.2.11 - Remote Code Execution 漏洞描述 Oracle E-Business Suite 12.2.3 through 12.2.11 is susceptible to remote code execu...
2022年11月26日 13:27CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 – SQL Injection
漏洞标题 CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 - SQL Injection 漏洞描述 SQL Injection exists in the Zh BaiduMap 3.0.0.1 component for Joomla! via the id parameter in...
2018年7月14日 08:14CVE-2020-7980: Satellian Intellian Aptus Web <= 1.24 - Remote Command Execution
漏洞标题 CVE-2020-7980: Satellian Intellian Aptus Web <= 1.24 - Remote Command Execution 漏洞描述 Intellian Aptus Web 1.24 allows remote attackers to execute arbitrary OS comman...
2020年2月21日 11:34CVE-2018-19439: Oracle Secure Global Desktop Administration Console 4.4 – Cross-Site Scripting
漏洞标题 CVE-2018-19439: Oracle Secure Global Desktop Administration Console 4.4 - Cross-Site Scripting 漏洞描述 Oracle Secure Global Desktop Administration Console 4.4 contains a ...
2018年6月7日 15:04CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
2023年8月21日 01:10CVE-2019-10717: BlogEngine.NET 3.3.7.0 – Local File Inclusion
漏洞标题 CVE-2019-10717: BlogEngine.NET 3.3.7.0 - Local File Inclusion 漏洞描述 BlogEngine.NET 3.3.7.0 allows /api/filemanager local file inclusion via the path parameter PoC代码
2019年8月16日 02:49CVE-2025-2010: WordPress JobWP Plugin <= 2.3.9 - SQL Injection
漏洞标题 CVE-2025-2010: WordPress JobWP Plugin <= 2.3.9 - SQL Injection 漏洞描述 The JobWP - Job Board, Job Listing, Career Page and Recruitment Plugin plugin for WordPress is v...
2025年3月31日 21:55CVE-2023-38035: Ivanti Sentry – Authentication Bypass
漏洞标题 CVE-2023-38035: Ivanti Sentry - Authentication Bypass 漏洞描述 A security vulnerability in MICS Admin Portal in Ivanti MobileIron Sentry versions 9.18.0 and below, which m...
2023年2月24日 21:43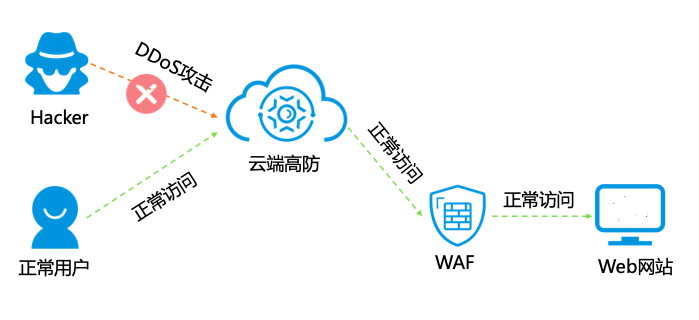
Nginx使用Lua模块实现WAF的原理解析_nginx
waf是通过执行一系列针对HTTP/HTTPS的安全策略来专门为Web应用提供保护的一款产品,本文重点给大家介绍Nginx使用Lua模块实现WAF的原理,需要的朋友参考下吧 目录一、WAF产生的背景二、什么是WAF...
2022年6月15日 09:06CVE-2023-30013: TOTOLink – Unauthenticated Command Injection
漏洞标题 CVE-2023-30013: TOTOLink - Unauthenticated Command Injection 漏洞描述 TOTOLINK X5000R V9.1.0u.6118_B20201102 and V9.1.0u.6369_B20230113 contain a command insertion vulnera...
2023年10月1日 03:00CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年12月25日 23:11(CVE-2021-26086) Atlassian Jira Server/Data Center 路径遍历漏洞
漏洞标题 (CVE-2021-26086) Atlassian Jira Server/Data Center 路径遍历漏洞 漏洞描述 (CVE-2021-26086) Atlassian Jira Server/Data Center 路径遍历漏洞 PoC代码 暂无
2021年2月17日 00:35CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting
漏洞标题 CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting 漏洞描述 WordPress Social Warfare plugin before 3.5.3 contains a cross-site scripting vulnerabilit...
2019年7月17日 08:34
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
2026年10月27日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

