
最新发布第999页

CVE-2016-1000134: WordPress HDW Video Gallery <=1.2 - Cross-Site Scripting
漏洞标题 CVE-2016-1000134: WordPress HDW Video Gallery <=1.2 - Cross-Site Scripting 漏洞描述 WordPress HDW Video Gallery 1.2 and before contains a cross-site scripting vulnerabi...
 2016年5月11日 20:27
CVE-2021-24276: WordPress Supsystic Contact Form <1.7.15 - Cross-Site Scripting
漏洞标题 CVE-2021-24276: WordPress Supsystic Contact Form <1.7.15 - Cross-Site Scripting 漏洞描述 WordPress Supsystic Contact Form plugin before 1.7.15 contains a cross-site scr...
2021年5月1日 13:43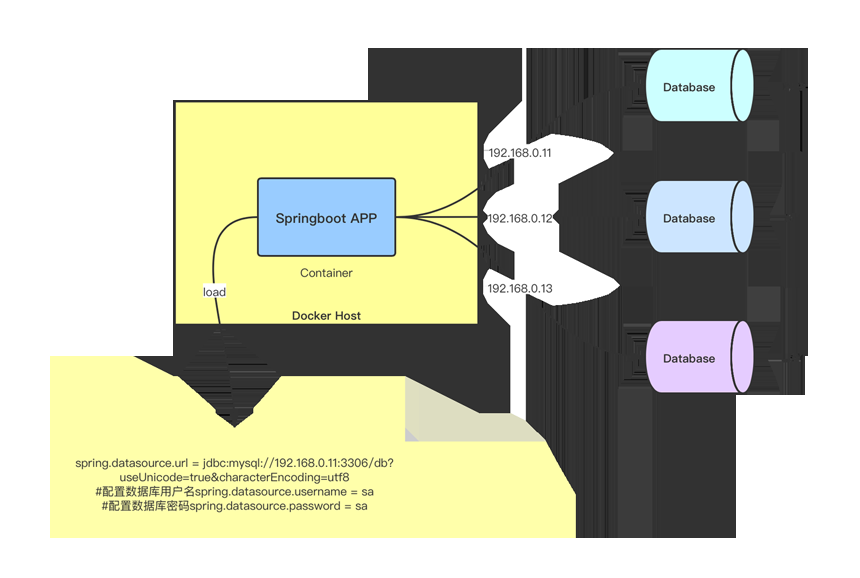
Docker如何给Springboot项目动态传参的实现方法_docker
这篇文章主要介绍了Docker如何给Springboot项目动态传参的实现方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧...
2023年2月20日 21:53CVE-2021-3223: Node RED Dashboard – Directory Traversal
漏洞标题 CVE-2021-3223: Node RED Dashboard - Directory Traversal 漏洞描述 Node-RED-Dashboard before 2.26.2 allows ui_base/js/..%2f directory traversal to read files. PoC代码
2021年5月18日 17:04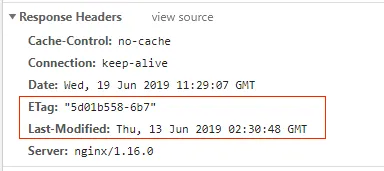
基于nginx设置浏览器协商缓存过程详解_nginx
这篇文章主要介绍了基于nginx设置浏览器协商缓存过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 这篇文章主要介绍了基于nginx设...
2026年3月21日 11:45CVE-2020-2103: Jenkins <=2.218 - Information Disclosure
漏洞标题 CVE-2020-2103: Jenkins <=2.218 - Information Disclosure 漏洞描述 Jenkins through 2.218, LTS 2.204.1 and earlier, is susceptible to information disclosure. An attacker c...
2020年10月13日 21:11CVE-2015-2067: Magento Server MAGMI – Directory Traversal
漏洞标题 CVE-2015-2067: Magento Server MAGMI - Directory Traversal 漏洞描述 Magento Server MAGMI (aka Magento Mass Importer) contains a directory traversal vulnerability in web/aja...
2015年12月20日 08:32CVE-2023-20864: VMware Aria Operations for Logs – Unauthenticated Remote Code Execution
漏洞标题 CVE-2023-20864: VMware Aria Operations for Logs - Unauthenticated Remote Code Execution 漏洞描述 VMware Aria Operations for Logs contains a deserialization vulnerability. ...
2023年12月26日 09:42CVE-2024-7097: WSO2 User Registration – Arbitrary Account Creation
漏洞标题 CVE-2024-7097: WSO2 User Registration - Arbitrary Account Creation 漏洞描述 The SOAP admin service in WSO2 products has a security vulnerability that allows the creation o...
2024年2月7日 09:37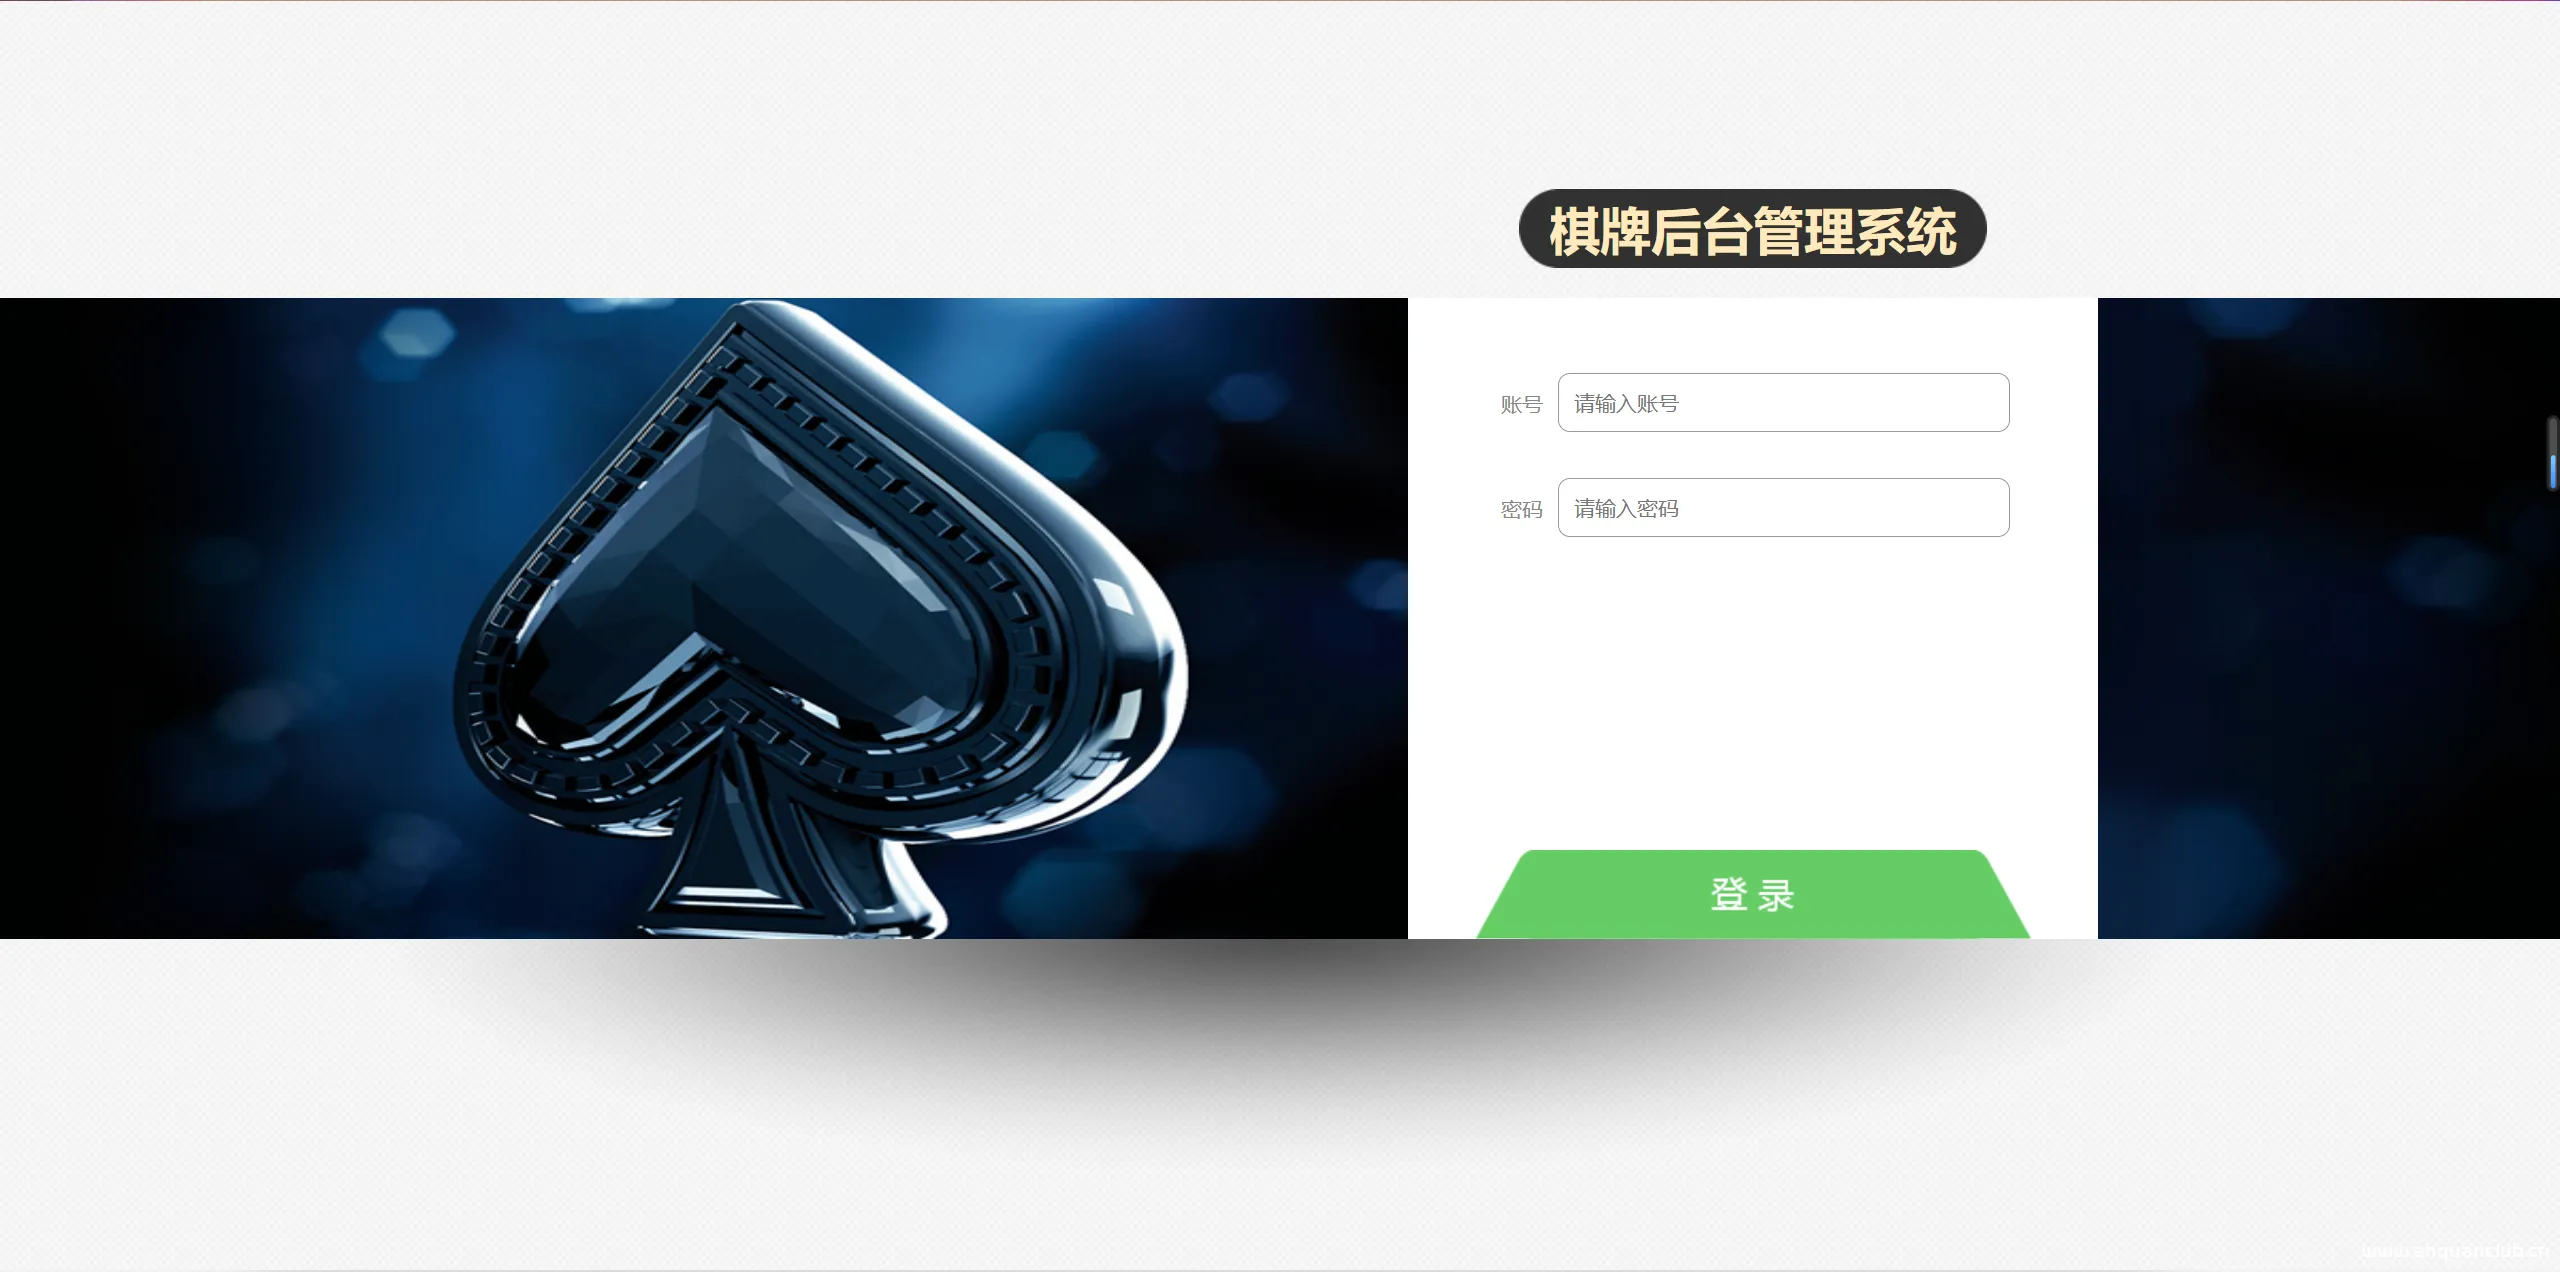
【防骗科普】菠菜网站是如何一步一步让你深陷泥潭,直到倾家荡产
论菠菜网站是如何一步一步让你深陷泥潭,直到倾家荡产的,今天借助一个同学分享的违规站点进行讲解,虽然该站点没有用户使用,但是远离赌博,人人有责! 第一部分 首先清楚今天的主角 因为主页...

 2023年1月13日 19:50
CVE-2022-2633: All-In-One Video Gallery <=2.6.0 - Server-Side Request Forgery
漏洞标题 CVE-2022-2633: All-In-One Video Gallery <=2.6.0 - Server-Side Request Forgery 漏洞描述 WordPress All-in-One Video Gallery plugin through 2.6.0 is susceptible to arbitra...
2022年8月31日 05:52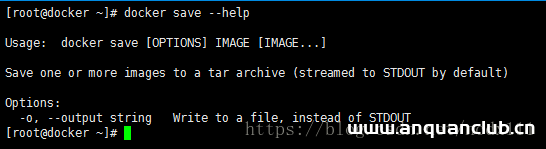
Docker镜像的导入导出代码实例_docker
这篇文章主要介绍了Docker镜像的导入导出代码实例,本文实例讲解的很透彻很明了,有需要的同学可以参考下 Docker镜像的导入导出 本文介绍Docker镜像的导入导出,用于迁移、备份、升级等场景,准...
2022年9月1日 21:13CVE-2022-40734: Laravel Filemanager v2.5.1 – Local File Inclusion
漏洞标题 CVE-2022-40734: Laravel Filemanager v2.5.1 - Local File Inclusion 漏洞描述 Laravel Filemanager (aka UniSharp) through version 2.5.1 is vulnerable to local file inclusion v...
2022年3月28日 00:03
Linux回收站机制实现过程及用法详解_Linux
这篇文章主要介绍了Linux回收站机制实现过程及用法详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 前言: linux系统下的rm是不可挽回...
2023年8月15日 20:59CVE-2021-22205: GitLab CE/EE – Remote Code Execution
漏洞标题 CVE-2021-22205: GitLab CE/EE - Remote Code Execution 漏洞描述 GitLab CE/EE starting from 11.9 does not properly validate image files that were passed to a file parser, res...
2021年4月30日 07:33CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the iNetLanka Multiple root (com_multir...
2010年11月4日 22:13
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
2026年10月7日 15:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

