
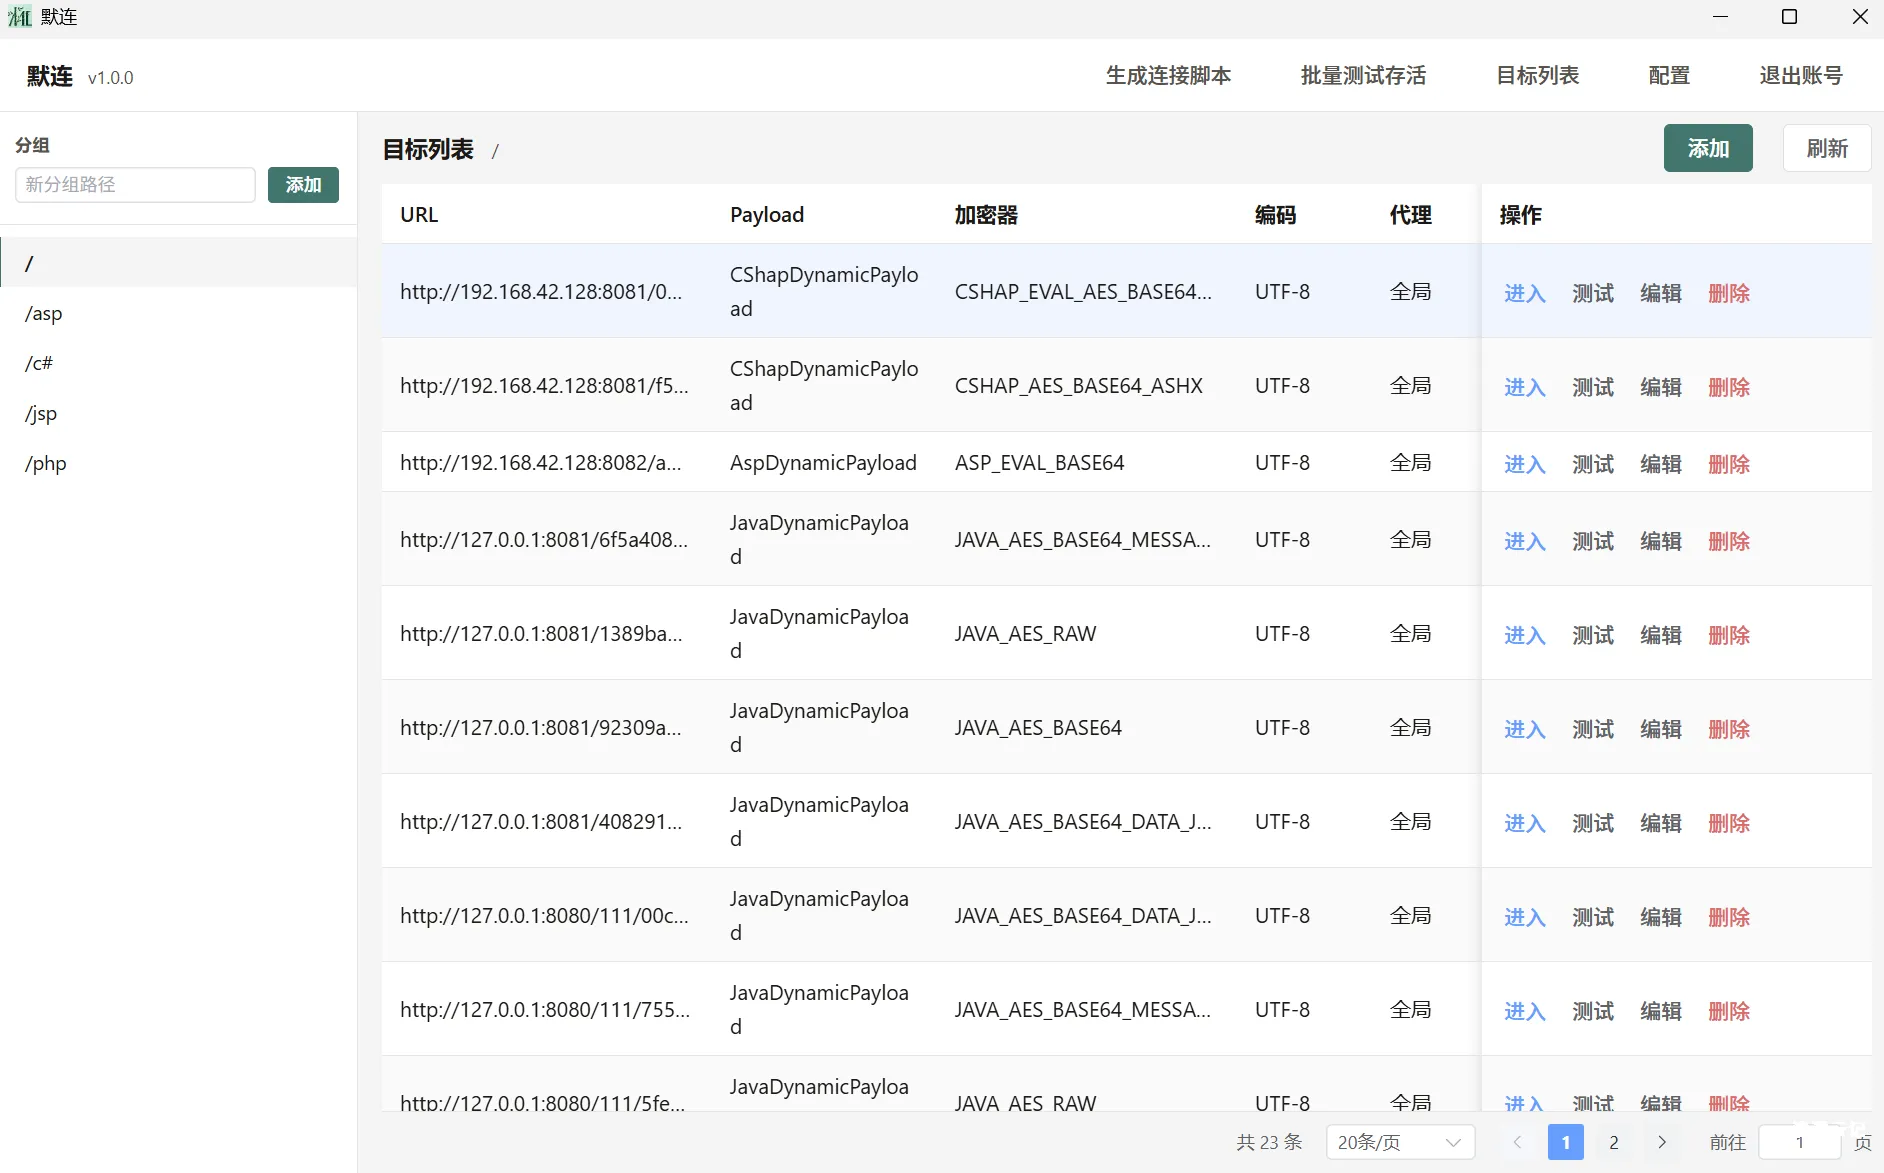
默连(morelian) 简简单单的一个webshell管理工具(支持常规的代码执行,文件管理等,并默认支持http与socks代理,兼容部分哥斯拉插件)
截止2026年5月1日,文末参与评论即可获取7天网站会员,数量有限,先到先得! 无需登录 前言 好久没有更新公众号了,最近又搓出来一个小工具,默连,寓意很简单,就是悄咪咪,静默连接。 工具支...

 2026年4月21日 10:31
EasyTools渗透测试工具箱(含下载地址)
项目地址: 如果EasyTools对您有所帮助的话,烦请点个小星星,谢谢 https://github.com/doki-byte/EasyTools 全功能版本下载地址: EasyTools渗透测试工具箱 一款综合性网络安全检测与运维工具...
2026年9月17日 18:46
积极响应净网行动,共同维护网络文明环境
提高法律意识 b.encenc.com(渗透云记)一直致力于打造专业的网络安全学习平台,为用户提供通俗易懂的专业知识讲解。然而,我们注意到一些不法分子利用本站的优质内容,因此我们对网站进行了整...
2026年3月1日 15:46
CVE-2024-33610: Sharp Multifunction Printers – Cookie Exposure
漏洞标题 CVE-2024-33610: Sharp Multifunction Printers - Cookie Exposure 漏洞描述 It was observed that Sharp printers are vulnerable to a listing of session cookies without authenti...
 2024年8月26日 01:09
CVE-2014-5187: Tom M8te (tom-m8te) Plugin 1.5.3 – Directory Traversal
漏洞标题 CVE-2014-5187: Tom M8te (tom-m8te) Plugin 1.5.3 - Directory Traversal 漏洞描述 Directory traversal vulnerability in the Tom M8te (tom-m8te) plugin 1.5.3 for WordPress allo...
2014年8月19日 09:23CVE-2018-11222: Pandora FMS <=7.0NG.722 - Remote Code Execution
漏洞标题 CVE-2018-11222: Pandora FMS <=7.0NG.722 - Remote Code Execution 漏洞描述 Pandora FMS versions <=7.0NG.722 are vulnerable to unauthenticated remote code execution by ...
2018年2月26日 19:53(CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞
漏洞标题 (CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞 漏洞描述 (CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞 PoC代码 暂无
2025年5月9日 02:24CVE-2021-21805: Advantech R-SeeNet 2.4.12 – OS Command Injection
漏洞标题 CVE-2021-21805: Advantech R-SeeNet 2.4.12 - OS Command Injection 漏洞描述 Advantech R-SeeNet 2.4.12 is susceptible to remote OS command execution via the ping.php script f...
2021年1月28日 01:41CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 – Local File Inclusion
漏洞标题 CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 - Local File Inclusion 漏洞描述 Oracle GlassFish Server Open Source Edition 3.0.1 (build 22) is vulnera...
2017年2月1日 18:49Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
2022年2月25日 13:38CVE-2019-2767: Oracle Business Intelligence Publisher – XML External Entity Injection
漏洞标题 CVE-2019-2767: Oracle Business Intelligence Publisher - XML External Entity Injection 漏洞描述 Oracle Business Intelligence Publisher is vulnerable to an XML external enti...
2019年3月4日 21:51CVE-2018-13379: Fortinet FortiOS – Credentials Disclosure
漏洞标题 CVE-2018-13379: Fortinet FortiOS - Credentials Disclosure 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.3 to 5.6.7 and 5.4.6 to 5.4.12 and FortiProxy 2.0.0, 1.2.0 to 1.2.8...
2018年4月1日 19:23CVE-2021-26475: EPrints 3.4.2 – Cross-Site Scripting
漏洞标题 CVE-2021-26475: EPrints 3.4.2 - Cross-Site Scripting 漏洞描述 EPrints 3.4.2 contains a reflected cross-site scripting vulnerability via the cgi/cal URI. PoC代码
2021年8月21日 04:32CVE-2023-3845: MooDating 1.2 – Cross-Site Scripting
漏洞标题 CVE-2023-3845: MooDating 1.2 - Cross-Site Scripting 漏洞描述 A vulnerability was found in mooSocial mooDating 1.2. It has been rated as problematic. Affected by this issue...
2023年3月8日 06:38CVE-2024-4348: osCommerce v4.0 – Cross-site Scripting
漏洞标题 CVE-2024-4348: osCommerce v4.0 - Cross-site Scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in osCommerce 4. Affected is an unknown func...
2024年11月27日 09:02CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion 漏洞描述 The News & Blog Designer Pack WordPre...
2023年3月15日 22:56CVE-2019-11253: Kubernetes API Server – YAML Parsing DoS (Billion Laughs)
漏洞标题 CVE-2019-11253: Kubernetes API Server - YAML Parsing DoS (Billion Laughs) 漏洞描述 The Kubernetes API server is vulnerable to a denial of service attack via YAML/JSON pars...
2019年1月12日 20:40CVE-2017-9805: Apache Struts2 S2-052 – Remote Code Execution
漏洞标题 CVE-2017-9805: Apache Struts2 S2-052 - Remote Code Execution 漏洞描述 The REST Plugin in Apache Struts 2.1.1 through 2.3.x before 2.3.34 and 2.5.x before 2.5.13 uses an XS...
2017年10月15日 03:08CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
2025年4月27日 03:34
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

