
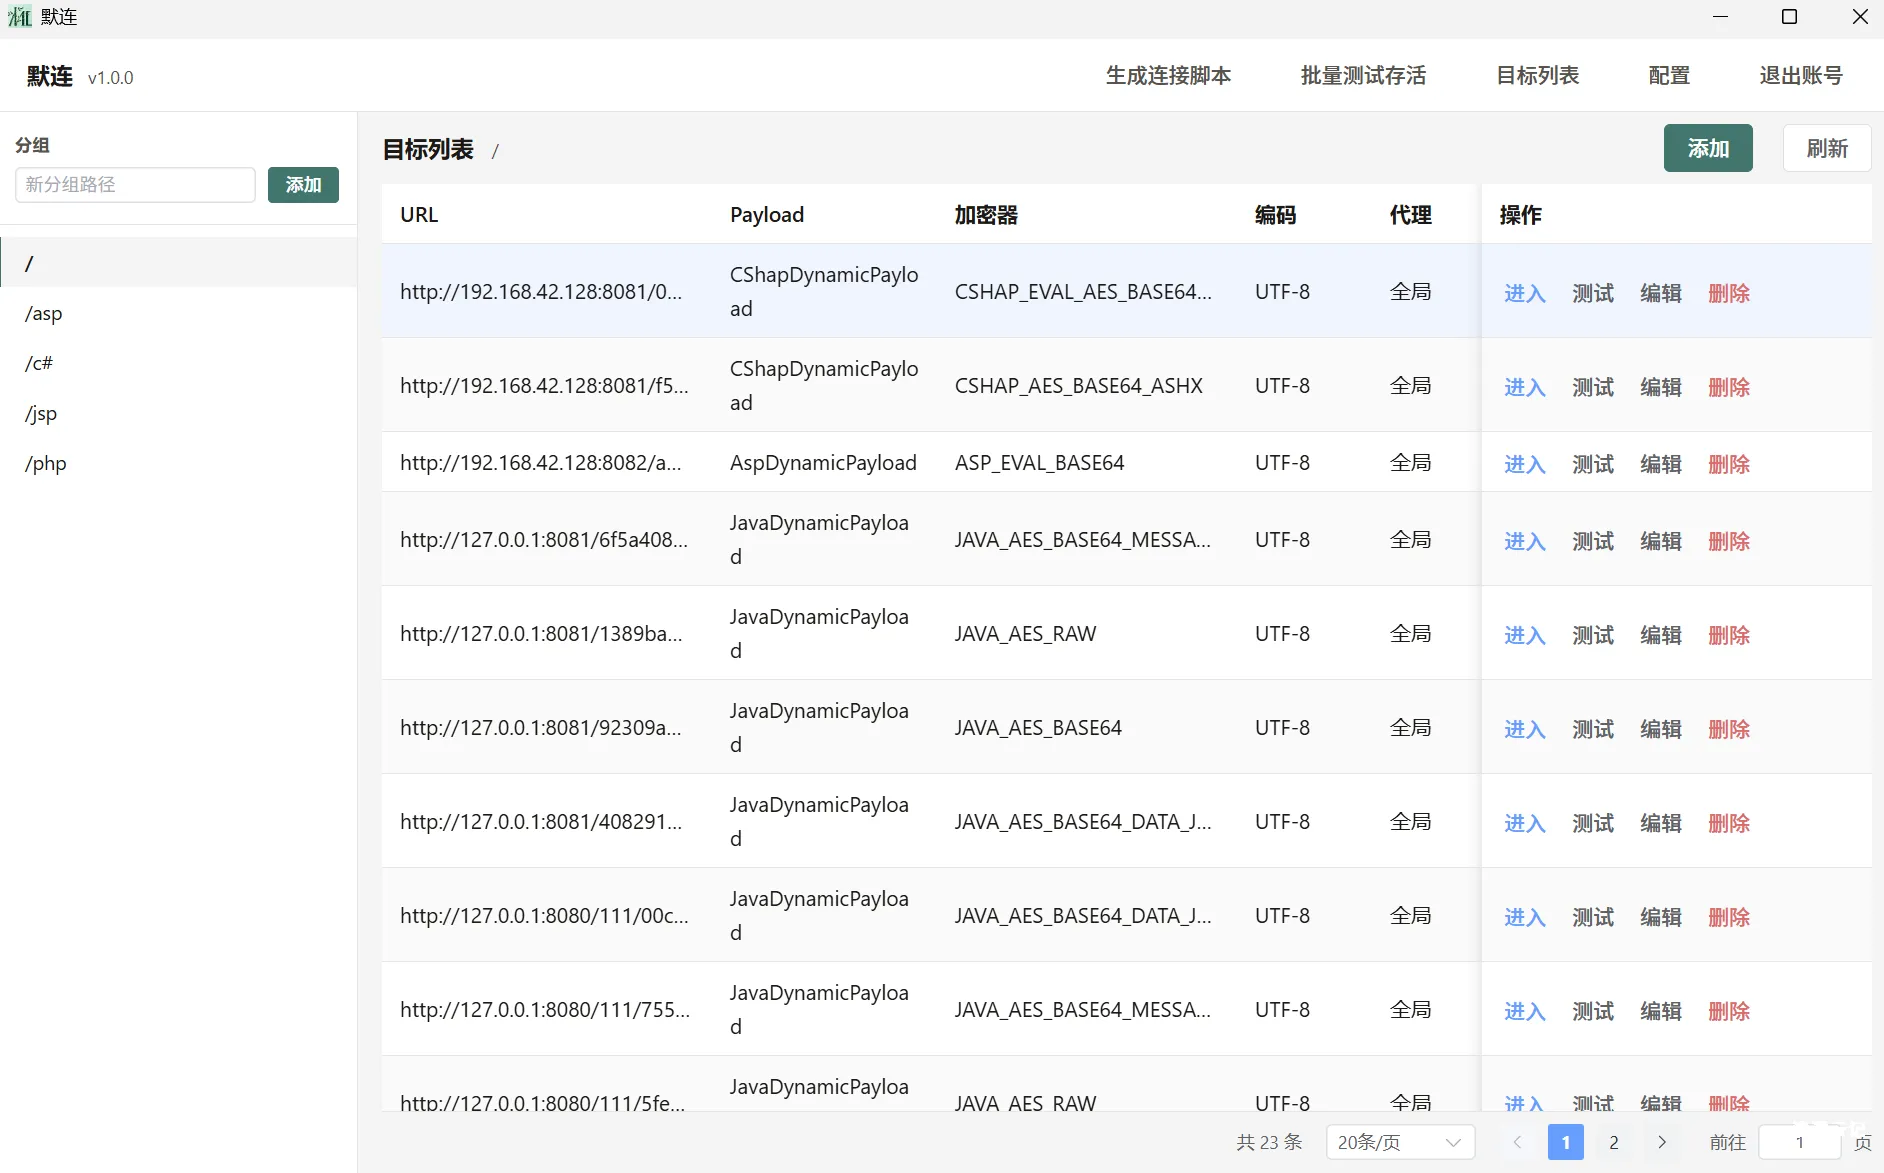
默连(morelian) 简简单单的一个webshell管理工具(支持常规的代码执行,文件管理等,并默认支持http与socks代理,兼容部分哥斯拉插件)
截止2026年5月1日,文末参与评论即可获取7天网站会员,数量有限,先到先得! 无需登录 前言 好久没有更新公众号了,最近又搓出来一个小工具,默连,寓意很简单,就是悄咪咪,静默连接。 工具支...

 2026年4月21日 10:31
EasyTools渗透测试工具箱(含下载地址)
项目地址: 如果EasyTools对您有所帮助的话,烦请点个小星星,谢谢 https://github.com/doki-byte/EasyTools 全功能版本下载地址: EasyTools渗透测试工具箱 一款综合性网络安全检测与运维工具...
2026年9月17日 18:46
积极响应净网行动,共同维护网络文明环境
提高法律意识 b.encenc.com(渗透云记)一直致力于打造专业的网络安全学习平台,为用户提供通俗易懂的专业知识讲解。然而,我们注意到一些不法分子利用本站的优质内容,因此我们对网站进行了整...
2026年3月1日 15:46
bugbounty技巧聚合20210818
漏洞报告 MTN Grou #1060518 No rate limit in otp code sending Mail.ru #1255676 Blind XSS Stored and CORS misconfiguration в отчете 'События' сервиса top.mail.ru...
 2022年3月10日 23:32

CVE-2021-22214: Gitlab CE/EE 10.5 – Server-Side Request Forgery
漏洞标题 CVE-2021-22214: Gitlab CE/EE 10.5 - Server-Side Request Forgery 漏洞描述 GitLab CE/EE versions starting from 10.5 are susceptible to a server-side request forgery vulnerab...
2021年5月20日 19:26CVE-2023-38992: Jeecg-Boot v3.5.1 – SQL Injection
漏洞标题 CVE-2023-38992: Jeecg-Boot v3.5.1 - SQL Injection 漏洞描述 SQL injection vulnerability via the title parameter at /sys/dict/loadTreeData in jeecg-boot v3.5.1. PoC代码
2023年2月9日 13:39CVE-2019-20224: Pandora FMS 7.0NG – Remote Command Injection
漏洞标题 CVE-2019-20224: Pandora FMS 7.0NG - Remote Command Injection 漏洞描述 Pandora FMS 7.0NG allows remote authenticated users to execute arbitrary OS commands via shell metach...
2019年4月25日 09:39CVE-2021-44228: Apache Log4j2 Remote Code Injection
漏洞标题 CVE-2021-44228: Apache Log4j2 Remote Code Injection 漏洞描述 Apache Log4j2 <=2.14.1 JNDI features used in configuration, log messages, and parameters do not protect aga...
2021年3月22日 06:27CVE-2018-11686: FlexPaper/FlowPaper 2.3.6 – Remote Code Execution
漏洞标题 CVE-2018-11686: FlexPaper/FlowPaper 2.3.6 - Remote Code Execution 漏洞描述 The Publish Service in FlexPaper (later renamed FlowPaper) 2.3.6 allows remote code execution vi...
2018年10月8日 08:06Linux下Makefile的编写与使用详解_Linux
目录MakefileMakefile文件命名和规则Makefile的工作原理Makefile变量Makefile函数Makefile clean规则Makefile 一个工程文件中的源文件可能有很多,并且不同的功能、模块等都放在不同的目录中,...
2022年6月15日 08:45CVE-2021-24452: WordPress W3 Total Cache <2.1.5 - Cross-Site Scripting
漏洞标题 CVE-2021-24452: WordPress W3 Total Cache <2.1.5 - Cross-Site Scripting 漏洞描述 WordPress W3 Total Cache plugin before 2.1.5 is susceptible to cross-site scripting via ...
2021年6月2日 06:18CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal
漏洞标题 CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal 漏洞描述 WordPress Backup Migration plugin versions up to 1.3.6 contain a path traversal and file va...
2023年12月27日 03:56CVE-2022-31137: Roxy-Wi options.py 远程命令执行漏洞
漏洞标题 CVE-2022-31137: Roxy-Wi options.py 远程命令执行漏洞 漏洞描述 Roxy-Wi options.py 存在远程命令执行漏洞,攻击者通过漏洞可以执行命令获取服务器权限 app="HAProxy-WI" P...
2022年3月20日 05:50CVE-2020-22208: 74cms – ajax_street.php ‘x’ SQL Injection
漏洞标题 CVE-2020-22208: 74cms - ajax_street.php 'x' SQL Injection 漏洞描述 SQL Injection in 74cms 3.2.0 via the x parameter to plus/ajax_street.php. PoC代码
2020年8月13日 01:04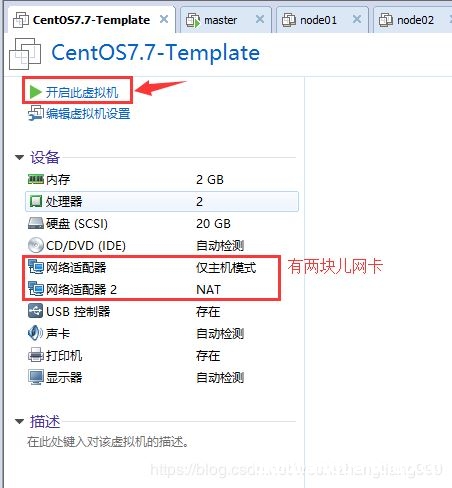
VMware安装Linux CentOS 7.7系统的详细教程_VMware
这篇文章主要介绍了VMware安装Linux CentOS 7.7系统的详细教程,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 如何在Vmware安...
2023年12月28日 21:12CVE-2021-36580: IceWarp Mail Server – Open Redirect
漏洞标题 CVE-2021-36580: IceWarp Mail Server - Open Redirect 漏洞描述 IceWarp Mail Server contains an open redirect via the referer parameter. This can lead to phishing attacks or ...
2021年1月6日 09:13CVE-2021-24681: Duplicate Page WordPress – Stored Cross-Site Scripting
漏洞标题 CVE-2021-24681: Duplicate Page WordPress - Stored Cross-Site Scripting 漏洞描述 Duplicate Page WordPress plugin <= 4.4.2 contains a stored cross-site scripting caused b...
2021年4月20日 21:04CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit – Broken Access Control
漏洞标题 CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit - Broken Access Control 漏洞描述 The Recover WooCommerc...
2025年3月3日 08:35(CVE-2020-36289) Atlassian Jira Server和Data Center QueryComponentRendererValue 信息泄露漏洞
漏洞标题 (CVE-2020-36289) Atlassian Jira Server和Data Center QueryComponentRendererValue 信息泄露漏洞 漏洞描述 (CVE-2020-36289) Atlassian Jira Server和Data Center QueryComponentRen...
2020年8月22日 09:26
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

