
最新发布第113页
ThinkPHP 漏洞利用工具
在Github上搜寻好用的安全工具,来充实武器库,实属一大乐趣所在。 当看到ThinkPHP十年磨一剑的提示,那么今天这里分享的工具就可以派上用场了,一键检测ThinkPHP全版本漏洞。 01、TPscan 一键T...

 2022年6月1日 20:13

CVE-2025-34077: WordPress Pie Register <= 3.7.1.4 - Authentication Bypass
漏洞标题 CVE-2025-34077: WordPress Pie Register <= 3.7.1.4 - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists in the WordPress Pie Register plugin ≤...
 2025年9月13日 07:31

[护网杯 2018]easy_tornado WriteUp – buu刷题笔记(超级详细!)
[护网杯 2018]easy_tornado 打开题目后,首先发现3个超链接 依次查看文件内容 flag.txt /flag.txt flag in /fllllllllllllag welconme.txt /welcome.txt render hints.txt /hints.txt md5(cooki...
2022年4月17日 16:58CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 – Local File Inclusion
漏洞标题 CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the givesight PowerMail Pro (com_powermail) com...
2010年12月14日 08:22CVE-2023-28121: WooCommerce Payments – Unauthorized Admin Access
漏洞标题 CVE-2023-28121: WooCommerce Payments - Unauthorized Admin Access 漏洞描述 An issue in WooCommerce Payments plugin for WordPress (versions 5.6.1 and lower) allows an unauth...
2023年4月23日 22:09
针对HTTP的隐藏攻击面分析
英文版:http://portswigger.net/research/cracking-the-lens-targeting-https-hidden-attack-surface 中文版: 针对HTTP的隐藏攻击面分析(上)http://www.anquanke.com/post/id/86578 针对HTT...
2022年3月10日 23:37Appspace服务端请求伪造漏洞(CVE-2021-27670)
漏洞标题 Appspace服务端请求伪造漏洞(CVE-2021-27670) 漏洞描述 Appspace 6.2.4存在漏洞,允许通过api/v1/core/proxy/jsonprequest接口来进行服务端请求伪造,危害系统安全。 PoC代码 暂无
2021年2月12日 09:14Carel pCOWeb
漏洞标题 Carel pCOWeb <B1.2.4 XSS (CVE-2019-11370) 漏洞描述 B1.2.4之前的Carel pCOWeb易受存储的跨站点脚本攻击,如config/pw_snmp.html“系统联系人”字段所示。 PoC代码 暂无
2019年5月31日 21:08CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059
漏洞标题 CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059 漏洞描述 Apache Struts 2.0.0 to 2.5.20 forced double OGNL evaluation when evaluated on raw user inp...
2019年10月19日 15:06CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
2025年12月26日 14:21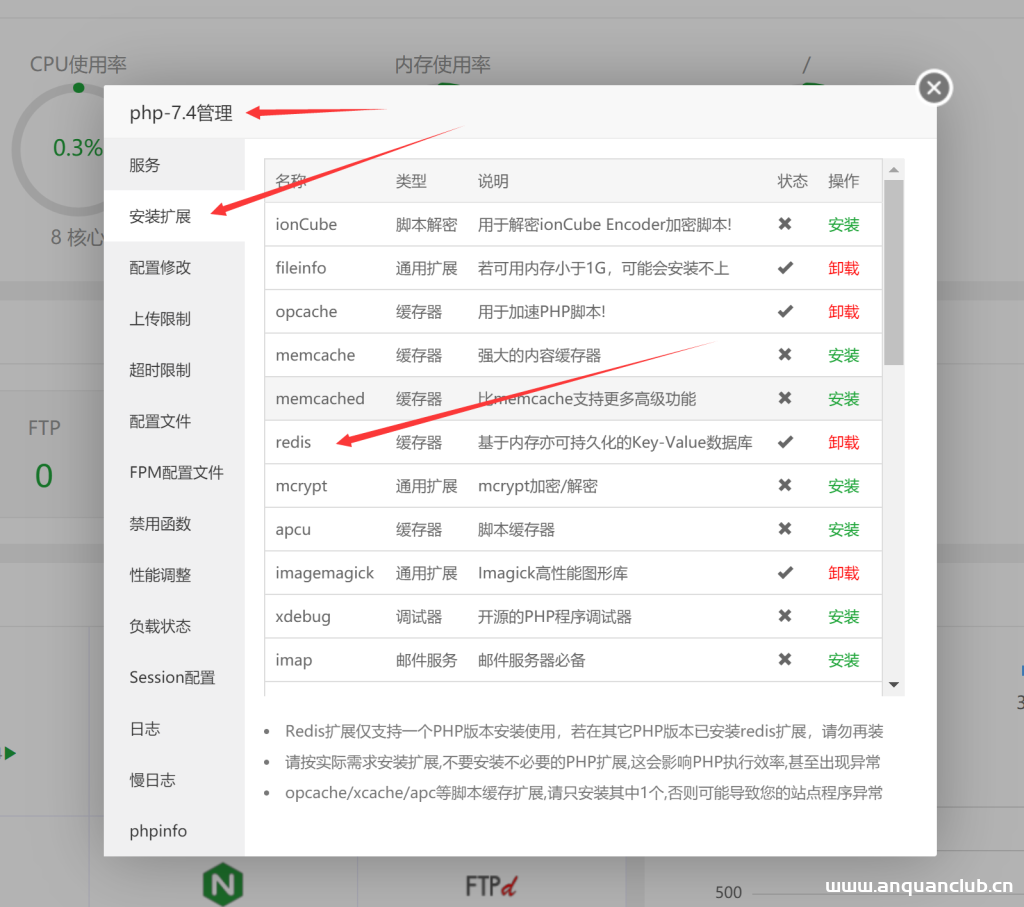
wordpress网站使用Redis缓存和PHP opcache为网站加速详细图文教程
相信建站的朋友都十分关心网站速度问题了,子比主题一直在强调极速优化这次词语,同时在之前的很多文章中我也简单的介绍了子比主题的关于速度优化的一些原理。理论上来讲使用子比主题搭配一个不...
2022年5月20日 20:05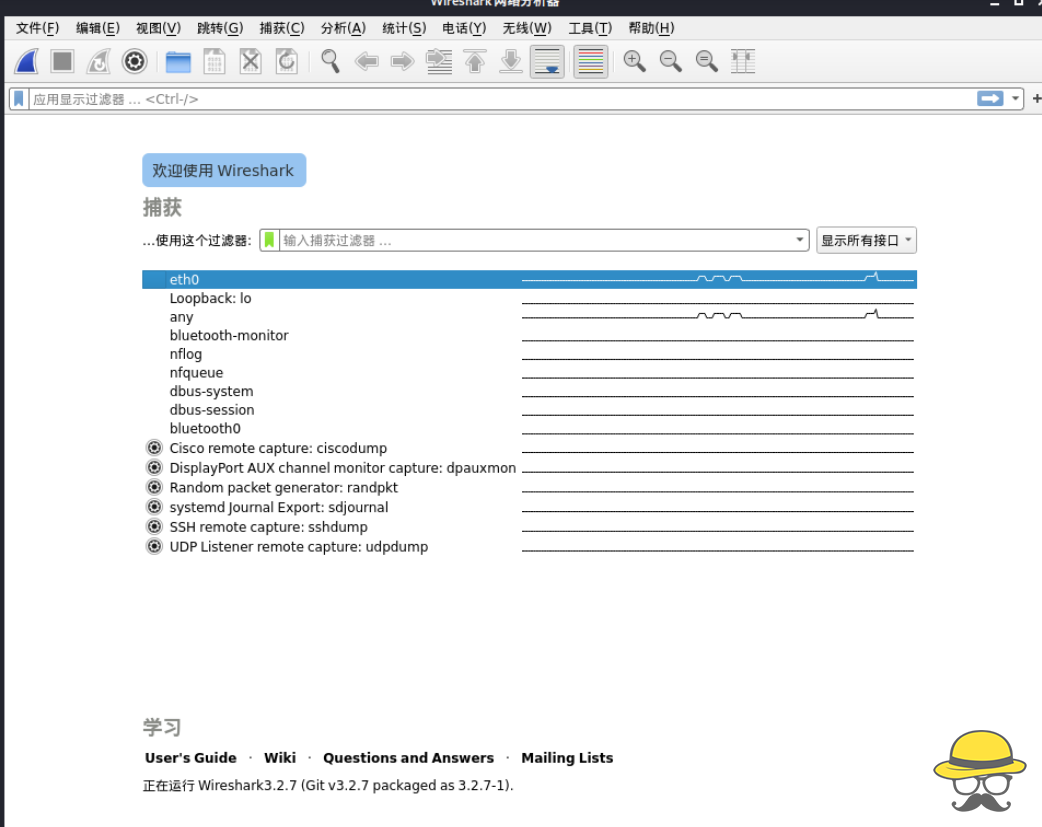
Wireshark分析HTTPS流量
Wireshark分析HTTPS流量 Kali Linux下使用Wireshark分析HTTPS流量 系统环境Kali-linux 5.9.0 软件版本Wireshark3.2.7 这里使用eth0网卡 可以看到有数据来源和去向以及具体数据包情况 数据包比较...
2023年1月13日 20:24IDEA/PyCharm/Webstorm/Phpstorm等 Jetbrains全家桶激活码
相关阅读 之前我们分享了最新的IDEA、PyCharm激活教程 很多网友都问Jetbrains其他产品激活码有吗?我们今天分享完整的激活码,激活方式您可以参考上面的教程,几乎是完全一致的。 激活工具下载 ...
2022年12月19日 10:40CVE-2021-46417: Franklin Fueling Systems Colibri Controller Module 1.8.19.8580 – Local File Inclusion
漏洞标题 CVE-2021-46417: Franklin Fueling Systems Colibri Controller Module 1.8.19.8580 - Local File Inclusion 漏洞描述 Franklin Fueling Systems Colibri Controller Module 1.8.19.85...
2021年11月27日 14:36
[GXYCTF2019]禁止套娃 – buu刷题笔记
打开环境就只是提示,flag在哪里呢?,查看源代码,和网络加载都没有什么线索,只能扫一下目录,但是buu靶场一扫目录就429,难受,看了大佬的笔记,有一个git文件泄露。 git源码泄露,可以看看...
2022年6月5日 16:37
[BJDCTF2020]Easy MD5 – buu刷题笔记
打开连接,只有一个输入框,测试了半天sql,并没有什么鸟用 使用burp抓包,查看报文头发现有信息隐藏在hint里面 select * from 'admin' where password=md5($pass,true) md5($pass,true)知识补...
2022年4月18日 11:02
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

