
最新发布第158页

CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
 2024年7月4日 13:18
CVE-2024-34257: TOTOLINK EX1800T TOTOLINK EX1800T – Command Injection
漏洞标题 CVE-2024-34257: TOTOLINK EX1800T TOTOLINK EX1800T - Command Injection 漏洞描述 TOTOLINK EX1800T V9.1.0cu.2112_B20220316 has a vulnerability in the apcliEncrypType paramete...
2024年7月17日 13:25CVE-2021-24488: WordPress Post Grid <2.1.8 - Cross-Site Scripting
漏洞标题 CVE-2021-24488: WordPress Post Grid <2.1.8 - Cross-Site Scripting 漏洞描述 WordPress Post Grid plugin before 2.1.8 contains a reflected cross-site scripting vulnerabili...
2021年12月1日 08:59CVE-2025-1974: CVE-2025-1974
漏洞标题 CVE-2025-1974: CVE-2025-1974 漏洞描述 shodan: ssl:"ingress-nginx" port:8443 Kubernetes ingress-nginx是云原生计算基金会(Cloud Native Computing Foundation)开源...
2025年9月7日 10:50CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection
漏洞标题 CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection 漏洞描述 The LearnPress WordPress LMS Plugin plugin for WordPress is vulnerable to time-based ...
2024年11月8日 06:27CVE-2011-3600: Apache OFBiz – XML External Entity Injection
漏洞标题 CVE-2011-3600: Apache OFBiz - XML External Entity Injection 漏洞描述 The /webtools/control/xmlrpc endpoint in OFBiz XML-RPC event handler is exposed to External Entity Inj...
2011年12月27日 15:59CVE-2022-31793: muhttpd <=1.1.5 - Local Inclusion
漏洞标题 CVE-2022-31793: muhttpd <=1.1.5 - Local Inclusion 漏洞描述 muhttpd 1.1.5 and before are vulnerable to unauthenticated local file inclusion. The vulnerability allows ret...
2022年5月12日 11:08CVE-2016-3081: Apache S2-032 Struts – Remote Code Execution
漏洞标题 CVE-2016-3081: Apache S2-032 Struts - Remote Code Execution 漏洞描述 Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when dynamic method invoca...
2016年3月18日 15:41CVE-2020-27838: KeyCloak – Information Exposure
漏洞标题 CVE-2020-27838: KeyCloak - Information Exposure 漏洞描述 A flaw was found in keycloak in versions prior to 13.0.0. The client registration endpoint allows fetching informa...
2020年11月7日 11:58CVE-2023-29357: Microsoft SharePoint – Authentication Bypass
漏洞标题 CVE-2023-29357: Microsoft SharePoint - Authentication Bypass 漏洞描述 Microsoft SharePoint Server Elevation of Privilege Vulnerability PoC代码
2023年1月31日 10:30CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年9月27日 20:00CVE-2004-0656: Pure-FTPd ≤ 1.0.18 – DoS via Connection Limit Exhaustion
漏洞标题 CVE-2004-0656: Pure-FTPd ≤ 1.0.18 - DoS via Connection Limit Exhaustion 漏洞描述 Pure-FTPd versions ≤ 1.0.18 are vulnerable to denial of service through connection limit...
2004年7月7日 14:07CVE-2022-1906: WordPress Copyright Proof <=4.16 - Cross-Site-Scripting
漏洞标题 CVE-2022-1906: WordPress Copyright Proof <=4.16 - Cross-Site-Scripting 漏洞描述 WordPress Copyright Proof plugin 4.16 and prior contains a cross-site scripting vulnerab...
2022年9月16日 14:33CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting
漏洞标题 CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting 漏洞描述 The plugin was affected by a reflected XSS in custom-face...
2021年10月10日 08:34CVE-2017-5638: Apache Struts 2 – Remote Command Execution S2-045 S2-046
漏洞标题 CVE-2017-5638: Apache Struts 2 - Remote Command Execution S2-045 S2-046 漏洞描述 Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 is vulnerable to remote comm...
2017年3月4日 00:23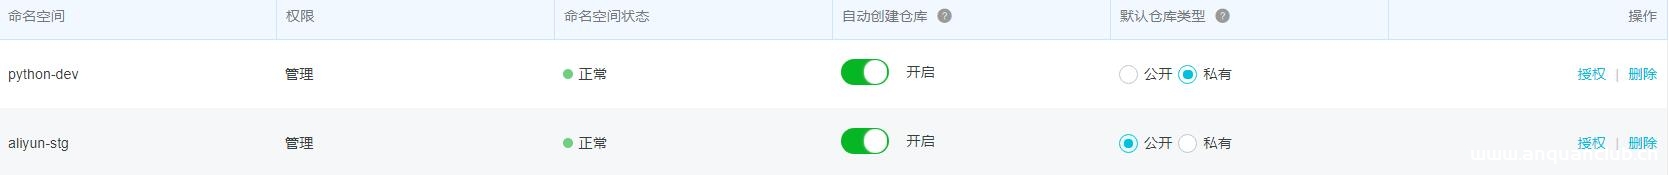
Docker 配置阿里云容器服务操作_docker
这篇文章主要介绍了Docker 配置阿里云容器服务操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 配置阿里云Docker容器服务 登录 阿里云镜像服务控制台 首先要有一个自己...
2023年2月7日 20:22
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

