
最新发布第20页

CVE-2019-8086: Adobe Experience Manager – XML External Entity Injection
漏洞标题 CVE-2019-8086: Adobe Experience Manager - XML External Entity Injection 漏洞描述 Adobe Experience Manager 6.5, 6.4, 6.3 and 6.2 are susceptible to XML external entity inje...
 2019年11月29日 05:20
CVE-2025-54309: CrushFTP – Authentication Bypass Race Condition
漏洞标题 CVE-2025-54309: CrushFTP - Authentication Bypass Race Condition 漏洞描述 CrushFTP 10 before 10.8.5 and 11 before 11.3.4_23, when the DMZ proxy feature is not used, mishand...
2025年4月24日 04:42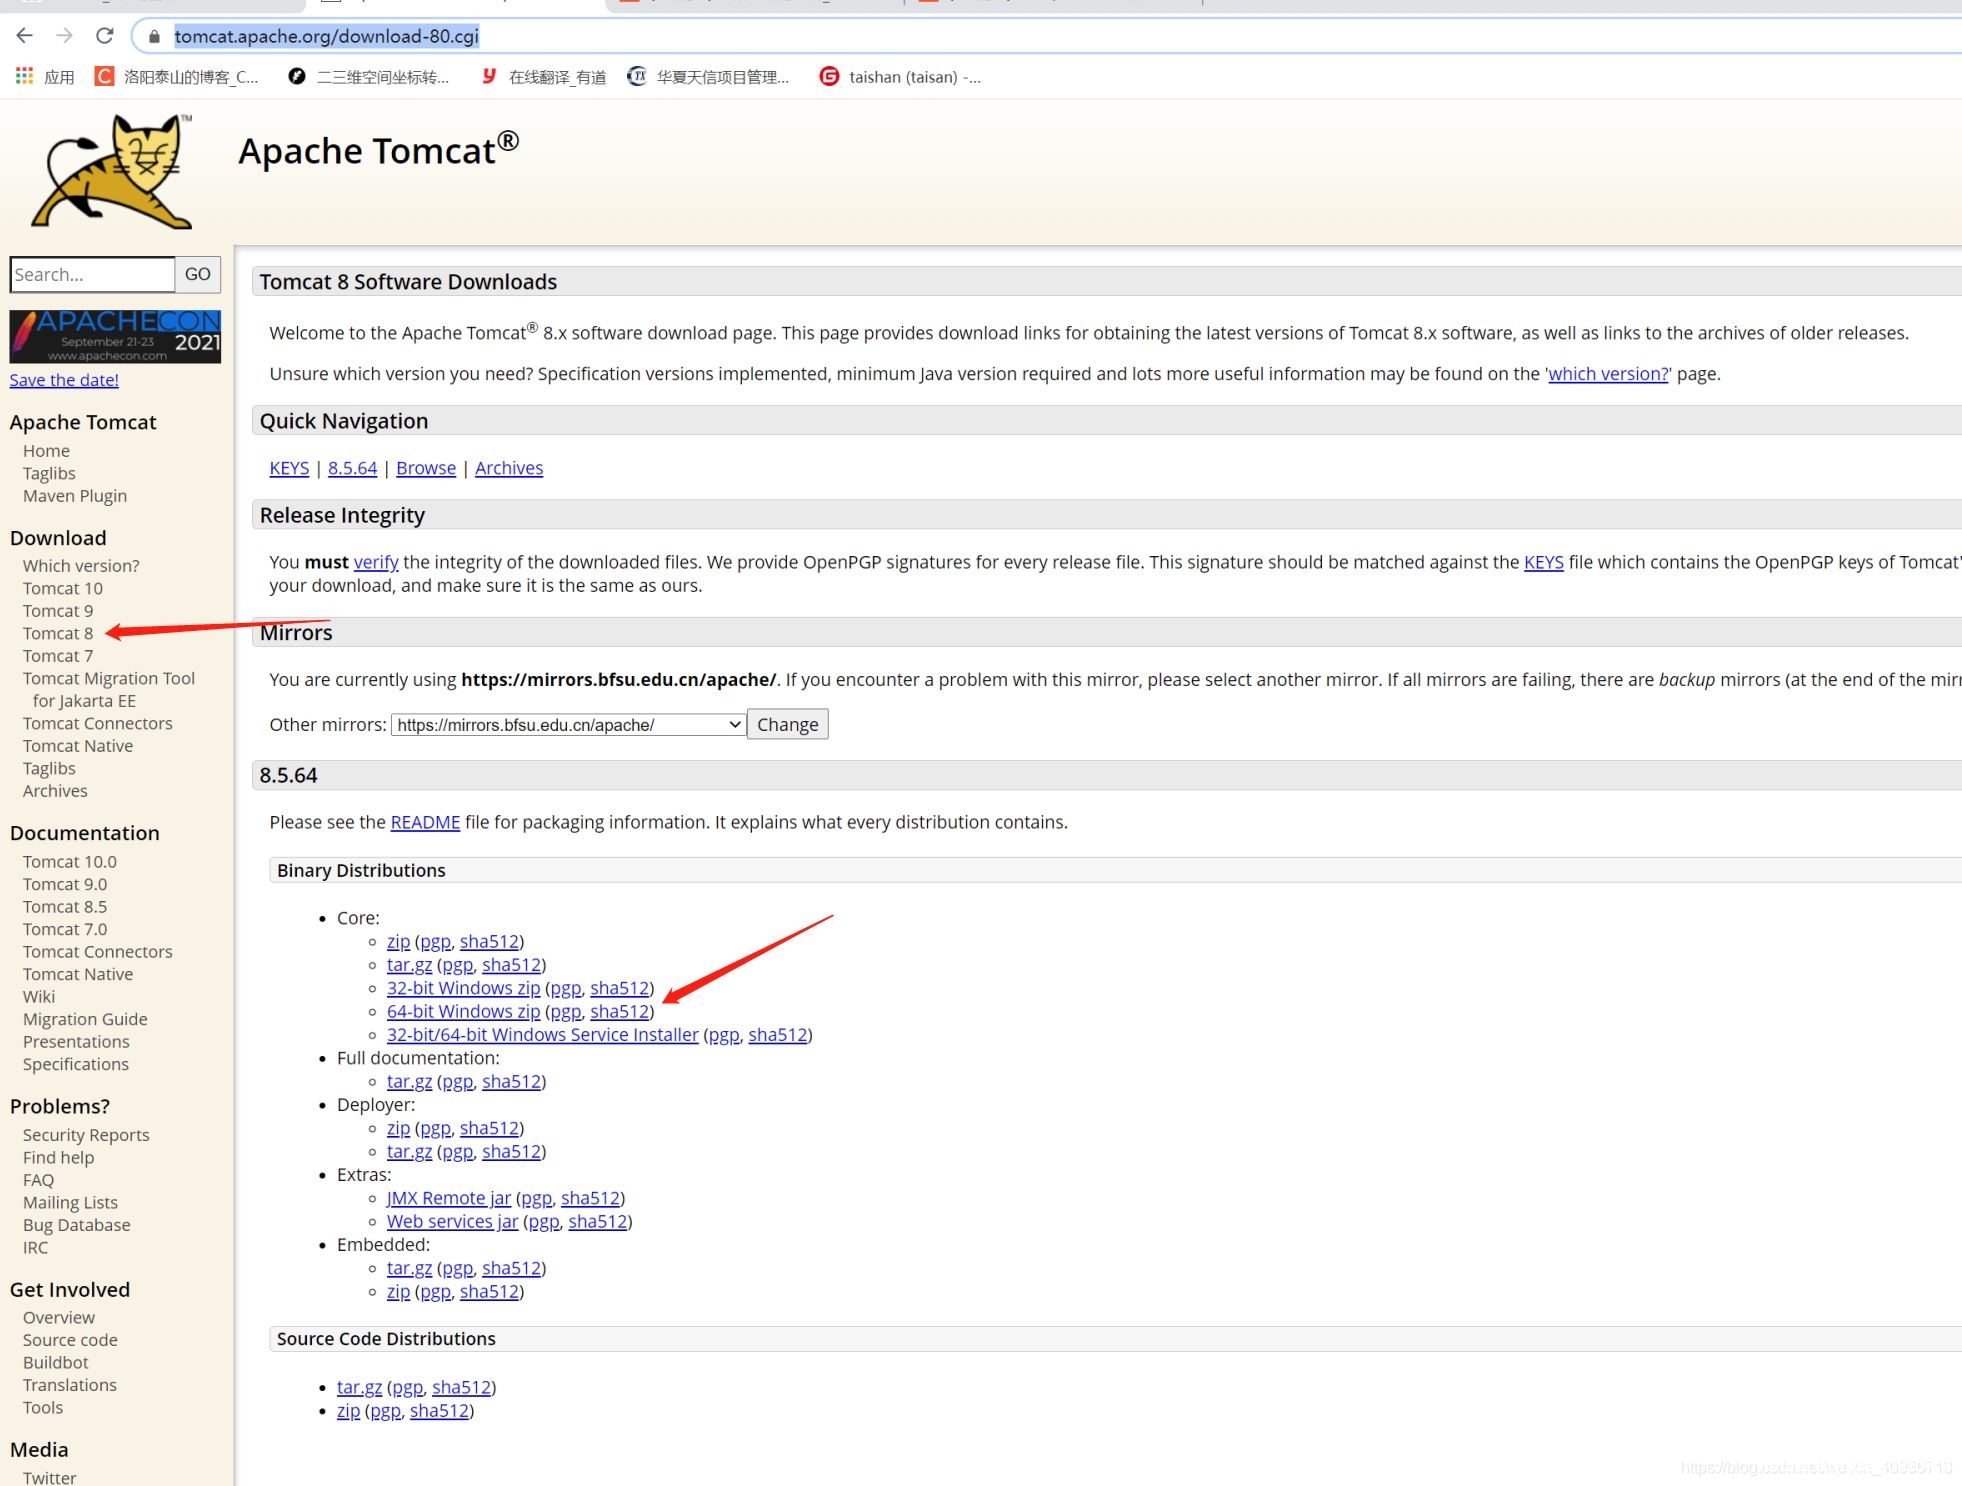
IDEA编辑器整合Apache Tomcat的详细教程_Tomcat
这篇文章主要介绍了IDEA编辑器整合Apache Tomcat教程,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1.到Apache Tomcat 官网...
2022年7月3日 20:11CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
2022年9月12日 18:46CVE-2025-34141: ETQ Reliance – Reflected XSS via SQLConverterServlet
漏洞标题 CVE-2025-34141: ETQ Reliance - Reflected XSS via SQLConverterServlet 漏洞描述 A reflected cross-site scripting (XSS) vulnerability exists in ETQ Reliance CG (legacy) platf...
2025年9月5日 01:08CVE-2018-11231: Opencart Divido – Sql Injection
漏洞标题 CVE-2018-11231: Opencart Divido - Sql Injection 漏洞描述 OpenCart Divido plugin is susceptible to SQL injection PoC代码
2018年9月14日 05:08CVE-2024-4455: YITH WooCommerce Ajax Search <= 2.4.0 - Cross-Site Scripting
漏洞标题 CVE-2024-4455: YITH WooCommerce Ajax Search <= 2.4.0 - Cross-Site Scripting 漏洞描述 The YITH WooCommerce Ajax Search plugin for WordPress is vulnerable to Stored Cross...
2024年10月18日 21:11
Linux添加静态路由两种实现方法解析_Linux
这篇文章主要介绍了Linux添加静态路由两种实现方法解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 添加路由的命令: 1.route add rou...
2023年7月1日 20:28CVE-2023-0942: WordPress Japanized for WooCommerce <2.5.5 - Cross-Site Scripting
漏洞标题 CVE-2023-0942: WordPress Japanized for WooCommerce <2.5.5 - Cross-Site Scripting 漏洞描述 WordPress Japanized for WooCommerce plugin before 2.5.5 is susceptible to cros...
2023年12月14日 01:39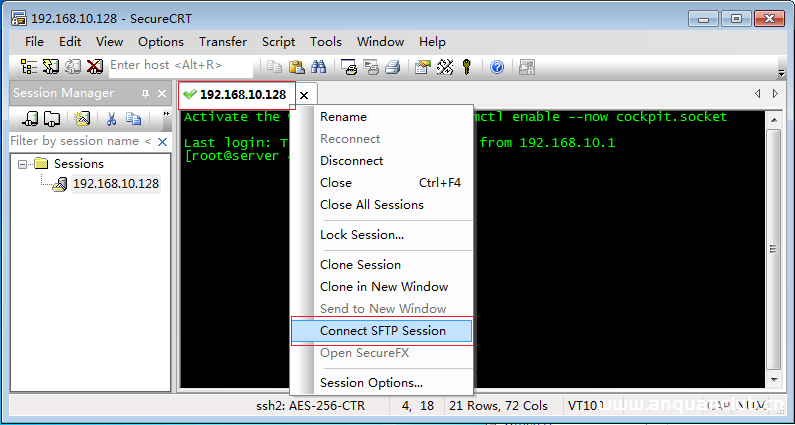
基于SecureCRT向远程Linux主机上传下载文件步骤图解_Linux
这篇文章主要介绍了基于SecureCRT向远程Linux主机上传下载文件,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 有时候直接在Linux服务器上...
2023年11月16日 21:27CVE-2019-16313: ifw8 Router ROM v4.31 – Credential Discovery
漏洞标题 CVE-2019-16313: ifw8 Router ROM v4.31 - Credential Discovery 漏洞描述 ifw8 Router ROM v4.31 is vulnerable to credential disclosure via action/usermanager.htm HTML source c...
2019年12月23日 18:24CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting
漏洞标题 CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting 漏洞描述 HashiCorp Consul and Consul Enterprise up to version 1.9.4 are vulnerable to ...
2020年8月11日 21:06CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年11月6日 23:22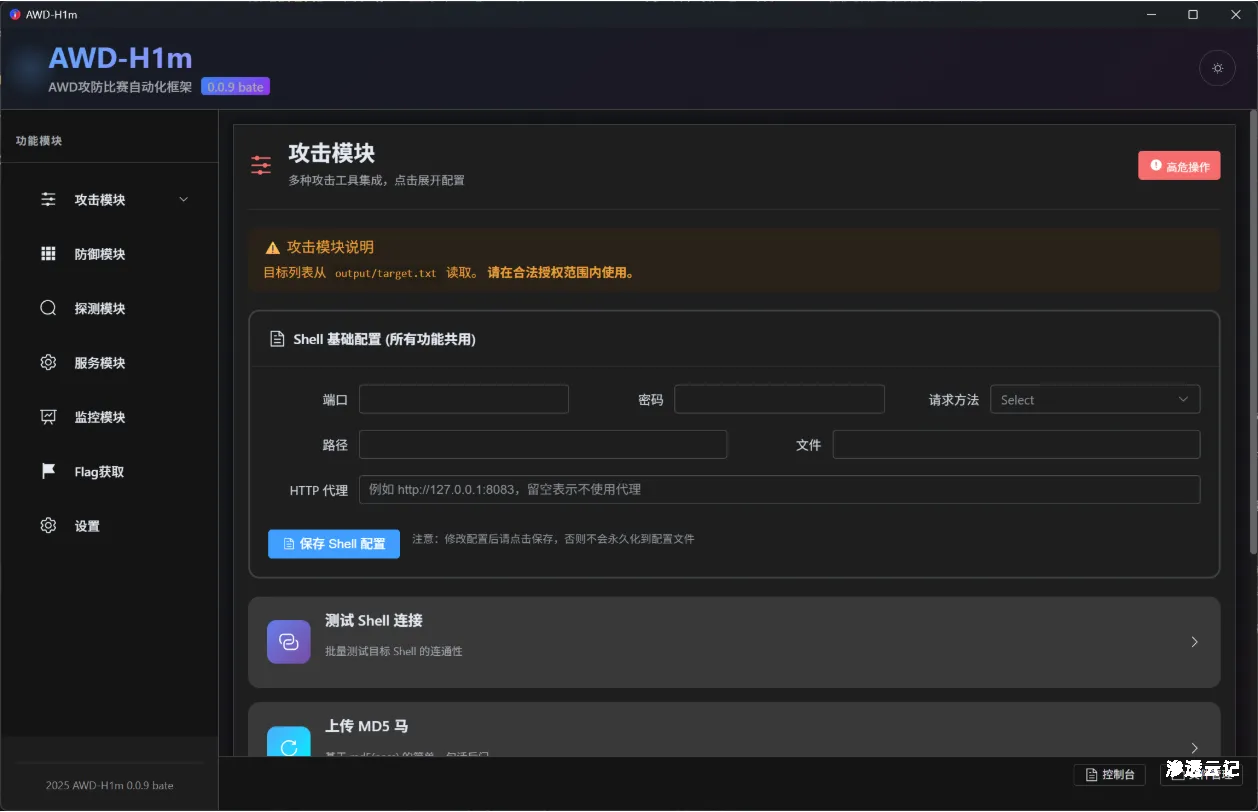
AWD-H1M-PRO -专为 CTF 设计的自动化 AWD 工具
项目介绍 AWD-H1m 是一款专为 CTF AWD (Attack With Defense) 赛制设计的桌面应用程序,帮助参赛选手在有限的比赛时间内高效完成攻击、防御、流量分析与 Flag 提交等核心任务。 在 AWD 竞赛中,...

 2026年3月25日 22:03
CVE-2016-9299: Jenkins CLI – HTTP Java Deserialization
漏洞标题 CVE-2016-9299: Jenkins CLI - HTTP Java Deserialization 漏洞描述 The remoting module in Jenkins before 2.32 and LTS before 2.19.3 allows remote attackers to execute arbitra...
2016年8月8日 08:40Apache APISIX Dashboard CVE-2021-45232 未授权访问漏洞
漏洞标题 Apache APISIX Dashboard CVE-2021-45232 未授权访问漏洞 漏洞描述 Apache APISIX Dashboard存在未授权访问漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
2021年2月8日 22:04
2026年10月29日 11:46
2026年10月28日 11:45
2026年10月27日 11:46
2026年10月26日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

