
最新发布第231页

Apache Airflow CVE-2022-24288 命令注入漏洞
漏洞标题 Apache Airflow CVE-2022-24288 命令注入漏洞 漏洞描述 Apache Airflow存在命令注入漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
 2022年1月8日 07:16
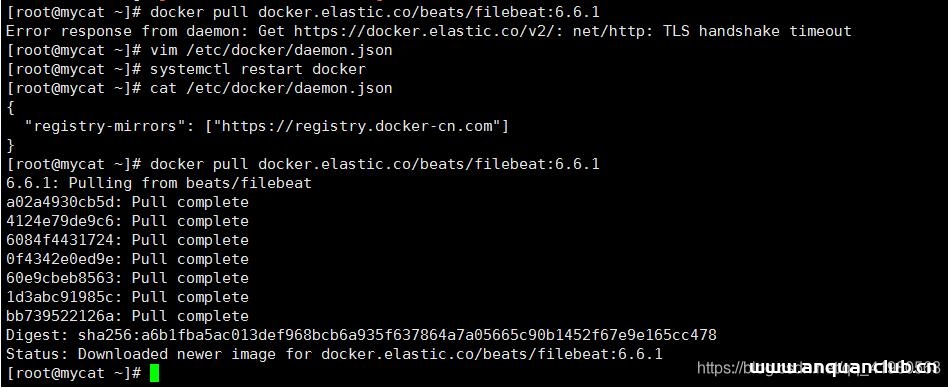
docker pull拉取超时的解决方案_docker
这篇文章主要介绍了docker pull拉取超时的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 最近docker pull镜像的时候非常不稳定,速度慢不说还经常超时失败 Pullin...
2022年8月17日 21:34
CNVD-2017-02833 fastjson 1.2.24 RCE
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 CNVD-2017-02833 fastjson 1.2.24 RCE Fastjson是一个Java库,可以将Java对象转换为JSON格式,当然它也可以将JSON字符串转换为Java对象。...

 2023年2月12日 11:39
CVE-2021-27561: YeaLink DM 3.6.0.20 – Remote Command Injection
漏洞标题 CVE-2021-27561: YeaLink DM 3.6.0.20 - Remote Command Injection 漏洞描述 Yealink Device Management (DM) 3.6.0.20 allows command injection as root via the /sm/api/v1/firewal...
2021年3月7日 08:42CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection
漏洞标题 CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection 漏洞描述 Prestashop posstaticfooter <= 1.0.0 is vulnerable to SQL Injection via posstaticfooter::...
2023年5月27日 00:10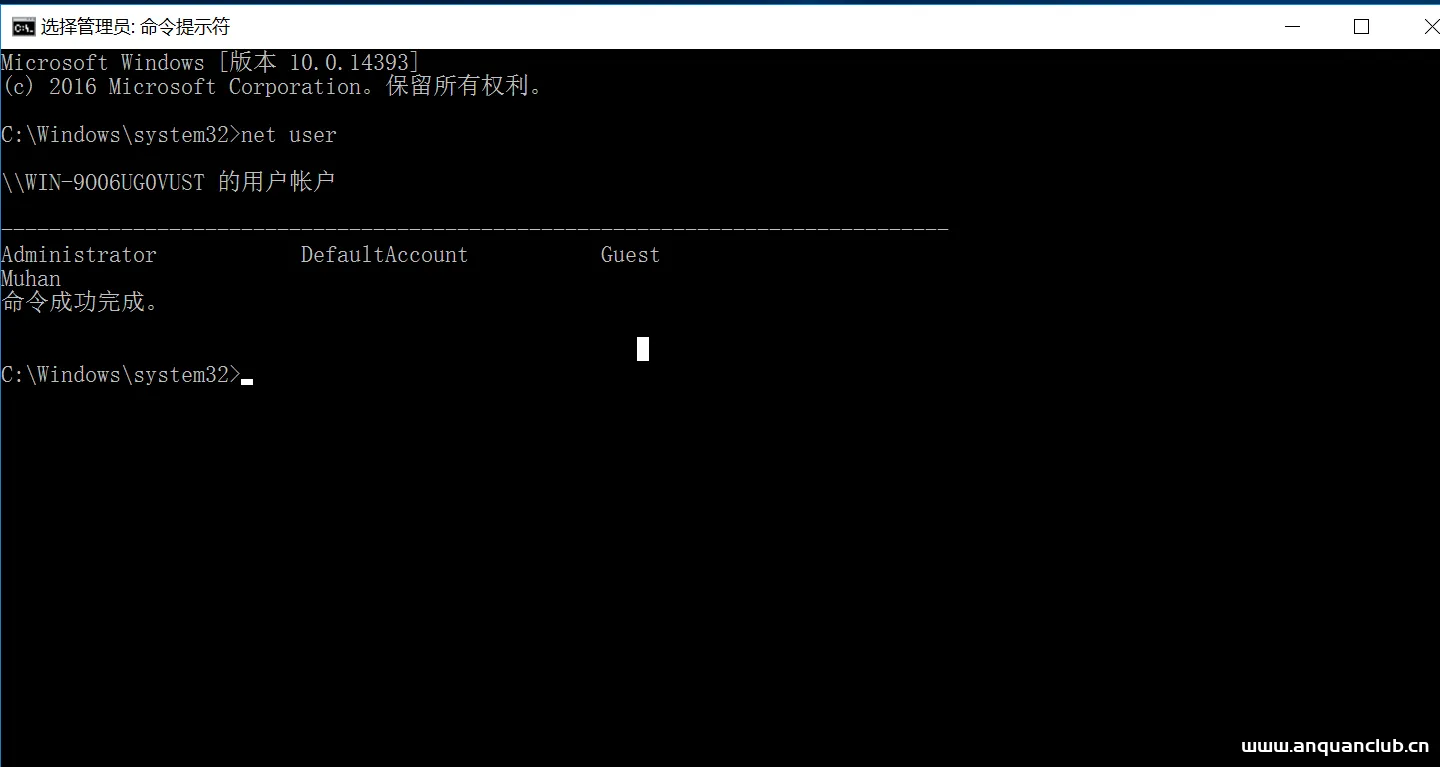
Window后期权限维持之创建Administrator的影子账号
简介 影子用户顾名思义就是一个隐藏用户,只能通过注册表查看这个用户,其它方式是找不到这个用户的信息的。在用户名后面添加$可以创建匿名的用户再添加到管理员组。 Net user看不到用户,但是...
2023年2月3日 21:35CVE-2019-19985: WordPress Email Subscribers & Newsletters <4.2.3 - Arbitrary File Retrieval
漏洞标题 CVE-2019-19985: WordPress Email Subscribers & Newsletters <4.2.3 - Arbitrary File Retrieval 漏洞描述 WordPress Email Subscribers & Newsletters plugin before 4.2...
2019年3月17日 06:27CVE-2017-1000028: GlassFish LFI
漏洞标题 CVE-2017-1000028: GlassFish LFI 漏洞描述 GlassFish是一款强健的商业兼容应用服务器,达到产品级质量,可免费用于开发、部署和重新分发。开发者可以免费获得源代码,还可以对代码进...
2017年8月21日 22:40CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection
漏洞标题 CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection 漏洞描述 The MasterStudy LMS WordPress Plugin for Online Courses and Education plugin for WordP...
2024年10月24日 15:37CVE-2016-1000148: WordPress S3 Video <=0.983 - Cross-Site Scripting
漏洞标题 CVE-2016-1000148: WordPress S3 Video <=0.983 - Cross-Site Scripting 漏洞描述 WordPress S3 Video and before contains a reflected cross-site scripting vulnerability which...
2016年2月5日 06:51
Centos7安装Docker(2020最新亲测可用,直接复制粘贴即可)_docker
这篇文章主要介绍了Centos7安装Docker(2020最新亲测可用,直接复制粘贴即可),文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起...
2022年10月25日 20:56CVE-2015-5354: Novius OS 5.0.1-elche – Open Redirect
漏洞标题 CVE-2015-5354: Novius OS 5.0.1-elche - Open Redirect 漏洞描述 Novius OS 5.0.1 (Elche) allows remote attackers to redirect users to arbitrary web sites and conduct phishing...
2015年11月24日 23:24CVE-2020-7136: HPE Smart Update Manager < 8.5.6 - Remote Unauthorized Access
漏洞标题 CVE-2020-7136: HPE Smart Update Manager < 8.5.6 - Remote Unauthorized Access 漏洞描述 HPE Smart Update Manager (SUM) prior to version 8.5.6 could allow remote unauthori...
2020年8月21日 21:24
docker 使用CMD或者ENTRYPOINT命令同时启动多个服务_docker
这篇文章主要介绍了docker 使用CMD或者ENTRYPOINT命令同时启动多个服务,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 需求:django中引入了celery,当启动django项目时,...
2023年1月24日 20:36CVE-2024-45293: TablePress < 2.4.3 - XXE Injection
漏洞标题 CVE-2024-45293: TablePress < 2.4.3 - XXE Injection 漏洞描述 The PHPSpreadsheet library used by the plugin is affected by an XXE as the security scanner that prevents XX...
2024年9月8日 14:37CVE-2023-27292: OpenCATS – Open Redirect
漏洞标题 CVE-2023-27292: OpenCATS - Open Redirect 漏洞描述 OpenCATS contains an open redirect vulnerability due to improper validation of user-supplied GET parameters. This, in tur...
2023年1月1日 01:27
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

