
最新发布第249页

CVE-2010-1461: Joomla! Component Photo Battle 1.0.1 – Local File Inclusion
漏洞标题 CVE-2010-1461: Joomla! Component Photo Battle 1.0.1 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Photo Battle (com_photobattle) component 1.0...
 2010年8月8日 15:27
CVE-2021-26855: Microsoft Exchange Server Remote Code Execution
漏洞标题 CVE-2021-26855: Microsoft Exchange Server Remote Code Execution 漏洞描述 Microsoft Exchange Server Remote Code Execution Vulnerability PoC代码
2021年4月22日 23:51CVE-2021-35587: Oracle Access Manager – Remote Code Execution
漏洞标题 CVE-2021-35587: Oracle Access Manager - Remote Code Execution 漏洞描述 The Oracle Access Manager portion of Oracle Fusion Middleware (component: OpenSSO Agent) is vulnerab...
2021年2月9日 13:30Apache Solr Velocity 模版注入漏洞(CVE-2019-17558)
漏洞标题 Apache Solr Velocity 模版注入漏洞(CVE-2019-17558) 漏洞描述 Apache Solr是美国阿帕奇(Apache)基金会的一款基于Lucene(一款全文搜索引擎)的搜索服务器。该产品支持层面搜索、...
2019年7月11日 14:24CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection
漏洞标题 CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection 漏洞描述 WordPress My Calendar plugin versions before 3.4.22 are vulnerable to an unauthenticated SQL injec...
2023年8月11日 23:12CVE-2025-25291: GitLab – SAML Authentication Bypass
漏洞标题 CVE-2025-25291: GitLab - SAML Authentication Bypass 漏洞描述 ruby-saml provides security assertion markup language (SAML) single sign-on (SSO) for Ruby. An authentication ...
2025年2月21日 06:06(CVE-2025-58751) Vite server.fs 安全绕过漏洞
漏洞标题 (CVE-2025-58751) Vite server.fs 安全绕过漏洞 漏洞描述 (CVE-2025-58751) Vite server.fs 安全绕过漏洞 PoC代码 暂无
2025年4月16日 19:51
【科普时间】短信轰炸的产生与如何防护
前言 为什么突然更新这么一篇老掉牙的文章呢? 原因那是相当简单,前两天的晚上,我正在那进行酣畅淋漓的峡谷大决斗,突然间,一大堆验证码犹如大江过境,直接淹没了我的视野,这事能忍? 当然...

 2023年1月31日 20:03
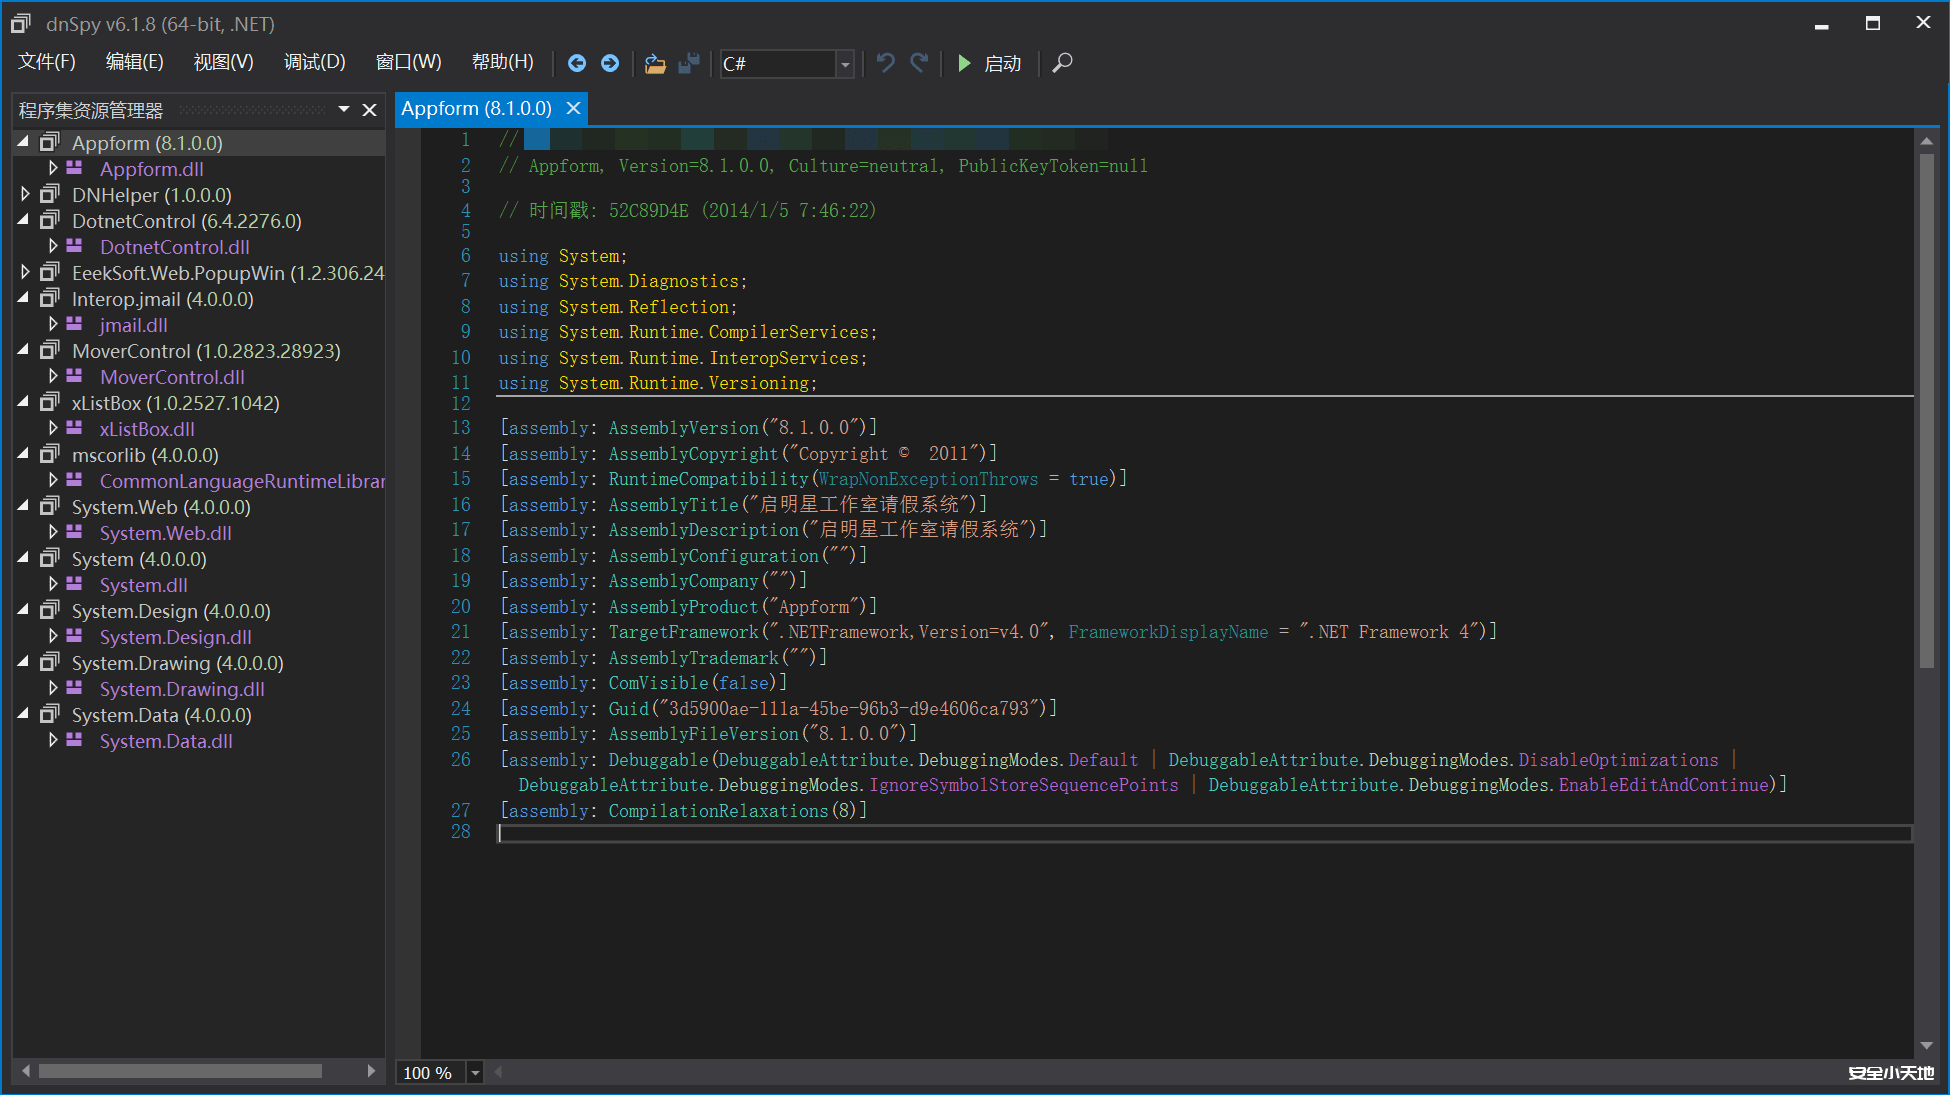
ASP.NET代码审计中常用的DLL反编译工具
前言 在针对ASP.NET开发的程序进行代码审计的时间,asp.net可以用C# ,VB.NET ,Jscript.net等等来开发,但是通常首选都是C#和VB.NET进行开发 审计ASP.NET的时候,首先得弄明白他的结构,他并不...
2024年3月3日 11:28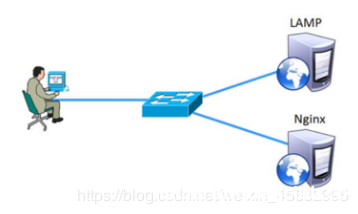
部署Nginx+Apache动静分离的实例详解_nginx
Nginx不仅能作为Web服务器,还具有反向代理、负载均衡和缓存的功能,这篇文章主要介绍了部署Nginx+Apache动静分离的实例代码,需要的朋友可以参考下 Nginx动静分离介绍 Nginx的静态处理能力很强...
2024年7月13日 21:15CVE-2020-24148: Import XML & RSS Feeds WordPress Plugin <= 2.0.1 Server-Side Request Forgery
漏洞标题 CVE-2020-24148: Import XML & RSS Feeds WordPress Plugin <= 2.0.1 Server-Side Request Forgery 漏洞描述 WordPress plugin Import XML and RSS Feeds (import-xml-feed) pl...
2020年2月12日 10:54CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
2022年4月25日 13:52
Linux ipcs命令的使用_Linux
这篇文章主要介绍了Linux ipcs命令的使用,帮助大家更好的学习和理解Linux,感兴趣的朋友可以了解下 1.命令简介 ipcs命令用于报告Linux中进程间通信设施的状态,显示的信息包括消息列表、共享内...
2023年7月3日 20:30aria2 webui 路径遍历漏洞(CVE-2023-39141)
漏洞标题 aria2 webui 路径遍历漏洞(CVE-2023-39141) 漏洞描述 WebUI-Aria2是hamza zia个人开发者的一个应用程序。用于创建与 aria2 交互的界面。 WebUI-Aria24fe2e版本存在路径遍历漏洞,该漏...
2023年3月4日 13:07CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access
漏洞标题 CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access 漏洞描述 WordPress Welcart e-Commerce plugin before 2.8.5 is susceptible to arbitrary file ac...
2022年8月5日 18:34Apache HTTPD 换行解析漏洞(CVE-2017-15715)
漏洞标题 Apache HTTPD 换行解析漏洞(CVE-2017-15715) 漏洞描述 Apache HTTPD 换行解析漏洞(CVE-2017-15715) PoC代码 暂无
2017年6月28日 19:09
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

