
最新发布第312页

CVE-2023-39677: PrestaShop MyPrestaModules – PhpInfo Disclosure
漏洞标题 CVE-2023-39677: PrestaShop MyPrestaModules - PhpInfo Disclosure 漏洞描述 PrestaShop modules by MyPrestaModules expose PHPInfo PoC代码
 2023年4月28日 00:38
CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
2020年8月12日 02:47CVE-2022-0599: WordPress Mapping Multiple URLs Redirect Same Page <=5.8 - Cross-Site Scripting
漏洞标题 CVE-2022-0599: WordPress Mapping Multiple URLs Redirect Same Page <=5.8 - Cross-Site Scripting 漏洞描述 WordPress Mapping Multiple URLs Redirect Same Page plugin 5.8 an...
2022年12月30日 19:24CVE-2022-45805: WordPress Paytm Payment Gateway <=2.7.3 - SQL Injection
漏洞标题 CVE-2022-45805: WordPress Paytm Payment Gateway <=2.7.3 - SQL Injection 漏洞描述 WordPress Paytm Payment Gateway plugin through 2.7.3 contains a SQL injection vulnerabi...
2022年6月9日 10:12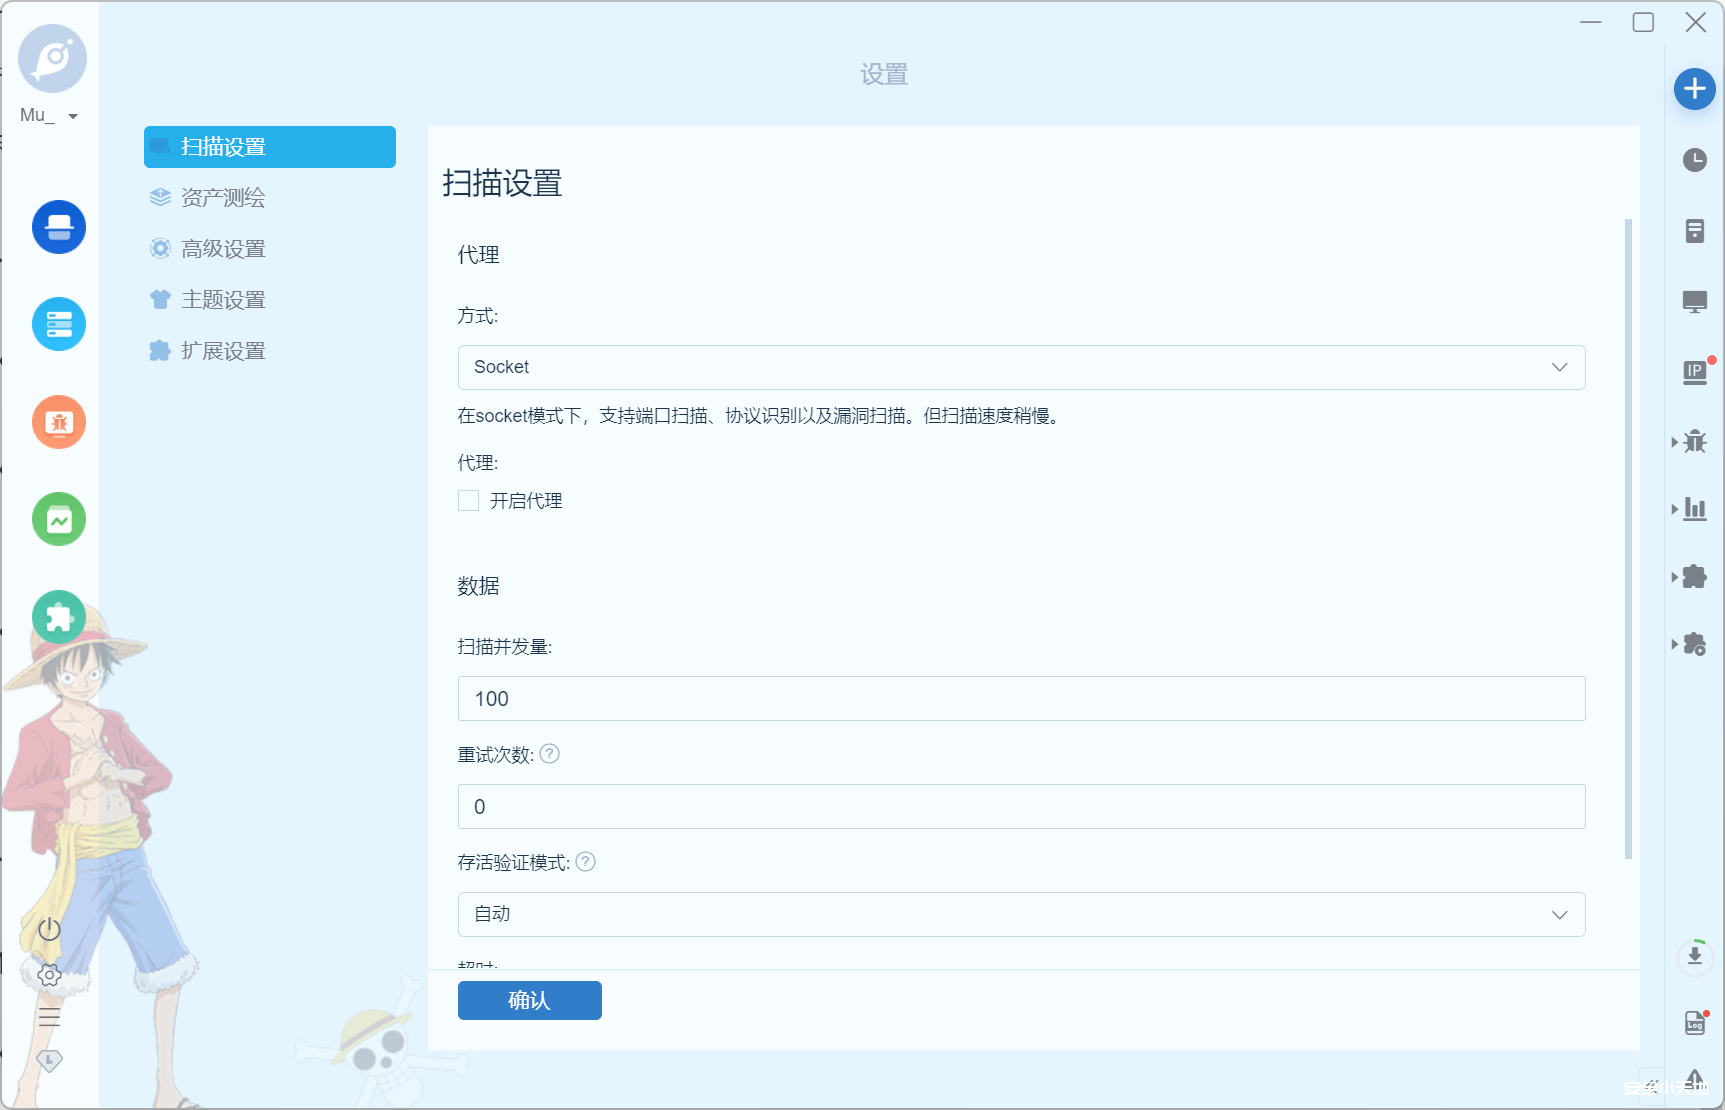
关于全局代理与局部代理的介绍
1. 为什么要全局代理 在渗透的时候要保护好自己啊,不要被溯源到。 在买的一些VPS上做扫描的时候,有可能会触发到VPS厂商(搬瓦工、Vultr的都有遇到过)的安全机制(如DDoS),将我们的VPS停机。做...

 2023年3月26日 11:04
CVE-2018-6200: vBulletin – Open Redirect
漏洞标题 CVE-2018-6200: vBulletin - Open Redirect 漏洞描述 vBulletin 3.x.x and 4.2.x through 4.2.5 contains an open redirect vulnerability via the redirector.php URL parameter. An ...
2018年2月18日 20:51CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion
漏洞标题 CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion 漏洞描述 phpMyAdmin before 4.8.5 is susceptible to local file inclusion. When the AllowArbitraryServer configura...
2019年6月14日 03:38CVE-2018-11784: Apache Tomcat – Open Redirect
漏洞标题 CVE-2018-11784: Apache Tomcat - Open Redirect 漏洞描述 Apache Tomcat versions prior to 9.0.12, 8.5.34, and 7.0.91 are prone to an open-redirection vulnerability because it...
2018年3月17日 17:02CVE-2025-53364: Parse Server – GraphQL Schema Information Disclosure
漏洞标题 CVE-2025-53364: Parse Server - GraphQL Schema Information Disclosure 漏洞描述 The Parse Server GraphQL API previously allowed public access to the GraphQL schema without r...
2025年6月12日 07:35CVE-2021-40655: D-Link DIR-605 – Information Disclosure
漏洞标题 CVE-2021-40655: D-Link DIR-605 - Information Disclosure 漏洞描述 An informtion disclosure issue exists in D-LINK-DIR-605 B2 Firmware Version - 2.01MT. An attacker can obta...
2021年8月26日 03:54CVE-2013-4117: WordPress Plugin Category Grid View Gallery 2.3.1 – Cross-Site Scripting
漏洞标题 CVE-2013-4117: WordPress Plugin Category Grid View Gallery 2.3.1 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in includes/CatGridPost.php in the Ca...
2013年12月15日 01:52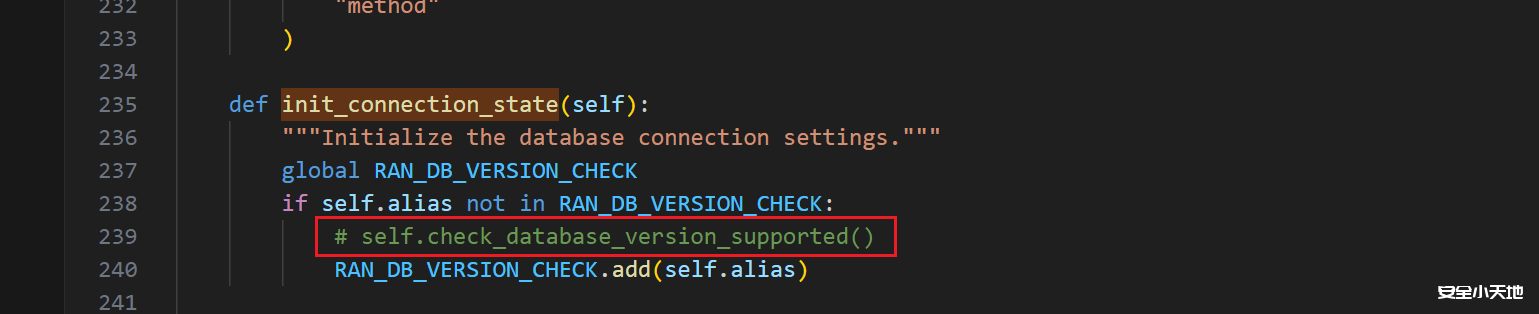
django报错数据库不支持低版本解决办法 django.db.utils.NotSupportedError: MySQL 8 or later is required (found 5.7.26)
Django提示mysq版本过低: django db. utils NotSuppotedError: MySQL 8 or later is required (found 5.7.26).因为mysql5.7及以下是免费的数据库,8.0之后是收费的。使用免费的数据库更放心,...
2024年3月22日 23:45CVE-2025-55182: React Server Components – Remote Code Execution
漏洞标题 CVE-2025-55182: React Server Components - Remote Code Execution 漏洞描述 React Server Components 19.0.0, 19.1.0, 19.1.1, and 19.2.0 including react-server-dom-parcel, reac...
2025年9月2日 22:56CVE-2021-24276: WordPress Supsystic Contact Form <1.7.15 - Cross-Site Scripting
漏洞标题 CVE-2021-24276: WordPress Supsystic Contact Form <1.7.15 - Cross-Site Scripting 漏洞描述 WordPress Supsystic Contact Form plugin before 1.7.15 contains a cross-site scr...
2021年9月28日 20:56CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload
漏洞标题 CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload 漏洞描述 Arbitrary File Upload vulnerability in WordPress Royal Elementor Addon...
2023年3月22日 16:43CVE-2021-24212: WooCommerce Help Scout – Arbitrary File Upload
漏洞标题 CVE-2021-24212: WooCommerce Help Scout - Arbitrary File Upload 漏洞描述 WooCommerce Help Scout plugin before version 2.9.1 contains an unrestricted file upload vulnerabili...
2021年3月11日 00:24
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

