
最新发布第338页

CVE-2017-12611: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-12611: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.0.0 through 2.3.33 and 2.5 through 2.5.10.1 uses an unintentional expression in a Fr...
 2017年12月16日 05:47
记两岸同胞的逻辑碰撞
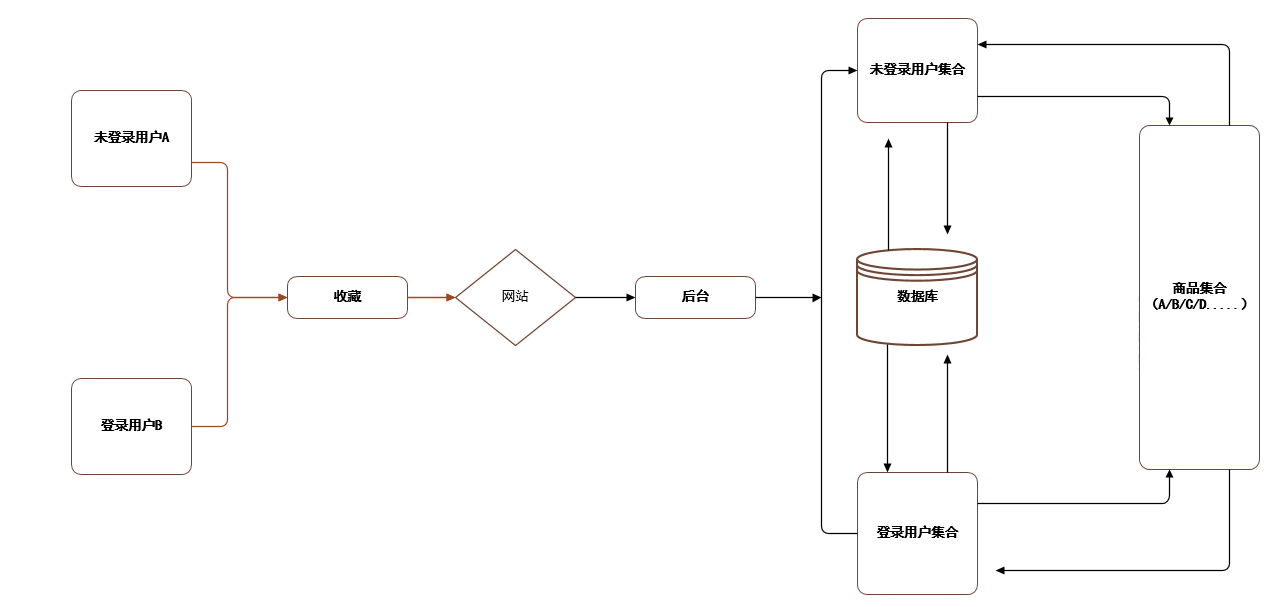
前言: 第一次挖这家src,看src自己给出的资产(赞一个),打开网站是一个电子商务C2C业务,大致扫了一眼业务,网站功能挺多的,出了不少货,挖的过程中,导致一些诡异的逻辑被触发了,在此仅对系...
2022年3月10日 23:37CVE-2023-43654: PyTorch TorchServe SSRF
漏洞标题 CVE-2023-43654: PyTorch TorchServe SSRF 漏洞描述 TorchServe is a tool for serving and scaling PyTorch models in production. TorchServe default configuration lacks proper i...
2023年11月10日 11:49CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF
漏洞标题 CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF 漏洞描述 WordPress Automatic plugin <3.92.1 is vulnerable to unauthenticated Ar...
2024年2月25日 20:47CVE-2021-22214: Gitlab CE/EE 10.5 – Server-Side Request Forgery
漏洞标题 CVE-2021-22214: Gitlab CE/EE 10.5 - Server-Side Request Forgery 漏洞描述 GitLab CE/EE versions starting from 10.5 are susceptible to a server-side request forgery vulnerab...
2021年4月19日 03:18CVE-2024-12987: DrayTek Vigor – Command Injection
漏洞标题 CVE-2024-12987: DrayTek Vigor - Command Injection 漏洞描述 DrayTek Gateway devices (Vigor2960, Vigor300B, etc.) are vulnerable to command injection via the session paramet...
2024年10月13日 09:50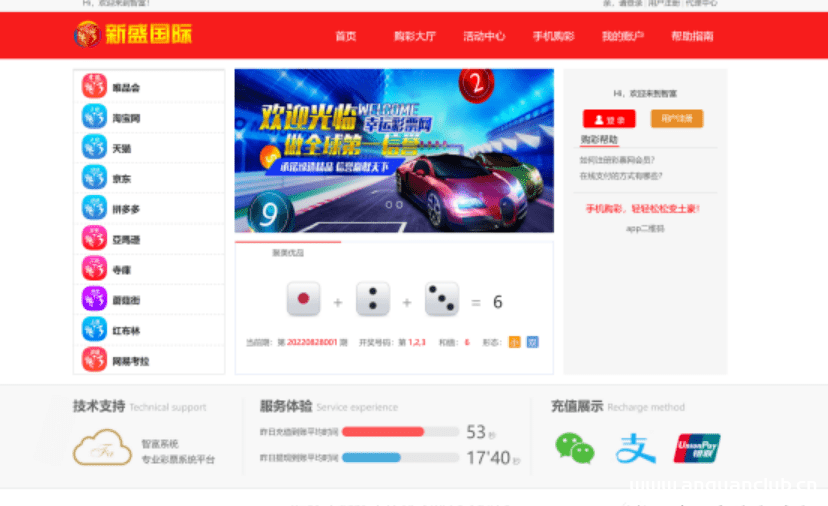
记一次彩票杀猪盘渗透
0x02 事件描述 网络赌博是指通过互联网手段(非法赌博网站、博彩App、微信群等)进行的赌博活动。由于网络赌博不合法,资金不受法律保护,有很多“出老千”的行为,很多人被骗后往往不敢报警,...
2026年2月13日 12:53CVE-2020-28185: TerraMaster TOS < 4.2.06 - User Enumeration
漏洞标题 CVE-2020-28185: TerraMaster TOS < 4.2.06 - User Enumeration 漏洞描述 User Enumeration vulnerability in TerraMaster TOS <= 4.2.06 allows remote unauthenticated attack...
2020年1月25日 00:46CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞
漏洞标题 CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞 漏洞描述 Liferay Portal CE是一款用来快速构建网站的开源系统。其7.2.0 GA1及以前的版本API接口中存在一处反序列化漏洞,利...
2020年7月31日 12:38
docker环境下分布式运行jmeter的教程详解_docker
这篇文章主要介绍了docker环境下分布式运行jmeter的教程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1.构建jmeter的基础镜像 dockerfile文件...
2023年4月19日 20:08CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年8月28日 17:49CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
2020年9月9日 08:33CVE-2017-12637: SAP NetWeaver Application Server Java 7.5 – Local File Inclusion
漏洞标题 CVE-2017-12637: SAP NetWeaver Application Server Java 7.5 - Local File Inclusion 漏洞描述 SAP NetWeaver Application Server Java 7.5 is susceptible to local file inclusion ...
2017年11月1日 05:59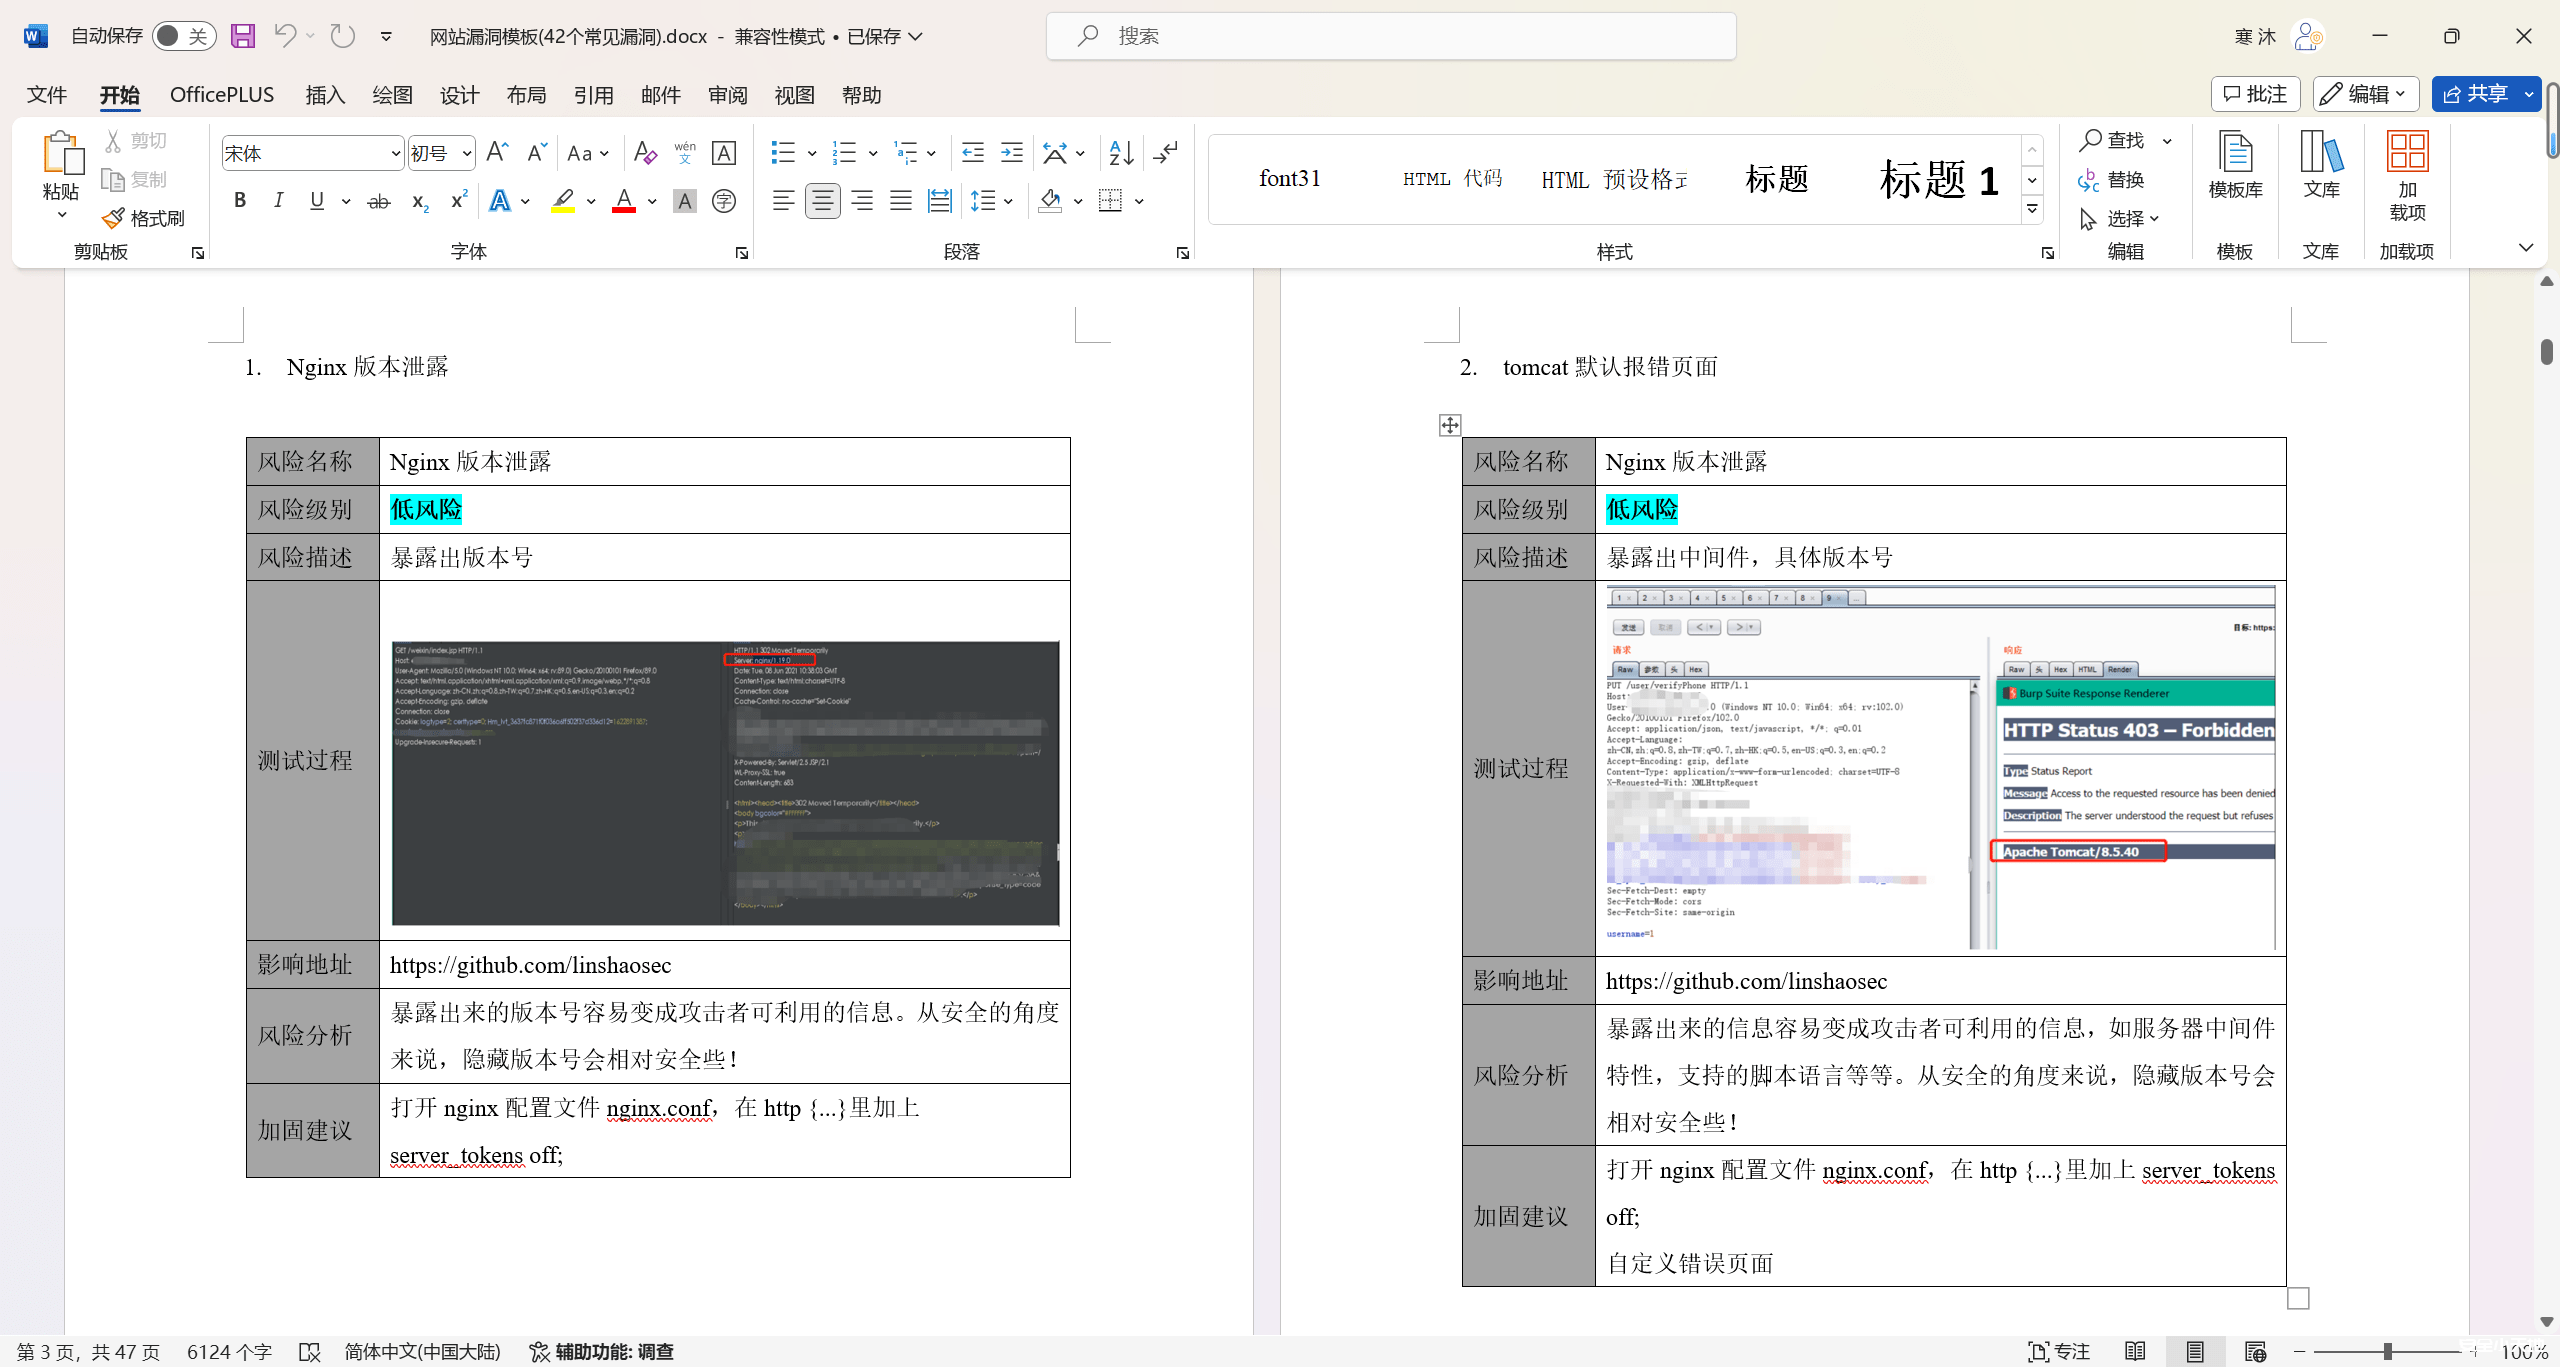
WaterExp:一款面向安服仔的扫描报告模板 和 碰瓷工具
项目名称 WaterExp 打工人新时代的摸鱼解决方案,安抚仔挖不到洞的最后一丝欢颜! http://github.com/linshaoSec/WaterExp 项目简介 (不产生实际攻击) (不会getshell) (面向水报告) 什么...

 2023年12月29日 15:54
CVE-2010-1340: Joomla! Component com_jresearch – ‘Controller’ Local File Inclusion
漏洞标题 CVE-2010-1340: Joomla! Component com_jresearch - 'Controller' Local File Inclusion 漏洞描述 A directory traversal vulnerability in jresearch.php in the J!Researc...
2010年3月11日 21:29CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection
漏洞标题 CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection 漏洞描述 Prestashop posstaticfooter <= 1.0.0 is vulnerable to SQL Injection via posstaticfooter::...
2023年12月14日 16:04
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

