
最新发布第352页

CVE-2019-14974: SugarCRM Enterprise 9.0.0 – Cross-Site Scripting
漏洞标题 CVE-2019-14974: SugarCRM Enterprise 9.0.0 - Cross-Site Scripting 漏洞描述 SugarCRM Enterprise 9.0.0 contains a cross-site scripting vulnerability via mobile/error-not-supp...
 2019年9月16日 18:33
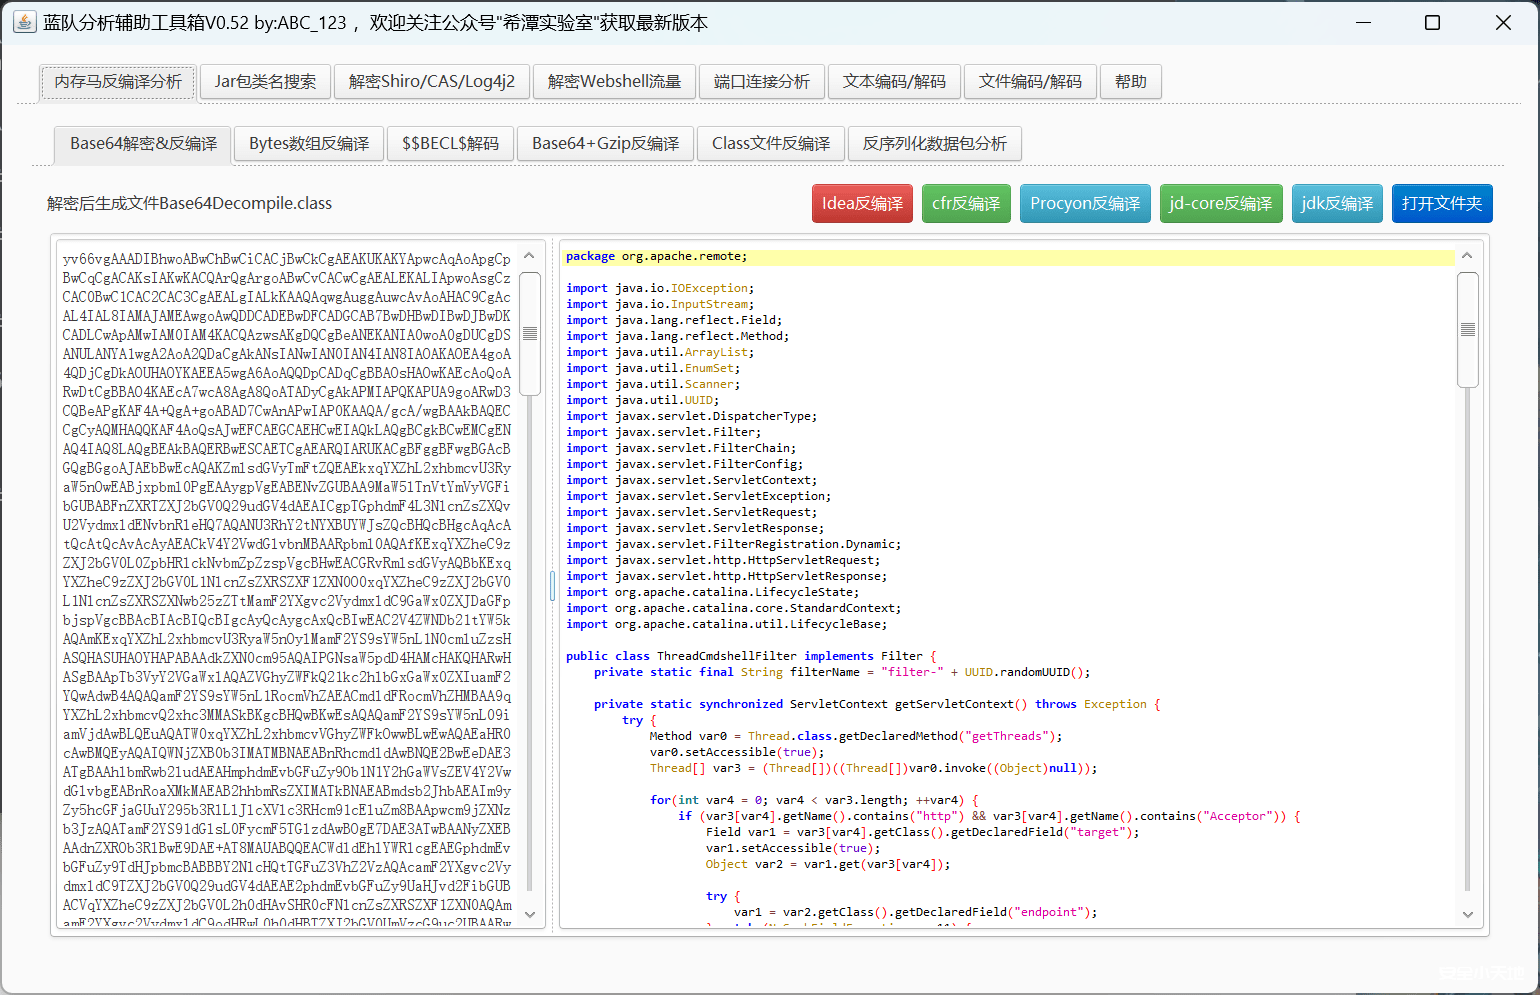
常见Webshell&重大漏洞的流量特征(附解密流量工具)
0x01 前言攻防演练中,经常会看到一些加密的流量,又分不清楚是不是误报,本文总结了一些常见的流量特征,附流量解密工具。远控C2cs流量特征:1,基础特征:心跳包2,请求特征:下发的指令,ur...

 2023年6月16日 16:43
CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
2023年5月12日 18:01CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 – SQL Injection
漏洞标题 CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 - SQL Injection 漏洞描述 SQL Injection exists in the PrayerCenter 3.0.2 component for Joomla! via the sessionid paramet...
2018年1月29日 08:23Apache OFBiz CVE-2024-32113 目录遍历漏洞
漏洞标题 Apache OFBiz CVE-2024-32113 目录遍历漏洞 漏洞描述 Apache OFBiz 存在目录遍历漏洞,此漏洞是由于未充分验证用户输入的url所导致的。 PoC代码 暂无
2024年11月3日 13:27CVE-2022-0653: WordPress Profile Builder Plugin Cross-Site Scripting
漏洞标题 CVE-2022-0653: Wordpress Profile Builder Plugin Cross-Site Scripting 漏洞描述 The Profile Builder User Profile & User Registration Forms WordPress plugin is vulnerable...
2022年1月25日 11:05CVE-2019-13462: Lansweeper Unauthenticated SQL Injection
漏洞标题 CVE-2019-13462: Lansweeper Unauthenticated SQL Injection 漏洞描述 Lansweeper before 7.1.117.4 allows unauthenticated SQL injection. PoC代码
2019年5月8日 23:05Copyparty1.8.6存在XSS漏洞(CVE-2025-54589)
漏洞标题 Copyparty1.8.6存在XSS漏洞(CVE-2025-54589) 漏洞描述 Copyparty1.8.6存在XSS漏洞,攻击者可以获取用户敏感信息。 PoC代码 暂无
2025年9月18日 09:57CVE-2020-26413: Gitlab CE/EE 13.4 – 13.6.2 – Information Disclosure
漏洞标题 CVE-2020-26413: Gitlab CE/EE 13.4 - 13.6.2 - Information Disclosure 漏洞描述 GitLab CE and EE 13.4 through 13.6.2 is susceptible to Information disclosure via GraphQL. Use...
2020年11月25日 18:51CVE-2022-27593: QNAP QTS Photo Station External Reference – Local File Inclusion
漏洞标题 CVE-2022-27593: QNAP QTS Photo Station External Reference - Local File Inclusion 漏洞描述 QNAP QTS Photo Station External Reference is vulnerable to local file inclusion v...
2022年8月4日 16:26CVE-2022-1595: WordPress HC Custom WP-Admin URL <=1.4 - Admin Login URL Disclosure
漏洞标题 CVE-2022-1595: WordPress HC Custom WP-Admin URL <=1.4 - Admin Login URL Disclosure 漏洞描述 The HC Custom WP-Admin URL WordPress plugin through 1.4 leaks the secret log...
2022年10月27日 02:09CVE-2017-1000170: WordPress Delightful Downloads Jquery File Tree 2.1.5 – Local File Inclusion
漏洞标题 CVE-2017-1000170: WordPress Delightful Downloads Jquery File Tree 2.1.5 - Local File Inclusion 漏洞描述 WordPress Delightful Downloads Jquery File Tree versions 2.1.5 and ...
2017年1月22日 07:07CVE-2018-8823: PrestaShop Responsive Mega Menu Module – Remote Code Execution
漏洞标题 CVE-2018-8823: PrestaShop Responsive Mega Menu Module - Remote Code Execution 漏洞描述 The 'Responsive Mega Menu' module for PrestaShop is prone to a remote code...
2018年1月18日 03:06CVE-2020-26876: WordPress WP Courses Plugin Information Disclosure
漏洞标题 CVE-2020-26876: WordPress WP Courses Plugin Information Disclosure 漏洞描述 WordPress WP Courses Plugin < 2.0.29 contains a critical information disclosure which expose...
2020年9月18日 17:25(CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞
漏洞标题 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 漏洞描述 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 PoC代码 暂无
2025年6月22日 09:53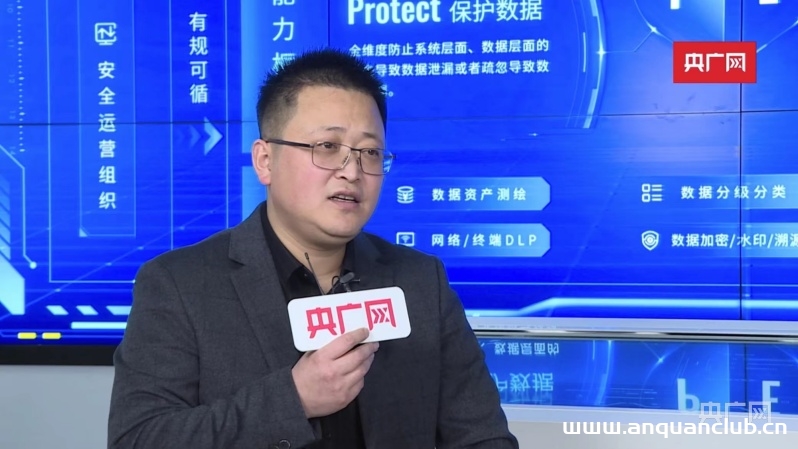
安恒信息苗春雨:学以致用产教融合,全方位助力网络安全人才体系建设
3月11日,西湖论剑·第五届中国杭州网络安全技能大赛(以下简称“大赛”)决赛在杭州拉开帷幕。作为首届全球数字贸易博览会的亮点单元,本次大赛由杭州市公安局、共青团杭州市委、杭州市学生联...
2022年3月16日 09:15
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

