
最新发布第365页

CVE-2021-24435: WordPress Titan Framework plugin <= 1.12.1 - Cross-Site Scripting
漏洞标题 CVE-2021-24435: WordPress Titan Framework plugin <= 1.12.1 - Cross-Site Scripting 漏洞描述 The iframe-font-preview.php file of the titan-framework does not properly esc...
 2021年10月27日 15:32
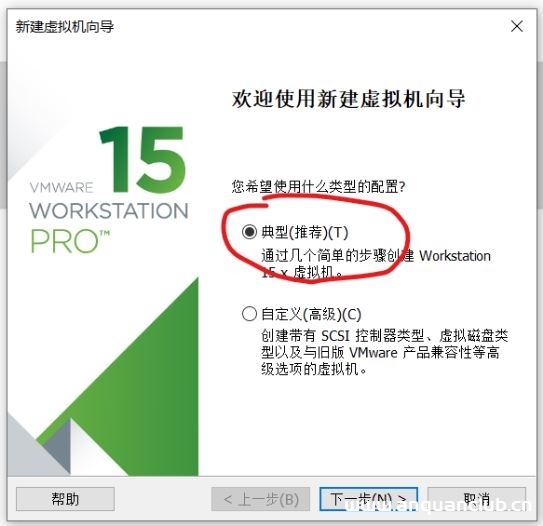
VMwarea虚拟机安装win7操作系统的教程图解_VMware
这篇文章主要介绍了VMwarea虚拟机安装win7操作系统的教程,本文图文并茂给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 VMwarea的安装过程就不演示了,主要看看如何装入wi...
2024年6月26日 20:09CVE-2021-21972: VMware vSphere Client (HTML5) – Remote Code Execution
漏洞标题 CVE-2021-21972: VMware vSphere Client (HTML5) - Remote Code Execution 漏洞描述 VMware vCenter vSphere Client (HTML5) contains a remote code execution vulnerability in a vC...
2021年8月25日 08:58
bugbounty技巧聚合20220126
漏洞报告 【Imgur】密码无长度 http://hackerone.com/reports/1411363 【Mail.ru 】子域接管 http://hackerone.com/reports/1348504 【Lark Technologies】能够使用 Lark 的 Compose Email 功能...
2022年3月10日 23:39Linux xargs命令的使用_Linux
这篇文章主要介绍了Linux xargs命令的使用,帮助大家更好的掌握Linux系统的使用,感兴趣的朋友可以了解下 1.功能: xargs可以将stdin中以空格或换行符进行分隔的数据,形成以空格分隔的参数(ar...
2023年7月16日 20:26CVE-2017-9841: PHPUnit – Remote Code Execution
漏洞标题 CVE-2017-9841: PHPUnit - Remote Code Execution 漏洞描述 PHPUnit before 4.8.28 and 5.x before 5.6.3 allows remote attackers to execute arbitrary PHP code via HTTP POST data...
2017年12月25日 19:06CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass
漏洞标题 CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass 漏洞描述 Stacks Mobile App Builder WordPress plugin ≤ 5.2.3 suffers from an authent...
2024年5月30日 00:27CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection
漏洞标题 CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection 漏洞描述 A SQL injection vulnerability in the product_all_one_img and image_product parameters of the...
2022年10月26日 11:03CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution
漏洞标题 CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution 漏洞描述 Zoho ManageEngine OpManager before 12.5.329 contains a remote code execution caus...
2021年2月27日 00:55Apache Superset 默认口令(CVE-2021-44451)
漏洞标题 Apache Superset 默认口令(CVE-2021-44451) 漏洞描述 ApacheSuperset是一款由Python语言为主开发的开源时髦数据探索分析以及可视化的报表平台;她支持丰富的数据源,且拥有多姿多彩的...
2021年12月23日 00:23CVE-2022-34534: Digital Watchdog DW Spectrum Server 4.2.0.32842 – Information Disclosure
漏洞标题 CVE-2022-34534: Digital Watchdog DW Spectrum Server 4.2.0.32842 - Information Disclosure 漏洞描述 Digital Watchdog DW Spectrum Server 4.2.0.32842 allows attackers to acces...
2022年3月23日 00:12CVE-2023-28343: Altenergy Power Control Software C1.2.5 – Remote Command Injection
漏洞标题 CVE-2023-28343: Altenergy Power Control Software C1.2.5 - Remote Command Injection 漏洞描述 Altenergy Power Control Software C1.2.5 is susceptible to remote command inject...
2023年8月15日 19:55CVE-2023-45375: PrestaShop PireosPay – SQL Injection
漏洞标题 CVE-2023-45375: PrestaShop PireosPay - SQL Injection 漏洞描述 In the module “PireosPay” (pireospay) up to version 1.7.9 from 01generator.com for PrestaShop, a guest can ...
2023年8月15日 08:17CVE-2022-0189: WordPress RSS Aggregator < 4.20 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2022-0189: WordPress RSS Aggregator < 4.20 - Authenticated Cross-Site Scripting 漏洞描述 WordPress RSS Aggregator < 4.20 is susceptible to cross-site scripting. ...
2022年1月18日 06:48
向居家程序员「送服」
共克时艰,免费领取4核4G轻量应用服务器 新老用户同享 免费领取1个月4核4G8M带宽1200GB流量包轻量应用服务器 登录直接购买即可 拿来直接当云主机,还是很香的哦 购买链接 须知,早入手,早享受

 2023年1月13日 20:11
CVE-2023-46747: F5 BIG-IP – Unauthenticated RCE via AJP Smuggling
漏洞标题 CVE-2023-46747: F5 BIG-IP - Unauthenticated RCE via AJP Smuggling 漏洞描述 CVE-2023-46747 is a critical severity authentication bypass vulnerability in F5 BIG-IP that coul...
2023年7月21日 07:48
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

