
最新发布第373页

CVE-2024-6646: Netgear-WN604 downloadFile.php – Information Disclosure
漏洞标题 CVE-2024-6646: Netgear-WN604 downloadFile.php - Information Disclosure 漏洞描述 There is an information leakage vulnerability in the downloadFile.php interface of Netgear ...
 2024年6月6日 10:17
CVE-2020-21998: HomeAutomation 3.3.2 – Open Redirect
漏洞标题 CVE-2020-21998: HomeAutomation 3.3.2 - Open Redirect 漏洞描述 HomeAutomation 3.3.2 contains a redirect vulnerability caused by improper verification of the 'redirect&...
2020年8月7日 13:27CVE-2023-38194: SuperWebMailer – Cross-Site Scripting
漏洞标题 CVE-2023-38194: SuperWebMailer - Cross-Site Scripting 漏洞描述 An issue was discovered in SuperWebMailer 9.00.0.01710 that allows keepalive.php XSS via a GET parameter. Po...
2023年7月7日 16:52CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization
漏洞标题 CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization 漏洞描述 WordPress Sitemap by click5 plugin before 1.0.36 is susceptible to missing authoriza...
2022年4月16日 17:40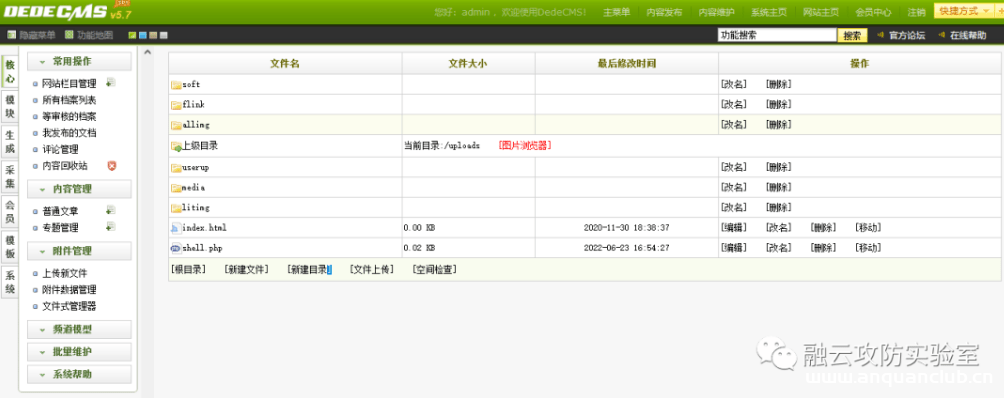
DEDECMS后台任意文件上传
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 DEDECMS后台任意文件上传 织梦内容管理系统(Dedecms)是一款PHP开源网站管理系统。该漏洞利用需要登录后台,并且后台的账户权限是管理员...

 2023年2月17日 13:59

docker cp 拷贝文件 和 进入容器的操作_docker
这篇文章主要介绍了docker cp 拷贝文件 和 进入容器的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 进入正在运行的容器 # 进入容器 新开一个终端 # docker exec -it ...
2022年7月5日 20:24CVE-2025-27817: Apache Kafka 客户端任意文件读取
漏洞标题 CVE-2025-27817: Apache Kafka 客户端任意文件读取 漏洞描述 允许未经身份验证的攻击者利用该漏洞实现任意文件读取,大多数据处理中间件或流式处理框架,如:Apache Spark Structured ...
2025年5月29日 22:11CVE-2017-18562: Error Log Viewer by BestWebSoft < 1.0.6 - Cross-Site Scripting
漏洞标题 CVE-2017-18562: Error Log Viewer by BestWebSoft < 1.0.6 - Cross-Site Scripting 漏洞描述 The error-log-viewer plugin before 1.0.6 for WordPress has multiple XSS issues. ...
2017年11月8日 00:44
防护措施 – 关键信息基础设施安全保护 – hvv面试题
什么是安全加固 为什么要做安全加固 法律法规利益保护安全检查自身安全 安全加固划分 安全加固准备阶段 基本要素准备 确定安全加固的范围;确定安全加固的时间进度;确定安全加固的人力资源与沟...
2022年6月30日 18:12CVE-2022-1168: WordPress WP JobSearch <1.5.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1168: WordPress WP JobSearch <1.5.1 - Cross-Site Scripting 漏洞描述 WordPress WP JobSearch plugin prior to 1.5.1 contains a cross-site scripting vulnerability....
2022年8月13日 03:26CVE-2017-18490: Contact Form Multi by BestWebSoft < 1.2.1 - Cross-Site Scripting
漏洞标题 CVE-2017-18490: Contact Form Multi by BestWebSoft < 1.2.1 - Cross-Site Scripting 漏洞描述 The contact-form-multi plugin before 1.2.1 for WordPress has multiple XSS issu...
2017年6月10日 11:26
强大的子域搜集工具-OneForAll
项目介绍 项目地址:http://github.com/shmilylty/OneForAll 在渗透测试中信息收集的重要性不言而喻,子域收集是信息收集中必不可少且非常重要的一环,目前网上也开源了许多子域收集的工具,但...
2023年1月13日 20:11CVE-2011-2780: Chyrp 2.x – Local File Inclusion
漏洞标题 CVE-2011-2780: Chyrp 2.x - Local File Inclusion 漏洞描述 A directory traversal vulnerability in includes/lib/gz.php in Chyrp 2.0 and earlier allows remote attackers to rea...
2011年10月12日 05:31CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass
漏洞标题 CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass 漏洞描述 Hard-Coded Cryptographic key allowing to forge session cookies that can be used to ent...
2025年4月14日 22:27CVE-2024-55550: Mitel MiCollab – Arbitary File Read
漏洞标题 CVE-2024-55550: Mitel MiCollab - Arbitary File Read 漏洞描述 The Mitel Collab Arbitrary File Read vulnerability allows an unauthenticated attacker to read arbitrary files ...
2024年5月13日 09:09CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
2023年8月21日 01:10
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

