
最新发布第37页

BlogEngine.NET 3.3.7.0 LFI (CVE-2019-10717)
漏洞标题 BlogEngine.NET 3.3.7.0 LFI (CVE-2019-10717) 漏洞描述 BlogEngine.NET 3.3.7.0允许/api/filemanager通过路径参数包含本地文件 PoC代码 暂无
 2019年4月18日 23:36
CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年7月4日 13:18CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection
漏洞标题 CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection 漏洞描述 The MasterStudy LMS WordPress Plugin for Online Courses and Education plugin for WordP...
2024年8月17日 20:13
懒人快速验证漏洞小工具
前言 懒人必备 简简单单 快速验证 逐步完善 持续更新 该工具主要是方便自己整理容易复现的poc,批量测试,然后恰烂洞,大佬勿喷呀(抱住狗头) 因为以前收集的poc都是东一个西一个的存放,到用...

 2023年2月12日 18:33
CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年11月17日 21:31CVE-2023-6568: Mlflow – Cross-Site Scripting
漏洞标题 CVE-2023-6568: Mlflow - Cross-Site Scripting 漏洞描述 The vulnerability allows an attacker to inject malicious code into the Content-Type header of a POST request, which i...
2023年9月19日 08:48CVE-2011-3600: Apache OFBiz – XML External Entity Injection
漏洞标题 CVE-2011-3600: Apache OFBiz - XML External Entity Injection 漏洞描述 The /webtools/control/xmlrpc endpoint in OFBiz XML-RPC event handler is exposed to External Entity Inj...
2011年3月1日 04:53CVE-2022-38840: Güralp MAN-EAM-0003 3.2.4 – XML External Entity (XXE)
漏洞标题 CVE-2022-38840: Güralp MAN-EAM-0003 3.2.4 - XML External Entity (XXE) 漏洞描述 cgi-bin/xmlstatus.cgi in Güralp MAN-EAM-0003 3.2.4 is vulnerable to an XML External Entity...
2022年10月25日 11:26CVE-2023-45249: Acronis Cyber Infrastructure – Default Password
漏洞标题 CVE-2023-45249: Acronis Cyber Infrastructure - Default Password 漏洞描述 Acronis Cyber Infrastructure (ACI) before build 5.0.1-61, 5.1.1-71, 5.2.1-69, 5.3.1-53, and 5.4.4-...
2023年6月23日 00:31CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect
漏洞标题 CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect 漏洞描述 WordPress Event Tickets < 5.2.2 is susceptible to an open redirect vulnerability. The plugin...
2021年9月22日 11:27CVE-2020-0618: Microsoft SQL Server Reporting Services – Remote Code Execution
漏洞标题 CVE-2020-0618: Microsoft SQL Server Reporting Services - Remote Code Execution 漏洞描述 Microsoft SQL Server Reporting Services is vulnerable to a remote code execution vu...
2020年4月10日 17:08CVE-2024-30569: Netgear R6850 – Information Disclosure
漏洞标题 CVE-2024-30569: Netgear R6850 - Information Disclosure 漏洞描述 Netgear R6850 router firmware version V1.1.0.88 contains an information leakage vulnerability in the curren...
2024年12月11日 05:49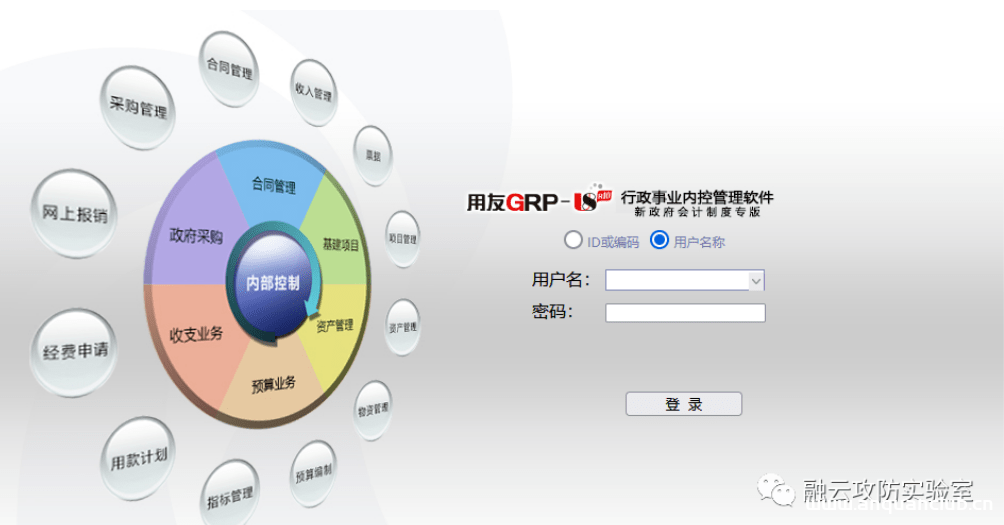
用友U8 UploadFileData任意文件上传
本文转载于公众号:融云攻防实验室,原文地址: 用友U8 UploadFileData任意文件上传 用友GRP-U8R10行政事业财务管理软件是用友公司专注于电子政务事业,基于云计算技术所推出的新一代产品,是我...
2026年2月13日 12:53
全球业务关闭,年收入百亿物流公司Expeditors遭受网络攻击
物流和货运代理巨头Expeditors International是总部位于美国西雅图的财富500强公司,在 100 多个国家和地区拥有上万名员工,去年年收入超过百亿。上周日,Expeditors宣布确认了一起网络攻击事件...
2022年3月10日 23:40CVE-2016-10368: Opsview Monitor Pro – Open Redirect
漏洞标题 CVE-2016-10368: Opsview Monitor Pro - Open Redirect 漏洞描述 Opsview Monitor Pro before 5.1.0.162300841, before 5.0.2.27475, before 4.6.4.162391051, and 4.5.x without a ce...
2016年8月11日 12:13CVE-2024-34982: LyLme-Spage – Arbitary File Upload
漏洞标题 CVE-2024-34982: LyLme-Spage - Arbitary File Upload 漏洞描述 An arbitrary file upload vulnerability in the component /include/file.php of lylme_spage v1.9.5 allows attacker...
2024年12月2日 04:52
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

