
最新发布第401页

CVE-2017-1000028: GlassFish LFI
漏洞标题 CVE-2017-1000028: GlassFish LFI 漏洞描述 GlassFish是一款强健的商业兼容应用服务器,达到产品级质量,可免费用于开发、部署和重新分发。开发者可以免费获得源代码,还可以对代码进...
 2017年9月4日 22:33
Centos系统中如何在指定位置下安装Nginx_nginx
这篇文章主要介绍了Centos系统中如何在指定位置下安装Nginx,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 Centos系统中如何在指定位置下安装Ngi...
2023年10月2日 20:43CVE-2022-23779: Zoho ManageEngine – Internal Hostname Disclosure
漏洞标题 CVE-2022-23779: Zoho ManageEngine - Internal Hostname Disclosure 漏洞描述 Zoho ManageEngine Desktop Central before 10.1.2137.8 exposes the installed server name to anyone....
2022年12月8日 21:46CVE-2008-0702: Titan FTP Server 6.03 and 6.0.5.549 – Heap Overflow via Long Commands
漏洞标题 CVE-2008-0702: Titan FTP Server 6.03 and 6.0.5.549 - Heap Overflow via Long Commands 漏洞描述 Titan FTP Server versions 6.03 and 6.05 (builds) contain multiple heap-based ...
2008年7月12日 16:49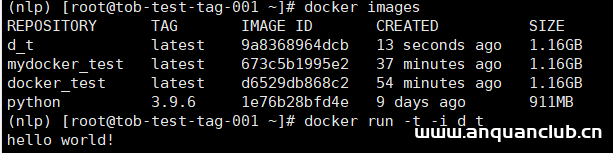
docker打包Python环境的过程详解_docker
这篇文章主要介绍了docker打包Python环境过程,准备工作需要大家复制python程序启动程序,具体操作流程跟随小编一起看看吧 docker打包Python环境过程,步骤如下所示: 1 导出pip list下面的依赖...
2022年6月15日 22:45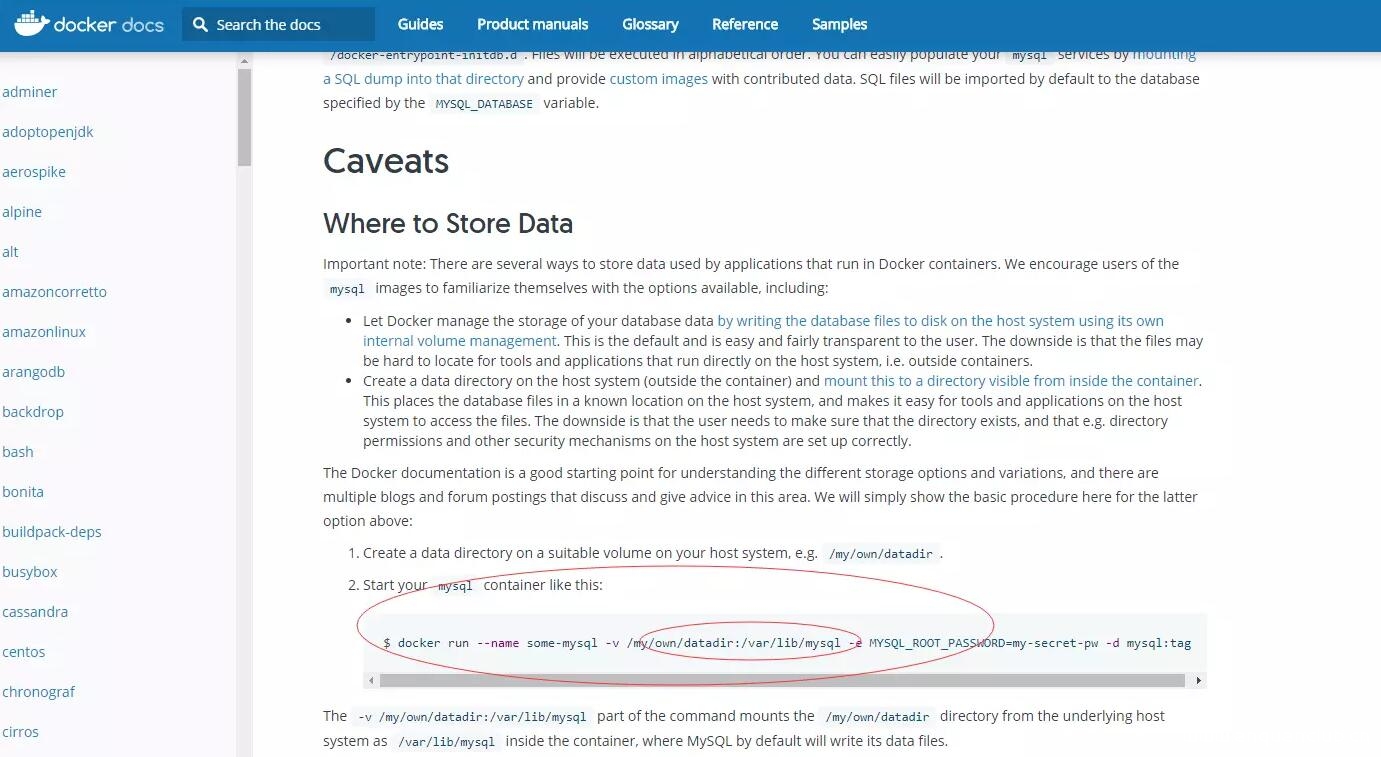
解决docker重启redis,mysql数据丢失的问题_docker
这篇文章主要介绍了解决docker重启redis,mysql数据丢失的问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 官方文档: 所以 mysql应如下启动: docker run -p 3306:3306 ...
2023年1月3日 21:23CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus – Remote Code Execution
漏洞标题 CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus - Remote Code Execution 漏洞描述 Zoho ManageEngine ServiceDesk Plus before 11306, ServiceDesk Plus MSP before 10530, and...
2021年9月16日 04:59CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
2022年3月3日 15:36Apache Solr 环境变量信息泄漏漏洞(CVE-2023-50290)
漏洞标题 Apache Solr 环境变量信息泄漏漏洞(CVE-2023-50290) 漏洞描述 Apache Solr 是一款开源搜索引擎。自Apache Solr 9.0.0起,由于 Solr Metrics API默认输出所有未单独配置保护策略的环境...
2023年7月20日 03:41
Centos8(最小化安装)全新安装Python3.8+pip的方法教程_Linux
这篇文章主要介绍了Centos8(最小化安装)全新安装Python3.8+pip的方法教程,本文给大家整理了一份命令,需要的朋友可以参考下 最小化安装Python8后安装Python3.8.1,网上找了一圈教程,没有一个...
2024年5月29日 20:51CVE-2017-7921: Hikvision – Authentication Bypass
漏洞标题 CVE-2017-7921: Hikvision - Authentication Bypass 漏洞描述 Hikvision DS-2CD2xx2F-I Series V5.2.0 build 140721 to V5.4.0 build 160530, DS-2CD2xx0F-I Series V5.2.0 build 1407...
2017年12月18日 15:32CVE-2022-25226: ThinVNC – Authentication Bypass
漏洞标题 CVE-2022-25226: ThinVNC - Authentication Bypass 漏洞描述 ThinVNC version 1.0b1 allows an unauthenticated user to bypass the authentication process via a specific command, ...
2022年5月7日 07:17CVE-2020-9484: Apache Tomcat Remote Command Execution
漏洞标题 CVE-2020-9484: Apache Tomcat Remote Command Execution 漏洞描述 When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7...
2020年6月28日 00:07CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal
漏洞标题 CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal 漏洞描述 spring-boot-actuator-logview before version 0.2.13 contains a directory traversal vulnerability i...
2021年11月29日 22:47
网络安全事件基础在线预览 – 关键信息基础设施安全保护 – hvv面试题
什么是渗透测试 一种通过模拟攻击者的技术与方法,挫败目标系统的安全控制措施并取得访问权限的安全测试方法。是安全管理框架中安全评估环节的重要手段。 渗透测试环节 前期交互 (Pre-engagemen...

 2022年7月3日 15:17
CVE-2022-29153: HashiCorp Consul/Consul Enterprise – Server-Side Request Forgery
漏洞标题 CVE-2022-29153: HashiCorp Consul/Consul Enterprise - Server-Side Request Forgery 漏洞描述 HashiCorp Consul and Consul Enterprise up to 1.9.16, 1.10.9, and 1.11 are suscept...
2022年11月28日 11:39
2026年10月21日 11:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

