
最新发布第472页

CVE-2024-27564: ChatGPT个人专用版 – Server Side Request Forgery
漏洞标题 CVE-2024-27564: ChatGPT个人专用版 - Server Side Request Forgery 漏洞描述 A Server-Side Request Forgery (SSRF) in pictureproxy.php of ChatGPT commit f9f4bbc allows attacker...
 2024年3月16日 09:35
CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read
漏洞标题 CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read 漏洞描述 An issue was discovered in Sitecore Experience Platform (XP), Experience Manager (XM...
2024年8月27日 09:28CVE-2017-7921: Hikvision – Authentication Bypass
漏洞标题 CVE-2017-7921: Hikvision - Authentication Bypass 漏洞描述 Hikvision DS-2CD2xx2F-I Series V5.2.0 build 140721 to V5.4.0 build 160530, DS-2CD2xx0F-I Series V5.2.0 build 1407...
2017年12月16日 20:21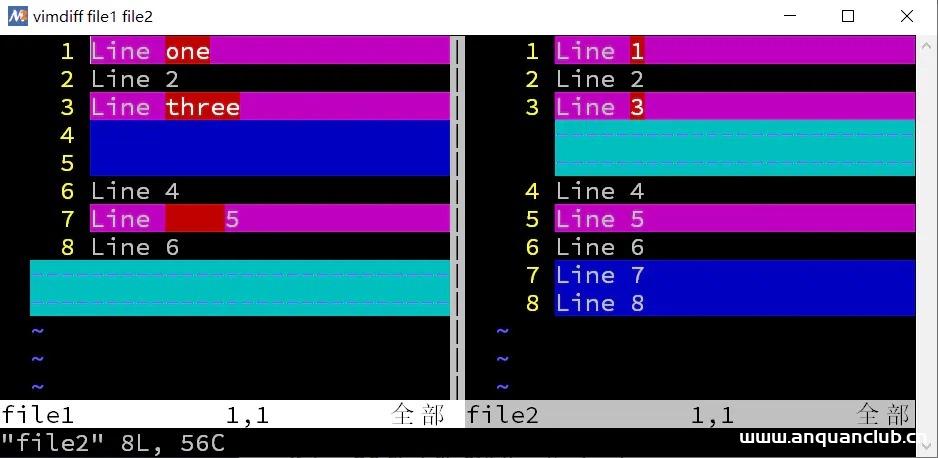
Linux下9种优秀的代码比对工具推荐小结_Linux
这篇文章主要介绍了Linux下9种优秀的代码比对工具推荐小结,不仅有命令行工具,还有 GUI 界面工具,让你轻松进行代码比对,感兴趣的可以一起来了解一下 在我们编写代码的时候,我们经常需要知道...
2023年11月1日 20:45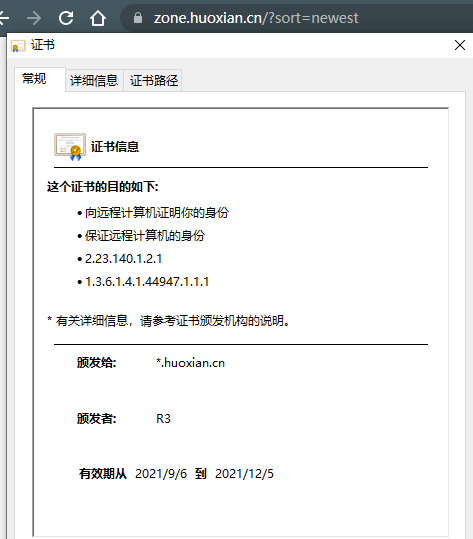
批量获取网站SSL证书里的域名
大佬们在日常刷洞过程中,或者批量扫某个POC时,总会扫到很多未知资产或者结果量太大一个个去验证资产归属太费时费力。而一些https站点的证书中能看到证书归属,一般通过证书定位的资产都比较准...
2022年3月10日 23:33CVE-2024-51378: CyberPanel – Command Injection
漏洞标题 CVE-2024-51378: CyberPanel - Command Injection 漏洞描述 CyberPanel contains a command injection vulnerability in the /ftp/getresetstatus and /dns/getresetstatus endpoints....
2024年5月4日 11:38Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776)
漏洞标题 Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776) 漏洞描述 【漏洞对象】Apache Struts 2 【涉及版本】2.3-2.3.34,2.5-2.5.16 【漏洞描述】软件存在输入验证漏洞,远程攻击者可...
2018年12月26日 21:43CVE-2023-45375: PrestaShop PireosPay – SQL Injection
漏洞标题 CVE-2023-45375: PrestaShop PireosPay - SQL Injection 漏洞描述 In the module “PireosPay” (pireospay) up to version 1.7.9 from 01generator.com for PrestaShop, a guest can ...
2023年1月10日 01:25CVE-2014-3206: Seagate BlackArmor NAS – Command Injection
漏洞标题 CVE-2014-3206: Seagate BlackArmor NAS - Command Injection 漏洞描述 Seagate BlackArmor NAS allows remote attackers to execute arbitrary code via the session parameter to lo...
2014年9月10日 12:02CVE-2024-23692: HTTP File Server Template_injection
漏洞标题 CVE-2024-23692: HTTP File Server Template_injection 漏洞描述 Rejetto HTTP文件服务器,直到并包括2.3m版本,都存在模板注入漏洞。此漏洞允许远程、未经认证的攻击者通过发送特制的...
2024年6月13日 12:35CVE-2020-8615: WordPress Plugin Tutor LMS 1.5.3 – Cross-Site Request Forgery
漏洞标题 CVE-2020-8615: Wordpress Plugin Tutor LMS 1.5.3 - Cross-Site Request Forgery 漏洞描述 A CSRF vulnerability in the Tutor LMS plugin before 1.5.3 for WordPress can result in...
2020年11月28日 01:00CVE-2014-2323: Lighttpd 1.4.34 SQL Injection and Path Traversal
漏洞标题 CVE-2014-2323: Lighttpd 1.4.34 SQL Injection and Path Traversal 漏洞描述 A SQL injection vulnerability in mod_mysql_vhost.c in lighttpd before 1.4.35 allows remote attacke...
2014年9月6日 21:11CVE-2021-24358: Plus Addons for Elementor Page Builder < 4.1.10 - Open Redirect
漏洞标题 CVE-2021-24358: Plus Addons for Elementor Page Builder < 4.1.10 - Open Redirect 漏洞描述 WordPress Plus Addons for Elementor Page Builder before 4.1.10 did not validate...
2021年8月27日 03:23CVE-2017-5638: Apache Struts 2 – Remote Command Execution S2-045 S2-046
漏洞标题 CVE-2017-5638: Apache Struts 2 - Remote Command Execution S2-045 S2-046 漏洞描述 Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 is vulnerable to remote comm...
2017年3月28日 04:54CVE-2025-57822: Next.js Middleware – Server-Side Request Forgery
漏洞标题 CVE-2025-57822: Next.js Middleware - Server-Side Request Forgery 漏洞描述 In Next.js prior to versions 14.2.32 and 15.4.7, when request headerswere insecurely passed to Ne...
2025年8月23日 16:19CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
2021年2月27日 12:00
2026年9月29日 11:45
2026年9月28日 11:45
2026年9月27日 11:45
2026年9月26日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

