
最新发布第47页

可疑样本动态调试基本流程
一、动态分析工作目标 动态分析必须要在隔离且受控的环境中执行可疑样本,使用虚拟机,通过监控可疑样本与操作系统、网络和其它进程的交互来理解其功能和意图。 观测真实行为:能观察到静态分析...

 2026年3月1日 15:46

CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 – Unauthenticated Remote Command Execution
漏洞标题 CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 - Unauthenticated Remote Command Execution 漏洞描述 Zoho ManageEngine ADSelfService Plus version 6113 and prior ...
 2021年4月13日 09:38
CVE-2023-39120: Nodogsplash – Directory Traversal
漏洞标题 CVE-2023-39120: Nodogsplash - Directory Traversal 漏洞描述 Nodogsplash product was affected by a directory traversal vulnerability that also impacted the OpenWrt product. ...
2023年12月16日 21:00CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
2022年10月10日 17:55CVE-2020-13935: Apache Tomcat WebSocket Frame Payload Length Validation Denial of Service
漏洞标题 CVE-2020-13935: Apache Tomcat WebSocket Frame Payload Length Validation Denial of Service 漏洞描述 Apache Tomcat versions 10.0.0-M1 to 10.0.0-M6, 9.0.0.M1 to 9.0.36, 8.5.0...
2020年1月18日 22:43CVE-2024-6586: Lightdash v0.1024.6 – Server-Side Request Forgery
漏洞标题 CVE-2024-6586: Lightdash v0.1024.6 - Server-Side Request Forgery 漏洞描述 Server-Side Request Forgery (“SSRF”) in the export dashboard functionality of Lightdash version...
2024年8月18日 14:03CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
2024年1月6日 17:33CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting
漏洞标题 CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting 漏洞描述 WordPress e-search 1.0 and before contains a reflected cross-site scripting vulnerability via...
2016年6月12日 17:21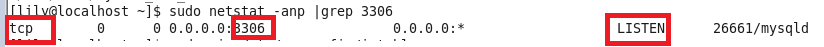
LINUX查看端口是否被占用过程解析_Linux
这篇文章主要介绍了LINUX查看端口是否被占用过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 之前查询端口是否被占用一直搞不明白...
2023年12月24日 21:23CVE-2020-13405: Microweber <1.1.20 - Information Disclosure
漏洞标题 CVE-2020-13405: Microweber <1.1.20 - Information Disclosure 漏洞描述 Microweber before 1.1.20 is susceptible to information disclosure via userfiles/modules/users/contr...
2020年1月19日 03:06CVE-2017-14135: OpenDreambox 2.0.0 – Remote Code Execution
漏洞标题 CVE-2017-14135: OpenDreambox 2.0.0 - Remote Code Execution 漏洞描述 OpenDreambox 2.0.0 is susceptible to remote code execution via the webadmin plugin. Remote attackers ca...
2017年4月5日 00:04CVE-2018-18809: TIBCO JasperReports Library – Directory Traversal
漏洞标题 CVE-2018-18809: TIBCO JasperReports Library - Directory Traversal 漏洞描述 The default server implementation of TIBCO Software Inc.'s TIBCO JasperReports Library, TIB...
2018年5月19日 11:04
Docker遇到Intellij IDEA,Java开发提升了十倍生产力_docker
这篇文章主要介绍了Docker遇到Intellij IDEA,Java开发提升了十倍生产力,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、开发前准备 ...
2023年4月6日 21:05CVE-2021-41826: PlaceOS 1.2109.1 – Open Redirection
漏洞标题 CVE-2021-41826: PlaceOS 1.2109.1 - Open Redirection 漏洞描述 PlaceOS Authentication Service before 1.29.10.0 allows app/controllers/auth/sessions_controller.rb open redire...
2021年8月17日 12:57
Linux QT Kit丢失及Version为空问题解决方案_Linux
这篇文章主要介绍了Linux QT Kit丢失及Version为空问题解决方案,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 目前遇到了这样一个问题 ...
2023年7月22日 21:08CVE-2023-3139: Protect WP Admin < 4.0 - Unauthenticated Protection Bypass
漏洞标题 CVE-2023-3139: Protect WP Admin < 4.0 - Unauthenticated Protection Bypass 漏洞描述 The Protect WP Admin WordPress plugin before version 4.0 disclosed the URL of the adm...
2023年6月12日 17:09
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

