
最新发布第505页

CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
 2022年6月2日 11:28
CVE-2022-38812: AeroCMS 0.1.1 – SQL Injection
漏洞标题 CVE-2022-38812: AeroCMS 0.1.1 - SQL Injection 漏洞描述 AeroCMS 0.1.1 contains a SQL injection caused by unsanitized author parameter, letting attackers execute arbitrary S...
2022年4月9日 14:31CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection
漏洞标题 CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection 漏洞描述 Rocket.Chat 3.11, 3.12 and 3.13 contains a NoSQL injection vulnerability which allows unauthenticated acce...
2021年5月16日 14:40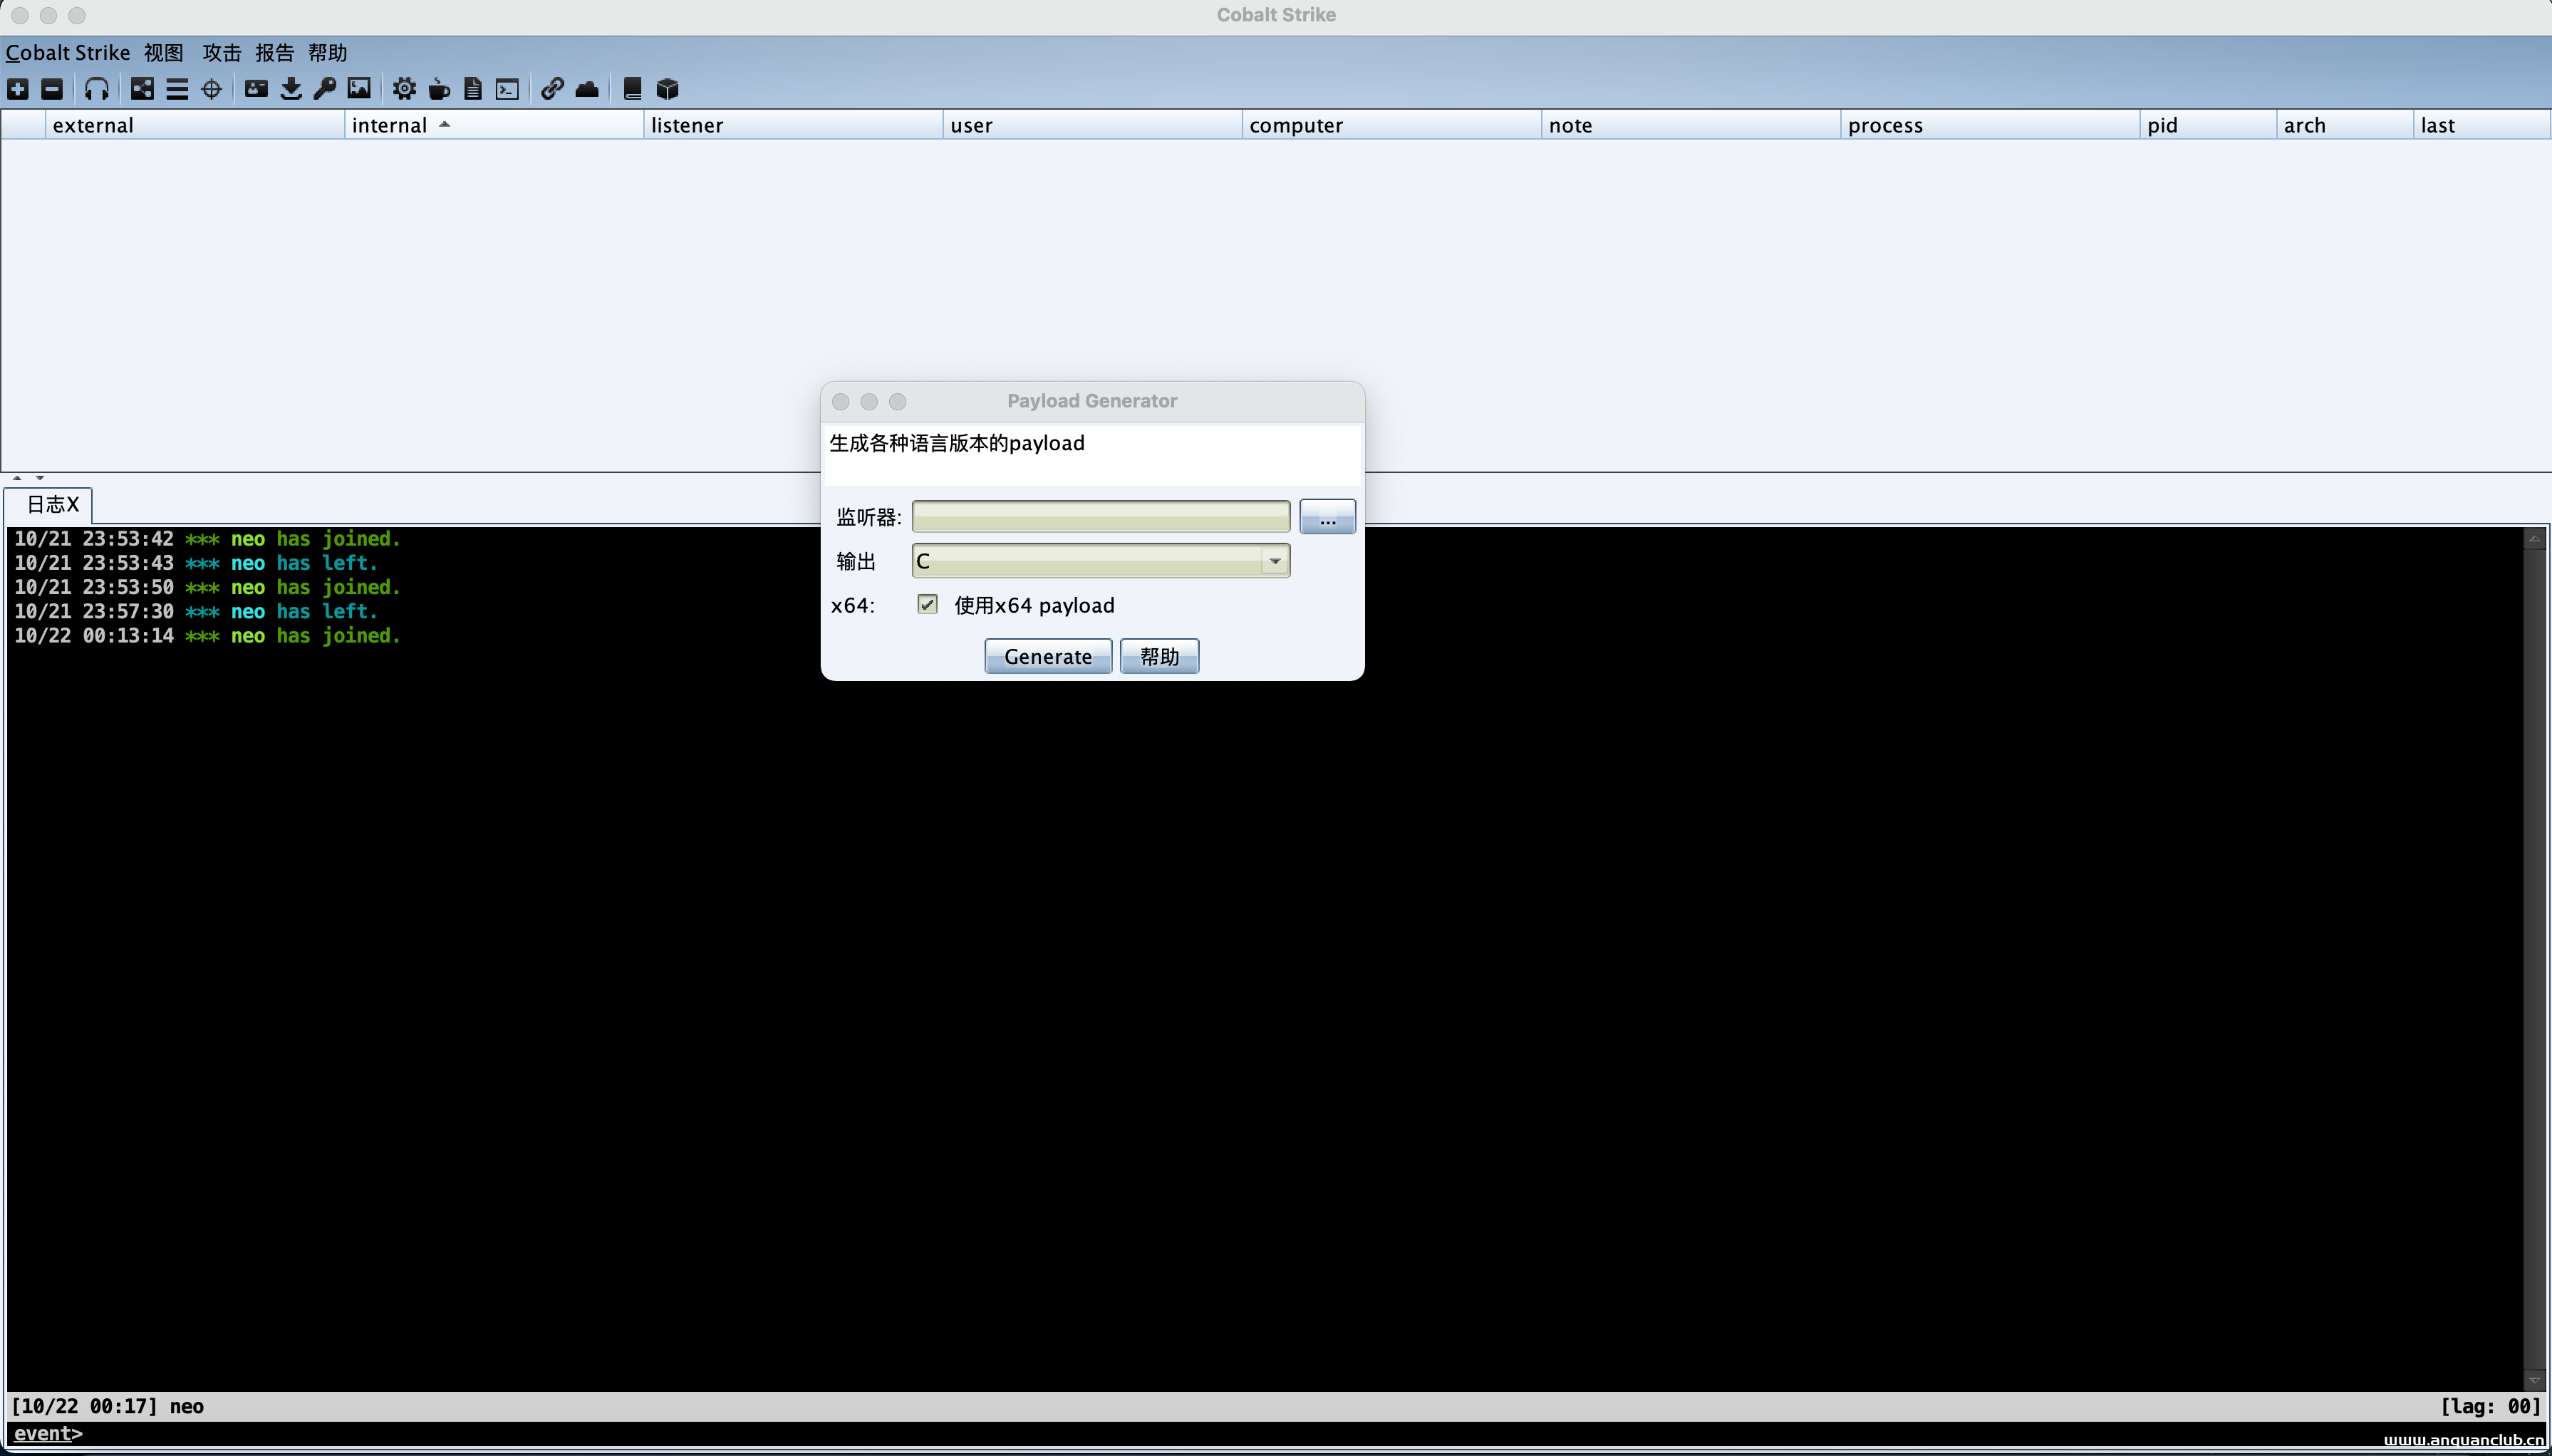
浅谈cs的shellcode的使用方法
前言:学习心得,大佬勿喷 看完本文你会了解到: 1、cs中的shellcode是做什么的? 2、用类似于cs、msf生成的shellcode的加载器是什么样的? 3、windows api是什么? 4、怎样从msf及cs生成的shel...
2022年3月10日 23:32CVE-2025-41393: Ricoh Web Image Monitor – Reflected XSS
漏洞标题 CVE-2025-41393: Ricoh Web Image Monitor - Reflected XSS 漏洞描述 A reflected cross-site scripting vulnerability exists in the laser printers and MFPs (multifunction printe...
2025年10月1日 23:15CVE-2018-6961: VMware NSX SD-WAN Edge – Command Injection
漏洞标题 CVE-2018-6961: VMware NSX SD-WAN Edge - Command Injection 漏洞描述 VMware NSX SD-WAN Edge (formerly VeloCloud Edge) before 3.1.2 contains an unauthenticated command inject...
2018年8月25日 13:41CVE-2025-51990: XWiki – Stored Cross-Site Scripting (XSS)
漏洞标题 CVE-2025-51990: XWiki – Stored Cross-Site Scripting (XSS) 漏洞描述 XWiki through version 17.3.0 contains stored cross-site scripting caused by improper sanitization of in...
2025年3月10日 14:53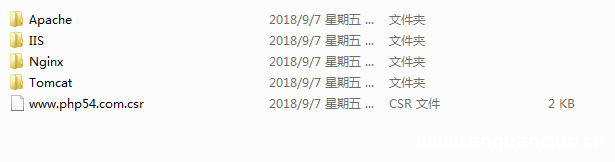
windows apache环境下部署SSL证书让网站支持https的配置方法_Linux
由于网站劫持与chrome浏览器默认不用https的提示网站不安全的原因,今天把SSL证书部署分享一下,希望能帮到大家 关于SSL证书的用处就不讲啦,需要部署的朋友应该已经了解过了,直接进入正题 安...
2023年5月8日 21:00CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File
漏洞标题 CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File 漏洞描述 The Google for WooCommerce plugin for WordPress ...
2024年11月13日 12:54CVE-2021-24320: WordPress Bello Directory & Listing Theme <1.6.0 - Cross-Site Scripting
漏洞标题 CVE-2021-24320: WordPress Bello Directory & Listing Theme <1.6.0 - Cross-Site Scripting 漏洞描述 WordPress Bello Directory & Listing theme before 1.6.0 contains...
2021年11月27日 05:22CVE-2024-32739: CyberPower < v2.8.3 - SQL Injection
漏洞标题 CVE-2024-32739: CyberPower < v2.8.3 - SQL Injection 漏洞描述 A sql injection vulnerability exists in CyberPower PowerPanel Enterprise prior to v2.8.3. PoC代码
2024年7月28日 17:19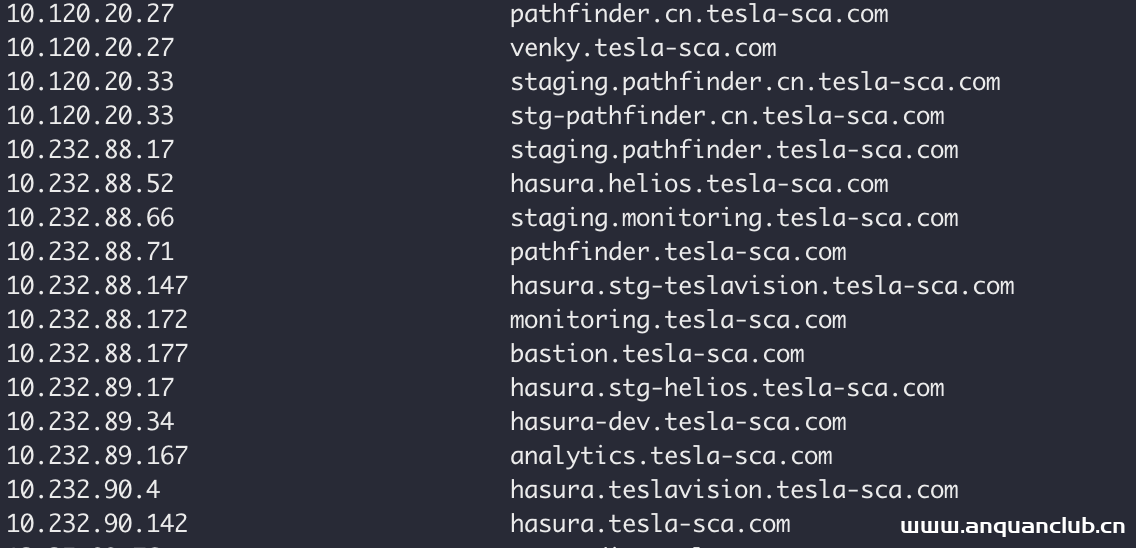
【今日思考题】当我们遇到解析到内网IP的域名的时候,可以干什么?
思考题?:当我们遇到这些解析到内网IP的域名的时候,可以干什么? 提示1: 可参考【搬运工】版块帖子 http://zone.huoxian.cn/t/porter?sort=newest 文字来源于- 火线 Zone-云安全社区,安全小天...
2022年3月10日 23:35CVE-2023-0676: phpIPAM 1.5.1 – Cross-site Scripting
漏洞标题 CVE-2023-0676: phpIPAM 1.5.1 - Cross-site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository phpipam/phpipam prior to 1.5.1. PoC代码
2023年11月17日 01:13CVE-2023-0669: Fortra GoAnywhere MFT – Remote Code Execution
漏洞标题 CVE-2023-0669: Fortra GoAnywhere MFT - Remote Code Execution 漏洞描述 Fortra GoAnywhere MFT is susceptible to remote code execution via unsafe deserialization of an arbitr...
2023年7月9日 11:35CVE-2021-3019: ffay lanproxy Directory Traversal
漏洞标题 CVE-2021-3019: ffay lanproxy Directory Traversal 漏洞描述 ffay lanproxy 0.1 is susceptible to a directory traversal vulnerability that could let attackers read /../conf/co...
2021年5月18日 17:00北京百卓多业务安全网关智能管理平台 CVE-2024-0939 任意文件上传漏洞
漏洞标题 北京百卓多业务安全网关智能管理平台 CVE-2024-0939 任意文件上传漏洞 漏洞描述 北京百卓多业务安全网关智能管理平台中存在任意文件上传漏洞,此漏洞是由于uploadfile.php未充分验证用...
2024年11月7日 00:13
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

