
最新发布第530页

Adobe ColdFusion /CFIDE/adminapi/accessmanager.cfc 代码执行漏洞(CVE-2023-29300)
漏洞标题 Adobe ColdFusion /CFIDE/adminapi/accessmanager.cfc 代码执行漏洞(CVE-2023-29300) 漏洞描述 Adobe ColdFusion 是 Adobe 公司开发的用于 Web 应用程序开发的商业应用程序服务器。...
 2023年5月9日 23:05
CVE-2018-19458: PHP Proxy 3.0.3 – Local File Inclusion
漏洞标题 CVE-2018-19458: PHP Proxy 3.0.3 - Local File Inclusion 漏洞描述 PHP Proxy 3.0.3 is susceptible to local file inclusion vulnerabilities that allow unauthenticated users to ...
2018年11月3日 06:26CVE-2024-28397: pyload-ng js2py – Remote Code Execution
漏洞标题 CVE-2024-28397: pyload-ng js2py - Remote Code Execution 漏洞描述 An issue in the component js2py.disable_pyimport() of js2py up to v0.74 allows attackers to execute arbitr...
2024年11月9日 19:26CVE-2022-38812: AeroCMS 0.1.1 – SQL Injection
漏洞标题 CVE-2022-38812: AeroCMS 0.1.1 - SQL Injection 漏洞描述 AeroCMS 0.1.1 contains a SQL injection caused by unsanitized author parameter, letting attackers execute arbitrary S...
2022年4月24日 17:28Apache OFBiz CVE-2024-38856 未授权代码执行漏洞
漏洞标题 Apache OFBiz CVE-2024-38856 未授权代码执行漏洞 漏洞描述 Apache OFBiz存在未授权代码执行漏洞,该漏洞是由于ProgramExport接口对用户的权限校验不当导致的。 PoC代码 暂无
2024年5月24日 22:54CVE-2021-45811: osTicket 1.15.x – SQL Injection
漏洞标题 CVE-2021-45811: osTicket 1.15.x - SQL Injection 漏洞描述 A SQL injection vulnerability in the "Search" functionality of "tickets.php" page in osTicket ...
2021年12月19日 14:54CVE-2023-6989: Shield Security WP Plugin <= 18.5.9 - Local File Inclusion
漏洞标题 CVE-2023-6989: Shield Security WP Plugin <= 18.5.9 - Local File Inclusion 漏洞描述 The Shield Security Smart Bot Blocking & Intrusion Prevention Security plugin for...
2023年8月1日 18:20CVE-2021-25008: The Code Snippets WordPress Plugin < 2.14.3 - Cross-Site Scripting
漏洞标题 CVE-2021-25008: The Code Snippets WordPress Plugin < 2.14.3 - Cross-Site Scripting 漏洞描述 The Wordpress plugin Code Snippets before 2.14.3 does not escape the snippet...
2021年9月17日 20:37CVE-2021-35394: RealTek AP Router SDK – Arbitrary Command Injection
漏洞标题 CVE-2021-35394: RealTek AP Router SDK - Arbitrary Command Injection 漏洞描述 The SDK exposes a UDP server that allows remote execution of arbitray commands. PoC代码
2021年2月17日 01:56CVE-2020-24589: WSO2 API Manager <=3.1.0 - Blind XML External Entity Injection
漏洞标题 CVE-2020-24589: WSO2 API Manager <=3.1.0 - Blind XML External Entity Injection 漏洞描述 WSO2 API Manager 3.1.0 and earlier is vulnerable to blind XML external entity in...
2020年1月6日 00:57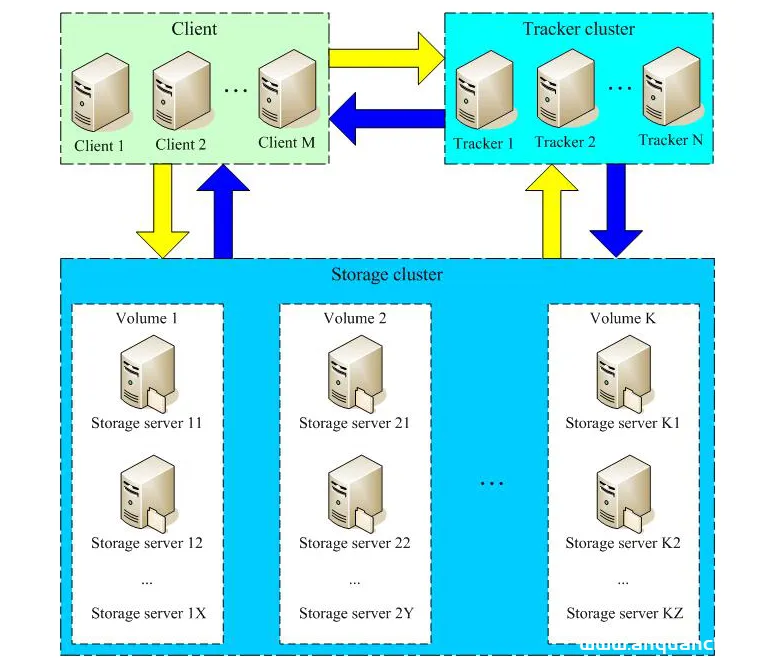
用nginx+FastDFS一步步搭建文件管理系统_服务器其它
FastDFS 是一个开源的高性能分布式文件系统(DFS)。 它的主要功能包括:文件存储,文件同步和文件访问,以及高容量和负载平衡。主要解决了海量数据存储问题,特别适合以中小文件(建议范围:4K...
2023年4月16日 20:56
linux 配置本地yum源,配置国内yum源,配置epel源的步骤_Linux
这篇文章主要介绍了linux 配置本地yum源,配置国内yum源,配置epel源的步骤,帮助大家更好的配置服务器,感兴趣的朋友可以了解下 一.配置本地yum源 1.挂载ISO镜像 mount -o loop /mnt/yum-iso/C...
2022年11月21日 20:10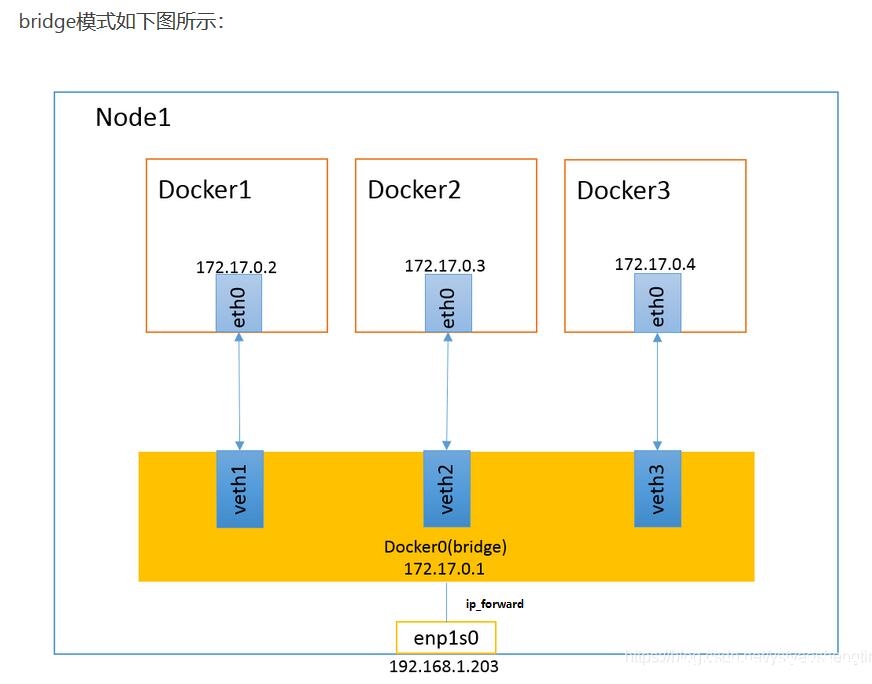
Docker与iptables及实现bridge方式网络隔离与通信操作_docker
这篇文章主要介绍了Docker与iptables及实现bridge方式网络隔离与通信操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 Docker提供了bridge, host, overlay等多种网络。同...
2023年1月6日 20:56CVE-2008-6668: nweb2fax <=0.2.7 - Local File Inclusion
漏洞标题 CVE-2008-6668: nweb2fax <=0.2.7 - Local File Inclusion 漏洞描述 nweb2fax 0.2.7 and earlier allow remote attackers to read arbitrary files via the id parameter submitted...
2008年2月17日 19:35CVE-2018-0127: Cisco RV132W/RV134W Router – Information Disclosure
漏洞标题 CVE-2018-0127: Cisco RV132W/RV134W Router - Information Disclosure 漏洞描述 Cisco RV132W ADSL2+ Wireless-N VPN Routers and Cisco RV134W VDSL2 Wireless-AC VPN Routers could...
2018年1月21日 21:55CVE-2023-27639: PrestaShop TshirteCommerce – Directory Traversal
漏洞标题 CVE-2023-27639: PrestaShop TshirteCommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年8月31日 00:41
2026年10月22日 11:46
2026年10月21日 11:45
2026年10月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

